Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control Juju Orchestration Cloud Credential Theft Juju Orchestration Vulnerability CVE-2026-4370
  • Vulnerability Report

CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control

Do Son April 3, 2026 0

Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops libinput Sandbox Escape CVE-2026-35093
  • Vulnerability Report

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops

Do Son April 3, 2026 0

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!
The MuPDF Vulnerability Turning “Safe” PDFs into System Hijackers MuPDF RCE Integer Overflow
  • Vulnerability Report

The MuPDF Vulnerability Turning “Safe” PDFs into System Hijackers

Do Son April 3, 2026 0

Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

The Hidden Costs of Managing Too Many Security Tools bc257a04-d077-46b7-a6bc-3011efc3ac3f
  • Technique

The Hidden Costs of Managing Too Many Security Tools

Do Son April 3, 2026 0
Security tool sprawl rarely starts as a strategy. It starts as a quick fix. A team adds...
Read More Read more about The Hidden Costs of Managing Too Many Security Tools
The EU’s AWS “Master Key”: How a Compromised Trivy Update Leaked 340GB of Data Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Data Leak

The EU’s AWS “Master Key”: How a Compromised Trivy Update Leaked 340GB of Data

Do Son April 3, 2026 0

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!

The WordPress Killer? Cloudflare Unveils EmDash, the AI-Native CMS Built for the Serverless Epoch Cloudflare EmDash CMS
  • Technology

The WordPress Killer? Cloudflare Unveils EmDash, the AI-Native CMS Built for the Serverless Epoch

Do Son April 3, 2026 0

Cloudflare debuts EmDash, an AI-native, serverless CMS built on Astro 6.0. Say goodbye to WordPress plugin hacks with V8 isolate sandboxing and passkey security.

OpenSSH 10.3 Patches Command Execution and “scp” Privilege Escalation OpenSSH 10.3 Patch SSH Command Injection CVE-2023-38408 OpenSSH Vulnerability CVE-2026-3497
  • Vulnerability Report

OpenSSH 10.3 Patches Command Execution and “scp” Privilege Escalation

Do Son April 3, 2026 0

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.

The Resurrection of the Beam: Google Challenges AirDrop with Android 17’s “Tap to Share” Android 17 Tap to Share Gemini Scam Detection Galaxy S26 AI Security
  • Android

The Resurrection of the Beam: Google Challenges AirDrop with Android 17’s “Tap to Share”

Do Son April 3, 2026 0

Google’s "Tap to Share" leaked for Android 17! Using NFC and UWB, this new Quick Share feature aims to end AirDrop's dominance. Discover how it works.
Inside the Rapid Evolution of the BlankGrabber Stealer BlankGrabber Stealer Python Malware Analysis
  • Malware

Inside the Rapid Evolution of the BlankGrabber Stealer

Do Son April 3, 2026 0

Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.

The Apache 2.0 Revolution: Google’s Gemma 4 Shatters the Open-Source Intelligence Ceiling Google Gemma 4 release
  • Technology

The Apache 2.0 Revolution: Google’s Gemma 4 Shatters the Open-Source Intelligence Ceiling

Do Son April 3, 2026 0

Google releases Gemma 4 under the Apache 2.0 license. Featuring multimodal edge models and a 31B "Dense" system, it redefines AI digital sovereignty for 2026.

The Lobster Craze: How OpenClaw is Triggering a High-Stakes AI Agent Arms Race in China Apple OpenClaw competitor Apple AI agent, Siri agentic capabilities, Apple computer-use agent OpenClaw Lobster
  • Technology

The Lobster Craze: How OpenClaw is Triggering a High-Stakes AI Agent Arms Race in China

Do Son April 3, 2026 0

ByteDance and OpenAI are racing to dominate "Lobster Husbandry." Discover how the OpenClaw agent is transforming WeChat, Xiaomi, and the global AI landscape.

Microsoft’s Declaration of Independence: The New MAI Models Challenging OpenAI and Google Microsoft MAI models
  • Technology

Microsoft’s Declaration of Independence: The New MAI Models Challenging OpenAI and Google

Do Son April 3, 2026 0

Microsoft CEO Mustafa Suleyman unveils MAI-Transcribe-1, MAI-Voice-1, and MAI-Image-2—proprietary AI built to undercut competitors and secure self-sufficiency.

Apple Severs All Payment Processing in Russia Following Government Mandates Apple Russia payment suspension iOS 26.3 Proximity Pairing, Apple DMA compliance 2026 Tap to Pay, Apple Pay Wireless charging Always-On Display, iOS 26 iOS 26, EU App APIs Rare Earths, Apple Supply Chain
  • Technology

Apple Severs All Payment Processing in Russia Following Government Mandates

Do Son April 3, 2026 0

Apple officially ceases all payment services in Russia as of April 1, 2026. Subscriptions, App Store buys, and iCloud+ renewals are now indefinitely frozen.

Critical 9.8 CVSS RCE Vulnerabilities Exposed in Progress ShareFile Progress ShareFile RCE Storage Zones Controller
  • Vulnerability Report

Critical 9.8 CVSS RCE Vulnerabilities Exposed in Progress ShareFile

Do Son April 3, 2026 0

Progress ShareFile hit by critical 9.8 CVSS RCE flaws (CVE-2026-2699). Unauthenticated attackers can hijack configuration and execute code. Update to v5.12.4!

Targeting the Cloud: IRGC Claims Strike on Oracle’s Dubai Data Sanctuary IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Technology

Targeting the Cloud: IRGC Claims Strike on Oracle’s Dubai Data Sanctuary

Do Son April 3, 2026 0

Iran's IRGC claims a strike on Oracle's Dubai data center, targeting U.S. tech infrastructure. Dubai officials deny damage as regional tensions escalate.

The Human Variable: How a Masterful Phishing Ruse Hijacked Axios and 100 Million Users Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Cybercriminals

The Human Variable: How a Masterful Phishing Ruse Hijacked Axios and 100 Million Users

Do Son April 3, 2026 0

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.

The Cloud in Flames: AWS Bahrain Fire Signals a New Era of Kinetic Strikes on Tech Infrastructure Amazon Redshift JDBC Driver RCE CVE-2026-8178 AWS Bahrain fire 2026 AWS UAE data center fire Amazon North Korean hacker keystroke latency, Arizona laptop farm infiltration
  • Technology

The Cloud in Flames: AWS Bahrain Fire Signals a New Era of Kinetic Strikes on Tech Infrastructure

Do Son April 3, 2026 0

A massive fire at an AWS facility in Bahrain highlights a dangerous shift toward kinetic strikes on cloud infrastructure. Is your multi-region strategy ready?

Where to Trade Gold Without Fiat Using Crypto 2026? cy
  • Technique

Where to Trade Gold Without Fiat Using Crypto 2026?

Do Son April 3, 2026 0
Trading gold using cryptocurrency removes the need for traditional bank transfers and allows for continuous market access....
Read More Read more about Where to Trade Gold Without Fiat Using Crypto 2026?
Smart Home Alert: Critical Flaws Exposed in TP-Link Tapo Security Cameras Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Smart Home Alert: Critical Flaws Exposed in TP-Link Tapo Security Cameras

Do Son April 3, 2026 0

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!
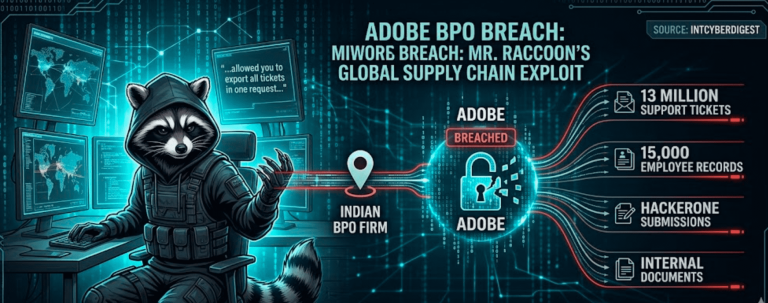
The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets Adobe BPO Breach Mr. Raccoon Hacker
  • Data Leak

The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets

Do Son April 3, 2026 0

13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.
200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover Perfmatters Vulnerability WordPress Site Takeover
  • Vulnerability Report

200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover

Do Son April 3, 2026 0

A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!
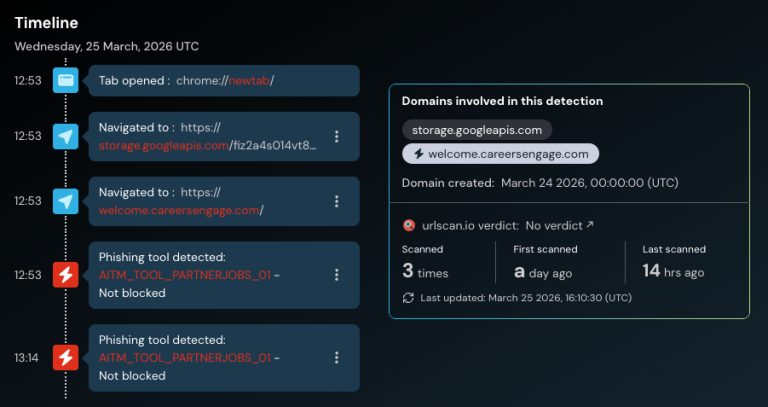
TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google” TikTok for Business Phishing AiTM Phishing Kit
  • Cybercriminals

TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google”

Do Son April 3, 2026 0

Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-64063CVSS 9.8
    Primakon Pi Portal 1.0.18 API endpoints fail to enforce sufficient authorization checks when processing requests. Specifically, a standard...
    📅 Updated: Nov 4, 2026
  • CVE-2025-51742CVSS 9.8
    An issue was discovered in jishenghua JSH_ERP 2.3.1. The /material/getMaterialEnableSerialNumberList endpoint passes the search query parameter directly to...
    📅 Updated: Nov 4, 2026
  • CVE-2025-50402CVSS 9.8
    FAST FAC1200R F400_FAC1200R_Q is vulnerable to Buffer Overflow in the function sub_80435780 via the parameter string fac_password.
    📅 Updated: Nov 4, 2026
  • CVE-2025-50399CVSS 9.8
    FAST FAC1200R F400_FAC1200R_Q is vulnerable to Buffer Overflow in the function sub_80435780 via the parameter password.
    📅 Updated: Nov 4, 2026
  • CVE-2025-65235CVSS 9.8
    OpenCode Systems USSD Gateway OC Release: 5 Version 6.13.11 was discovered to contain a SQL injection vulnerability via...
    📅 Updated: Nov 4, 2026
  • CVE-2025-65236CVSS 9.8
    OpenCode Systems USSD Gateway OC Release: 5 was discovered to contain a SQL injection vulnerability via the Session...
    📅 Updated: Nov 4, 2026
  • CVE-2025-55469CVSS 9.8
    Incorrect access control in youlai-boot v2.21.1 allows attackers to escalate privileges and access the Administrator backend.
    📅 Updated: Nov 4, 2026
  • CVE-2025-65669CVSS 9.1
    An issue was discovered in classroomio 0.1.13. Student accounts are able to delete courses from the Explore page...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.