Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
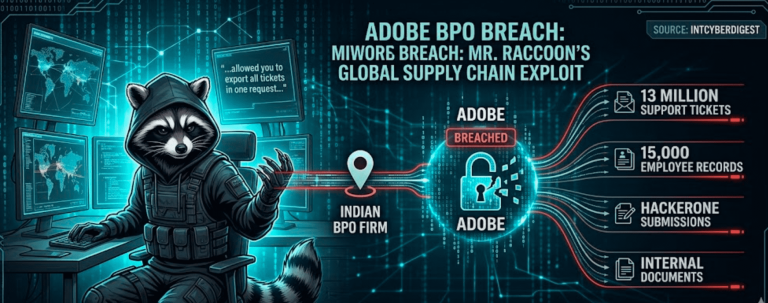
The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets Adobe BPO Breach Mr. Raccoon Hacker
  • Data Leak

The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets

Do Son April 3, 2026 0

13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.
200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover Perfmatters Vulnerability WordPress Site Takeover
  • Vulnerability Report

200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover

Do Son April 3, 2026 0

A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!
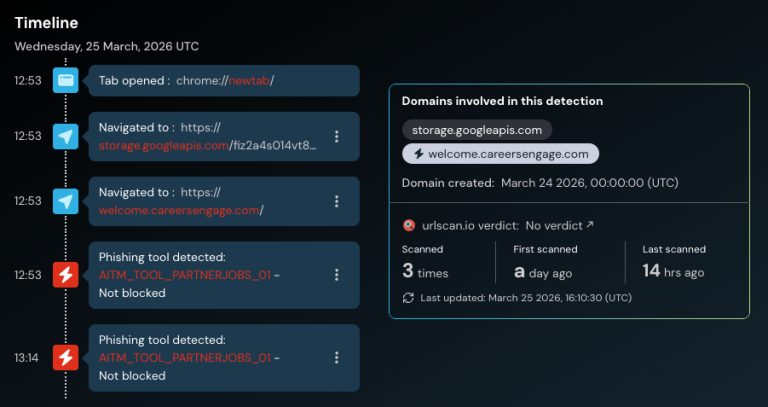
TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google” TikTok for Business Phishing AiTM Phishing Kit
  • Cybercriminals

TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google”

Do Son April 3, 2026 0

Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.

Joomla! Issues Security Patch: Critical File Deletion and Webservice Flaws Exposed Joomla Vulnerability CVE-2026-23898
  • Vulnerability Report

Joomla! Issues Security Patch: Critical File Deletion and Webservice Flaws Exposed

Do Son April 2, 2026 0

Joomla releases critical 8.6 CVSS patches for CVE-2026-23898 & CVE-2026-23899. Prevent arbitrary file deletion and API leaks—update to 5.4.4 or 6.0.4 today!

Lodash Patches High-Severity Code Injection Vulnerability Lodash Code Injection CVE-2026-4800
  • Vulnerability Report

Lodash Patches High-Severity Code Injection Vulnerability

Do Son April 2, 2026 0

Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

NVIDIA Patches High-Severity Flaws Threatening Jetson Edge AI Systems NVIDIA FLARE Vulnerability Federated Learning Security NVIDIA Jetson Linux Edge AI Security BioNeMo Vulnerability Insecure Deserialization NVIDIA RTX 50 Super delay NVIDIA Nsight Vulnerability Merlin Transformers4Rec NVIDIA AI Bubble $57 Billion Revenue H20 AI chip NVIDIA earnings Blackwell AI Nvidia DGX-1 Vulnerabilities CVE-2024-0143 NVIDIA Linux Gaming, VKD3D Performance
  • Vulnerability Report

NVIDIA Patches High-Severity Flaws Threatening Jetson Edge AI Systems

Do Son April 2, 2026 0

NVIDIA fixes high-severity vulnerabilities (CVSS 8.3) in Jetson Linux for Xavier, Orin, and Thor. Protect your autonomous systems—update to 36.5 or 35.6.4.
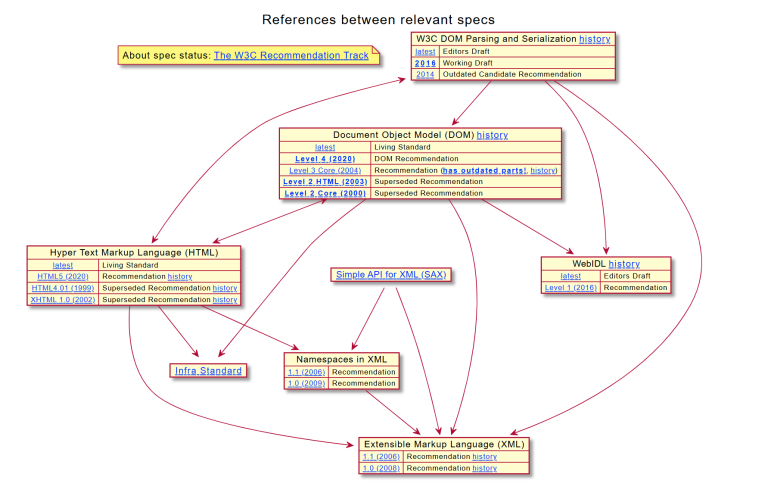
The xmldom CDATA Flaw That Puts 23 Million Weekly Users at Risk xmldom Vulnerability XML Injection
  • Vulnerability Report

The xmldom CDATA Flaw That Puts 23 Million Weekly Users at Risk

Do Son April 2, 2026 0

Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

Security Alert: Critical Vulnerability Hits Anritsu Remote Spectrum Monitors Ollama Heap Leak CVE-2026-5757 Anritsu Vulnerability Authentication Bypass Gootloader Malware Malformed ZIP Evasion Blender Malware, StealC V2 Lectora, XSS CVE-2025-9125 HFS RCE, Template Injection Arch Linux Malware, CHAOS RAT CVE-2024-56404 - CVE-2024-39327 CVE-2025-2538
  • Vulnerability Report

Security Alert: Critical Vulnerability Hits Anritsu Remote Spectrum Monitors

Do Son April 2, 2026 0

CISA alerts to a 9.8 CVSS flaw in Anritsu Spectrum Monitors (CVE-2026-3356). No patch is coming for this authentication bypass. Secure your network now!

“ChatGPT Ad Blocker” Extension Caught Harvesting Your Private Conversations ChatGPT Ad Blocker OpenAI Malware
  • Data Leak

“ChatGPT Ad Blocker” Extension Caught Harvesting Your Private Conversations

Do Son April 2, 2026 0

DomainTools unmasks a malicious "ChatGPT Ad Blocker" Chrome extension that steals private conversations and sends them to Discord. Check your extensions now!
The 3GB Compromise: Why Raspberry Pi is Raising Prices and Launching a New “Goldilocks” Model Raspberry Pi 4 3GB release
  • Technology

The 3GB Compromise: Why Raspberry Pi is Raising Prices and Launching a New “Goldilocks” Model

Do Son April 2, 2026 0

Faced with a 7x spike in memory costs, Raspberry Pi has raised prices and launched a new 3GB Pi 4. Discover the new 2026 hardware pricing landscape here.

Collateral Damage: Anthropic’s Aggressive DMCA Dragnet Snares Thousands of Innocent GitHub Forks Anthropic Claude Lawsuit Claude Max limits, AI subscription lawsuit, Claude Pro vs Max Claude Mythos security audit Claude Identity Verification Anthropic DMCA GitHub takedown bugs Nuclear weapons Xcode, Claude AI Anthropic, Claude Sonnet 4 Claude AI, AI safety
  • Technology

Collateral Damage: Anthropic’s Aggressive DMCA Dragnet Snares Thousands of Innocent GitHub Forks

Do Son April 2, 2026 0

Anthropic's 8,100-repo DMCA sweep for Claude Code accidentally nuked thousands of legitimate forks. Discover the fallout and the silent restoration on GitHub.

Oracle Axes 30,000 Staff to Fuel a $10 Billion AI Gamble IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Technology

Oracle Axes 30,000 Staff to Fuel a $10 Billion AI Gamble

Do Son April 2, 2026 0

Oracle has initiated its largest layoff in history, cutting up to 30,000 jobs to pivot $10B toward AI infrastructure amid a 50% stock decline and rising debt.
The Infinite Loop: Microsoft Retracts Broken Windows 11 Update KB5079391 Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The Infinite Loop: Microsoft Retracts Broken Windows 11 Update KB5079391

Do Son April 2, 2026 0

Microsoft has pulled the broken KB5079391 update after it caused infinite installation loops. Learn how the new KB5086672 fix resolves error 0x80073712.

The DarkSword Threat: Apple Issues Emergency iOS 18.7.7 Patch for Legacy iPhones DarkSword exploit kit iOS 18.7.7 security update CVE-2024-44308 & CVE-2024-44309 Apple appeal, Epic Games lawsuit
  • Vulnerability Report

The DarkSword Threat: Apple Issues Emergency iOS 18.7.7 Patch for Legacy iPhones

Do Son April 2, 2026 0

Apple releases iOS 18.7.7 to combat the "DarkSword" exploit kit. Protect your legacy iPhone or iPad from this state-level threat by updating today.

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia UNC5221 HAFNIUM Extradition PRC State Espionage
  • Cyber Security
  • Malware

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

Do Son April 2, 2026 0

Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Critical 9.2 Severity Flaw in Gigabyte Control Center Exposed Gigabyte Control Center CVE-2026-4415
  • Vulnerability Report

Critical 9.2 Severity Flaw in Gigabyte Control Center Exposed

Do Son April 2, 2026 0

Gigabyte Control Center faces a critical 9.2 severity flaw (CVE-2026-4415). Unauthenticated attackers can write files and execute code—update to 25.12.10.01 now.

The Fatal Human Error: How One Manual Step Leaked Claude Code to the World Anthropic Claude Code telemetry rollback response and developer community controversy Claude Code human error Claude AI Data Wipe, Constraining AI Tools Anthropic lawsuit, AI copyright Claude Code, web editor
  • Data Leak

The Fatal Human Error: How One Manual Step Leaked Claude Code to the World

Do Son April 2, 2026 0

Anthropic's Boris Cherny confirms a "human error" leaked Claude Code's source via MAP files. Discover how manual steps led to 8,100+ GitHub repository purges.

Inside the BRUSHWORM Malware Campaign Bridging Air-Gaps with USB “Sleeper” Cells Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Malware

Inside the BRUSHWORM Malware Campaign Bridging Air-Gaps with USB “Sleeper” Cells

Do Son April 2, 2026 0

Elastic Security Labs uncovers BRUSHWORM and BRUSHLOGGER: AI-aided malware using USB drives to steal data from air-gapped financial networks. Update your defenses!

The $1.75 Trillion Launch: SpaceX Files Confidential IPO to Eclipse Global Capital Records Anthropic SpaceX partnership SpaceX IPO 1.75 trillion 2026 Tech IPO wave, SpaceX OpenAI Anthropic valuation SpaceX IPO 2026, $800 Billion Valuation SpaceX $1.5 Trillion IPO, Starship Starlink
  • Technology

The $1.75 Trillion Launch: SpaceX Files Confidential IPO to Eclipse Global Capital Records

Do Son April 2, 2026 0

SpaceX has filed for a record-breaking $1.75 trillion IPO. Discover Musk’s 2026 plan for Orbital AI data centers, Starlink's growth, and the road to Mars.

The 5TB Power Play: Google AI Pro Crushes the Competition with Massive Free Storage and Autonomous Agents Google Gemini Pentagon deal Google AI Pro 5TB storage Gemini 3.1 Pro launch
  • Technology

The 5TB Power Play: Google AI Pro Crushes the Competition with Massive Free Storage and Autonomous Agents

Do Son April 2, 2026 0

Google AI Pro hits 5TB! Discover the 2026 storage boost and new Gemini AI Agents for Workspace, Gmail, and Chrome—all at no extra cost to your subscription.

The May Inquisition: UK Regulators to Probe if Microsoft’s “AI Super-Ecosystem” is Stifling the Cloud Microsoft Strategic Market Status investigation Dell CES 2026 AI PC marketing, Microsoft Copilot+ PC consumer apathy Microsoft AI Sales Quota Enterprise AI Demand Edge Copilot, AI browsing
  • Technology

The May Inquisition: UK Regulators to Probe if Microsoft’s “AI Super-Ecosystem” is Stifling the Cloud

Do Son April 2, 2026 0

The UK CMA is launching a "Strategic Market Status" probe into Microsoft in May 2026. Discover how AI and cloud bundling are under the regulatory microscope.

The $852 Billion Behemoth: OpenAI’s Record-Breaking $122B Funding Signals the Dawn of the AI Superapp OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

The $852 Billion Behemoth: OpenAI’s Record-Breaking $122B Funding Signals the Dawn of the AI Superapp

Do Son April 2, 2026 0

OpenAI hits an $852B valuation after a record $122B funding round. Discover the 2026 roadmap for the "AI Superapp" and the imminent move toward a public IPO.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-84719CVSS 9.9
    A flaw was found in the Ansible Automation Platform automation-controller. When a WorkflowJobTemplate is copied, the deep-copy permission...
    📅 Updated: Nov 5, 2026
  • CVE-2026-84474CVSS 9.9
    A flaw was found in Red Hat Ansible Automation Platform's automation- controller. The provisioning-callback secret (host_config_key) is exposed...
    📅 Updated: Nov 5, 2026
  • CVE-2026-84502CVSS 9.9
    A flaw was found in Red Hat Ansible Automation Platform's automation- controller. The Project scm_url field is not...
    📅 Updated: Nov 5, 2026
  • CVE-2026-76578CVSS 9.8
    A flaw was found in FreeIPA. The self-managed OTP token ACI does not require authentication and does not...
    📅 Updated: Nov 5, 2026
  • CVE-2026-75884CVSS 9.1
    A flaw was found in AWX. The container group pod_spec_override field uses an incomplete blocklist that only restricts...
    📅 Updated: Nov 5, 2026
  • CVE-2026-122051CVSS 10.0
    A flaw has been found in Edimax BR-6208AC 1.32. Affected by this vulnerability is an unknown functionality of...
    📅 Updated: Nov 4, 2026
  • CVE-2026-4631CVSS 9.8
    Cockpit's remote login feature passes user-supplied hostnames and usernames from the web interface to the SSH client without...
    📅 Updated: Nov 4, 2026
  • CVE-2026-4480CVSS 9.0
    A flaw was found in the Samba printing subsystem. Samba passes the client-controlled job description string to the...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.