Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical 9.8 CVSS RCE Vulnerabilities Exposed in Progress ShareFile Progress ShareFile RCE Storage Zones Controller
  • Vulnerability Report

Critical 9.8 CVSS RCE Vulnerabilities Exposed in Progress ShareFile

Do Son April 3, 2026 0

Progress ShareFile hit by critical 9.8 CVSS RCE flaws (CVE-2026-2699). Unauthenticated attackers can hijack configuration and execute code. Update to v5.12.4!

Targeting the Cloud: IRGC Claims Strike on Oracle’s Dubai Data Sanctuary IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Technology

Targeting the Cloud: IRGC Claims Strike on Oracle’s Dubai Data Sanctuary

Do Son April 3, 2026 0

Iran's IRGC claims a strike on Oracle's Dubai data center, targeting U.S. tech infrastructure. Dubai officials deny damage as regional tensions escalate.

The Human Variable: How a Masterful Phishing Ruse Hijacked Axios and 100 Million Users Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Cybercriminals

The Human Variable: How a Masterful Phishing Ruse Hijacked Axios and 100 Million Users

Do Son April 3, 2026 0

The Axios npm hijack exposed millions to a RAT. Discover how North Korean-nexus actor UNC1069 used a masterful phishing ruse to bypass 2FA and steal credentials.

The Cloud in Flames: AWS Bahrain Fire Signals a New Era of Kinetic Strikes on Tech Infrastructure Amazon Redshift JDBC Driver RCE CVE-2026-8178 AWS Bahrain fire 2026 AWS UAE data center fire Amazon North Korean hacker keystroke latency, Arizona laptop farm infiltration
  • Technology

The Cloud in Flames: AWS Bahrain Fire Signals a New Era of Kinetic Strikes on Tech Infrastructure

Do Son April 3, 2026 0

A massive fire at an AWS facility in Bahrain highlights a dangerous shift toward kinetic strikes on cloud infrastructure. Is your multi-region strategy ready?

Where to Trade Gold Without Fiat Using Crypto 2026? cy
  • Technique

Where to Trade Gold Without Fiat Using Crypto 2026?

Do Son April 3, 2026 0
Trading gold using cryptocurrency removes the need for traditional bank transfers and allows for continuous market access....
Read More Read more about Where to Trade Gold Without Fiat Using Crypto 2026?
Smart Home Alert: Critical Flaws Exposed in TP-Link Tapo Security Cameras Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Smart Home Alert: Critical Flaws Exposed in TP-Link Tapo Security Cameras

Do Son April 3, 2026 0

TP-Link warns of high-severity flaws (CVSS 8.7) in Tapo C520WS cameras. Attackers can bypass auth or blind your security. Update to firmware 1.2.4 now!
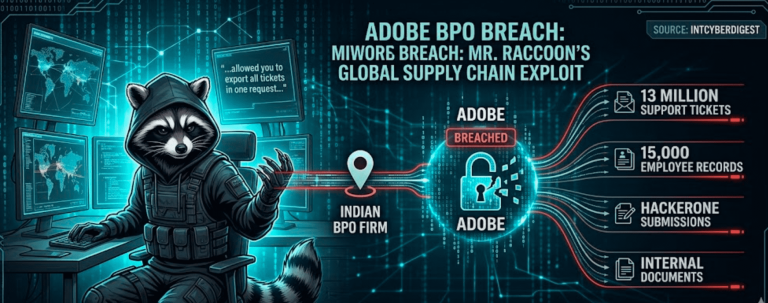
The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets Adobe BPO Breach Mr. Raccoon Hacker
  • Data Leak

The BPO Backdoor: How “Mr. Raccoon” Swiped 13 Million Adobe Support Tickets

Do Son April 3, 2026 0

13M Adobe tickets leaked! Mr. Raccoon bypassed elite defenses by targeting a BPO partner in India. See how the "human element" cracked the supply chain.
200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover Perfmatters Vulnerability WordPress Site Takeover
  • Vulnerability Report

200,000+ Sites at Risk: Perfmatters Flaw Enables Full WordPress Site Takeover

Do Son April 3, 2026 0

A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!
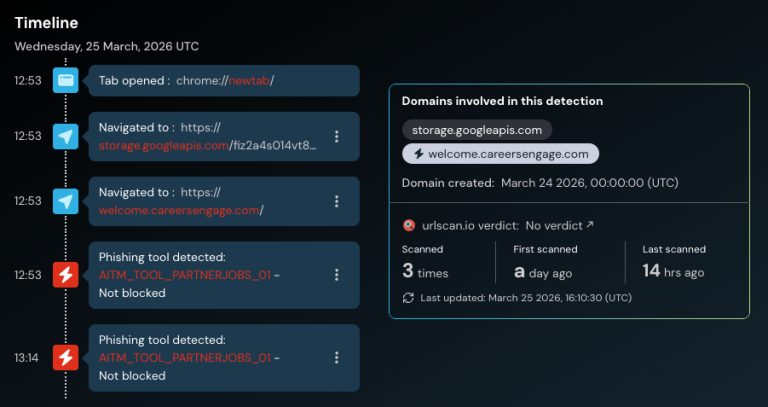
TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google” TikTok for Business Phishing AiTM Phishing Kit
  • Cybercriminals

TikTok for Business Under Siege: New Phishing Campaign Exploits “Login with Google”

Do Son April 3, 2026 0

Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.

Joomla! Issues Security Patch: Critical File Deletion and Webservice Flaws Exposed Joomla Vulnerability CVE-2026-23898
  • Vulnerability Report

Joomla! Issues Security Patch: Critical File Deletion and Webservice Flaws Exposed

Do Son April 2, 2026 0

Joomla releases critical 8.6 CVSS patches for CVE-2026-23898 & CVE-2026-23899. Prevent arbitrary file deletion and API leaks—update to 5.4.4 or 6.0.4 today!

Lodash Patches High-Severity Code Injection Vulnerability Lodash Code Injection CVE-2026-4800
  • Vulnerability Report

Lodash Patches High-Severity Code Injection Vulnerability

Do Son April 2, 2026 0

Lodash (CVE-2026-4800) faces an 8.1 CVSS code injection flaw in the _.template function. Attackers can bypass validation via imports. Update to 4.18.0 now!

NVIDIA Patches High-Severity Flaws Threatening Jetson Edge AI Systems NVIDIA FLARE Vulnerability Federated Learning Security NVIDIA Jetson Linux Edge AI Security BioNeMo Vulnerability Insecure Deserialization NVIDIA RTX 50 Super delay NVIDIA Nsight Vulnerability Merlin Transformers4Rec NVIDIA AI Bubble $57 Billion Revenue H20 AI chip NVIDIA earnings Blackwell AI Nvidia DGX-1 Vulnerabilities CVE-2024-0143 NVIDIA Linux Gaming, VKD3D Performance
  • Vulnerability Report

NVIDIA Patches High-Severity Flaws Threatening Jetson Edge AI Systems

Do Son April 2, 2026 0

NVIDIA fixes high-severity vulnerabilities (CVSS 8.3) in Jetson Linux for Xavier, Orin, and Thor. Protect your autonomous systems—update to 36.5 or 35.6.4.
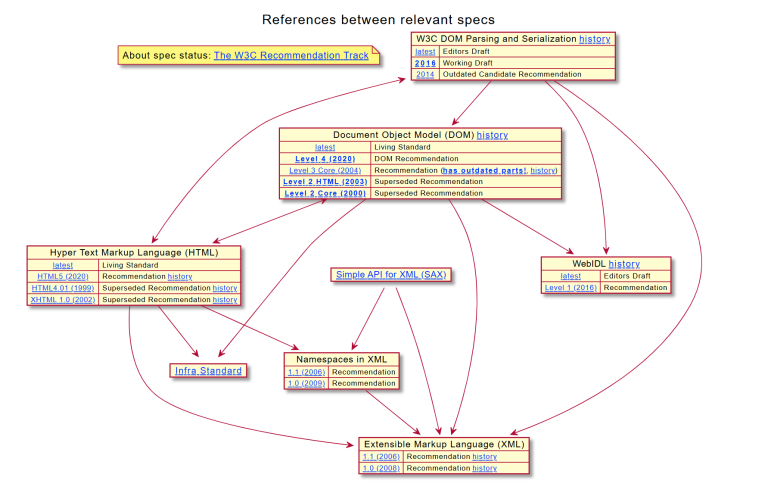
The xmldom CDATA Flaw That Puts 23 Million Weekly Users at Risk xmldom Vulnerability XML Injection
  • Vulnerability Report

The xmldom CDATA Flaw That Puts 23 Million Weekly Users at Risk

Do Son April 2, 2026 0

Fix CVE-2026-34601 in @xmldom/xmldom (CVSS 7.5). A CDATA injection flaw allows attackers to bypass "safe zones" and manipulate business logic. Update now!

Security Alert: Critical Vulnerability Hits Anritsu Remote Spectrum Monitors Ollama Heap Leak CVE-2026-5757 Anritsu Vulnerability Authentication Bypass Gootloader Malware Malformed ZIP Evasion Blender Malware, StealC V2 Lectora, XSS CVE-2025-9125 HFS RCE, Template Injection Arch Linux Malware, CHAOS RAT CVE-2024-56404 - CVE-2024-39327 CVE-2025-2538
  • Vulnerability Report

Security Alert: Critical Vulnerability Hits Anritsu Remote Spectrum Monitors

Do Son April 2, 2026 0

CISA alerts to a 9.8 CVSS flaw in Anritsu Spectrum Monitors (CVE-2026-3356). No patch is coming for this authentication bypass. Secure your network now!

“ChatGPT Ad Blocker” Extension Caught Harvesting Your Private Conversations ChatGPT Ad Blocker OpenAI Malware
  • Data Leak

“ChatGPT Ad Blocker” Extension Caught Harvesting Your Private Conversations

Do Son April 2, 2026 0

DomainTools unmasks a malicious "ChatGPT Ad Blocker" Chrome extension that steals private conversations and sends them to Discord. Check your extensions now!
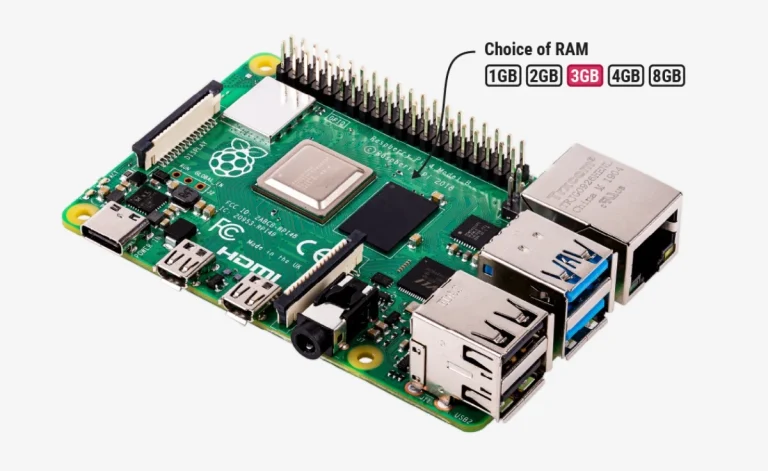
The 3GB Compromise: Why Raspberry Pi is Raising Prices and Launching a New “Goldilocks” Model Raspberry Pi 4 3GB release
  • Technology

The 3GB Compromise: Why Raspberry Pi is Raising Prices and Launching a New “Goldilocks” Model

Do Son April 2, 2026 0

Faced with a 7x spike in memory costs, Raspberry Pi has raised prices and launched a new 3GB Pi 4. Discover the new 2026 hardware pricing landscape here.

Collateral Damage: Anthropic’s Aggressive DMCA Dragnet Snares Thousands of Innocent GitHub Forks Anthropic Claude Lawsuit Claude Max limits, AI subscription lawsuit, Claude Pro vs Max Claude Mythos security audit Claude Identity Verification Anthropic DMCA GitHub takedown bugs Nuclear weapons Xcode, Claude AI Anthropic, Claude Sonnet 4 Claude AI, AI safety
  • Technology

Collateral Damage: Anthropic’s Aggressive DMCA Dragnet Snares Thousands of Innocent GitHub Forks

Do Son April 2, 2026 0

Anthropic's 8,100-repo DMCA sweep for Claude Code accidentally nuked thousands of legitimate forks. Discover the fallout and the silent restoration on GitHub.

Oracle Axes 30,000 Staff to Fuel a $10 Billion AI Gamble IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Technology

Oracle Axes 30,000 Staff to Fuel a $10 Billion AI Gamble

Do Son April 2, 2026 0

Oracle has initiated its largest layoff in history, cutting up to 30,000 jobs to pivot $10B toward AI infrastructure amid a 50% stock decline and rising debt.

The Infinite Loop: Microsoft Retracts Broken Windows 11 Update KB5079391 Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The Infinite Loop: Microsoft Retracts Broken Windows 11 Update KB5079391

Do Son April 2, 2026 0

Microsoft has pulled the broken KB5079391 update after it caused infinite installation loops. Learn how the new KB5086672 fix resolves error 0x80073712.

The DarkSword Threat: Apple Issues Emergency iOS 18.7.7 Patch for Legacy iPhones DarkSword exploit kit iOS 18.7.7 security update CVE-2024-44308 & CVE-2024-44309 Apple appeal, Epic Games lawsuit
  • Vulnerability Report

The DarkSword Threat: Apple Issues Emergency iOS 18.7.7 Patch for Legacy iPhones

Do Son April 2, 2026 0

Apple releases iOS 18.7.7 to combat the "DarkSword" exploit kit. Protect your legacy iPhone or iPad from this state-level threat by updating today.

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia UNC5221 HAFNIUM Extradition PRC State Espionage
  • Cyber Security
  • Malware

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

Do Son April 2, 2026 0

Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Critical 9.2 Severity Flaw in Gigabyte Control Center Exposed Gigabyte Control Center CVE-2026-4415
  • Vulnerability Report

Critical 9.2 Severity Flaw in Gigabyte Control Center Exposed

Do Son April 2, 2026 0

Gigabyte Control Center faces a critical 9.2 severity flaw (CVE-2026-4415). Unauthenticated attackers can write files and execute code—update to 25.12.10.01 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.