Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
ResokerRAT Uses Telegram to Hijack Your PC and Disable Your Security Keys GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Malware

ResokerRAT Uses Telegram to Hijack Your PC and Disable Your Security Keys

Do Son April 6, 2026 0

Researchers unmask ResokerRAT, a stealthy Trojan using Telegram to spy on systems and block security tools like Task Manager. Is your PC calling home?
The Python Predator: PXA Stealer Surges 10% as it Targets Global Finance and Crypto in 2026 PXA Stealer Surge Q1 2026 Malware Trends
  • Malware

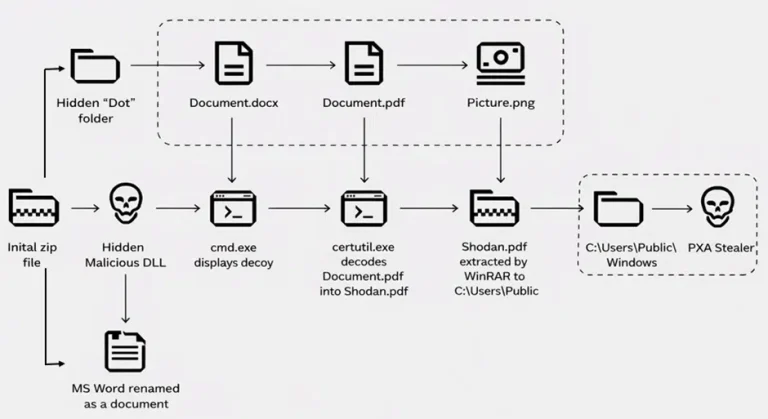
The Python Predator: PXA Stealer Surges 10% as it Targets Global Finance and Crypto in 2026

Do Son April 6, 2026 0

PXA Stealer activity surges in Q1 2026, targeting global finance. Learn how this Python-based malware uses Telegram and LOLBins to hijack crypto and banking data.

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 30 – April 5, 2026) Vulnerability Digest Zero-Day Exploits Seedworm APT Dindoor Backdoor RedKitten Campaign AI-Generated Malware WSUS RCE ShadowPad CVE-2025-59287
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (March 30 – April 5, 2026)

Do Son April 6, 2026 0

1,361 vulnerabilities found this week: 129 are critical. Prioritize Chrome’s Dawn exploit, FortiClient EMS, and new AI pipeline attacks. Get the full list.

The $17 Million Bounty: Google Smashes Records and Launches AI Frontier for 15th VRP Anniversary Google VRP 2025 Bug Bounty Records
  • Vulnerability Report

The $17 Million Bounty: Google Smashes Records and Launches AI Frontier for 15th VRP Anniversary

Do Son April 5, 2026 0

Google’s 2025 VRP hit an all-time high with $17.1M in payouts. Discover how the new AI VRP and elite bugSWAT events are shaping the future of security.

Zero Authentication, Total Control: Critical CVSS 10 Flaw Uncovered in Dgraph Database Dgraph Vulnerability CVSS 10.0 Dgraph Admin Leak CVE-2026-40173
  • Vulnerability Report

Zero Authentication, Total Control: Critical CVSS 10 Flaw Uncovered in Dgraph Database

Do Son April 5, 2026 2

Dgraph patches a critical 10.0 CVSS flaw (CVE-2026-33976). Unauthenticated attackers can overwrite databases and read local files. Update to v25.3.1 now!

Hackers are Using “Legit” IT Tools to Hijack the 2026 Tax Season 2026 Tax Phishing RMM Abuse
  • Cybercriminals

Hackers are Using “Legit” IT Tools to Hijack the 2026 Tax Season

Do Son April 5, 2026 0

Proofpoint identifies a surge in 2026 tax scams using RMM tools (39%) to bypass security. Learn how TA4922 and TA2730 target your data this filing season.

Under Active Attack: Critical 9.1 CVSS FortiClient EMS Flaw Exploited in the Wild Knowledge Deliver RCE vulnerability FortiClient EMS Vulnerability CVE-2026-35616 Cisco SD-WAN Vulnerability CVE-2026-20122 PCPcat, Next.js RCE Salesloft breach, Salesforce CRM WIREFIRE web shell
  • Vulnerability Report

Under Active Attack: Critical 9.1 CVSS FortiClient EMS Flaw Exploited in the Wild

Do Son April 4, 2026 0

Fortinet warns CVE-2026-35616 (CVSS 9.1) in FortiClient EMS is being exploited in the wild. Unauthenticated RCE risk—apply emergency hotfixes immediately!

Apache Traffic Server Patches “Double-Header” DoS and Request Smuggling Flaws Apache Traffic Server Vulnerabilities CVE-2024-56195 and CVE-2024-56196
  • Vulnerability Report

Apache Traffic Server Patches “Double-Header” DoS and Request Smuggling Flaws

Do Son April 3, 2026 0

Apache Traffic Server fixes two CVSS 7.5 flaws (CVE-2025-58136 & CVE-2025-65114). Prevent DoS and request smuggling—update to 10.1.2 or 9.2.13 now!
Password Hijack in the Modern Stack: Payload CMS Patches Critical 9.1 CVSS Reset Flaw Payload CMS Vulnerability CVE-2026-34751
  • Vulnerability Report

Password Hijack in the Modern Stack: Payload CMS Patches Critical 9.1 CVSS Reset Flaw

Do Son April 3, 2026 0

Payload CMS fixes a critical 9.1 CVSS flaw (CVE-2026-34751) in its password reset flow. Attackers could hijack accounts. Update to v3.79.1 immediately!

CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control Juju Orchestration Cloud Credential Theft Juju Orchestration Vulnerability CVE-2026-4370
  • Vulnerability Report

CVE-2026-4370 (CVSS 10): Critical Juju Flaw Grants Attackers Total Infrastructure Control

Do Son April 3, 2026 0

Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops libinput Sandbox Escape CVE-2026-35093
  • Vulnerability Report

Breaking the Input: Sandbox Escape Hits libinput, Exposing Leading Linux Desktops

Do Son April 3, 2026 0

Critical 8.8 CVSS flaw in libinput allows sandbox escape via malicious Lua plugins. Affects GNOME, KDE, and Fedora. Update to 1.31.1 or 1.30.3 now!
The MuPDF Vulnerability Turning “Safe” PDFs into System Hijackers MuPDF RCE Integer Overflow
  • Vulnerability Report

The MuPDF Vulnerability Turning “Safe” PDFs into System Hijackers

Do Son April 3, 2026 0

Artifex MuPDF faces a 7.8 CVSS integer overflow (CVE-2026-3308) allowing RCE via "crafted" PDFs. With no official patch, sandboxing is vital. Update now.

The Hidden Costs of Managing Too Many Security Tools bc257a04-d077-46b7-a6bc-3011efc3ac3f
  • Technique

The Hidden Costs of Managing Too Many Security Tools

Do Son April 3, 2026 0
Security tool sprawl rarely starts as a strategy. It starts as a quick fix. A team adds...
Read More Read more about The Hidden Costs of Managing Too Many Security Tools
The EU’s AWS “Master Key”: How a Compromised Trivy Update Leaked 340GB of Data Apple Google EU alliance DMA European Commission Breach Trivy Supply Chain Attack Europa.eu Breach EU Cloud Infrastructure EU Cyber Sanctions State-Sponsored Hacking EU 2040 Emissions Target, Europe Climate Leadership AWS Azure DMA Cloud Gatekeeper DSA violation, illegal content Apple DMA Delay, iPhone Mirroring EU EU Age Verification, Google Play Integrity Corning Antitrust, EU Competition Apple EU Digital Markets Act App Store commission European Union cyberattacks - InvestAI EU Targets Musk’s X Digital Markets Act, EU fines
  • Data Leak

The EU’s AWS “Master Key”: How a Compromised Trivy Update Leaked 340GB of Data

Do Son April 3, 2026 0

A massive supply-chain attack hit the European Commission via a compromised Trivy update. 340GB of data was leaked by ShinyHunters. Rotate your AWS keys!

The WordPress Killer? Cloudflare Unveils EmDash, the AI-Native CMS Built for the Serverless Epoch Cloudflare EmDash CMS
  • Technology

The WordPress Killer? Cloudflare Unveils EmDash, the AI-Native CMS Built for the Serverless Epoch

Do Son April 3, 2026 0

Cloudflare debuts EmDash, an AI-native, serverless CMS built on Astro 6.0. Say goodbye to WordPress plugin hacks with V8 isolate sandboxing and passkey security.

OpenSSH 10.3 Patches Command Execution and “scp” Privilege Escalation OpenSSH 10.3 Patch SSH Command Injection CVE-2023-38408 OpenSSH Vulnerability CVE-2026-3497
  • Vulnerability Report

OpenSSH 10.3 Patches Command Execution and “scp” Privilege Escalation

Do Son April 3, 2026 0

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.

The Resurrection of the Beam: Google Challenges AirDrop with Android 17’s “Tap to Share” Android 17 Tap to Share Gemini Scam Detection Galaxy S26 AI Security
  • Android

The Resurrection of the Beam: Google Challenges AirDrop with Android 17’s “Tap to Share”

Do Son April 3, 2026 0

Google’s "Tap to Share" leaked for Android 17! Using NFC and UWB, this new Quick Share feature aims to end AirDrop's dominance. Discover how it works.
Inside the Rapid Evolution of the BlankGrabber Stealer BlankGrabber Stealer Python Malware Analysis
  • Malware

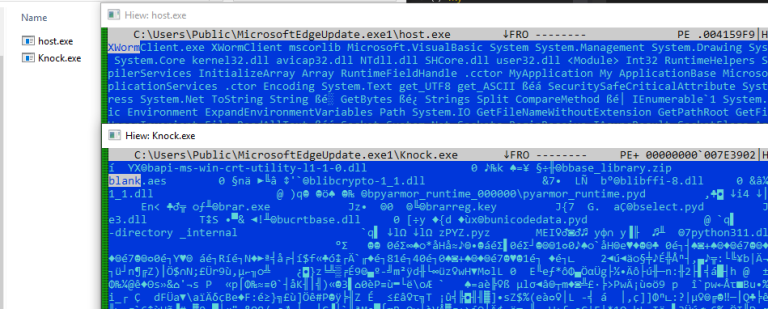
Inside the Rapid Evolution of the BlankGrabber Stealer

Do Son April 3, 2026 0

Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.

The Apache 2.0 Revolution: Google’s Gemma 4 Shatters the Open-Source Intelligence Ceiling Google Gemma 4 release
  • Technology

The Apache 2.0 Revolution: Google’s Gemma 4 Shatters the Open-Source Intelligence Ceiling

Do Son April 3, 2026 0

Google releases Gemma 4 under the Apache 2.0 license. Featuring multimodal edge models and a 31B "Dense" system, it redefines AI digital sovereignty for 2026.

The Lobster Craze: How OpenClaw is Triggering a High-Stakes AI Agent Arms Race in China Apple OpenClaw competitor Apple AI agent, Siri agentic capabilities, Apple computer-use agent OpenClaw Lobster
  • Technology

The Lobster Craze: How OpenClaw is Triggering a High-Stakes AI Agent Arms Race in China

Do Son April 3, 2026 0

ByteDance and OpenAI are racing to dominate "Lobster Husbandry." Discover how the OpenClaw agent is transforming WeChat, Xiaomi, and the global AI landscape.

Microsoft’s Declaration of Independence: The New MAI Models Challenging OpenAI and Google Microsoft MAI models
  • Technology

Microsoft’s Declaration of Independence: The New MAI Models Challenging OpenAI and Google

Do Son April 3, 2026 0

Microsoft CEO Mustafa Suleyman unveils MAI-Transcribe-1, MAI-Voice-1, and MAI-Image-2—proprietary AI built to undercut competitors and secure self-sufficiency.

Apple Severs All Payment Processing in Russia Following Government Mandates Apple Russia payment suspension iOS 26.3 Proximity Pairing, Apple DMA compliance 2026 Tap to Pay, Apple Pay Wireless charging Always-On Display, iOS 26 iOS 26, EU App APIs Rare Earths, Apple Supply Chain
  • Technology

Apple Severs All Payment Processing in Russia Following Government Mandates

Do Son April 3, 2026 0

Apple officially ceases all payment services in Russia as of April 1, 2026. Subscriptions, App Store buys, and iCloud+ renewals are now indefinitely frozen.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.