
 Do Son
Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.
Elastic Security Labs unmasks REF1695, a threat actor using the CNB Bot and custom XMRig loaders for Monero mining and CPA fraud. Is your server a silent miner?

Microsoft Edge 147 Beta is testing a new "Auto-Startup" feature that launches the browser on boot without asking. Learn how to disable this 2026 update.

Windows 11 24H2 support ends October 13, 2026. Microsoft is preparing mandatory updates to version 25H2 for Home and Pro users to ensure continued security.

Microsoft Defender warns of a 2026 WhatsApp malware campaign using VBS and renamed system tools to hijack PCs via AWS and Tencent Cloud. Stay alert!

Microsoft introduces native "Feature Flags" in Windows 11 Dev Build 26300. Unlock hidden experimental features safely without needing third-party tools like ViveTool.

Apple makes a "last stand" at the Supreme Court over App Store fees, while Epic Games strikes a silent truce with Google to focus on its greatest adversary.
Software engineer vacancies have surged 30% in 2026. Discover how "vibe coding" and AI-generated technical debt are creating a massive new demand for human devs.
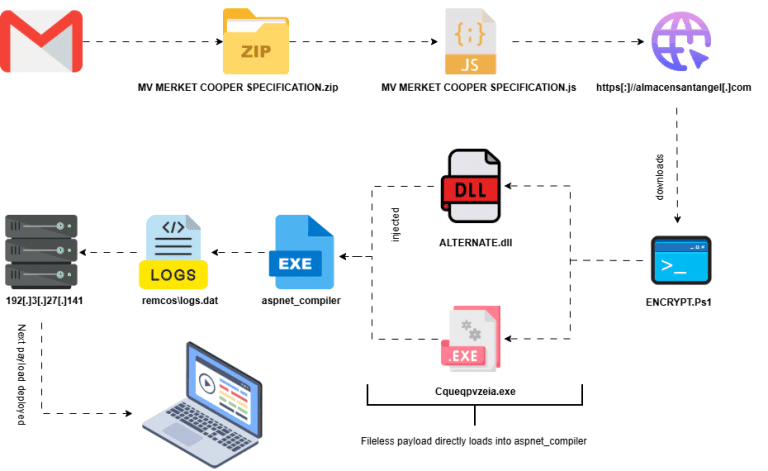
Researchers unmask a fileless Remcos RAT campaign using obfuscated JS and LOLBins to hijack systems in-memory. See the technical breakdown from Lat61.
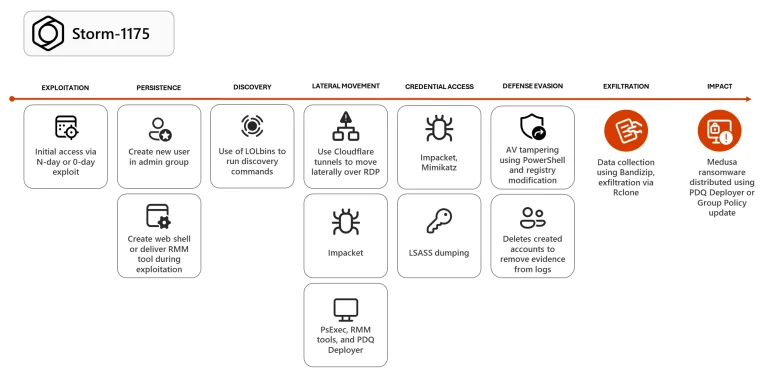
Microsoft exposes Storm-1175: a high-speed threat actor deploying Medusa ransomware in under 24 hours via zero-day exploits. Learn how to stop the blitz.

A critical 9.8 CVSS flaw in Ninja Forms - File Upload plugin allows unauthenticated RCE. 50,000+ WordPress sites are at risk. Update to v3.3.27 now!

Keycloak 26.5.7 fixes an MFA bypass that could let attackers skip two-factor checks. Upgrade your identity server to close the gap.

CVE-2026-34838: A critical 10.0 flaw in GroupOffice allows authenticated users to trigger RCE via insecure deserialization. Update to v26.0.12 immediately!
CERT@VDE warns of critical RCE and SQLi flaws in MB Connect Line's mbCONNECT24 (up to v2.19.4). Unauthenticated attackers can gain full system control. Patch now!

CVE-2026-34950: A critical 9.1 CVSS flaw in fast-jwt allows authentication bypass via leading whitespace. Learn how a regex error leads to algorithm confusion.

Google Chrome 148 introduces native "Lazy Loading" for video and audio tags. Save bandwidth and boost loading speeds with this essential 2026 web update.

Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.

Unit 42 reveals how GCP Vertex AI agents can become "double agents," exfiltrating data and accessing Google’s internal code. Learn why BYOSA is essential.

Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.

Operation DualScript uses parallel execution to bypass defenses, hijacking crypto wallets and banking data via RetroRAT and clipboard swapping.

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?