
 Do Son
Attackers are impersonating Linux leaders on Slack to drop malware via fake Google Workspace links. Protect your dev environment—verify before acting!

OpenSSL's April 2026 advisory reveals 7 flaws, including a moderate RSA memory leak (CVE-2026-31790). Learn if your version is affected and how to patch.

NCSC unmasks APT28’s "digital funnel" using router DNS hijacking to steal OAuth tokens and passwords. Protect your remote workforce—patch your routers now.
Venom Stealer is a new C++ MaaS targeting crypto wallets like Tonkeeper. It features silent UAC elevation and Chrome encryption bypass. Learn how to defend.
North Korea’s "Contagious Interview" campaign expands to 1,700+ malicious packages across npm, PyPI, and more. Learn how to protect your dev environment.
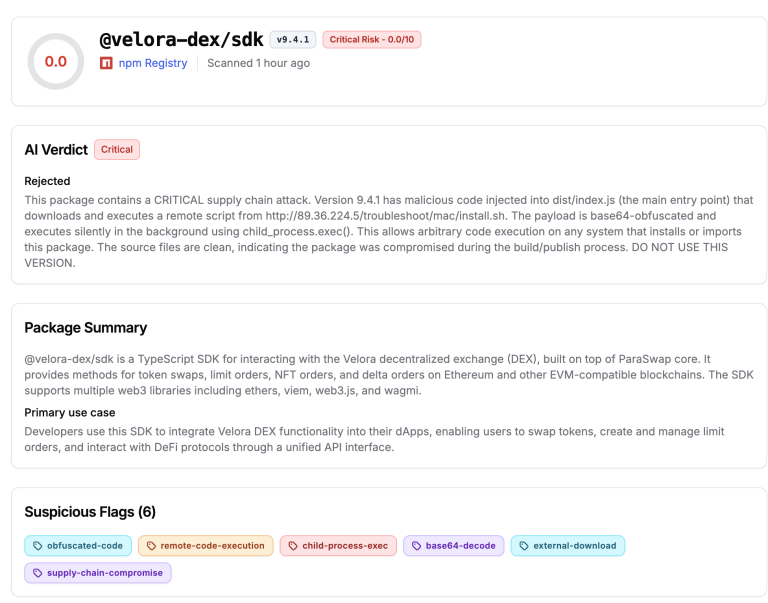
A malicious update to @velora-dex/sdk (v9.4.1) drops a stealthy macOS backdoor on import. Learn how to detect the zsh.profiler infection and rotate secrets.
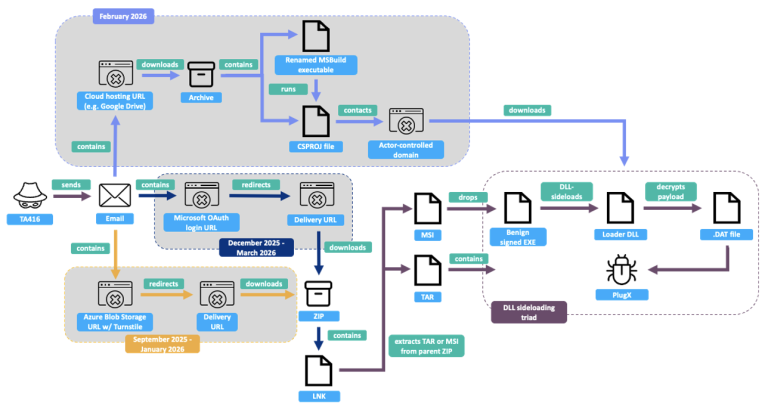
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.
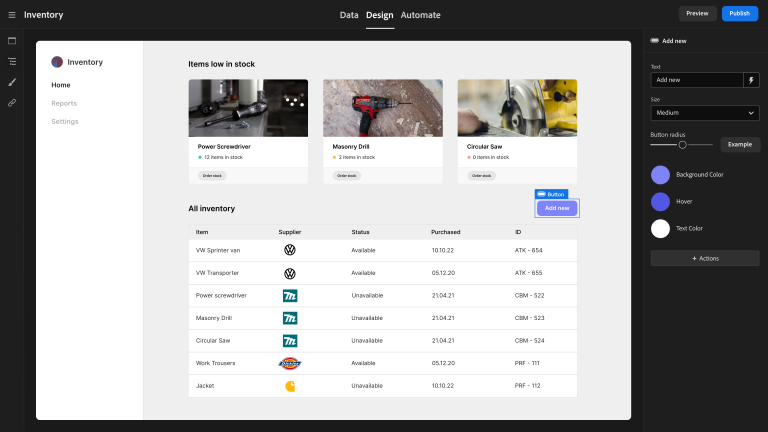
Critical 9.6 CVSS flaws in Budibase allow unauthenticated RCE and data exfiltration via SSRF. Secure your internal tools—update to v3.33.4 now.

CVE-2026-34612: A critical 10.0 flaw in Kestra allows RCE via SQL injection in label searches. Protect your orchestration server—update to v1.3.7 now!

A critical 9.8 CVSS flaw in Convoy (CVE-2026-33746) allows unauthenticated admin access via forged JWTs. Update to v4.5.1 immediately to secure your KVM.

Electron patches 5 flaws (CVSS 7.0-8.4) allowing sandbox escapes and context isolation bypass. Update to v41, 40, or 39 to secure your desktop app now.
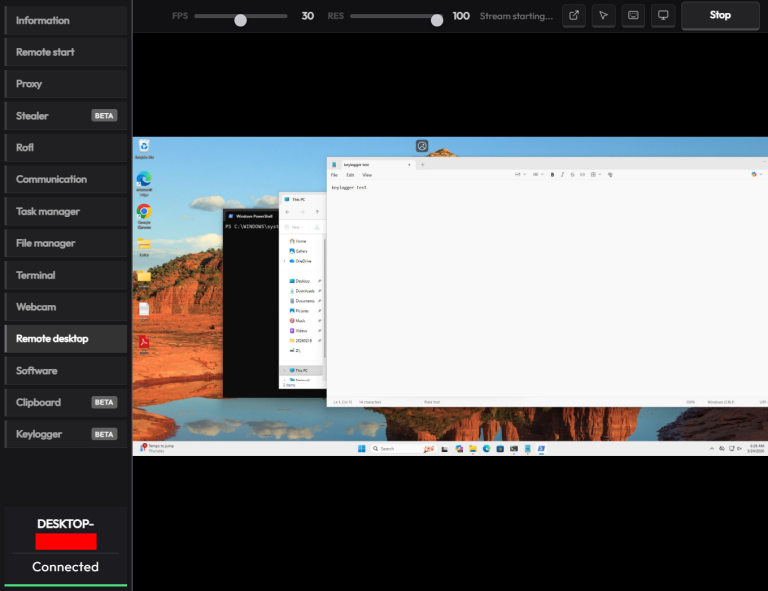
Kaspersky uncovers CrystalX RAT, a malicious MaaS on Telegram that pairs data theft with "prankware" to troll victims and lock systems. Patch now!

BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

Adobe is bypassing Chrome security by quietly editing your hosts file to track Creative Cloud installations. Learn how this stealth telemetry works in 2026.

ThreatLabz unmasks Xloader 8.7, the evolved successor to Formbook. Learn how its advanced obfuscation and decoy C2s bypass modern security defenses.

GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.
After 35 years of support, the Linux Kernel is officially retiring the Intel i486. Linux 7.1 marks the beginning of the end for this ancestral CPU lineage.
The Browser Choice Alliance, including Chrome and Vivaldi, condemns Microsoft’s new Edge auto-startup as "predatory proselytization." Is Edge a Gatekeeper?
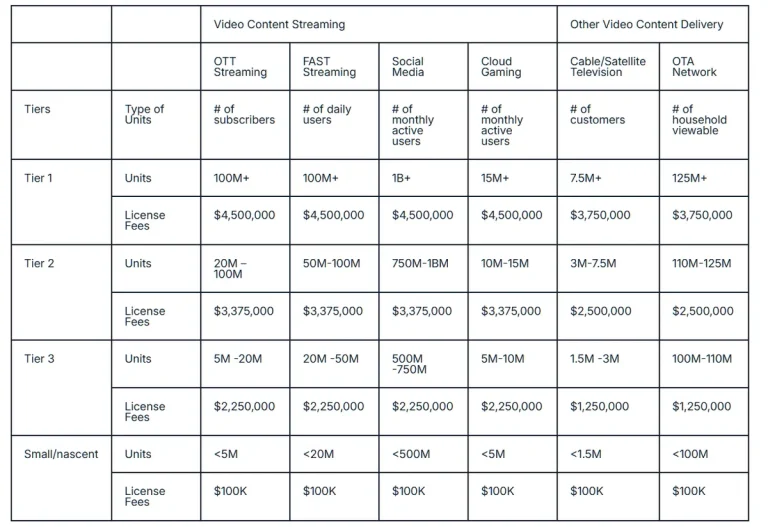
Via LA quietly replaces the $100k H.264 annual cap with a tiered system up to $4.5M. Discover how this 2026 patent pool shift impacts global streaming giants.

McAfee unmasks Operation NoVoice: a sophisticated Android rootkit that survives factory resets to clone WhatsApp sessions and seize full device control.

Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.