Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
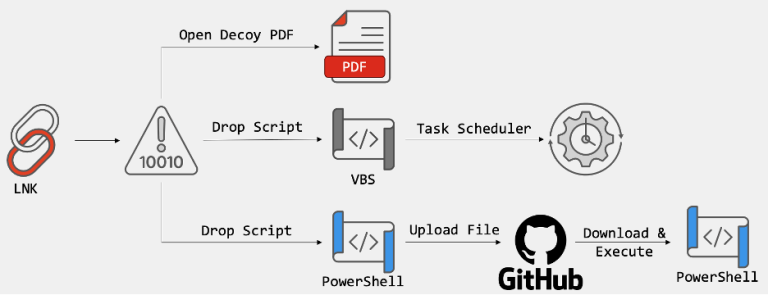
New Phishing Campaign Abuses GitHub to Target South Korea GitHub C2 LNK Malware
  • Cybercriminals

New Phishing Campaign Abuses GitHub to Target South Korea

Do Son April 9, 2026 0

FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.
The $86,000 Patch: Chrome 147 Crushes “Critical” WebML Memory Flaws Chrome 147 Security WebML Vulnerabilities
  • Vulnerability Report

The $86,000 Patch: Chrome 147 Crushes “Critical” WebML Memory Flaws

Do Son April 9, 2026 0

Google Chrome 147 is out with critical security fixes for WebML and V8. Protect your browser from overflows and memory leaks—update to version 147 now!

CISA Warning: Critical Ivanti EPMM Code Injection Vulnerability Under Active Attack Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability Report

CISA Warning: Critical Ivanti EPMM Code Injection Vulnerability Under Active Attack

Do Son April 9, 2026 0

CISA adds critical Ivanti EPMM flaw (CVE-2026-1340) to KEV catalog. The 9.8 CVSS code injection allows unauthenticated RCE. Patch mandated by April 11!
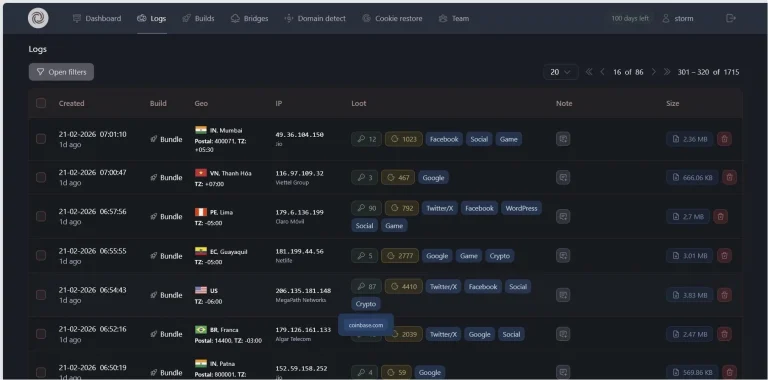
Storm: 2026’s Newest Infostealer Bypasses Chrome to Hijack Your MFA Sessions Storm Infostealer Session Cookie Theft
  • Malware

Storm: 2026’s Newest Infostealer Bypasses Chrome to Hijack Your MFA Sessions

Do Son April 9, 2026 0

Storm malware bypasses Chrome security by shipping encrypted files for server-side decryption. Learn how it steals session cookies to defeat MFA in 2026.
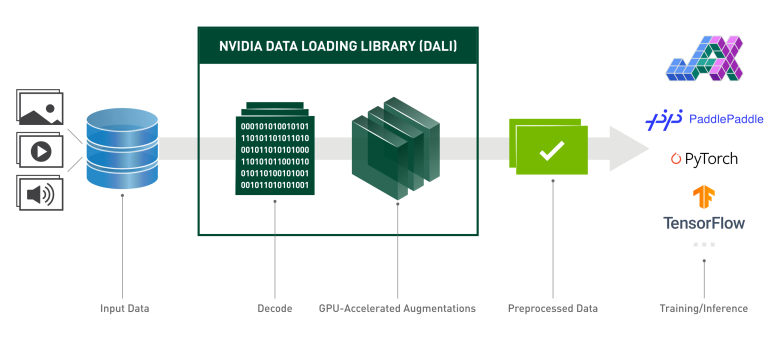
High-Severity Patches: NVIDIA Secures DALI and Triton Inference Server NVIDIA AI Security Deserialization Exploit
  • Vulnerability Report

High-Severity Patches: NVIDIA Secures DALI and Triton Inference Server

Do Son April 8, 2026 0

NVIDIA patches high-severity flaws in DALI and Triton Inference Server. Prevent arbitrary code execution and DoS—upgrade to DALI v2.0 and Triton r26.02 now.

Firecracker Security Alert: Virtio-PCI Vulnerability Could Lead to Out-of-Bounds Memory Access Firecracker Vulnerability Virtio-PCI OOB Write
  • Vulnerability Report

Firecracker Security Alert: Virtio-PCI Vulnerability Could Lead to Out-of-Bounds Memory Access

Do Son April 8, 2026 0

AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.
CVE-2026-34208 (CVSS 10): Critical Sandbox Escape Uncovered in SandboxJS SandboxJS Escape Host Object Poisoning SandboxJS Vulnerability CVE-2026-26954
  • Vulnerability Report

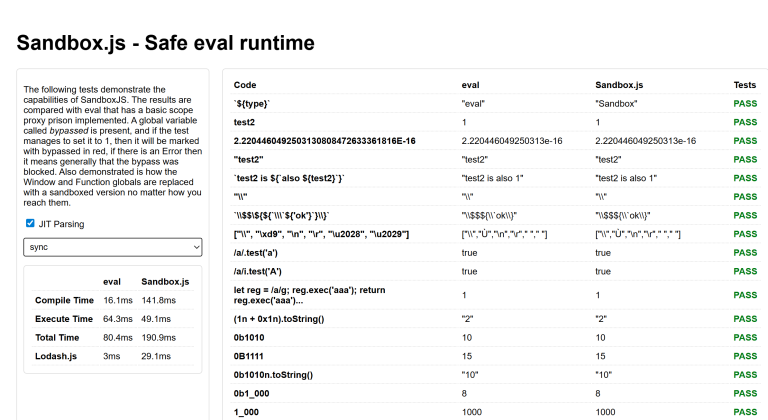
CVE-2026-34208 (CVSS 10): Critical Sandbox Escape Uncovered in SandboxJS

Do Son April 8, 2026 0

CVE-2026-34208: A critical 10.0 flaw in SandboxJS allows code to escape and poison host objects like Math.random. Secure your environment—update immediately!

Apache ActiveMQ Patches RCE and Path Traversal Flaws ActiveMQ RCE Jolokia Exploit ActiveMQ CVE-2025-27533 ActiveMQ Deserialization RCE, CVE-2025-54539
  • Vulnerability Report

Apache ActiveMQ Patches RCE and Path Traversal Flaws

Do Son April 8, 2026 0

Apache ActiveMQ patches a critical 2026 RCE flaw. Learn how CVE-2026-34197 uses Jolokia and Spring XML to hijack the JVM. Update to 5.19.5 or 6.2.3 now!

Critical Zero-Day: Unauthenticated RCE Exploited in Weaver E-cology 10.0 Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

Critical Zero-Day: Unauthenticated RCE Exploited in Weaver E-cology 10.0

Do Son April 8, 2026 0

Weaver E-cology 10.0 faces a critical 9.3 CVSS RCE (CVE-2026-22679). Unauthenticated attackers can hijack servers via a debug endpoint. Patch immediately!

Exploited in the Wild: Critical 9.3 CVSS Flaw Turns Tianxin Systems into Hacker Gateways PAN-OS Root RCE CL-STA-1132 Exploitation Tianxin RCE CVE-2021-4473 React Native Supply Chain Attack AstrOOnauta Malware Gladinet Zero-Day, LFI RCE Chain WordPress Theme, Account Takeover CVE-2024-50623 - European Space Agency cyberattack
  • Vulnerability Report

Exploited in the Wild: Critical 9.3 CVSS Flaw Turns Tianxin Systems into Hacker Gateways

Do Son April 8, 2026 0

Shadowserver warns of active exploitation of CVE-2021-4473 in Tianxin systems. This 9.3 CVSS flaw allows unauthenticated RCE. Patch your firmware immediately!

Team Cymru Mapped the Yurei Ransomware Toolkit Before It Could Strike Yurei Ransomware Open-Source Malware
  • Malware

Team Cymru Mapped the Yurei Ransomware Toolkit Before It Could Strike

Do Son April 8, 2026 0

Team Cymru unmasks Yurei ransomware, a "Stranger Things" themed operation built on open-source code. Learn how proactive telemetry mapped their toolkit.

Zero-Day Alert: Sophisticated PDF Exploit Targets Adobe Reader for Massive Data Theft Adobe Reader Zero-Day PDF Exploit
  • Vulnerability Report

Zero-Day Alert: Sophisticated PDF Exploit Targets Adobe Reader for Massive Data Theft

Do Son April 8, 2026 0

A critical Adobe Reader zero-day allows attackers to steal local files and achieve system control via malicious PDFs. Learn how the unpatched exploit works.
Phorpiex’s New P2P Upgrade Makes This 15-Year-Old Botnet Unstoppable Phorpiex Botnet P2P Malware Resilience
  • Malware

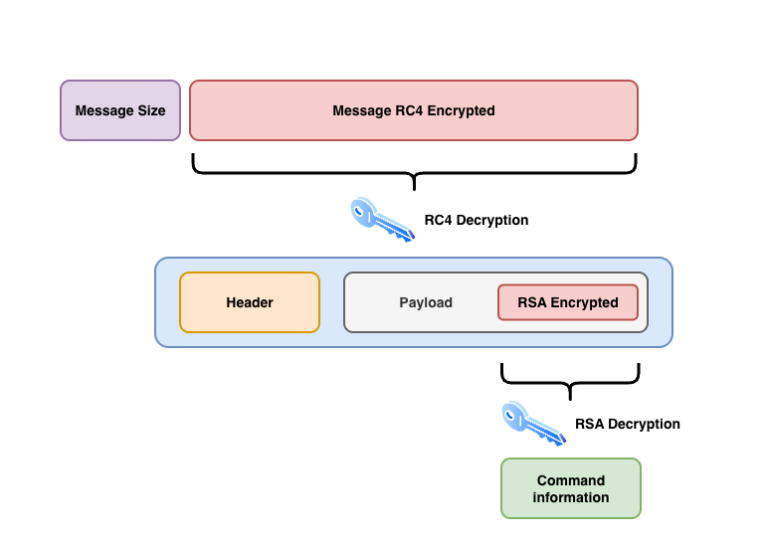
Phorpiex’s New P2P Upgrade Makes This 15-Year-Old Botnet Unstoppable

Do Son April 8, 2026 0

Bitsight unmasks the Phorpiex "Twizt" variant: a self-healing P2P botnet with RSA-encrypted payloads and LFI scanners. See how this 2011 threat stays relevant.
Russian Military Hackers Hijack Thousands of Home Routers for Global Espionage Forest Blizzard DNS Hijacking
  • Cybercriminals

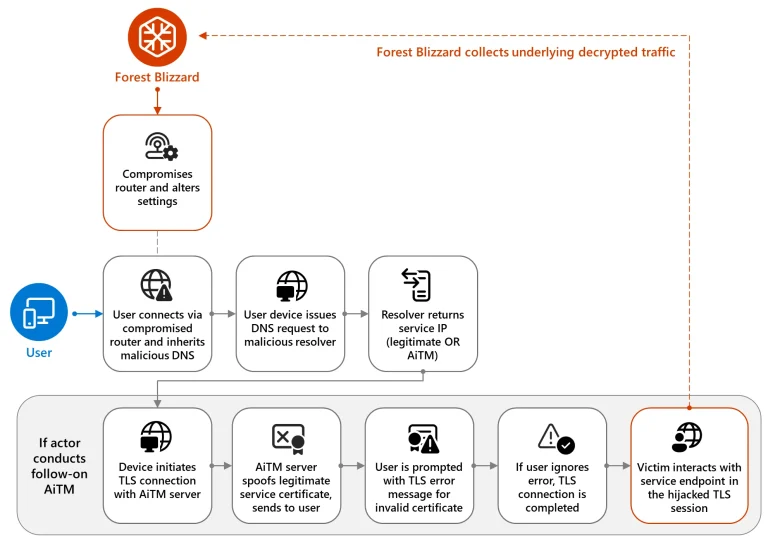
Russian Military Hackers Hijack Thousands of Home Routers for Global Espionage

Do Son April 8, 2026 0

Microsoft exposes Forest Blizzard’s hijacking of 5,000+ SOHO routers for DNS spying and AiTM attacks on Microsoft 365 and governments. Patch your router now!

North Korean State Actors Linked to Massive $285 Million Drift Protocol Heist Drift Protocol Solana DeFi Hack
  • Cybercriminals

North Korean State Actors Linked to Massive $285 Million Drift Protocol Heist

Do Son April 8, 2026 0

Attackers drained $285M from Drift Protocol in just 12 minutes using a fake token and pre-signed transactions. Learn how the 2026 DeFi heist went down.

Critical Security Update: IBM Patches Multiple Vulnerabilities in Verify Identity and Access IBM Verify Root Escalation
  • Vulnerability Report

Critical Security Update: IBM Patches Multiple Vulnerabilities in Verify Identity and Access

Do Son April 8, 2026 0

IBM patches critical flaws in Verify Identity Access, including a 9.3 CVSS root escalation and 8.1 auth bypass. Secure your identity gateway—update now!

The Python Pivot: Kimsuky’s New Multi-Stage LNK Maze for Stealthy Backdoors Kimsuky Multi-stage LNK
  • Malware

The Python Pivot: Kimsuky’s New Multi-Stage LNK Maze for Stealthy Backdoors

Do Son April 8, 2026 0

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.

Critical Alert: Iranian-Affiliated Actors Target U.S. Infrastructure via Industrial Control Systems Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Critical Alert: Iranian-Affiliated Actors Target U.S. Infrastructure via Industrial Control Systems

Do Son April 8, 2026 0

FBI and CISA warn of Iranian APTs hijacking internet-facing PLCs to disrupt U.S. energy and water systems. Learn the 2026 TTPs and how to defend your OT.

The AI Collective: Telegram Unlocks Autonomous “Bot-to-Bot” Dialogue for Multi-Agent Workflows Telegram Bot-to-Bot communication
  • Technology

The AI Collective: Telegram Unlocks Autonomous “Bot-to-Bot” Dialogue for Multi-Agent Workflows

Do Son April 8, 2026 0

Telegram’s new "Bot-to-Bot" mode allows AI agents to talk to each other. Automate complex tasks by pairing "executor" and "overseer" bots in a single chat.

The “Entertainment Only” Paradox: Why Microsoft’s Copilot Legal Terms Just Ignited a Viral Controversy Microsoft Copilot Terms of Service Satya Nadella SN Scratchpad, Microsoft Microslop backlash
  • Technology

The “Entertainment Only” Paradox: Why Microsoft’s Copilot Legal Terms Just Ignited a Viral Controversy

Do Son April 8, 2026 0

Microsoft faces backlash over Copilot terms labeling the AI as "entertainment only." Discover why this legacy clause contradicts its 2026 marketing narrative.

The Cloud-Only Safety Net: Microsoft to Bypass Local Recycle Bins in Major OneDrive Overhaul OneDrive cloud deletion 2026 OneDrive Facial Recognition, Three-Time Limit OneDrive Suspension, Data Loss
  • Technology

The Cloud-Only Safety Net: Microsoft to Bypass Local Recycle Bins in Major OneDrive Overhaul

Do Son April 8, 2026 0

Starting May 2026, OneDrive cloud deletions will no longer land in your local Recycle Bin. Learn how this mandatory update changes file recovery forever.

AI Against AI: Anthropic Unveils “Project Glasswing” to Stop the Next Great Cyber War Anthropic Project Glasswing
  • Technology

AI Against AI: Anthropic Unveils “Project Glasswing” to Stop the Next Great Cyber War

Do Son April 8, 2026 0

Anthropic launches Project Glasswing, using the unreleased "Claude Mythos" model to find thousands of zero-days and defend global infrastructure from AI threats.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.