 Do Son
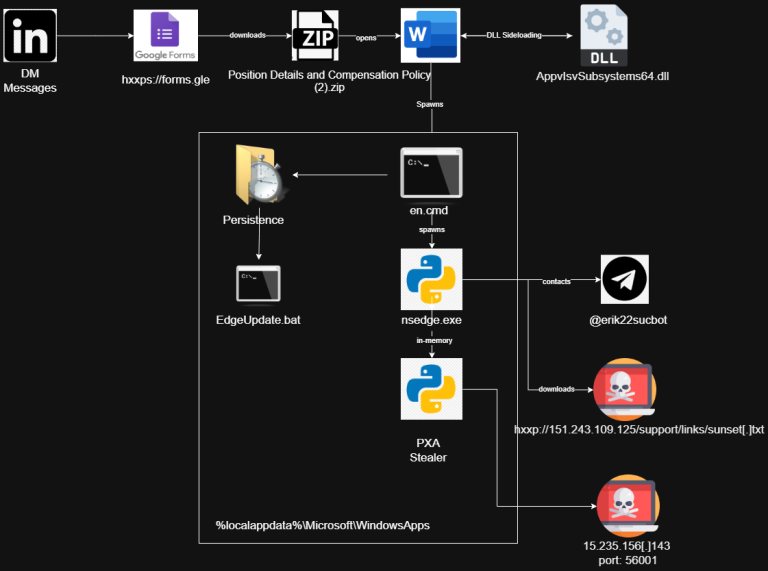
LinkedIn job seekers are being targeted by a sophisticated Vietnam-based group using PXA Stealer. This 100MB malware bypasses MFA and drains crypto wallets.
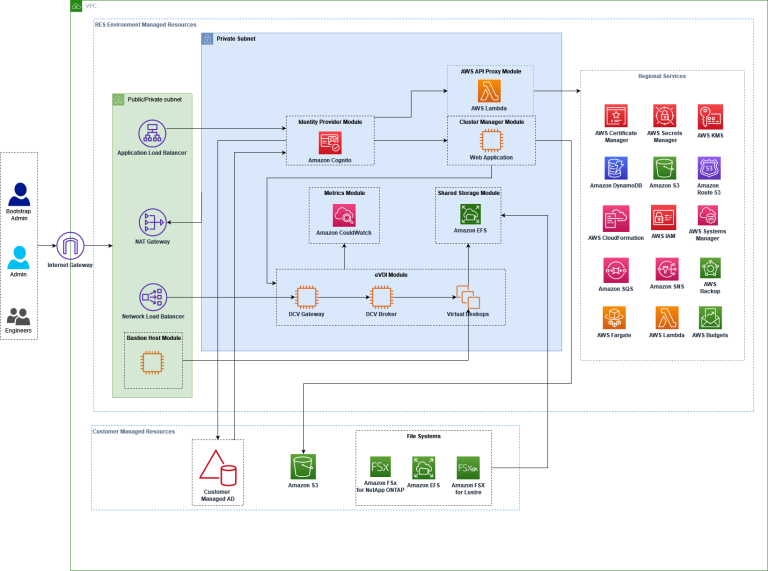
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.
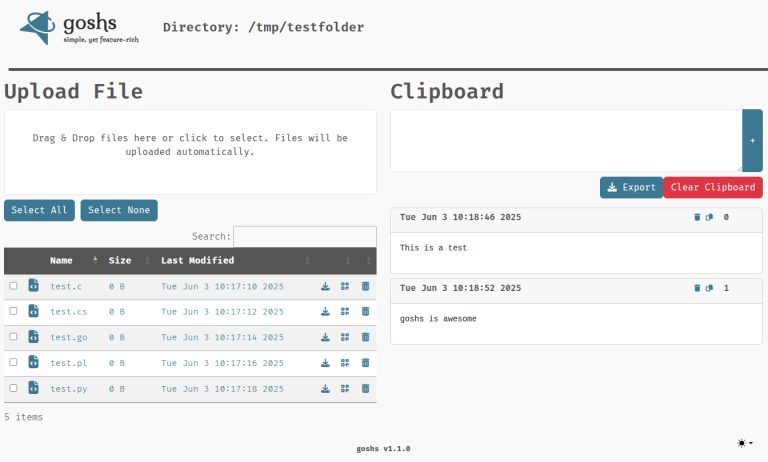
Critical 9.8 flaws in goshs v2.0.0-beta.2 allow unauthenticated attackers to write or delete any file on your system. Update to v2.0.0-beta.3 immediately!

Juniper warns of a critical 9.8 CVSS flaw in JSI vLWC. A default password allows unauthenticated attackers to take full device control. Update to 3.0.94 now!
Everest Forms patches a critical 9.8 CVSS PHP Object Injection vulnerability affecting 100,000+ sites. Update to v3.4.4 now to prevent full site takeover!

 cybernewswire
Austin, Texas, United States, 9th April 2026, CyberNewswire
Vite patches critical flaws (CVE-2026-39364 & CVE-2026-39363) allowing arbitrary file reads and .env leaks via WebSockets and query params. Upgrade to 8.0.5!

Mitel patches a critical 9.8 CVSS SQL injection in MiCollab. Learn how this unauthenticated flaw chains to full system takeover. Upgrade to v10.2 SP1 now!

React patches a 7.5 CVSS DoS vulnerability in Server Components (CVE-2026-23869). Stop CPU exhaustion attacks—update your 19.x dependencies now!

Critical 9.3 CVSS flaw (CVE-2026-34078) in Flatpak allows apps to escape sandboxes and access all host files. Secure your Linux system—update to v1.16.4 now!
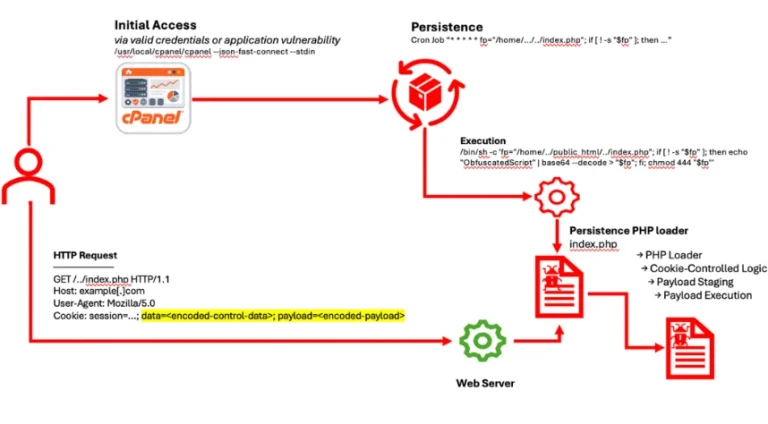
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.

A developer's "human error" leaked sensitive GitHub tokens in an Apache HTTP Server update. Learn how GitHub's safety nets prevented a major security breach.

Microsoft’s Windows 11 Health Dashboard is officially clear of bugs—for now. Discover the latest fixes and why a mandatory 25H2 update is coming this October.
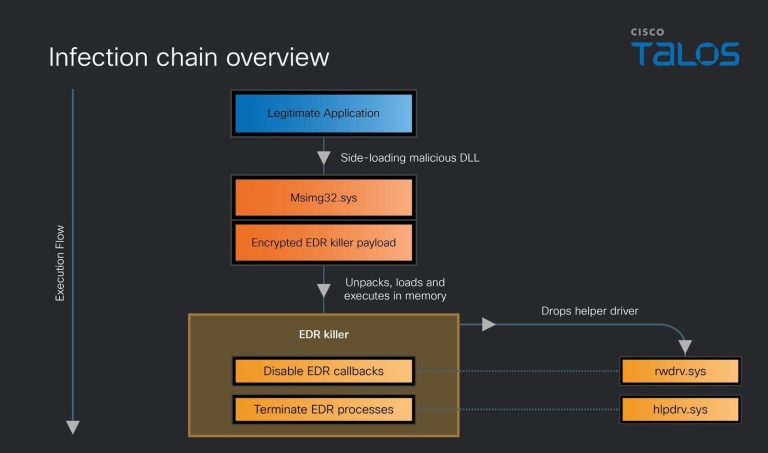
Cisco Talos unmasks a Qilin ransomware payload that terminates 300+ EDR drivers and manipulates the Windows kernel. See how this "EDR Killer" stays invisible.

Mandiant uncovers BRICKSTORM, a threat actor hiding in VMware vSphere for 393 days. Learn how to close the visibility gap and harden your ESXi infrastructure.

Microsoft’s sudden suspension of VeraCrypt and WireGuard accounts reveals the dangers of automated bureaucracy in the critical path of security software.

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!

Palo Alto Networks patches critical flaws in Cortex XDR and ADEM, including a SYSTEM-level privilege escalation. Secure your security tools—patch today!

Microsoft has suspended VeraCrypt’s developer account, blocking critical driver signatures. Without a fix, future Windows updates and system boots are at risk.

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!

SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!
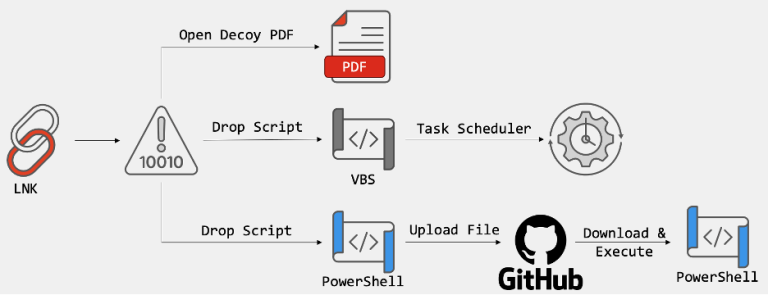
FortiGuard Labs unmasks a South Korean espionage wave abusing the GitHub API for C2 and using LNK files to stay invisible. Protect your network from LotL.