Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features Windows Insider Program Structural Changes
  • Windows

Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features

Do Son April 13, 2026 0

Microsoft simplifies the Windows Insider Program! Discover the new Experimental Channel, native Feature Flags, and data-safe "in-place upgrades."

The Great Gallic Exodus: Inside France’s Bold Mission to Ditch Microsoft for Linux French Digital Sovereignty Greg Kroah-Hartman AI code review CVE-2025-38352 Linux kernel exploit, Android 32-bit UAF vulnerability CVE-2022-36946 Linux Kernel 6.16, Hardware Support
  • Linux

The Great Gallic Exodus: Inside France’s Bold Mission to Ditch Microsoft for Linux

Do Son April 13, 2026 0

France is severing ties with US tech giants. Discover the "La Suite" initiative and the mandate to move 80,000+ state employees from Windows to Linux by 2027.

The Script Editor Shift: How ClickFix Evades macOS 26.4 Security to Deliver Atomic Stealer ClickFix macOS Script Editor Attack
  • Malware

The Script Editor Shift: How ClickFix Evades macOS 26.4 Security to Deliver Atomic Stealer

Do Son April 13, 2026 0

Jamf identifies a macOS ClickFix pivot: attackers now use the Script Editor to bypass Terminal scans and deliver Atomic Stealer. Learn how to stay protected.

LucidRook: Sophisticated Spear-Phishing Campaign Targets Taiwan with Custom Malware Stack LucidRook Malware Taiwan Cyber Attack
  • Cybercriminals
  • Malware

LucidRook: Sophisticated Spear-Phishing Campaign Targets Taiwan with Custom Malware Stack

Do Son April 13, 2026 0

Cisco Talos reveals UAT-10362’s "Lucid" malware family targeting Taiwan. Using Lua, Rust, and regional locks, this threat prioritizes extreme stealth.

Supply Chain Alert: Critical 9.4 CVSS RCE Hits Sonatype Nexus Repository Manager Nexus Repository RCE Supply Chain Security Nexus Repository Manager - CVE-2024-5082 & CVE-2024-5083
  • Vulnerability

Supply Chain Alert: Critical 9.4 CVSS RCE Hits Sonatype Nexus Repository Manager

Do Son April 13, 2026 0

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!
Under 10 Hours: The marimo Terminal RCE Exploited in a Record-Breaking AI Sprint marimo Terminal RCE AI-Assisted Exploitation
  • Vulnerability Report

Under 10 Hours: The marimo Terminal RCE Exploited in a Record-Breaking AI Sprint

Do Son April 13, 2026 0

Unauthenticated RCE in marimo (CVE-2026-39987) exploited in the wild in record time. Attackers gained root access in under 10 hours. Patch to v0.23.0 now!

Total CMS Takeover: Movable Type Patches Critical 9.8 CVSS Perl RCE Movable Type Vulnerability Perl RCE
  • Vulnerability Report

Total CMS Takeover: Movable Type Patches Critical 9.8 CVSS Perl RCE

Do Son April 13, 2026 0

Movable Type patches a critical 9.8 CVSS RCE vulnerability in its Listing Framework. Secure your CMS against Perl code execution and SQLi—update today!
The CVE Watchtower: Weekly Threat Intelligence Briefing (April 6 – April 12, 2026) Vulnerability Digest Active Exploitation
  • Weekly Recap

The CVE Watchtower: Weekly Threat Intelligence Briefing (April 6 – April 12, 2026)

Do Son April 13, 2026 0

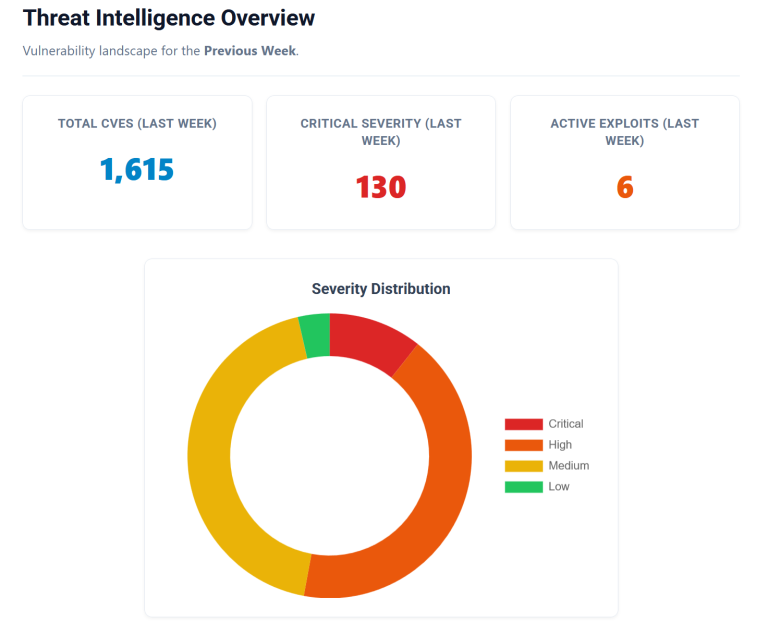
Weekly vulnerability digest (April 6-12, 2026): 1,615 new flaws, CISA KEV alerts for Ivanti and Fortinet, and critical RCE in AI tools like Flowise.
The Stealthy Evolution of the DesckVB RAT Infection Chain DesckVB RAT Fileless Malware
  • Malware

The Stealthy Evolution of the DesckVB RAT Infection Chain

Do Son April 13, 2026 0

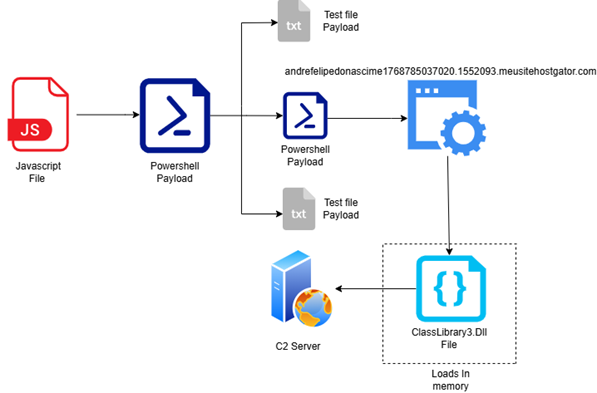
Lat61 Team uncovers DesckVB RAT, a stealthy 2026 Trojan using in-memory .NET loaders & JS obfuscation to hijack systems and evade AV. Learn how it works.

Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat CVE-2023-45648 Apache Tomcat Security Encryption Bypass
  • Vulnerability Report

Encryption Bypasses and Kubernetes Token Leaks Hit Apache Tomcat

Do Son April 13, 2026 0

Apache Tomcat discloses 10 vulnerabilities including encryption bypasses and Kubernetes token leaks. Upgrade now to secure your Java-based web applications.
The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network FrostArmada Campaign DNS Redirection
  • Cybercriminals

The Invisible Hijack: How FrostArmada Turned 18,000 Routers Into a Global Spy Network

Do Son April 13, 2026 0

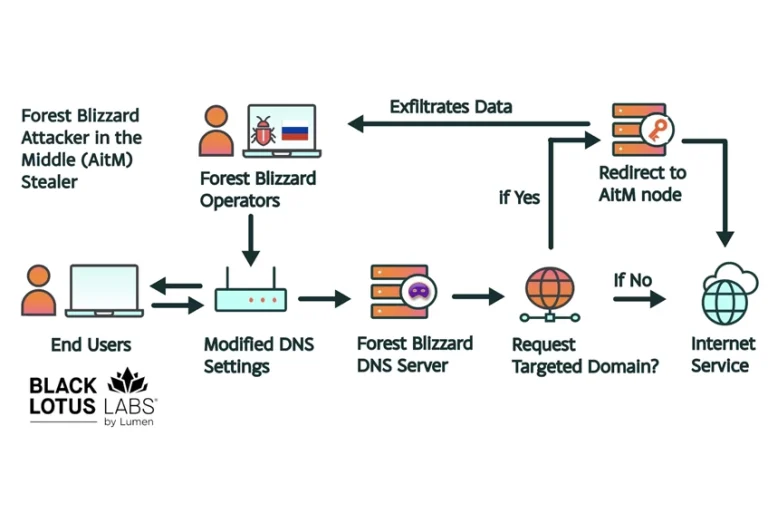
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Vulnerability Report

CVE-2026-40175 (CVSS 10): Critical Axios Vulnerability and Exploit Code Disclosed Publicly

Do Son April 12, 2026 0

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!

Best 7 Credential Leak Monitoring Services Ragic Enterprise Cloud Database - CVE-2024-9983 - CVE-2024-9984 - CVE-2024-9985
  • Technique

Best 7 Credential Leak Monitoring Services

Do Son April 12, 2026 0
Credential leaks have shifted from isolated security events to a continuous operational risk that organizations must actively...
Read More Read more about Best 7 Credential Leak Monitoring Services
Root Access at Risk: Critical Nix Sandbox Escape Overwrites Sensitive System Files Nix Sandbox Escape Root Escalation CVE-2024-45593
  • Vulnerability Report

Root Access at Risk: Critical Nix Sandbox Escape Overwrites Sensitive System Files

Do Son April 10, 2026 0

Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!

Critical Privilege Escalation in Checkmk: Root Access at Risk Checkmk Privilege Escalation
  • Vulnerability Report

Critical Privilege Escalation in Checkmk: Root Access at Risk

Do Son April 10, 2026 0

Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!

The “Seal of Approval” Trap: How Hackers are Hijacking GitHub and Jira Notifications phishing-3390518_1280
  • Cybercriminals

The “Seal of Approval” Trap: How Hackers are Hijacking GitHub and Jira Notifications

Do Son April 10, 2026 0

Cisco Talos exposes "Platform-as-a-Proxy" (PaaP). Hackers are abusing GitHub and Jira's trusted mail servers to bypass SPF/DKIM and deliver phishing lures.
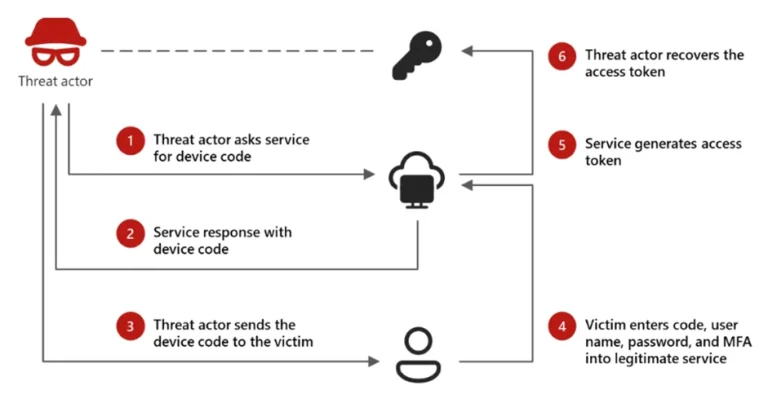
New AI-Driven Phishing Campaign Subverts Microsoft’s Device Code Flow EvilToken Device Code Phishing
  • Cybercriminals

New AI-Driven Phishing Campaign Subverts Microsoft’s Device Code Flow

Do Son April 10, 2026 0

Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
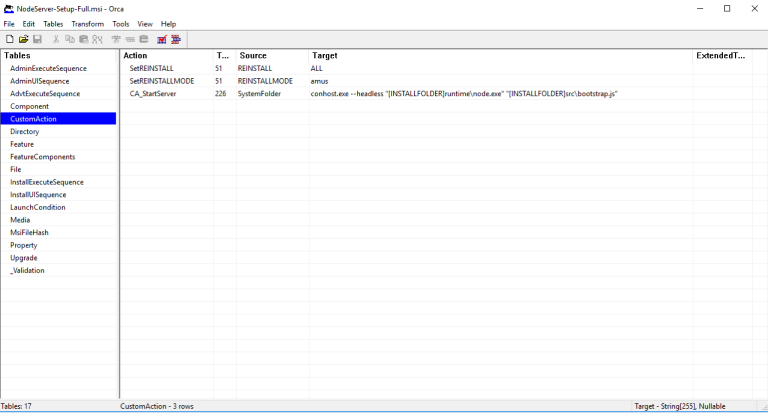
New ClickFix Campaign Unveiled: Modular NodeJS Malware Targets Windows Users Node.js Infostealer ClickFix Campaign
  • Malware

New ClickFix Campaign Unveiled: Modular NodeJS Malware Targets Windows Users

Do Son April 10, 2026 0

Netskope uncovers a Node.js-based ClickFix campaign using gRPC over Tor for stealthy crypto theft. A leaked file exposed their entire MaaS backend.

North Korea’s “Portfolio Model” Shatters Modern Attribution Attribution Resistance DPRK Cyber Portfolio
  • Cyber Security

North Korea’s “Portfolio Model” Shatters Modern Attribution

Do Son April 10, 2026 0

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.

HPE Aruba Patches High-Severity Credential Theft Flaw CVE-2024-26305 _ CVE-2025-23058 Aruba 5G Core Open Redirect
  • Vulnerability Report

HPE Aruba Patches High-Severity Credential Theft Flaw

Do Son April 10, 2026 0

HPE Aruba Networking patches a critical 8.8 CVSS open redirect in its Private 5G Core. Prevent credential harvesting—update to version 1.25.3.1 immediately.
North Korean Hackers Pivot to AI: New npm Malware Targets Cursor, Claude, and Gemini Tokens AI Tool Targeting Contagious Interview
  • Malware

North Korean Hackers Pivot to AI: New npm Malware Targets Cursor, Claude, and Gemini Tokens

Do Son April 10, 2026 0

North Korean hackers are now targeting AI tools like Cursor and Claude. The OtterCookie malware steals API keys and conversation logs. Is your dev environment safe?

TP-Link Archer AX53 Hit by Multiple High-Severity Vulnerabilities Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

TP-Link Archer AX53 Hit by Multiple High-Severity Vulnerabilities

Do Son April 10, 2026 0

TP-Link urges Archer AX53 v1.0 users to update firmware to fix 5 critical flaws, including OS command injection & file leaks. Secure your network now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.