Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Critical SSRF Flaw Discovered in Axios – CVE-2025-62718 (CVSS 9.3) Axios Vulnerability NO_PROXY Bypass
  • Vulnerability Report

Critical SSRF Flaw Discovered in Axios – CVE-2025-62718 (CVSS 9.3)

Do Son April 14, 2026 0

Axios CVE-2025-62718 allows a critical NO_PROXY bypass via hostname normalization errors. Protect your internal network from SSRF—patch or normalize today!

Log4j’s “Silent” Security Gap: New Advisories Warn of Data Loss and TLS Bypasses CVE-2021-45046 Log4j Security Silent Log Failures
  • Vulnerability Report

Log4j’s “Silent” Security Gap: New Advisories Warn of Data Loss and TLS Bypasses

Do Son April 13, 2026 0

Apache Log4j 2.25.4 fixes 4 "silent" flaws, including TLS bypasses and log injection. Secure your infrastructure—upgrade now to prevent data loss.
Apache ActiveMQ Patches “OOM” and MQTT Protocol Flaws Apache ActiveMQ Memory Exhaustion
  • Vulnerability Report

Apache ActiveMQ Patches “OOM” and MQTT Protocol Flaws

Do Son April 13, 2026 0

Apache ActiveMQ patches critical TLSv1.3 memory exhaustion (CVE-2026-39304) and an MQTT regression. Upgrade to 6.2.4 or 5.19.5 to secure your broker!

Triple Security Advisory Prompts Immediate Upgrade to Apache OpenMeetings Version 9.0.0 CVE-2023-28936 OpenMeetings Security Credential Theft
  • Vulnerability Report

Triple Security Advisory Prompts Immediate Upgrade to Apache OpenMeetings Version 9.0.0

Do Son April 13, 2026 0

Apache OpenMeetings 9.0.0 fixes critical flaws including hard-coded "remember-me" keys and REST login credential exposure. Secure your video suite today!
High-Severity RCE and XSS Vulnerabilities Patched in Apache Storm 2.8.6 Apache Storm RCE Deserialization Vulnerability
  • Vulnerability Report

High-Severity RCE and XSS Vulnerabilities Patched in Apache Storm 2.8.6

Do Son April 13, 2026 0

Apache Storm patches a critical RCE via unsafe deserialization and a stored XSS in its UI. Secure your data streams—upgrade to version 2.8.6 today!
LiteLLM Under Fire: Triple Threat Vulnerabilities Expose AI Gateways to Total Takeover LiteLLM SQL Injection CVE-2026-42208 LiteLLM Vulnerability AI Infrastructure Security
  • Vulnerability Report

LiteLLM Under Fire: Triple Threat Vulnerabilities Expose AI Gateways to Total Takeover

Do Son April 13, 2026 0

LiteLLM patches critical 9.4 CVSS flaws, including OIDC cache collisions and pass-the-hash attacks. Secure your AI infrastructure—upgrade to v1.83.0 now!

How Shadow IT Expands Attack Surface Between Pentests compagnons-Fa9b57hffnM-unsplash
  • Technique

How Shadow IT Expands Attack Surface Between Pentests

Do Son April 13, 2026 0
Organizations often focus on known assets during security assessments, but many systems and applications exist outside official...
Read More Read more about How Shadow IT Expands Attack Surface Between Pentests
The End of Phone Activation: How to Activate Windows and Office Offline in 2026 Microsoft Developer Account Suspension Microsoft Web Activation Portal Driver Signing Account Suspension Windows 11 Smart App Control Windows 11 SE end of support, Microsoft education hardware pivot Microsoft Product Activation Portal 2025, Windows telephone activation discontinued Windows Update Naming, Microsoft Update Microsoft earnings, OpenAI valuation VBScript deprecation Microsoft Pakistan, Office Closure Microsoft job cuts Microsoft Own AI Models
  • Technology

The End of Phone Activation: How to Activate Windows and Office Offline in 2026

Do Son April 13, 2026 0

Microsoft has retired its legacy telephone activation system. Learn how to use the new Web Activation Portal to license Windows and Office without an internet connection.

The CPUID Watering Hole Attack Turning CPU-Z into a Trojan CVE-2023-22952 CPUID Watering Hole DLL Sideloading
  • Malware

The CPUID Watering Hole Attack Turning CPU-Z into a Trojan

Do Son April 13, 2026 0

April 2026 Alert: CPUID downloads for CPU-Z and HWMonitor were poisoned with STX RAT via DLL sideloading. Check your systems for CRYPTBASE.dll now!

OpenAI’s Silent Breach: Why You Must Update Your macOS ChatGPT App Before May 8 OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Malware

OpenAI’s Silent Breach: Why You Must Update Your macOS ChatGPT App Before May 8

Do Son April 13, 2026 0

OpenAI revokes legacy macOS certificates after a malicious @Axios library incursion. Update ChatGPT and Codex by May 8, 2026, to avoid software failure.

Vanished Without a Trace: Why Microsoft is Secretly Purging Open-Source Developer Accounts Microsoft Developer Account Suspension
  • Technology

Vanished Without a Trace: Why Microsoft is Secretly Purging Open-Source Developer Accounts

Do Son April 13, 2026 0

Microsoft is under fire for "expunging" developer accounts for projects like WireGuard and UTM. Learn how these silent bans are paralyzing open-source drivers.

STX RAT: The New Financial Predator Hiding in the “Start of Text” STX RAT Financial Malware
  • Malware

STX RAT: The New Financial Predator Hiding in the “Start of Text”

Do Son April 13, 2026 0

eSentire TRU uncovers STX RAT, a modular Trojan targeting finance with HVNC, AMSI Ghosting, and advanced encryption. Secure your perimeter—learn how it works.
Laravel Passport Patches Machine-to-Human Authentication Bypass Laravel Passport Vulnerability Authentication Bypass
  • Vulnerability Report

Laravel Passport Patches Machine-to-Human Authentication Bypass

Do Son April 13, 2026 0

Laravel Passport patches a 7.1 CVSS authentication bypass where machine tokens masquerade as human users. Protect your app—upgrade to v13.7.1 now!

Under Fire Again: Rockstar Games Hit by ShinyHunters in Massive Snowflake Data Breach Rockstar Games Snowflake Breach
  • Data Leak

Under Fire Again: Rockstar Games Hit by ShinyHunters in Massive Snowflake Data Breach

Do Son April 13, 2026 0

Hackers target Rockstar Games via Snowflake. While Rockstar calls the data "non-substantial," could internal budgets and future launch dates be at risk?
The Copilot Retreat: Why Microsoft is Scrubbing Its AI Brand from Windows 11 Apps Windows 11 AI Rebranding
  • Windows

The Copilot Retreat: Why Microsoft is Scrubbing Its AI Brand from Windows 11 Apps

Do Son April 13, 2026 0

Microsoft is quietly rebranding Copilot features in Windows 11. Discover why Notepad’s AI is now called "Advanced Features" and what this means for the OS.
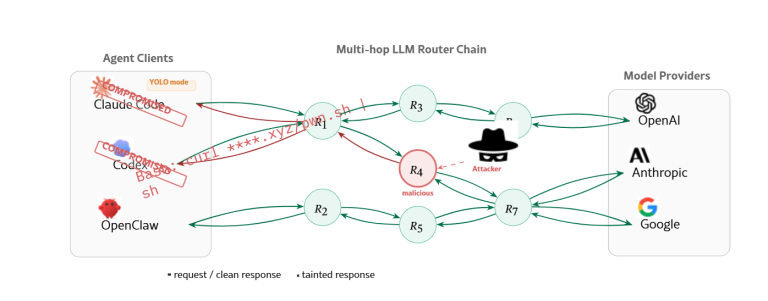
The Weakest Link: How “Transit Hubs” are Quietly Draining Crypto and Stealing AI Data API Transit Hub Vulnerabilities
  • Data Leak

The Weakest Link: How “Transit Hubs” are Quietly Draining Crypto and Stealing AI Data

Do Son April 13, 2026 0

New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.

Why Your Windows Lock Screen Clock is Wrong: Microsoft Explains the 30-Second Lag Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

Why Your Windows Lock Screen Clock is Wrong: Microsoft Explains the 30-Second Lag

Do Son April 13, 2026 0

Noticed the time lagging on your Ctrl+Alt+Delete screen? Microsoft reveals why the Secure Lock Screen runs 30 seconds behind and why they aren't fixing it.

Google’s $135 Million Payday: Are You Eligible for the Android Cellular Data Settlement? Google Android Data Settlement Linux terminal Android
  • Android
  • Data Leak

Google’s $135 Million Payday: Are You Eligible for the Android Cellular Data Settlement?

Do Son April 13, 2026 0

Google settles for $135M over claims it used Android cellular data without consent. Check your eligibility and learn how to claim your share of the payout.

Linux Kernel 7.0 Arrives: A Massive Overhaul for System Stability and Security Linus Torvalds AI bug reports Linux Kernel 7.0 Linux EFI Zboot - CVE-2022-42719 Linux KVM Intel AMX kernel panic, KVM guest host crash 2025
  • Linux

Linux Kernel 7.0 Arrives: A Massive Overhaul for System Stability and Security

Do Son April 13, 2026 0

Linux Kernel 7.0 is here! The 2026 milestone focuses on hardware support, memory safety, and security fixes for x86, ARM64, and RISC-V architectures.

The Encryption Ghost: How the FBI Recovers “Deleted” Signal Messages from iPhone Caches Signal cloud backup iOS Notification Database
  • Vulnerability Report

The Encryption Ghost: How the FBI Recovers “Deleted” Signal Messages from iPhone Caches

Do Son April 13, 2026 0

Signal's encryption is solid, but iOS is leaking your data. Learn how the FBI uses notification caches to recover deleted messages and how to stop it.

One-Touch Security: Google Expands End-to-End Encryption to Gmail on Android and iOS Gmail Mobile E2EE Gmail POP3 support end 2026, Gmailify deprecated January 2026 Gmail spam filter, political bias
  • Technology

One-Touch Security: Google Expands End-to-End Encryption to Gmail on Android and iOS

Do Son April 13, 2026 0

Gmail brings "One-Touch" end-to-end encryption to Android and iOS. Learn how Workspace Enterprise users can now secure sensitive emails natively on mobile.

Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features Windows Insider Program Structural Changes
  • Windows

Microsoft Fixes the Insider Mess: The End of “Clean Installs” and Staggered Features

Do Son April 13, 2026 0

Microsoft simplifies the Windows Insider Program! Discover the new Experimental Channel, native Feature Flags, and data-safe "in-place upgrades."

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17359CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17147CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.