Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Vim Modeline Vulnerability: How a Crafted File Can Hijack Your System Vim RCE Modeline Vulnerability Vim RCE Modeline Sandbox Bypass
  • Vulnerability Report

Vim Modeline Vulnerability: How a Crafted File Can Hijack Your System

Do Son April 1, 2026 0

Vim patches a critical 8.2 CVSS RCE (CVE-2026-34982). Malicious "modelines" can bypass sandboxes to execute commands. Update to 9.2.0276 immediately!

183 Million Targets: Inside the North Korean Supply Chain Strike on Axios and the WAVESHAPER Backdoor axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Malware

183 Million Targets: Inside the North Korean Supply Chain Strike on Axios and the WAVESHAPER Backdoor

Do Son April 1, 2026 0

Google warns of a massive Axios supply chain attack. Versions 1.14.1 & 0.30.4 deploy the WAVESHAPER.V2 backdoor via a hijacked NPM account. Patch now!

The Unpatched Kyverno SSRF Flaw That Turns Policies Into Cluster-Wide Backdoors Kyverno SSRF Kubernetes Policy Engine Kyverno Privilege Escalation CVE-2026-22039
  • Vulnerability Report

The Unpatched Kyverno SSRF Flaw That Turns Policies Into Cluster-Wide Backdoors

Do Son March 31, 2026 0

Kyverno (CVE-2026-4789) faces an unpatched SSRF flaw in its CEL HTTP functions, allowing attackers to bypass K8s namespaces. Secure your cluster now!

Top CISO Conferences Every Cybersecurity Leader Should Attend Undertow Vulnerability CVE-2025-12543 CVE-2025-0107: PoC Exploit Code Undersea Cable Security, China Tech Ban
  • Technique

Top CISO Conferences Every Cybersecurity Leader Should Attend

Do Son March 31, 2026 0
Cyber risk hasn’t just intensified it has fundamentally changed. For most CISOs in 2026, the challenge isn’t...
Read More Read more about Top CISO Conferences Every Cybersecurity Leader Should Attend
Critical Vulnerability in Perl Core Modules Leaves Systems Exposed Perl Vulnerability zlib Exploitation
  • Vulnerability Report

Critical Vulnerability in Perl Core Modules Leaves Systems Exposed

Do Son March 31, 2026 0

Perl (CVE-2026-4176) faces a 9.8 CVSS flaw due to a vulnerable zlib module. Affecting versions since 5.9.4, it demands an urgent update. Learn how to patch.
Public PoC Exploit and Full Details Disclosed for Nginx UI’s 9.4 CVSS Backup Flaw Backup Tampering Exploit
  • Vulnerability Report

Public PoC Exploit and Full Details Disclosed for Nginx UI’s 9.4 CVSS Backup Flaw

Do Son March 31, 2026 0

Public PoC exploit and details are out for Nginx UI’s 9.4 CVSS backup flaw (CVE-2026-33026). Attackers can hijack servers via tampered backups. Update now!
Critical CrewAI Vulnerabilities Allow RCE and Sandbox Escapes via Prompt Injection CrewAI Vulnerabilities AI Agent Security
  • Vulnerability Report

Critical CrewAI Vulnerabilities Allow RCE and Sandbox Escapes via Prompt Injection

Do Son March 31, 2026 0

CERT/CC warns of critical flaws in CrewAI. Insecure fallbacks and prompt injection enable RCE and SSRF. No full patch yet—learn how to secure your agents.
Anthropic Accidentally Leaks Claude Code’s “Secret Sauce” via npm Blunder Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

Anthropic Accidentally Leaks Claude Code’s “Secret Sauce” via npm Blunder

Do Son March 31, 2026 0

Anthropic's proprietary Claude Code logic and unreleased features leaked via an npm source map error. Explore the 46,000-line blueprint here.

The Reservation Hijack: When Your Hotel Booking Becomes a Cyber Trap Reservation Hijacking Hotel Phishing
  • Cybercriminals

The Reservation Hijack: When Your Hotel Booking Becomes a Cyber Trap

Do Son March 31, 2026 0

Gen Digital warns of a reservation hijack scam using real stay dates and hotel names to steal credit cards via WhatsApp. Don't tap that link!

Under Active Attack: Nginx UI’s Critical 9.8 Vulnerability Exploited in the Wild Nginx UI RCE CVE-2026-42238 Nginx UI PoC CVE-2026-33032
  • Vulnerability Report

Under Active Attack: Nginx UI’s Critical 9.8 Vulnerability Exploited in the Wild

Do Son March 31, 2026 0

Public PoC code and full details are out for a 9.8 CVSS flaw in Nginx UI (CVE-2026-33032). With no official patch, servers are at risk. Secure yours now!

The Instant Weaponization of Oracle’s 10.0 CVSS “Zero-Day-Like” Flaw PAN-OS Root RCE CL-STA-1132 Exploitation Tianxin RCE CVE-2021-4473 React Native Supply Chain Attack AstrOOnauta Malware Gladinet Zero-Day, LFI RCE Chain WordPress Theme, Account Takeover CVE-2024-50623 - European Space Agency cyberattack
  • Vulnerability Report

The Instant Weaponization of Oracle’s 10.0 CVSS “Zero-Day-Like” Flaw

Do Son March 31, 2026 0

CloudSEK warn of instant exploitation for Oracle WebLogic's CVE-2026-21962. With a 10.0 CVSS score, this RCE allows full server takeover. Patch now!

The End of the Open APK? Google’s 2026 Roadmap to “Vanquish” Unsigned Sideloading Android sideloading signature requirement
  • Android

The End of the Open APK? Google’s 2026 Roadmap to “Vanquish” Unsigned Sideloading

Do Son March 31, 2026 0

Google is ending direct APK sideloading. By 2027, all Android apps must be cryptographically signed or face a mandatory 24-hour waiting period for installation.

Google Drive Deploys AI-Powered Ransomware Shields for All Users Google Drive ransomware detection
  • Malware

Google Drive Deploys AI-Powered Ransomware Shields for All Users

Do Son March 31, 2026 0

Google Drive's AI now detects 14x more ransomware. Learn how to use the new "infallible temporal anchor" for one-click file restoration in March 2026.

The Stealth Pitch: Why GitHub Copilot is Secretly Injecting Ads Into Your Pull Requests GitHub Copilot PR advertising
  • Technology

The Stealth Pitch: Why GitHub Copilot is Secretly Injecting Ads Into Your Pull Requests

Do Son March 31, 2026 0

GitHub Copilot was caught secretly injecting ads for Raycast and Microsoft Teams into 11,000+ PRs. See how they hid the code and why developers are furious.
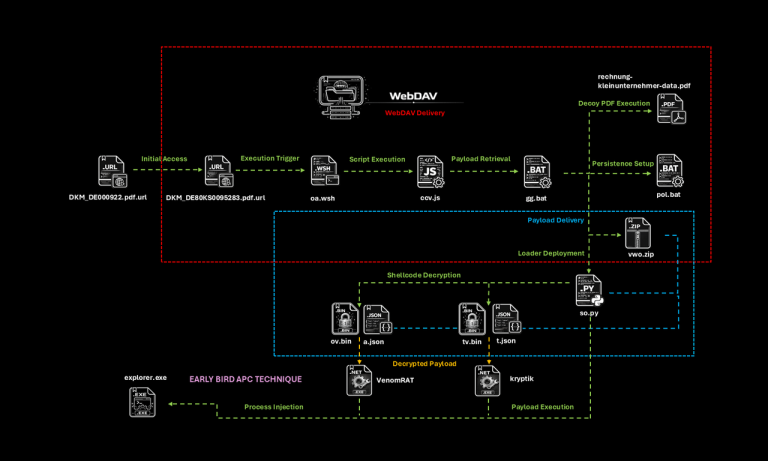
The Malware That Chats Back: Inside G DATA’s Real-Time Notepad Encounter with the “Kiss Loader” Author Kiss Loader Early Bird APC Injection
  • Malware

The Malware That Chats Back: Inside G DATA’s Real-Time Notepad Encounter with the “Kiss Loader” Author

Do Son March 31, 2026 0

G DATA analysts chat with a malware author via Notepad while analyzing "Kiss Loader," a new threat using Early Bird APC injection and VenomRAT. Read more!

The $4.4 Billion Unraveling: Unity Shutters ironSource and Puts Supersonic on the Auction Block Unity ironSource shutdown game accessibility, Unity screen reader
  • Technology

The $4.4 Billion Unraveling: Unity Shutters ironSource and Puts Supersonic on the Auction Block

Do Son March 31, 2026 0

Unity is officially dismantling its $4.4B ironSource acquisition. By April 30, 2026, the network will shut down as Unity pivots to its new Vector architecture.
The 25-Second Heist: Inside FAUX#ELEVATE’s “Inflated” Phishing Attack on French Corporations FAUX#ELEVATE Living-off-the-Land Attack
  • Malware

The 25-Second Heist: Inside FAUX#ELEVATE’s “Inflated” Phishing Attack on French Corporations

Do Son March 31, 2026 0

Securonix uncovers FAUX#ELEVATE, a 25-second attack using 10MB "inflated" VBScripts to steal credentials and mine crypto in French corporate environments.

Axios Under Siege: Critical npm Supply Chain Attack Hijacks Lead Maintainer to Drop Multi-Platform RAT TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Axios Under Siege: Critical npm Supply Chain Attack Hijacks Lead Maintainer to Drop Multi-Platform RAT

Do Son March 31, 2026 0

Axios versions 1.14.1 & 0.30.4 have been poisoned. A hijacked maintainer account is dropping a RAT via postinstall scripts. Revert to safe versions now!
CISA Issues Emergency Mandate as Critical 9.3 NetScaler Flaw “Bleeds” Admin Sessions Citrix NetScaler Vulnerability CVE-2026-3055
  • Vulnerability Report

CISA Issues Emergency Mandate as Critical 9.3 NetScaler Flaw “Bleeds” Admin Sessions

Do Son March 31, 2026 0

CISA adds Citrix NetScaler CVE-2026-3055 to KEV. This 9.3 CVSS flaw "bleeds" admin sessions via SAML. Federal agencies must patch by April 2, 2026.
High-Severity RCE Discovered in Foreman’s WebSocket Proxy Foreman RCE Command Injection
  • Vulnerability Report

High-Severity RCE Discovered in Foreman’s WebSocket Proxy

Do Son March 30, 2026 0

Foreman patches a critical 8.0 CVSS command injection flaw (CVE-2026-1961). Malicious hostnames can trigger RCE via WebSocket proxies. Update to 3.18.1 now!
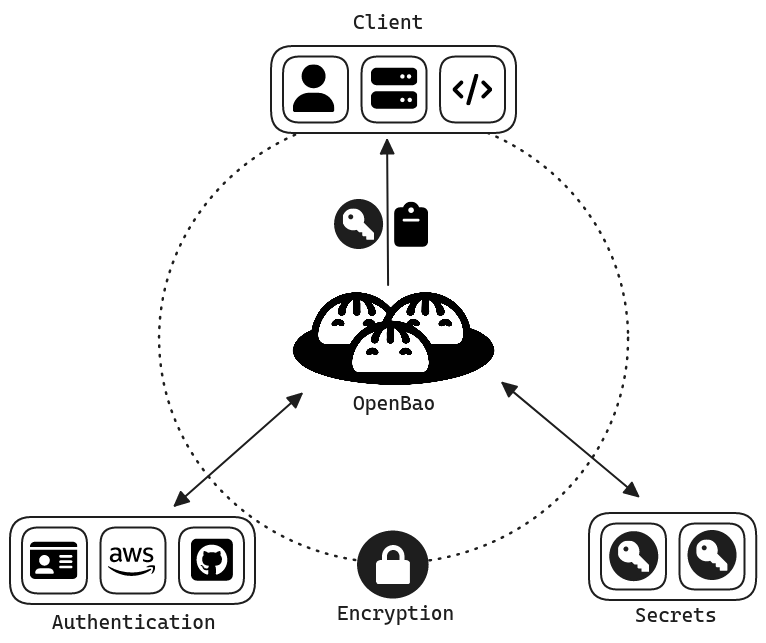
Critical 9.6 CVSS OIDC Flaws in OpenBao Turn “Direct Login” Into a Phishing Trap OpenBao Vulnerability OIDC Session Hijacking
  • Vulnerability Report

Critical 9.6 CVSS OIDC Flaws in OpenBao Turn “Direct Login” Into a Phishing Trap

Do Son March 30, 2026 0

OpenBao patches critical 9.6 and 9.4 CVSS flaws in OIDC flows. Learn how "direct mode" enables session hijacking and XSS token theft. Update to 2.5.2 now.
The Weakest Link: Popular Node.js Config Library “Convict” Hit by Prototype Pollution Prototype Pollution node-convict Vulnerability
  • Vulnerability Report

The Weakest Link: Popular Node.js Config Library “Convict” Hit by Prototype Pollution

Do Son March 30, 2026 0

Node-convict (CVE-2026-33864) faces a 9.4 CVSS Prototype Pollution flaw. Bypass filters and hijack Node.js apps. Update to version 6.2.5 now to stay secure.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    Watchtower Verified📅 Updated: Nov 7, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-80668CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: nf_conntrack_expect: use conntrack GC to reap expectations...
    📅 Updated: Nov 6, 2026
  • CVE-2026-120844CVSS 9.8
    Incorrect Privilege Assignment vulnerability in miniOrange OAuth Single Sign On – SSO (OAuth Client) miniorange-login-with-eve-online-google-facebook allows Privilege Escalation.This...
    📅 Updated: Nov 6, 2026
  • CVE-2026-114630CVSS 9.1
    The ELEX WordPress HelpDesk & Customer Ticketing System plugin for WordPress is vulnerable to arbitrary file deletion due...
    📅 Updated: Nov 6, 2026
  • CVE-2026-71495CVSS 10.0
    Wanderer is a self-hosted trail database for saving and sharing adventures. Prior to 0.20.0, when PUBLIC_PRIVATE_INSTANCE is not...
    📅 Updated: Nov 6, 2026
  • CVE-2026-116769CVSS 9.3
    CVE-2026-116769 is an authentication bypass vulnerability in Secure Access servers starting with version 13.0 and prior to 14.61....
    📅 Updated: Nov 6, 2026
  • CVE-2026-97718CVSS 9.4
    CVE-2026-97718 Is a cross-site request forgery vulnerability in version 14.60 of the Secure Access server.  Because of a...
    📅 Updated: Nov 6, 2026
  • CVE-2024-5535CVSS 9.1
    Issue summary: Calling the OpenSSL API function SSL_select_next_proto with an empty supported client protocols buffer may cause a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-64618CVSS 9.8
    Improper Neutralization of Special Elements used in an SQL Command ("SQL Injection") vulnerability exists in Apache Fineract (through...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.