
 cybernewswire

 Do Son
TP-Link releases critical firmware updates for Archer NX200, NX210, NX500, and NX600 models to patch authentication bypass and command injection flaws.

Ubuntu 26.04 LTS is moving to sudo-rs and enabling visual password feedback by default. Discover why Canonical is ending 45 years of terminal silence in 2026.

Spring Cloud Config faces a high-severity CVSS 8.6 flaw (CVE-2026-22739). Attackers can manipulate profiles to access local files or launch SSRF attacks.

The FCC has banned the sale of foreign-made consumer routers in the US. Discover how this 2026 mandate affects brands like Netgear and your home internet costs.

Malefactors claim a massive breach of OVHcloud, allegedly stealing 1.6M customer dossiers and 5.9M domain records. Discover the risks to Europe’s cloud giant.

Apple confirms WWDC 2026 for June 8-12. Explore the debut of iOS 27, the long-awaited "Siri 2.0" chatbot, and software groundwork for the rumored iPhone Fold.

Tech giants pledge $12.5M to help open-source maintainers survive a "tempest" of AI-generated bug reports. Discover the 2026 plan to fortify the global supply chain.

Google releases Chrome 146.0.7680.164/165, patching 8 high-severity flaws including use-after-free and buffer overflows. Update your desktop browser now.

Cloud Software Group warns of a critical 9.3 CVSS memory overread in NetScaler. Patch now to prevent data exposure and session hijacking.

Trend Micro uncovers a selective PureLog Stealer campaign using fake legal notices and fileless execution to target healthcare and government sectors.

Wazuh patches two critical 9.1 CVSS flaws (CVE-2026-25769 & CVE-2026-25770) allowing total cluster takeover. Upgrade to v4.14.3 now to stay protected.
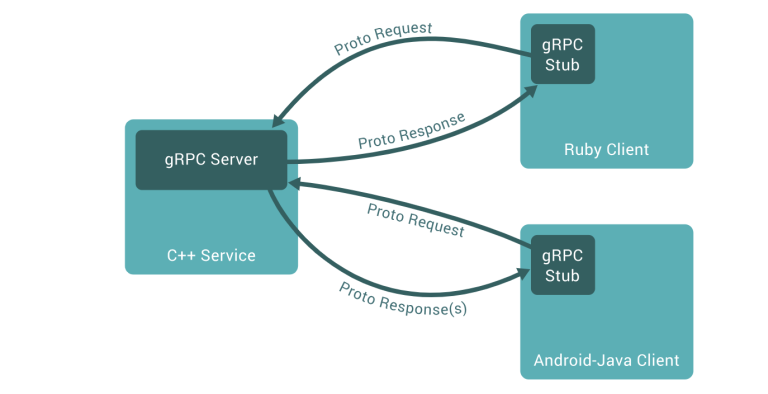
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
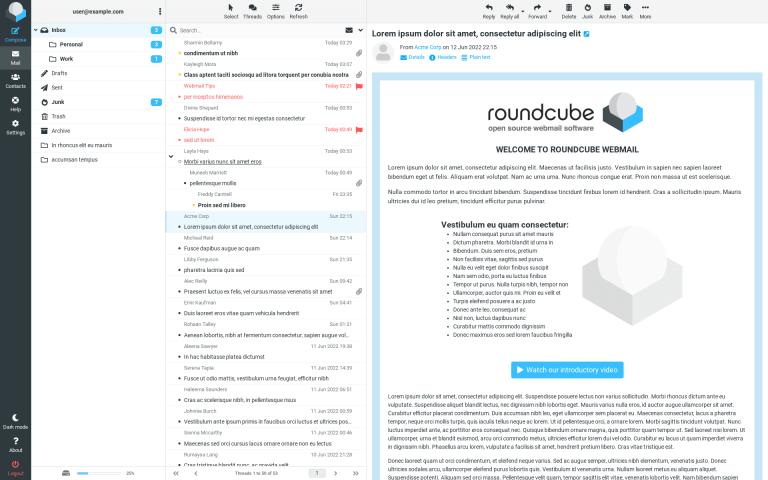
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.

PoC exploit code is now public for CVE-2026-25185. Discover how a complex vulnerability in Windows .lnk shortcuts can be weaponized to leak network data.

Cybercriminals are targeting OpenClaw developers with a fake $5,000 CLAW token airdrop. Learn how this GitHub-based wallet drainer works and stay protected.

A critical 10.0 CVSS flaw in WAGO managed switches (CVE-2026-3587) allows unauthenticated remote takeover via an undocumented CLI backdoor. Update immediately.
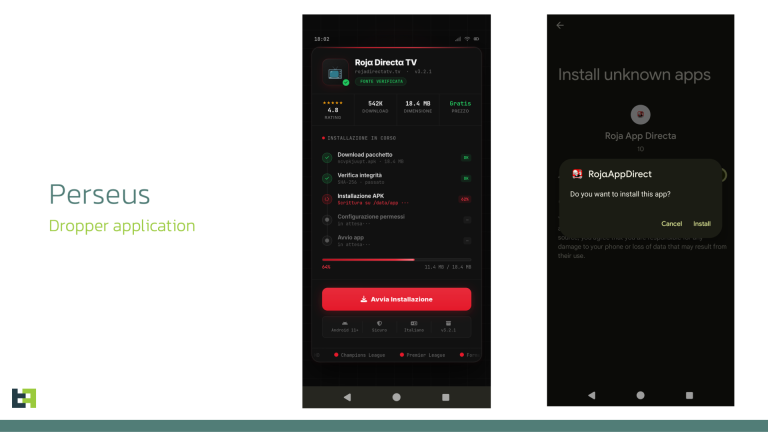
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.

Google is secretly testing AI-generated headlines to replace original webpage titles. Discover why publishers fear this loss of editorial dominion in 2026.
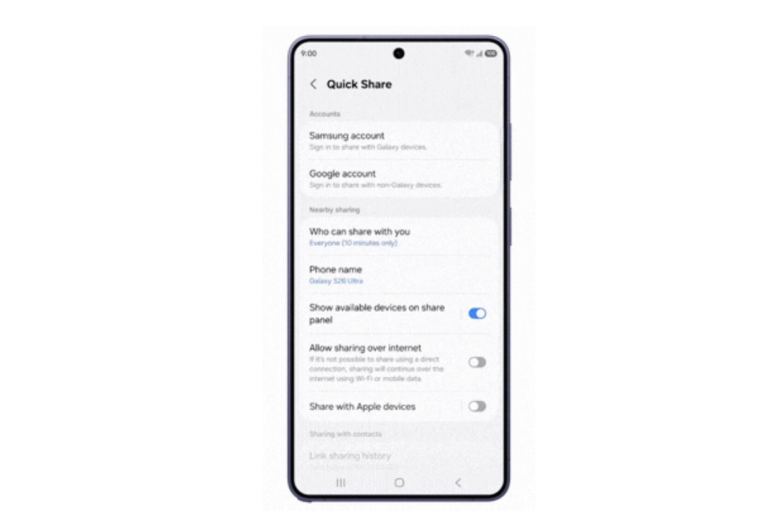
Samsung breaks the historic barrier! The Galaxy S26 now officially supports AirDrop via Quick Share. Learn how to enable cross-platform sharing with Apple.

Intel is pivoting to long-term socket support with the rumored LGA1954. Discover how Robert Hallock’s team is ending the era of mandatory motherboard upgrades.