Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Vulnerability Report

Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover

Do Son March 21, 2026 0

Oracle warns of a critical 9.8 CVSS vulnerability (CVE-2026-21992) allowing unauthenticated attackers to take over Fusion Middleware and Identity Manager.

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy Hex Botnet On-Host Compilation
  • Malware

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy

Do Son March 21, 2026 0

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw

Do Son March 21, 2026 0

PoC exploit code is now public for CVE-2026-20643. Apple issues its first Background Security Improvement to fix this cross-origin Navigation API flaw.
Two High-Severity Spring Boot Flaws Expose Actuator Endpoints Spring Cloud Config Vulnerability CVE-2026-40982 Spring Boot Vulnerability CVSS 9.1 Bypass CVE-2022-31692 Spring Boot Vulnerability Authentication Bypass
  • Vulnerability Report

Two High-Severity Spring Boot Flaws Expose Actuator Endpoints

Do Son March 20, 2026 0

Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

New Mirai Variant and “Monaco” Miner Targeting Linux Devices Linux Malware CondiBot
  • Malware

New Mirai Variant and “Monaco” Miner Targeting Linux Devices

Do Son March 20, 2026 0

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes Windows libarchive Flaw CVE-2025-59284
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes

Do Son March 20, 2026 0

Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets CVE-2024-9042 ingress-nginx Vulnerability CVE-2026-4342
  • Vulnerability Report

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets

Do Son March 20, 2026 0

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.

Engineering-First List: Top California Software Development Companies Andariel APT
  • Technique

Engineering-First List: Top California Software Development Companies

Do Son March 20, 2026 0

Compare California software development companies by AI/ML & DevOps capabilities, and delivery model. Profiles, pricing, and a framework to make the right call.

Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats DriverFixer0428, Contagious Interview Cache Smuggling, ClickFix Evasion North Korean Cyber Espionage
  • Malware

Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats

Do Son March 20, 2026 0

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.
The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail Operation GhostMail Zero-Click XSS
  • Cyber Security

The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail

Do Son March 20, 2026 0

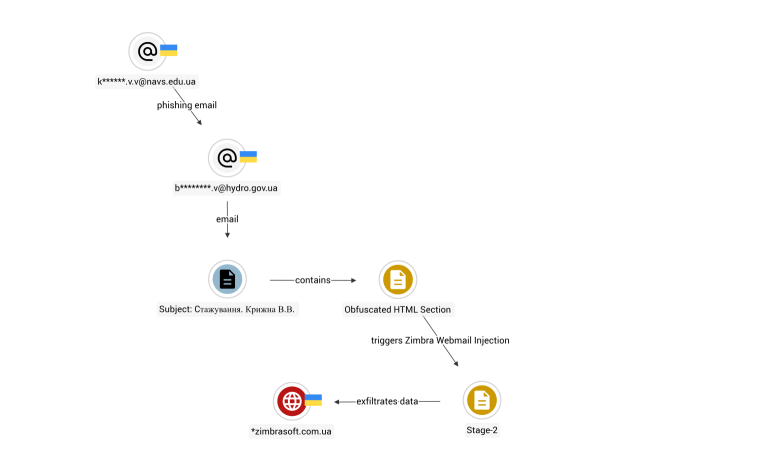
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE CursorJack Cursor Vulnerability
  • Vulnerability Report

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE

Do Son March 20, 2026 0

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire P2P cryptominer malware threat Ollama endpoint attacks IoT Botnets DDoS Attacks
  • Malware

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire

Do Son March 20, 2026 0

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT Forbidden Hyena BlackReaperRAT
  • Cybercriminals

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT

Do Son March 20, 2026 0

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers CVE-2024-22234 Spring Security Vulnerability CVE-2026-22732
  • Vulnerability Report

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers

Do Son March 20, 2026 0

A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats Iranian Cyberwarfare DOJ Domain Seizure
  • Cybercriminals

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats

Do Son March 20, 2026 0

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps CVE-2024-22259 Spring Framework Vulnerabilities CVE-2026-22737
  • Vulnerability Report

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps

Do Son March 20, 2026 0

Researchers found two flaws in Spring Framework (CVE-2026-22737 & CVE-2026-22735) allowing path bypasses and stream corruption. Patch your apps today.

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs Chrome Security Update Critical Vulnerabilities
  • Vulnerability Report

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs

Do Son March 20, 2026 0

Google releases an urgent Chrome update patching 26 security flaws, including 3 critical WebGL and Base vulnerabilities. Update to version 146 today.

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware kill chain
  • Malware

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware

Do Son March 20, 2026 0

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.

Critical Quest KACE Flaw Exploited for Total Network Takeover Quest KACE Vulnerability CVE-2025-32975 FortiGate SSO Bypass, Active Exploitation GoAnywhere RCE, Storm-1175 Cisco VPN RCE, ASA Zero-Day TinyColor Supply Chain Attack SK Telecom, data breach Erlang/OTP RCE, OT Network Security Ivanti CSA Attacks WordPress RCE, Theme Vulnerability
  • Vulnerability Report

Critical Quest KACE Flaw Exploited for Total Network Takeover

Do Son March 20, 2026 0

Arctic Wolf warns that hackers are actively exploiting a critical Quest KACE vulnerability (CVE-2025-32975) to completely take over enterprise networks.
Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’ Boggy Serpens Iranian APT
  • Cybercriminals

Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’

Do Son March 20, 2026 0

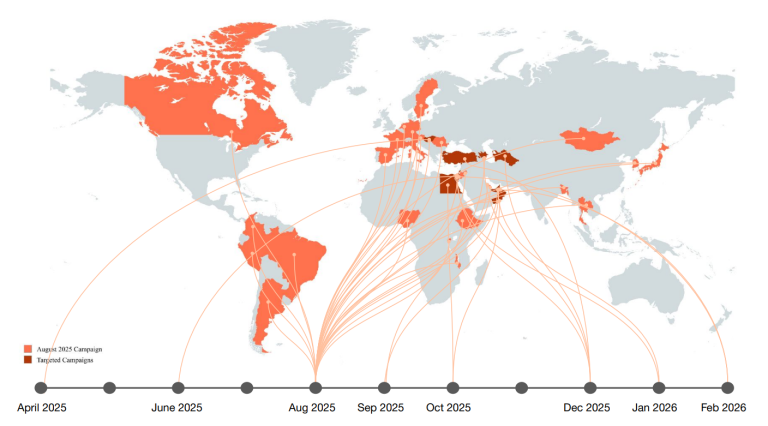
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back tech
  • Technique

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back

Do Son March 19, 2026 0
If you’ve been hesitant to try an AI image/photo editor, the hesitation is probably rooted in an...
Read More Read more about Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back
Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution

Do Son March 19, 2026 0

Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121489CVSS 10.0
    Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') vulnerability in Apache Juneau. The microservice DirectoryResource...
    📅 Updated: Nov 5, 2026
  • CVE-2026-96677CVSS 10.0
    Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Apache Juneau. HTML document serialization does...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73117CVSS 10.0
    Improper Neutralization of CRLF Sequences in HTTP Headers ('HTTP Response Splitting') vulnerability in Apache Juneau. The Apache Juneau...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73116CVSS 10.0
    Insufficiently Protected Credentials vulnerability in Apache Juneau. The Apache Juneau RestClient followed HTTP redirects while keeping credential headers...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73101CVSS 10.0
    Generation of Error Message Containing Sensitive Information vulnerability in Apache Juneau. The REST server sends the internal exception...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73100CVSS 10.0
    Insertion of Sensitive Information into Log File vulnerability in Apache Juneau. The default REST server call logger records...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73099CVSS 10.0
    Cross-Site Request Forgery (CSRF) vulnerability in Apache Juneau. The REST server accepts a "content" query parameter that replaces...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73098CVSS 10.0
    Improper control of dynamically-loaded code vulnerability in Apache Juneau. When Apache Juneau parses a value into a property...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.