Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
SEO Poisoning and “ClickFix” Tactics: The Rise of MacSync Stealer OSX/Amos Stealer Electron ASAR Trojan MioLab Malware macOS Security MacSync Stealer macOS Malware ambar-src npm Malware Supply Chain Typosquatting Matryoshka Mac Malware ClickFix Crypto Scam Infostealer Evolution macOS Malware Predator Spyware Intellexa Anti-Analysis XCSSET macOS Malware, Xcode Supply Chain
  • Malware

SEO Poisoning and “ClickFix” Tactics: The Rise of MacSync Stealer

Do Son March 23, 2026 0

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
New “StoatWaffle” Malware Emerges in North Korean “Contagious Interview” Campaign StoatWaffle WaterPlum
  • Malware

New “StoatWaffle” Malware Emerges in North Korean “Contagious Interview” Campaign

Do Son March 23, 2026 0

Researchers uncovered StoatWaffle, a new Node.js malware by North Korean hackers targeting developers via malicious VSCode repositories to steal data.

The Weekly Breach: 7 Maximum CVSS Flaws and the DarkSword Exploit Unveiled shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Weekly Recap

The Weekly Breach: 7 Maximum CVSS Flaws and the DarkSword Exploit Unveiled

Do Son March 23, 2026 0

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.
Unmasking DarkSword: GTIG Exposes Full-Chain iOS Exploit Used by Global Spies DarkSword Exploit iOS Zero-Day
  • Vulnerability Report

Unmasking DarkSword: GTIG Exposes Full-Chain iOS Exploit Used by Global Spies

Do Son March 22, 2026 0

Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.
Weaponizing Trust: FBI Warns Iran’s MOIS is Using Telegram as a Malware C2 Hub Telegram C2 Iran MOIS
  • Malware

Weaponizing Trust: FBI Warns Iran’s MOIS is Using Telegram as a Malware C2 Hub

Do Son March 22, 2026 0

The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.

Disconnect Immediately: Rockwell Automation Issues Urgent Warning for Industrial Controllers Rockwell Automation Warning OT Security Rockwell SQLi, Industrial Safety DoS Verve Asset Manager API OT Privilege Escalation Rockwell NAT Router, Critical Auth Bypass Rockwell ICS Privilege Escalation, MSI Repair Attack CVE-2025-7353 Critical vulnerability, industrial control systems Rockwell vulnerability, ICS security Rockwell Arena, Memory Abuse Rockwell Automation, RCE Vulnerability CVE-2025-24479 and CVE-2025-24480 - CVE-2025-0477
  • Vulnerability Report

Disconnect Immediately: Rockwell Automation Issues Urgent Warning for Industrial Controllers

Do Son March 22, 2026 0

Rockwell Automation issues an urgent warning: disconnect industrial controllers from the internet immediately to protect against active threat actors.
Malicious Windsurf IDE Extension Uses Solana Blockchain to Steal Developer Data Windsurf Stealer Solana Blockchain Malware
  • Malware

Malicious Windsurf IDE Extension Uses Solana Blockchain to Steal Developer Data

Do Son March 22, 2026 0

Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
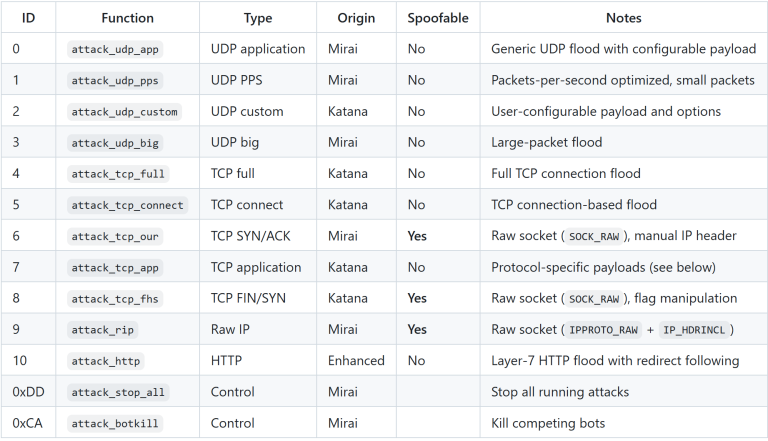
Turf War in Your Living Room: ‘Katana’ Botnet Hijacks Android TV Boxes with Custom Rootkits Katana Botnet Android TV Malware
  • Malware

Turf War in Your Living Room: ‘Katana’ Botnet Hijacks Android TV Boxes with Custom Rootkits

Do Son March 22, 2026 0

Nokia researchers uncover the Katana botnet, a Mirai variant using custom rootkits to hijack unmanaged Android TV boxes in a massive IoT turf war.
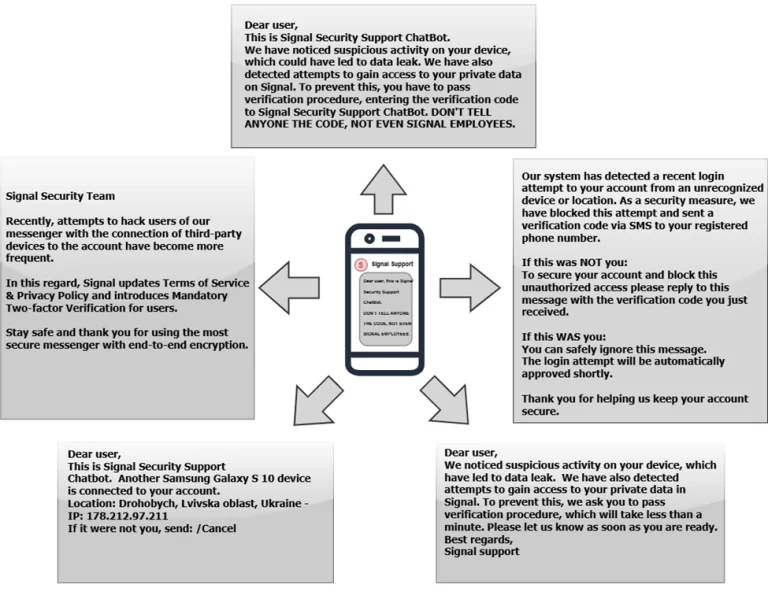
FBI Warns of Russian Intelligence Hijacking Encrypted Messaging Apps Signal Phishing CMA Account Takeover
  • Cyber Security

FBI Warns of Russian Intelligence Hijacking Encrypted Messaging Apps

Do Son March 22, 2026 0

The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.
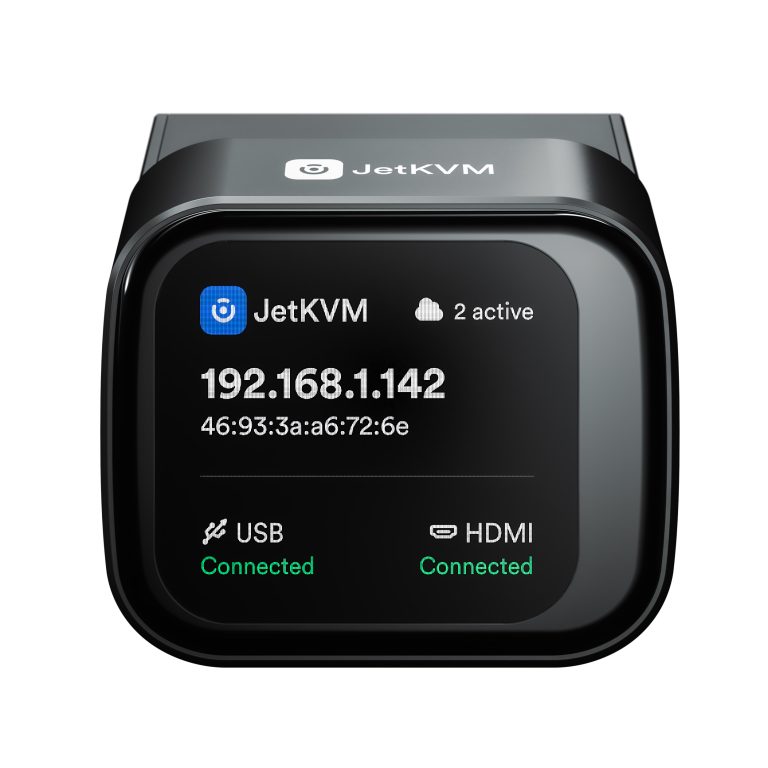
Below the EDR: How Unsecured IP-KVM Switches Grant Total System Takeover IP-KVM Vulnerabilities Hardware Security
  • Vulnerability Report

Below the EDR: How Unsecured IP-KVM Switches Grant Total System Takeover

Do Son March 22, 2026 0

Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.
Active Exploits: CISA Adds Critical Craft CMS and Apple ‘DarkSword’ Flaws to KEV CISA KEV Catalog DarkSword Exploit Draytek Routers VMware vCenter RCE CVE-2024-37079
  • Vulnerability Report

Active Exploits: CISA Adds Critical Craft CMS and Apple ‘DarkSword’ Flaws to KEV

Do Son March 21, 2026 0

CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.

The Bot Takeover: Why AI is Set to Drown Out Human Internet Traffic by 2027 Cloudflare layoffs 2026 AI bot traffic surge Content Signals Policy, AI Content Usage Cloudflare, Certificate Misissuance Salesforce, supply chain attack DDoS attack, Cloudflare Perplexity AI, Web Scraping Pay Per Crawl Cloudflare abuse R2 outage HTTP Cloudflare Blocking
  • Technology

The Bot Takeover: Why AI is Set to Drown Out Human Internet Traffic by 2027

Do Son March 21, 2026 0

Cloudflare CEO Matthew Prince warns that AI bot traffic will soon eclipse human users. Discover the data behind the 2026 internet traffic paradigm shift.
The Command Line Coup: Why Google is Pivoting Project Mariner to Chase the Rise of AI Agents Google Project Mariner pivot
  • Technology

The Command Line Coup: Why Google is Pivoting Project Mariner to Chase the Rise of AI Agents

Do Son March 21, 2026 0

Google is recalibrating Project Mariner as "browser agents" lose ground to high-velocity programming tools like OpenClaw. Inside the 2026 AI agent shift.

The Tripartite Titan: Inside OpenAI’s Secret Plan to Merge ChatGPT, Codex, and Atlas into a Unified “Super App” OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Tripartite Titan: Inside OpenAI’s Secret Plan to Merge ChatGPT, Codex, and Atlas into a Unified “Super App”

Do Son March 21, 2026 0

OpenAI is building a desktop "Super App" merging ChatGPT, Codex, and its Atlas browser. Discover how Fidji Simo is pivoting to fight Anthropic in 2026.

The Great Bifurcation: Apple’s Ingenious “Data Offloading” Strategy Secures Major Legal Win Against Masimo Apple Watch EU Ban, Wi-Fi Sync Apple Watch blood oxygen workaround
  • Technology

The Great Bifurcation: Apple’s Ingenious “Data Offloading” Strategy Secures Major Legal Win Against Masimo

Do Son March 21, 2026 0

An ITC judge has cleared Apple’s Watch workaround. Discover how offloading blood oxygen math to the iPhone bypassed Masimo’s patents and averted an import ban.

Meta’s Metaverse Mercy: Why Horizon Worlds Escaped Execution for a “Maintenance Purgatory” Metaverse, AI NPCs Horizon Worlds VR reversal
  • Technology

Meta’s Metaverse Mercy: Why Horizon Worlds Escaped Execution for a “Maintenance Purgatory”

Do Son March 21, 2026 0

Meta has rescinded the death sentence for Horizon Worlds VR. Discover why the platform is entering "maintenance purgatory" as resources shift to generative AI.

Bezos’ $100 Billion Gamble: The Clandestine “Project Prometheus” Plan to Buy and AI-Overhaul Global Industry Jeff Bezos AI Co-CEO Project Prometheus
  • Technology

Bezos’ $100 Billion Gamble: The Clandestine “Project Prometheus” Plan to Buy and AI-Overhaul Global Industry

Do Son March 21, 2026 0

Jeff Bezos is raising $100 billion to acquire and AI-automate heavy industries like aerospace and defense. Discover the secrets of his "Project Prometheus."

The Mac Takeover: Google Gemini’s “Desktop Intelligence” Arrives to Challenge ChatGPT and Claude Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

The Mac Takeover: Google Gemini’s “Desktop Intelligence” Arrives to Challenge ChatGPT and Claude

Do Son March 21, 2026 0

Google is testing a standalone Gemini app for Mac featuring "Desktop Intelligence." Discover how Gemini will "see" your screen to rival ChatGPT and Claude.

The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer

Do Son March 21, 2026 0

OpenAI acquires Astral, the creators of Ruff and uv. Discover how Rust-powered tools will transform Codex from a code generator into a full AI software engineer.

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs Android sideloading restrictions 2026
  • Android

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs

Do Son March 21, 2026 0

Google's 2026 "Anti-Fraud Crucible" introduces a 24-hour wait and mandatory reboots for sideloading. Discover how Limited Distribution Accounts save hobbyists.

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure Netwrix Vulnerability Password Secure
  • Vulnerability Report

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure

Do Son March 21, 2026 0

Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems QNAP QVR Pro Vulnerability CVE-2026-22898 CVE-2022-27595 - CVE-2024-48860 & CVE-2024-48861
  • Vulnerability Report

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems

Do Son March 21, 2026 0

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121489CVSS 10.0
    Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') vulnerability in Apache Juneau. The microservice DirectoryResource...
    📅 Updated: Nov 5, 2026
  • CVE-2026-96677CVSS 10.0
    Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Apache Juneau. HTML document serialization does...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73117CVSS 10.0
    Improper Neutralization of CRLF Sequences in HTTP Headers ('HTTP Response Splitting') vulnerability in Apache Juneau. The Apache Juneau...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73116CVSS 10.0
    Insufficiently Protected Credentials vulnerability in Apache Juneau. The Apache Juneau RestClient followed HTTP redirects while keeping credential headers...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73101CVSS 10.0
    Generation of Error Message Containing Sensitive Information vulnerability in Apache Juneau. The REST server sends the internal exception...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73100CVSS 10.0
    Insertion of Sensitive Information into Log File vulnerability in Apache Juneau. The default REST server call logger records...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73099CVSS 10.0
    Cross-Site Request Forgery (CSRF) vulnerability in Apache Juneau. The REST server accepts a "content" query parameter that replaces...
    📅 Updated: Nov 5, 2026
  • CVE-2026-73098CVSS 10.0
    Improper control of dynamically-loaded code vulnerability in Apache Juneau. When Apache Juneau parses a value into a property...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.