Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back tech
  • Technique

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back

Do Son March 19, 2026 0
If you’ve been hesitant to try an AI image/photo editor, the hesitation is probably rooted in an...
Read More Read more about Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back
Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution

Do Son March 19, 2026 0

Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.

High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments CVE-2023-22508 Atlassian Bamboo Vulnerability CVE-2026-21570
  • Vulnerability Report

High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments

Do Son March 19, 2026 0

Atlassian warns of a high-severity RCE vulnerability (CVE-2026-21570) in Bamboo Data Center. Patch now to secure your CI/CD pipelines from malicious code.

Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps CVE-2026-31938 jsPDF Vulnerability CVE-2026-25755 jsPDF, CVE-2025-68428 jsPDF Vulnerability CVE-2026-24133
  • Vulnerability Report

Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps

Do Son March 19, 2026 0

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.

CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026 WhatsApp_Image_2026-03-19_at_123734_PM_1773916667xQo48s29B5
  • Press Release

CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026

cybernewswire March 19, 2026 0
Austin, United States, 19th March 2026, CyberNewswire
Read More Read more about CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026
SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft Logo_Press_Release_1024x720_17736822601EiIdxPHe9
  • Press Release

SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft

cybernewswire March 19, 2026 0
Austin, TX, USA, 19th March 2026, CyberNewswire
Read More Read more about SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft
AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers

Do Son March 19, 2026 0

Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.

CISA Issues Urgent Warning Following Global Cyberattack on Stryker GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

CISA Issues Urgent Warning Following Global Cyberattack on Stryker

Do Son March 19, 2026 0
In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...
Read More Read more about CISA Issues Urgent Warning Following Global Cyberattack on Stryker
The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future Meta Horizon Worlds Quest shutdown Meta AI, Child Safety Meta Robotics, Android of Robotics Meta AI, Llama 4.X Meta, AI regulation Meta AI, Data Center Impact Meta AI, Superintelligence Meta Copyrighted Data AI chatbot
  • Technology

The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future

Do Son March 19, 2026 0

Meta is pulling the plug on Horizon Worlds for Quest headsets on June 15, 2026. Discover why the "metaverse" is pivoting to a mobile-only AI future.

The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming FIFA World Cup 2026 YouTube partnership
  • Technology

The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming

Do Son March 19, 2026 0

FIFA names YouTube a "Preferred Platform" for the 2026 World Cup. Stream the first 10 minutes of every match, access exclusive creator content, and more.

The AI Opt-Out: Google’s Strategic Defiance Against CMA Search Regulations Google CMA search riposte
  • Technology

The AI Opt-Out: Google’s Strategic Defiance Against CMA Search Regulations

Do Son March 19, 2026 0

Google challenges UK CMA search mandates, proposing a "central switch" over choice screens and a new AI Overview opt-out for publishers. Read the 2026 update.
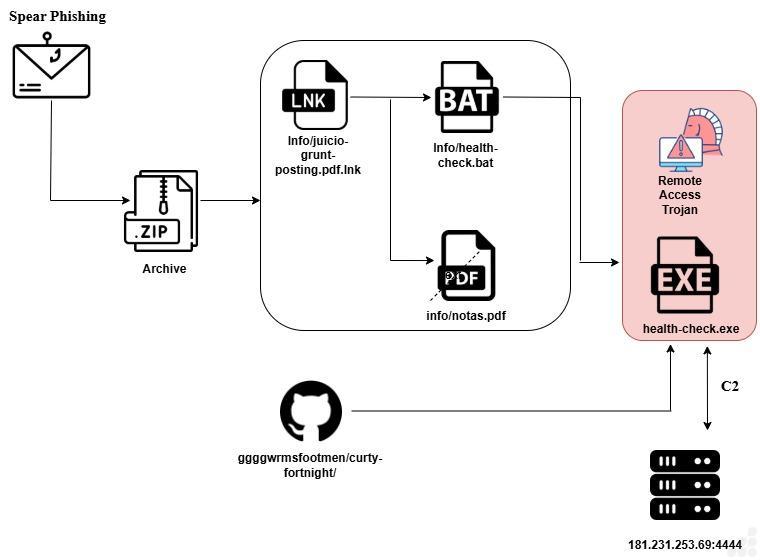
The Judicial Decoy: Sophisticated Rust RAT Infiltrates Argentina’s Federal Courts Rust RAT Argentina Legal Cyberattack
  • Malware

The Judicial Decoy: Sophisticated Rust RAT Infiltrates Argentina’s Federal Courts

Do Son March 19, 2026 0

Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.

Warlock Ransomware Evolves: New Tools and Kernel-Level Evasion Threaten Global Sectors EV2GO Charging Platform ICSA-26-057-04 Lazarus Group, Crypto Hacks LazyStealer
  • Malware

Warlock Ransomware Evolves: New Tools and Kernel-Level Evasion Threaten Global Sectors

Do Son March 19, 2026 0

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.
Total Takeover: Critical 10.0 CVSS Path Traversal Flaw Hits Ubiquiti UniFi Networks UniFi OS vulnerabilities, Ubiquiti security flaws, CVE-2026-47367, CVE-2026-47369, CVE-2026-47370 Ubiquiti UniFi OS Vulnerabilities UniFi OS Firmware Update 2026 UniFi Play Vulnerability Critical RCE Patch Ubiquiti UniFi Vulnerability CVE-2026-22557
  • Vulnerability Report

Total Takeover: Critical 10.0 CVSS Path Traversal Flaw Hits Ubiquiti UniFi Networks

Do Son March 19, 2026 0

Ubiquiti warns of a critical 10.0 CVSS Path Traversal flaw (CVE-2026-22557) in UniFi Network Applications allowing total system takeover. Patch immediately.
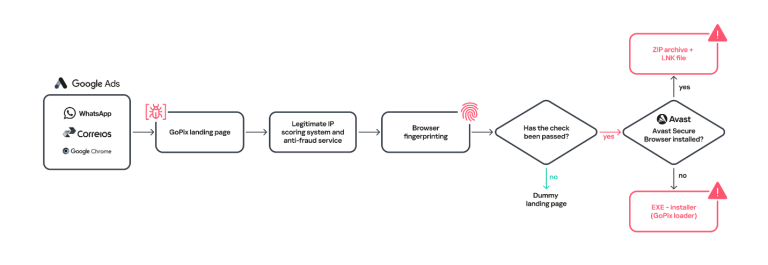
Ghost in the Browser: Advanced ‘GoPix’ Trojan Unveils Unprecedented MitM Attacks GoPix Trojan Brazilian Banking Malware
  • Malware

Ghost in the Browser: Advanced ‘GoPix’ Trojan Unveils Unprecedented MitM Attacks

Do Son March 19, 2026 0

Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
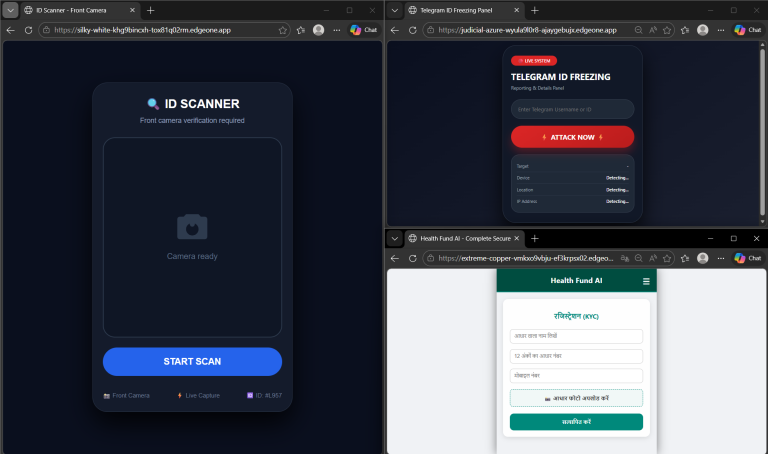
The New Face of Phishing: Hackers Weaponize Browser Prompts to Steal Biometric Data Biometric Phishing Browser Permission Hijacking
  • Cybercriminals

The New Face of Phishing: Hackers Weaponize Browser Prompts to Steal Biometric Data

Do Son March 19, 2026 0

Cyble exposes a phishing campaign abusing browser permissions to silently steal biometric data, audio, and locations for deepfakes and identity fraud.
Exploited in the Wild: CISA Warns of Active Attacks on Microsoft SharePoint and Zimbra CISA KEV Catalog SharePoint RCE CISA, Known Exploited Vulnerabilities CVE-2023-33010
  • Vulnerability Report

Exploited in the Wild: CISA Warns of Active Attacks on Microsoft SharePoint and Zimbra

Do Son March 19, 2026 0

CISA adds actively exploited Microsoft SharePoint RCE (CVE-2026-20963) and Zimbra XSS (CVE-2025-66376) to its KEV catalog. Update your systems immediately.

Exploited in the Wild: Interlock Ransomware Weaponizes Critical 10.0 CVSS Cisco Zero-Day Interlock Ransomware Cisco Zero-Day
  • Malware

Exploited in the Wild: Interlock Ransomware Weaponizes Critical 10.0 CVSS Cisco Zero-Day

Do Son March 19, 2026 0

Amazon threat intel reveals Interlock ransomware is actively exploiting a critical 10.0 CVSS Cisco zero-day (CVE-2026-20131) to hijack firewall networks.
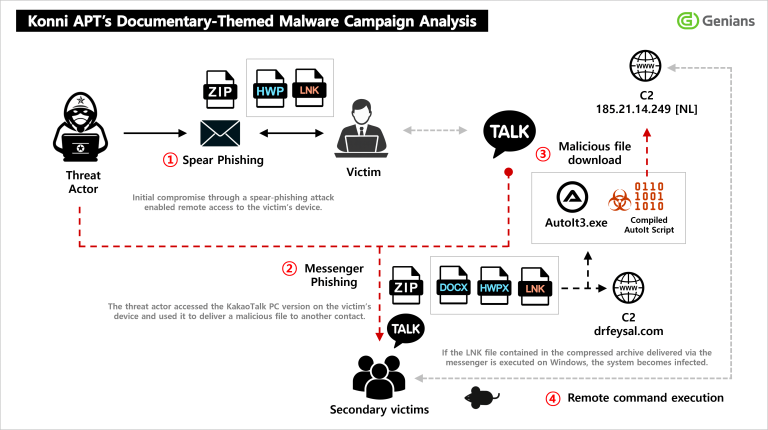
The Trojan Contact: Konni APT Hijacks KakaoTalk to Turn Victims into Attackers Konni APT KakaoTalk Malware
  • Cybercriminals

The Trojan Contact: Konni APT Hijacks KakaoTalk to Turn Victims into Attackers

Do Son March 19, 2026 0

Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.

The Polymarket Trojan: Verified GitHub Org Hijacked to Distribute Crypto-Stealing Bots GitHub Supply Chain Attack Polymarket Malware
  • Malware

The Polymarket Trojan: Verified GitHub Org Hijacked to Distribute Crypto-Stealing Bots

Do Son March 19, 2026 0

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

PoC Exploit Publicly Disclosed: ‘RegPwn’ Flaw Grants SYSTEM Access via Windows Accessibility RegPwn Vulnerability CVE-2026-24291
  • Vulnerability Report

PoC Exploit Publicly Disclosed: ‘RegPwn’ Flaw Grants SYSTEM Access via Windows Accessibility

Do Son March 18, 2026 0

Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.

Critical 9.8 CVSS Schneider Electric Flaw Exposes SCADA and Data Center Systems CVE-2024-10575 CVE-2025-1960 Schneider Electric Vulnerability CVE-2026-0667
  • Vulnerability Report

Critical 9.8 CVSS Schneider Electric Flaw Exposes SCADA and Data Center Systems

Do Son March 18, 2026 0

Schneider Electric patches a critical 9.8 CVSS flaw (CVE-2026-0667) in SCADAPack RTUs and EcoStruxure Data Center Expert. Update to secure your systems.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-57108CVSS 9.8
    Kitware VTK (Visualization Toolkit) through 9.5.0 contains a heap use-after-free vulnerability in vtkGLTFDocumentLoader. The vulnerability manifests during mesh...
    📅 Updated: Nov 5, 2026
  • CVE-2025-29270CVSS 10.0
    Incorrect access control in the realtime.cgi endpoint of Deep Sea Electronics devices DSE855 v1.1.0 to v1.1.26 allows attackers...
    📅 Updated: Nov 5, 2026
  • CVE-2025-63453CVSS 9.8
    Car-Booking-System-PHP v.1.0 is vulnerable to SQL Injection in /carlux/contact.php.
    📅 Updated: Nov 5, 2026
  • CVE-2025-63452CVSS 9.4
    Car-Booking-System-PHP v.1.0 is vulnerable to SQL Injection in /carlux/forgot-pass.php.
    📅 Updated: Nov 5, 2026
  • CVE-2025-63451CVSS 9.8
    Car-Booking-System-PHP v.1.0 is vulnerable to SQL Injection in /carlux/sign-in.php.
    📅 Updated: Nov 5, 2026
  • CVE-2025-61304CVSS 9.8
    OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address.
    📅 Updated: Nov 5, 2026
  • CVE-2025-63601CVSS 9.9
    Snipe-IT before version 8.3.3 contains a remote code execution vulnerability that allows an authenticated attacker to upload a...
    📅 Updated: Nov 5, 2026
  • CVE-2025-56231CVSS 9.1
    Tonec Internet Download Manager 6.42.41.1 and earlier suffers from Missing SSL Certificate Validation, which allows attackers to bypass...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.