
 Do Son
A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

Containerized applications power a large portion of modern cloud infrastructure. Development teams rely on container images to...

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.

Qualys discovers CVE-2026-3888, a critical Local Privilege Escalation (LPE) flaw in Ubuntu Desktop. Learn how a 30-day time window exposes root access.

The EU Council hits Chinese and Iranian cyber threat actors with severe sanctions for hacking critical infrastructure and spreading Olympic disinformation.

Warning: A critical bug in M5 MacBooks and macOS Tahoe causes Wi-Fi to vanish after a factory reset. Learn how to avoid "soft-bricking" your new Mac.
Google Gemini is adding branching threads! Explore divergent AI responses and parallel dialogues without losing your primary chat history. Coming soon in 2026.

Google is shielding Android 17 users by banning non-essential apps from the Accessibility API. Discover how Advanced Protection Mode locks down your device.

Microsoft is turning Notepad into a powerful Markdown editor with new image support. Discover how the classic text tool is evolving for the Windows 11 era.

Locked out of your C drive? Microsoft confirms Samsung Galaxy Connect is breaking Windows 11 permissions. Learn how to fix the KB5084914 "Access Denied" bug.

Google has cut the Gemini API Tier 2 spend requirement to $100 and added per-project spend caps. Learn how to upgrade faster and prevent "billing catastrophes."

Apple's new "Background Security Improvement" delivers surgical iOS and macOS patches in under a minute. Learn how cryptex tech is fixing the WebKit 2026 flaw.

OpenAI launches GPT-5.4 mini and nano. Experience "Thinking" mode on Free/Go tiers and discover how subagent architecture is slashing AI costs by 90%.

Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.

A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.
Technology is no longer just a supporting function in modern organizations; it is the foundation upon which...
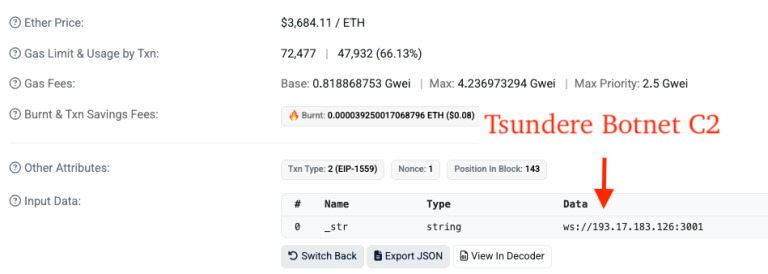
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Two critical flaws in Spring AI (CVE-2026-22729 & CVE-2026-22730) allow attackers to bypass access controls via JSONPath and SQL injection. Update now.

Bishop Fox publicly disclosed details of a critical 9.1 CVSS zero-click SQL injection in FortiClient EMS (CVE-2026-21643). Patch to 7.4.5 immediately.

A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.