Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats DriverFixer0428, Contagious Interview Cache Smuggling, ClickFix Evasion North Korean Cyber Espionage
  • Malware

Game Over: Vidar Stealer 2.0 is Hijacking Gamers with Fake Cheats

Do Son March 20, 2026 0

Acronis uncovers a massive campaign targeting gamers with fake cheats to deliver Vidar Stealer 2.0, a highly evasive malware stealing crypto and passwords.
The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail Operation GhostMail Zero-Click XSS
  • Cyber Security

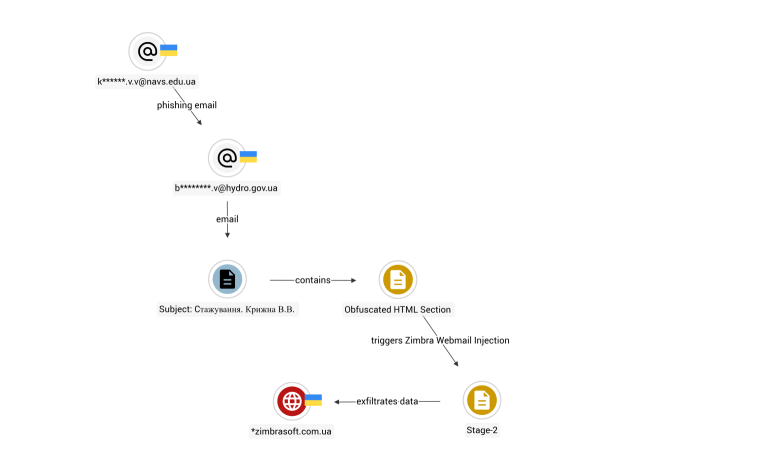
The Invisible Breach: ‘Operation GhostMail’ Uses Zero-Click XSS to Hijack Ukrainian Webmail

Do Son March 20, 2026 0

Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE CursorJack Cursor Vulnerability
  • Vulnerability Report

Developer Alert: “CursorJack” Technique Weaponizes Deeplinks to Hijack Cursor IDE

Do Son March 20, 2026 0

Proofpoint details 'CursorJack', a novel exploit using malicious MCP deeplinks in the Cursor AI editor to execute arbitrary code on developer machines.

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire P2P cryptominer malware threat Ollama endpoint attacks IoT Botnets DDoS Attacks
  • Malware

Operation Takedown: DOJ and Global Allies Smash 30-Terabit IoT Botnet Empire

Do Son March 20, 2026 0

The US DOJ, alongside Canada and Germany, has dismantled four massive IoT botnets responsible for record-breaking 30 Tbps DDoS attacks worldwide.

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT Forbidden Hyena BlackReaperRAT
  • Cybercriminals

The AI-Powered Arsenal: How ‘Forbidden Hyena’ Uses Generative AI to Spawn BlackReaperRAT

Do Son March 20, 2026 0

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers CVE-2024-22234 Spring Security Vulnerability CVE-2026-22732
  • Vulnerability Report

The Silent Leak: Critical 9.1 CVSS Spring Security Flaw Strips Away Vital HTTP Headers

Do Son March 20, 2026 0

A critical 9.1 CVSS flaw in Spring Security (CVE-2026-22732) fails to write HTTP headers, exposing Java apps to severe data leaks. Update immediately.

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats Iranian Cyberwarfare DOJ Domain Seizure
  • Cybercriminals

Takedown: DOJ Seizes Iranian MOIS Domains Used for Global Hacking and Hit Squad Threats

Do Son March 20, 2026 0

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps CVE-2024-22259 Spring Framework Vulnerabilities CVE-2026-22737
  • Vulnerability Report

Bypassed Boundaries: Two New Vulnerabilities Threaten Spring Framework Apps

Do Son March 20, 2026 0

Researchers found two flaws in Spring Framework (CVE-2026-22737 & CVE-2026-22735) allowing path bypasses and stream corruption. Patch your apps today.

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs Chrome Security Update Critical Vulnerabilities
  • Vulnerability Report

Urgent Patch: Massive Google Chrome Update Patches 26 Flaws, Including 3 Critical Bugs

Do Son March 20, 2026 0

Google releases an urgent Chrome update patching 26 security flaws, including 3 critical WebGL and Base vulnerabilities. Update to version 146 today.

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware kill chain
  • Malware

The Typosquatting Trap: Fake Telegram Portal Delivers Stealthy Memory-Resident Malware

Do Son March 20, 2026 0

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.

Critical Quest KACE Flaw Exploited for Total Network Takeover Quest KACE Vulnerability CVE-2025-32975 FortiGate SSO Bypass, Active Exploitation GoAnywhere RCE, Storm-1175 Cisco VPN RCE, ASA Zero-Day TinyColor Supply Chain Attack SK Telecom, data breach Erlang/OTP RCE, OT Network Security Ivanti CSA Attacks WordPress RCE, Theme Vulnerability
  • Vulnerability Report

Critical Quest KACE Flaw Exploited for Total Network Takeover

Do Son March 20, 2026 0

Arctic Wolf warns that hackers are actively exploiting a critical Quest KACE vulnerability (CVE-2025-32975) to completely take over enterprise networks.
Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’ Boggy Serpens Iranian APT
  • Cybercriminals

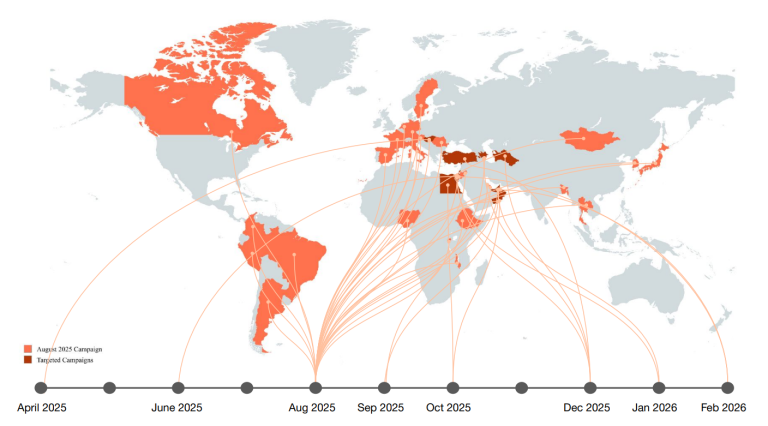
Hijacked Accounts and AI Code: The Deadly New Playbook of Iranian APT ‘Boggy Serpens’

Do Son March 20, 2026 0

Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back tech
  • Technique

Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back

Do Son March 19, 2026 0
If you’ve been hesitant to try an AI image/photo editor, the hesitation is probably rooted in an...
Read More Read more about Myth-Busting: 5 Myths About AI Photo Editors That Are Holding You Back
Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution Jenkins security advisory 2026, CVE-2026-53435, CVE-2026-53436 Jenkins Plugin RCE CI/CD Security Advisory Jenkins Vulnerability CVE-2026-33001 Jenkins CLI DoS, Coverage Plugin XSS Jenkins SAML Hijacking, Plaintext Secrets CVE-2023-43495 - Jenkins Vulnerability
  • Vulnerability Report

Critical Jenkins Flaws Expose CI/CD Servers to Remote Code Execution

Do Son March 19, 2026 0

Jenkins patches critical flaws (CVE-2026-33001 & CVE-2026-33002) allowing remote code execution and full CI/CD pipeline compromise. Update to 2.555 now.

High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments CVE-2023-22508 Atlassian Bamboo Vulnerability CVE-2026-21570
  • Vulnerability Report

High-Severity RCE Flaw in Atlassian Bamboo Threatens CI/CD Environments

Do Son March 19, 2026 0

Atlassian warns of a high-severity RCE vulnerability (CVE-2026-21570) in Bamboo Data Center. Patch now to secure your CI/CD pipelines from malicious code.

Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps CVE-2026-31938 jsPDF Vulnerability CVE-2026-25755 jsPDF, CVE-2025-68428 jsPDF Vulnerability CVE-2026-24133
  • Vulnerability Report

Invisible Ink: Critical 9.6 CVSS jsPDF Flaw Turns Generated Documents into XSS Traps

Do Son March 19, 2026 0

A critical 9.6 CVSS vulnerability in jsPDF (CVE-2026-31938) allows attackers to inject malicious scripts via XSS. Update to version 4.2.1 immediately.

CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026 WhatsApp_Image_2026-03-19_at_123734_PM_1773916667xQo48s29B5
  • Press Release

CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026

cybernewswire March 19, 2026 0
Austin, United States, 19th March 2026, CyberNewswire
Read More Read more about CISO Whisperer Names 11 Vendors Leading the Shift from Tools to Outcomes at RSA Conference 2026
SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft Logo_Press_Release_1024x720_17736822601EiIdxPHe9
  • Press Release

SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft

cybernewswire March 19, 2026 0
Austin, TX, USA, 19th March 2026, CyberNewswire
Read More Read more about SpyCloud’s 2026 Identity Exposure Report Reveals Explosion of Non-Human Identity Theft
AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

AI Workflows Under Fire: Critical RCE and File Write Flaws Expose Langflow Servers

Do Son March 19, 2026 0

Two critical flaws in Langflow (CVE-2026-33017 & CVE-2026-33309) allow unauthenticated remote code execution and arbitrary file writes. Secure servers now.

CISA Issues Urgent Warning Following Global Cyberattack on Stryker GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cybercriminals

CISA Issues Urgent Warning Following Global Cyberattack on Stryker

Do Son March 19, 2026 0
In a move to protect the nation’s critical infrastructure, the Cybersecurity and Infrastructure Security Agency (CISA) has...
Read More Read more about CISA Issues Urgent Warning Following Global Cyberattack on Stryker
The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future Meta Horizon Worlds Quest shutdown Meta AI, Child Safety Meta Robotics, Android of Robotics Meta AI, Llama 4.X Meta, AI regulation Meta AI, Data Center Impact Meta AI, Superintelligence Meta Copyrighted Data AI chatbot
  • Technology

The VR Retreat: Meta to Shutter Horizon Worlds on Quest Headsets for Mobile-Only Future

Do Son March 19, 2026 0

Meta is pulling the plug on Horizon Worlds for Quest headsets on June 15, 2026. Discover why the "metaverse" is pivoting to a mobile-only AI future.

The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming FIFA World Cup 2026 YouTube partnership
  • Technology

The Digital Kickoff: FIFA and YouTube Join Forces for Unprecedented 2026 World Cup Streaming

Do Son March 19, 2026 0

FIFA names YouTube a "Preferred Platform" for the 2026 World Cup. Stream the first 10 minutes of every match, access exclusive creator content, and more.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.