Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
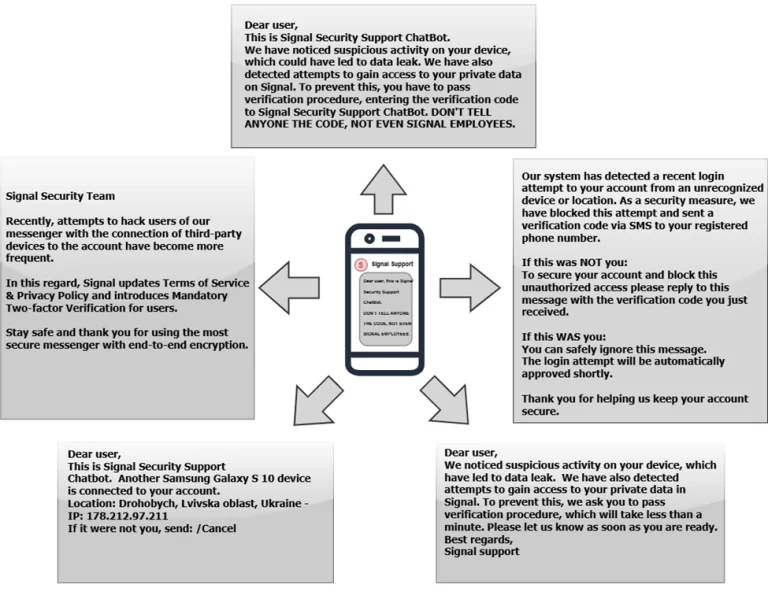
FBI Warns of Russian Intelligence Hijacking Encrypted Messaging Apps Signal Phishing CMA Account Takeover
  • Cyber Security

FBI Warns of Russian Intelligence Hijacking Encrypted Messaging Apps

Do Son March 22, 2026 0

The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.
Below the EDR: How Unsecured IP-KVM Switches Grant Total System Takeover IP-KVM Vulnerabilities Hardware Security
  • Vulnerability Report

Below the EDR: How Unsecured IP-KVM Switches Grant Total System Takeover

Do Son March 22, 2026 0

Eclypsium researchers reveal how compromised IP-KVM switches bypass EDR and software security to grant attackers total, BIOS-level system takeover.
Active Exploits: CISA Adds Critical Craft CMS and Apple ‘DarkSword’ Flaws to KEV CISA KEV Catalog DarkSword Exploit Draytek Routers VMware vCenter RCE CVE-2024-37079
  • Vulnerability Report

Active Exploits: CISA Adds Critical Craft CMS and Apple ‘DarkSword’ Flaws to KEV

Do Son March 21, 2026 0

CISA adds 5 actively exploited flaws to its KEV catalog, including a critical 10.0 CVSS Craft CMS bug and Apple zero-days linked to DarkSword malware.

The Bot Takeover: Why AI is Set to Drown Out Human Internet Traffic by 2027 Cloudflare layoffs 2026 AI bot traffic surge Content Signals Policy, AI Content Usage Cloudflare, Certificate Misissuance Salesforce, supply chain attack DDoS attack, Cloudflare Perplexity AI, Web Scraping Pay Per Crawl Cloudflare abuse R2 outage HTTP Cloudflare Blocking
  • Technology

The Bot Takeover: Why AI is Set to Drown Out Human Internet Traffic by 2027

Do Son March 21, 2026 0

Cloudflare CEO Matthew Prince warns that AI bot traffic will soon eclipse human users. Discover the data behind the 2026 internet traffic paradigm shift.
The Command Line Coup: Why Google is Pivoting Project Mariner to Chase the Rise of AI Agents Google Project Mariner pivot
  • Technology

The Command Line Coup: Why Google is Pivoting Project Mariner to Chase the Rise of AI Agents

Do Son March 21, 2026 0

Google is recalibrating Project Mariner as "browser agents" lose ground to high-velocity programming tools like OpenClaw. Inside the 2026 AI agent shift.

The Tripartite Titan: Inside OpenAI’s Secret Plan to Merge ChatGPT, Codex, and Atlas into a Unified “Super App” OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Tripartite Titan: Inside OpenAI’s Secret Plan to Merge ChatGPT, Codex, and Atlas into a Unified “Super App”

Do Son March 21, 2026 0

OpenAI is building a desktop "Super App" merging ChatGPT, Codex, and its Atlas browser. Discover how Fidji Simo is pivoting to fight Anthropic in 2026.

The Great Bifurcation: Apple’s Ingenious “Data Offloading” Strategy Secures Major Legal Win Against Masimo Apple Watch EU Ban, Wi-Fi Sync Apple Watch blood oxygen workaround
  • Technology

The Great Bifurcation: Apple’s Ingenious “Data Offloading” Strategy Secures Major Legal Win Against Masimo

Do Son March 21, 2026 0

An ITC judge has cleared Apple’s Watch workaround. Discover how offloading blood oxygen math to the iPhone bypassed Masimo’s patents and averted an import ban.

Meta’s Metaverse Mercy: Why Horizon Worlds Escaped Execution for a “Maintenance Purgatory” Metaverse, AI NPCs Horizon Worlds VR reversal
  • Technology

Meta’s Metaverse Mercy: Why Horizon Worlds Escaped Execution for a “Maintenance Purgatory”

Do Son March 21, 2026 0

Meta has rescinded the death sentence for Horizon Worlds VR. Discover why the platform is entering "maintenance purgatory" as resources shift to generative AI.

Bezos’ $100 Billion Gamble: The Clandestine “Project Prometheus” Plan to Buy and AI-Overhaul Global Industry Jeff Bezos AI Co-CEO Project Prometheus
  • Technology

Bezos’ $100 Billion Gamble: The Clandestine “Project Prometheus” Plan to Buy and AI-Overhaul Global Industry

Do Son March 21, 2026 0

Jeff Bezos is raising $100 billion to acquire and AI-automate heavy industries like aerospace and defense. Discover the secrets of his "Project Prometheus."

The Mac Takeover: Google Gemini’s “Desktop Intelligence” Arrives to Challenge ChatGPT and Claude Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

The Mac Takeover: Google Gemini’s “Desktop Intelligence” Arrives to Challenge ChatGPT and Claude

Do Son March 21, 2026 0

Google is testing a standalone Gemini app for Mac featuring "Desktop Intelligence." Discover how Gemini will "see" your screen to rival ChatGPT and Claude.

The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Rust-Powered Brain: Why OpenAI Just Acquired Astral to Build the First True AI Software Engineer

Do Son March 21, 2026 0

OpenAI acquires Astral, the creators of Ruff and uv. Discover how Rust-powered tools will transform Codex from a code generator into a full AI software engineer.

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs Android sideloading restrictions 2026
  • Android

The Death of Open Sideloading? Google’s New “Anti-Fraud Crucible” for Android APKs

Do Son March 21, 2026 0

Google's 2026 "Anti-Fraud Crucible" introduces a 24-hour wait and mandatory reboots for sideloading. Discover how Limited Distribution Accounts save hobbyists.

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure Netwrix Vulnerability Password Secure
  • Vulnerability Report

Critical 9.3 CVSS Flaws Uncovered in Netwrix Password Secure

Do Son March 21, 2026 0

Netwrix issues an urgent advisory for critical vulnerabilities in its Password Secure platform allowing arbitrary code execution. Update to v26.3.100 now.

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems QNAP QVR Pro Vulnerability CVE-2026-22898 CVE-2022-27595 - CVE-2024-48860 & CVE-2024-48861
  • Vulnerability Report

Critical 9.3 CVSS Flaw in QNAP QVR Pro Exposes Surveillance Systems

Do Son March 21, 2026 0

QNAP warns of a critical 9.3 CVSS flaw (CVE-2026-22898) allowing remote attackers to bypass authentication and access QVR Pro surveillance systems. Patch now.

Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Vulnerability Report

Critical 9.8 CVSS Flaw Exposes Oracle Identity Manager to Total Takeover

Do Son March 21, 2026 0

Oracle warns of a critical 9.8 CVSS vulnerability (CVE-2026-21992) allowing unauthenticated attackers to take over Fusion Middleware and Identity Manager.

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy Hex Botnet On-Host Compilation
  • Malware

Weaponizing gcc: Inside the Stealthy ‘Hex’ Botnet’s On-Host Compilation Strategy

Do Son March 21, 2026 0

Hunt Intelligence uncovers the "Hex" botnet, a stealthy campaign using stolen SSH credentials and on-host compilation to evade traditional binary scanners.

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Apple Deploys First-Ever Background Security Patch for Cross-Origin Flaw

Do Son March 21, 2026 0

PoC exploit code is now public for CVE-2026-20643. Apple issues its first Background Security Improvement to fix this cross-origin Navigation API flaw.
Two High-Severity Spring Boot Flaws Expose Actuator Endpoints Spring Cloud Config Vulnerability CVE-2026-40982 Spring Boot Vulnerability CVSS 9.1 Bypass CVE-2022-31692 Spring Boot Vulnerability Authentication Bypass
  • Vulnerability Report

Two High-Severity Spring Boot Flaws Expose Actuator Endpoints

Do Son March 20, 2026 0

Two high-severity flaws (CVE-2026-22731 & CVE-2026-22733) in Spring Boot Actuators allow authentication bypass. Update your framework today to stay secure.

New Mirai Variant and “Monaco” Miner Targeting Linux Devices Linux Malware CondiBot
  • Malware

New Mirai Variant and “Monaco” Miner Targeting Linux Devices

Do Son March 20, 2026 0

Eclypsium uncovers two new Linux malware strains: a CondiBot DDoS variant and the Monaco SSH cryptominer targeting servers and IoT. Secure your network.

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes Windows libarchive Flaw CVE-2025-59284
  • Vulnerability Report

PoC Exploit Publicly Disclosed: Windows ‘libarchive’ Flaw Leaks NetNTLMv2 Hashes

Do Son March 20, 2026 0

Exploit code and details for CVE-2025-59284 are now public. Discover how a Windows libarchive flaw leaks NetNTLMv2 hashes via malicious .tar archives.

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets CVE-2024-9042 ingress-nginx Vulnerability CVE-2026-4342
  • Vulnerability Report

High-Severity ingress-nginx Flaw Exposes Kubernetes Secrets

Do Son March 20, 2026 0

A high-severity 8.8 CVSS flaw (CVE-2026-4342) in ingress-nginx allows attackers to inject malicious code and steal Kubernetes Secrets. Patch immediately.

Engineering-First List: Top California Software Development Companies Andariel APT
  • Technique

Engineering-First List: Top California Software Development Companies

Do Son March 20, 2026 0

Compare California software development companies by AI/ML & DevOps capabilities, and delivery model. Profiles, pricing, and a framework to make the right call.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.