 Do Son
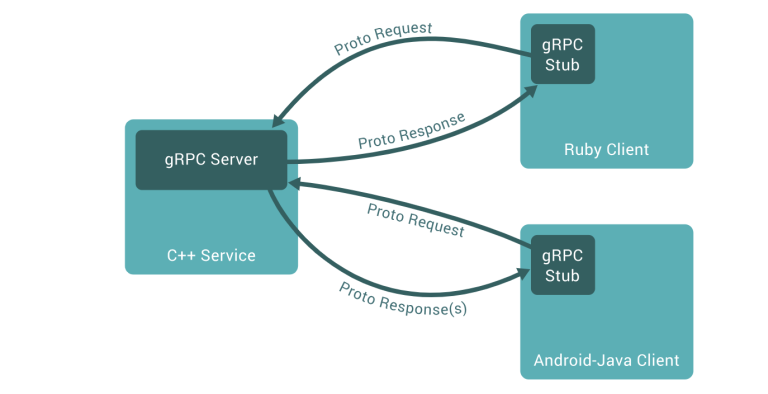
A critical 9.1 CVSS flaw in gRPC-Go (CVE-2026-33186) allows attackers to bypass authorization by omitting a leading slash. Upgrade to v1.79.3 immediately.

Researchers reveal Infostealer.Speagle, a "parasitic" malware hijacking Cobra DocGuard infrastructure to mask the theft of sensitive ballistic missile data.
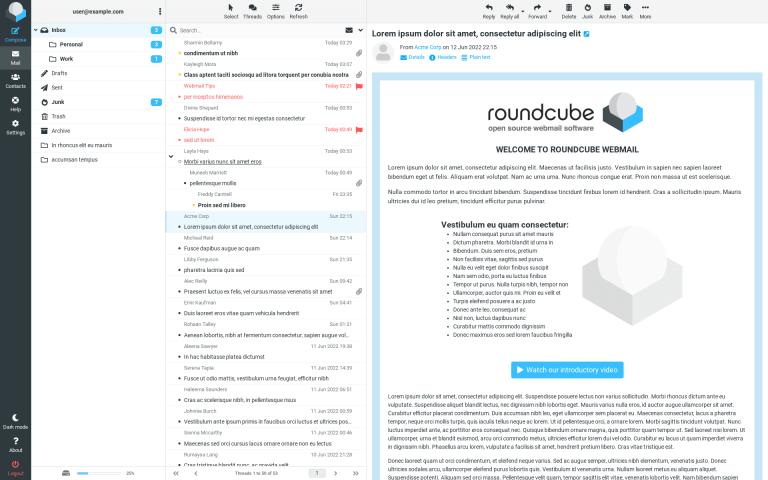
Roundcube v1.6.14 patches a critical pre-authentication file write flaw and account hijacking bugs. Secure your webmail server with this high-priority update.

PoC exploit code is now public for CVE-2026-25185. Discover how a complex vulnerability in Windows .lnk shortcuts can be weaponized to leak network data.

Cybercriminals are targeting OpenClaw developers with a fake $5,000 CLAW token airdrop. Learn how this GitHub-based wallet drainer works and stay protected.

A critical 10.0 CVSS flaw in WAGO managed switches (CVE-2026-3587) allows unauthenticated remote takeover via an undocumented CLI backdoor. Update immediately.
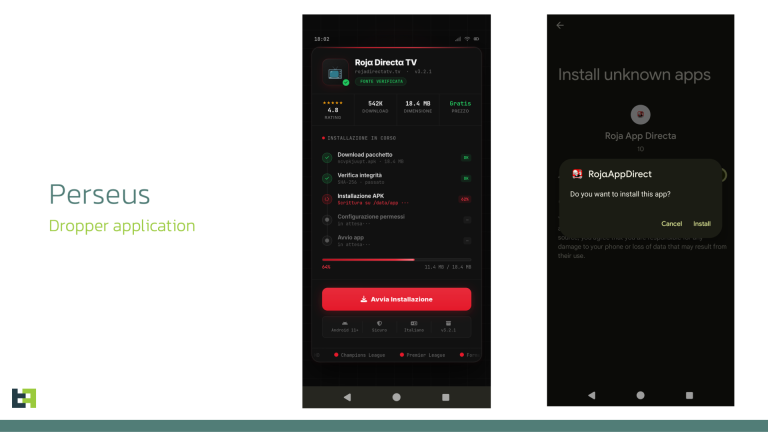
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.

Google is secretly testing AI-generated headlines to replace original webpage titles. Discover why publishers fear this loss of editorial dominion in 2026.
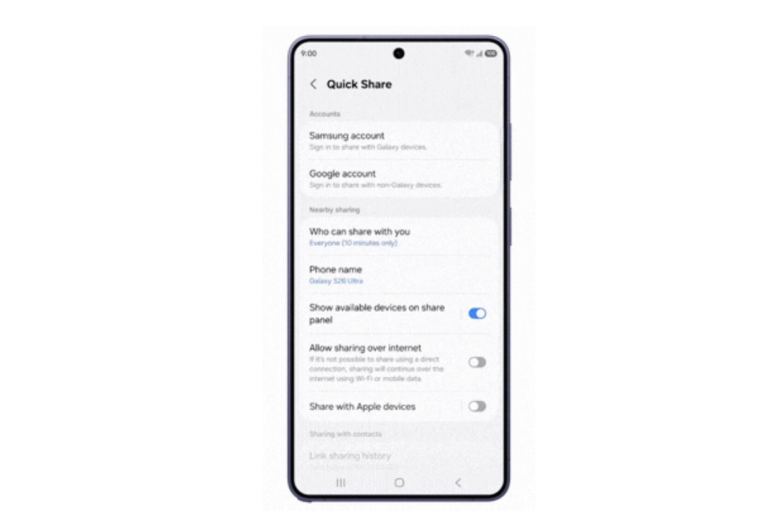
Samsung breaks the historic barrier! The Galaxy S26 now officially supports AirDrop via Quick Share. Learn how to enable cross-platform sharing with Apple.

Intel is pivoting to long-term socket support with the rumored LGA1954. Discover how Robert Hallock’s team is ending the era of mandatory motherboard upgrades.
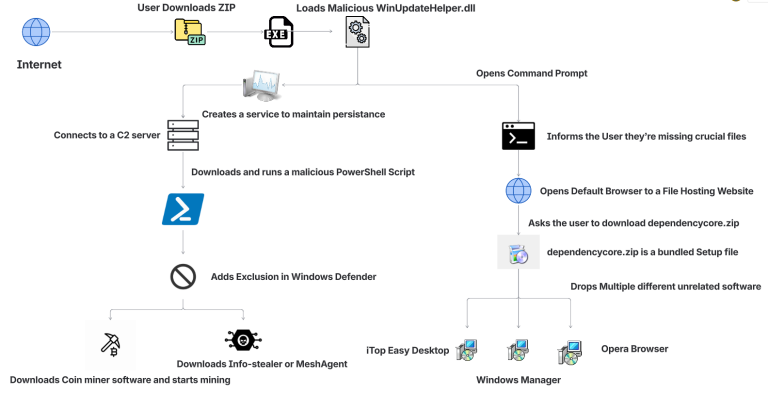
McAfee researchers found a massive malware campaign using LLMs to "vibe code" 1,700+ fake downloads. From Roblox mods to AI tools, your PC is the target.
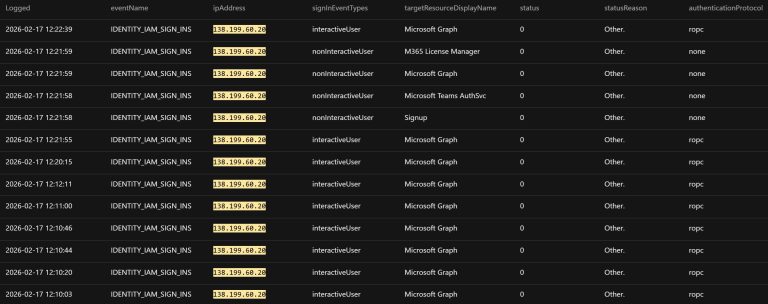
Trend Micro reveals how an exposed Spring Boot Actuator and a spreadsheet of plaintext secrets led to a malware-less SharePoint data exfiltration attack.

Microsoft releases emergency update KB5085516 to fix a critical bug falsely claiming users are "offline." Restore access to OneDrive, Teams, and Copilot now.
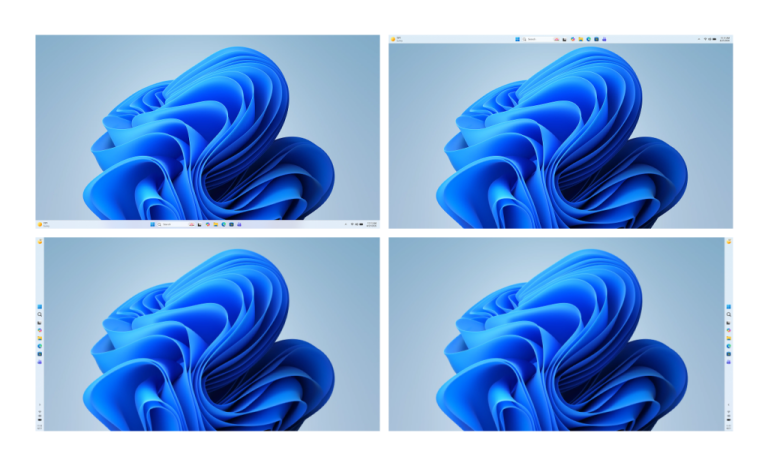
Microsoft plans a 2026 Windows 11 overhaul, moving the Start menu to a native framework. But will the coercive Microsoft account mandate finally be broken?

Beware of "MacSync Stealer": A new macOS malware campaign using SEO poisoning and terminal commands to hijack crypto wallets and system keys.
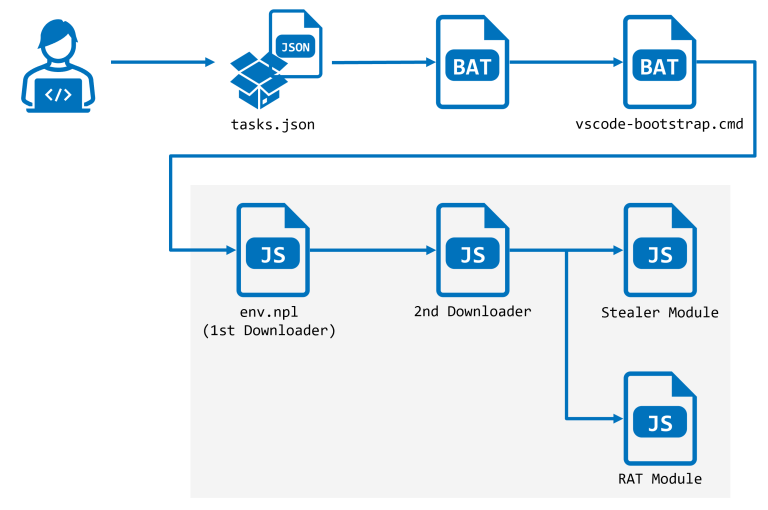
Researchers uncovered StoatWaffle, a new Node.js malware by North Korean hackers targeting developers via malicious VSCode repositories to steal data.

This week in cybersecurity: 1,348 new vulnerabilities discovered, including seven critical 10.0 CVSS flaws and the highly active DarkSword exploit chain.
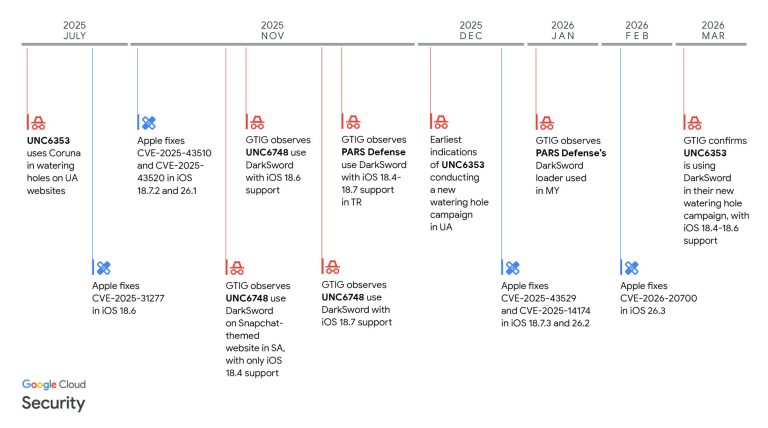
Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.
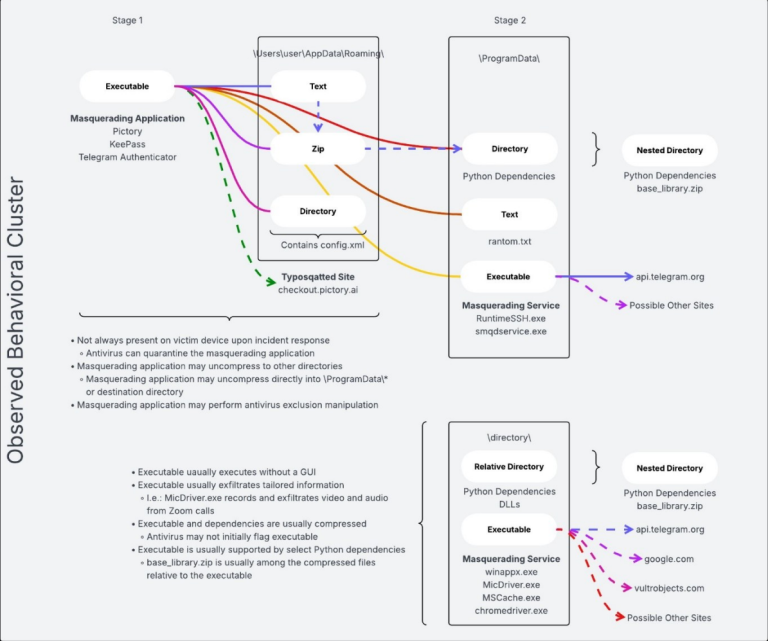
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.

Rockwell Automation issues an urgent warning: disconnect industrial controllers from the internet immediately to protect against active threat actors.
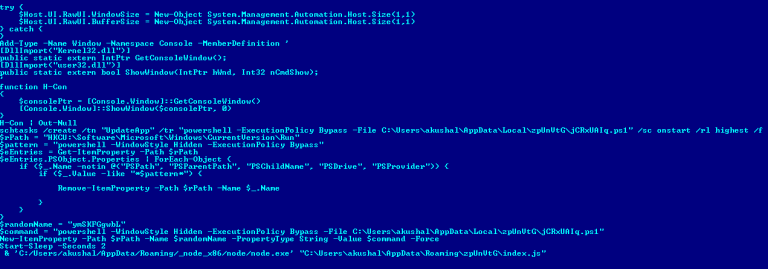
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
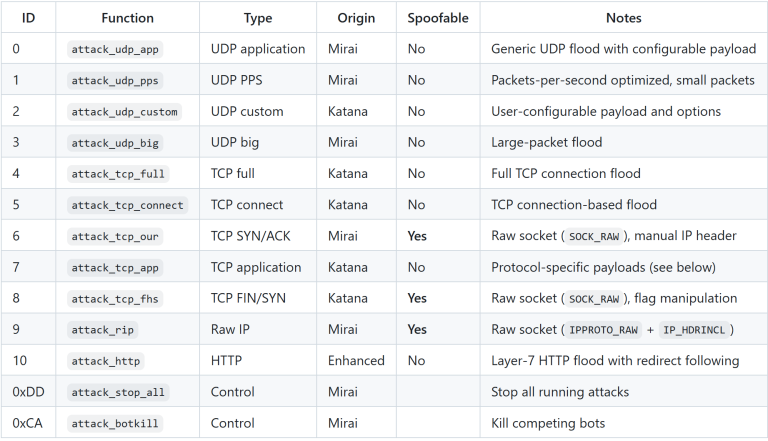
Nokia researchers uncover the Katana botnet, a Mirai variant using custom rootkits to hijack unmanaged Android TV boxes in a massive IoT turf war.