
 Do Son
Google challenges UK CMA search mandates, proposing a "central switch" over choice screens and a new AI Overview opt-out for publishers. Read the 2026 update.
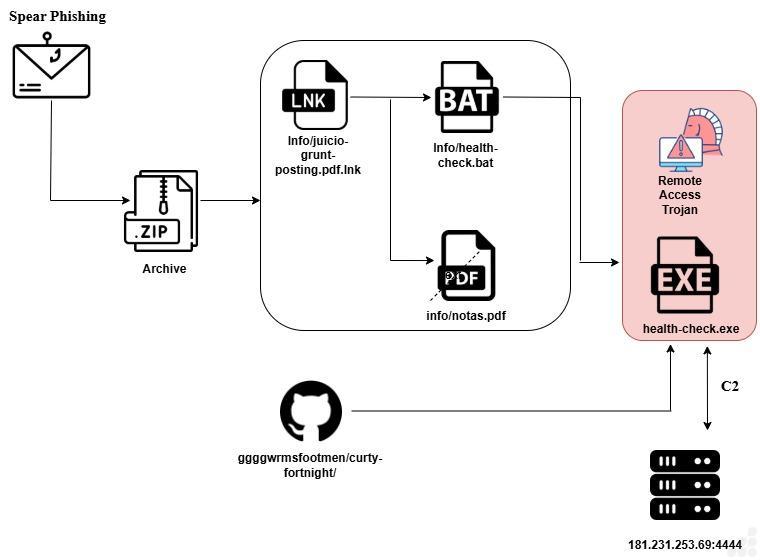
Lat61 Threat Intelligence uncovers a stealthy Rust RAT targeting Argentina's legal sector via weaponized judicial PDFs. Learn about its evasion tactics.

Trend Micro reveals Warlock ransomware is using kernel-level BYOVD attacks and abused IT tools to bypass security and hijack Active Directory.
Ubiquiti warns of a critical 10.0 CVSS Path Traversal flaw (CVE-2026-22557) in UniFi Network Applications allowing total system takeover. Patch immediately.
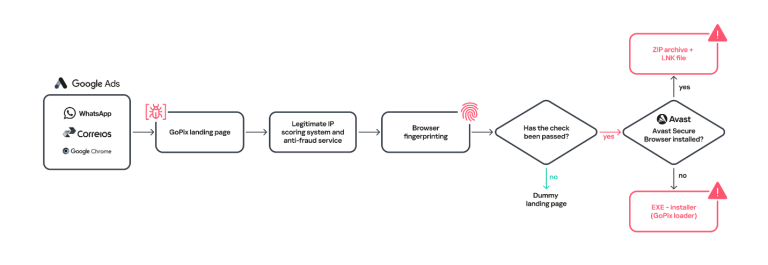
Kaspersky Labs details GoPix, a highly advanced Brazilian banking Trojan using memory-only implants and MitM attacks to target Pix and crypto.
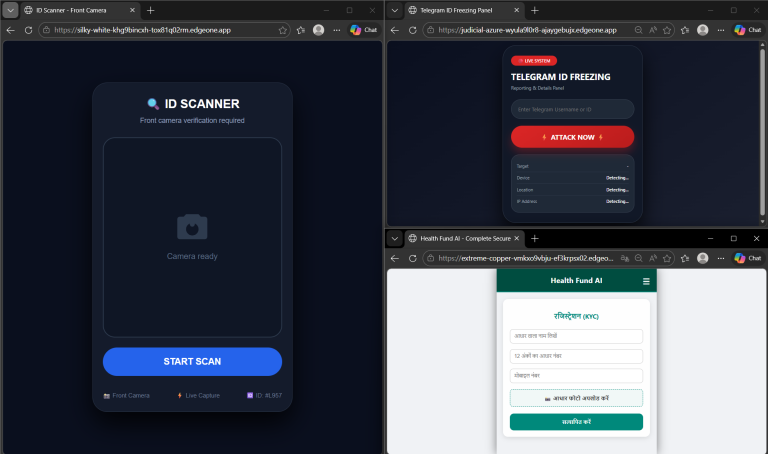
Cyble exposes a phishing campaign abusing browser permissions to silently steal biometric data, audio, and locations for deepfakes and identity fraud.
CISA adds actively exploited Microsoft SharePoint RCE (CVE-2026-20963) and Zimbra XSS (CVE-2025-66376) to its KEV catalog. Update your systems immediately.

Amazon threat intel reveals Interlock ransomware is actively exploiting a critical 10.0 CVSS Cisco zero-day (CVE-2026-20131) to hijack firewall networks.
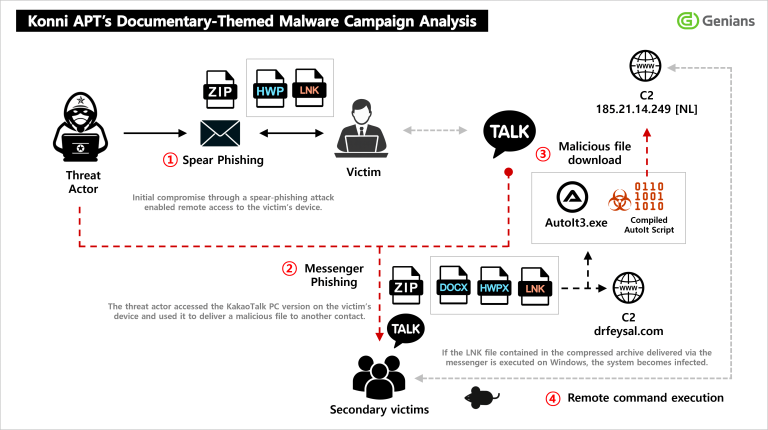
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.

StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.

Exploit code and details for RegPwn (CVE-2026-24291) are publicly disclosed. The Windows local privilege escalation flaw grants attackers SYSTEM access.

Schneider Electric patches a critical 9.8 CVSS flaw (CVE-2026-0667) in SCADAPack RTUs and EcoStruxure Data Center Expert. Update to secure your systems.

A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

Containerized applications power a large portion of modern cloud infrastructure. Development teams rely on container images to...

Rapid7 exposes a global ClickFix campaign hijacking WordPress sites with fake Cloudflare CAPTCHAs to deliver stealthy infostealers and drain digital wallets.

Aryaka Threat Labs exposes BlackSanta, a Russian-linked malware targeting HR teams with fake resumes to deploy an EDR-killer and steal crypto wallets.

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.

Qualys discovers CVE-2026-3888, a critical Local Privilege Escalation (LPE) flaw in Ubuntu Desktop. Learn how a 30-day time window exposes root access.

The EU Council hits Chinese and Iranian cyber threat actors with severe sanctions for hacking critical infrastructure and spreading Olympic disinformation.

Warning: A critical bug in M5 MacBooks and macOS Tahoe causes Wi-Fi to vanish after a factory reset. Learn how to avoid "soft-bricking" your new Mac.
Google Gemini is adding branching threads! Explore divergent AI responses and parallel dialogues without losing your primary chat history. Coming soon in 2026.

Google is shielding Android 17 users by banning non-essential apps from the Accessibility API. Discover how Advanced Protection Mode locks down your device.