Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Notepad’s Metamorphosis: From Plain Text to Markdown-Powered Image Rendering in Windows 11 Windows 11 Notepad image support
  • Windows

Notepad’s Metamorphosis: From Plain Text to Markdown-Powered Image Rendering in Windows 11

Do Son March 18, 2026 0

Microsoft is turning Notepad into a powerful Markdown editor with new image support. Discover how the classic text tool is evolving for the Windows 11 era.

Locked Out of Your Own PC? The Samsung Galaxy Connect Bug Paralyzing Windows 11 C Drives Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Locked Out of Your Own PC? The Samsung Galaxy Connect Bug Paralyzing Windows 11 C Drives

Do Son March 18, 2026 0

Locked out of your C drive? Microsoft confirms Samsung Galaxy Connect is breaking Windows 11 permissions. Learn how to fix the KB5084914 "Access Denied" bug.

The $100 Fast Track: Google Slashes Gemini API Tier 2 Requirements and Adds Critical Spend Caps Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

The $100 Fast Track: Google Slashes Gemini API Tier 2 Requirements and Adds Critical Spend Caps

Do Son March 18, 2026 0

Google has cut the Gemini API Tier 2 spend requirement to $100 and added per-project spend caps. Learn how to upgrade faster and prevent "billing catastrophes."

The 60-Second Patch: How Apple’s “Background Security Improvement” Ends Update Purgatory Apple Background Security CVE-2026-20643 Apple Background Security Improvement Apple Backdoor Apple Lawsuit, Data Exfiltration CVE-2024-44131 - CVE-2025-24118 PoC
  • Technology

The 60-Second Patch: How Apple’s “Background Security Improvement” Ends Update Purgatory

Do Son March 18, 2026 0

Apple's new "Background Security Improvement" delivers surgical iOS and macOS patches in under a minute. Learn how cryptex tech is fixing the WebKit 2026 flaw.

Thinking Small, Acting Big: OpenAI Unveils GPT-5.4 Mini and Nano for the Subagent Era GPT-5.4 mini Thinking mode
  • Technology

Thinking Small, Acting Big: OpenAI Unveils GPT-5.4 Mini and Nano for the Subagent Era

Do Son March 18, 2026 0

OpenAI launches GPT-5.4 mini and nano. Experience "Thinking" mode on Free/Go tiers and discover how subagent architecture is slashing AI costs by 90%.

Pandora’s Box: IBM X-Force Uncovers Likely AI-Generated “Slopoly” Malware Weaponizable AI AI Cyber Threats
  • Malware

Pandora’s Box: IBM X-Force Uncovers Likely AI-Generated “Slopoly” Malware

Do Son March 18, 2026 0

Uncontrolled access to weaponizable AI empowers both cybercriminals and state-sponsored actors. Learn how defenders can prepare for this emerging threat.

Edge of Disaster: Critical 9.8 CVSS Flaw in Oracle Cloud Infrastructure Toolkit Allows Complete Takeover IRGC Oracle Cloud Dubai strike Oracle global layoffs 2026 Oracle Fusion Middleware Vulnerability CVE-2026-21992 Oracle Edge Cloud Vulnerability CVE-2026-21994 Oracle Critical RCE, EBS Marketing Flaws CVE-2024-21182 PoC Exploit Oracle EBS Auth Bypass, CVE-2025-61884
  • Vulnerability Report

Edge of Disaster: Critical 9.8 CVSS Flaw in Oracle Cloud Infrastructure Toolkit Allows Complete Takeover

Do Son March 18, 2026 0

A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.

How Technology Is Powering the Next Generation of Business Growth Fractile AI inference chip AI Market Trends 2025, Similarweb AI Report
  • Technique

How Technology Is Powering the Next Generation of Business Growth

Do Son March 18, 2026 0
Technology is no longer just a supporting function in modern organizations; it is the foundation upon which...
Read More Read more about How Technology Is Powering the Next Generation of Business Growth
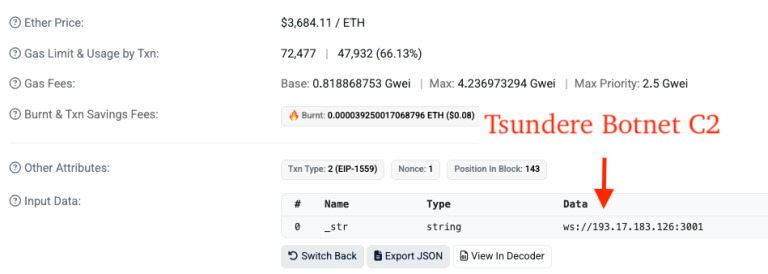
The Cyber Nexus: Iranian Group ‘Muddy Water’ Caught Deploying Russian ‘Tsundere’ Botnet via EtherHiding Tsundere Botnet Muddy Water
  • Cybercriminals

The Cyber Nexus: Iranian Group ‘Muddy Water’ Caught Deploying Russian ‘Tsundere’ Botnet via EtherHiding

Do Son March 18, 2026 0

eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

Critical Spring AI Flaws Expose Databases to SQL and JSONPath Injection Spring AI Vulnerability Remote Code Execution (RCE) Spring AI Vulnerability CVE-2026-22730
  • Vulnerability Report

Critical Spring AI Flaws Expose Databases to SQL and JSONPath Injection

Do Son March 17, 2026 0

Two critical flaws in Spring AI (CVE-2026-22729 & CVE-2026-22730) allow attackers to bypass access controls via JSONPath and SQL injection. Update now.

Publicly Disclosed: Bishop Fox Reveals Critical Pre-Auth SQL Injection in FortiClient EMS FortiSandbox Vulnerability Unauthenticated RCE FortiClient EMS Vulnerability CVE-2026-21643 FortiClient EMS Vulnerability CVE-2026-21643 CVE-2023-34992 - CVE-2023-37936 Fortinet Vulnerabilities CVE-2025-64155
  • Vulnerability Report

Publicly Disclosed: Bishop Fox Reveals Critical Pre-Auth SQL Injection in FortiClient EMS

Do Son March 17, 2026 0

Bishop Fox publicly disclosed details of a critical 9.1 CVSS zero-click SQL injection in FortiClient EMS (CVE-2026-21643). Patch to 7.4.5 immediately.

Instant Hijack: Critical 10.0 CVSS File Browser Flaw Grants Automatic Admin Rights File Browser Vulnerability CVE-2026-32760
  • Vulnerability Report

Instant Hijack: Critical 10.0 CVSS File Browser Flaw Grants Automatic Admin Rights

Do Son March 17, 2026 0

A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.

Orchid Security Recognized by Gartner® as a Representative Vendor of Guardian Agents 1200-700_1773683858Gk7gZkJgJe
  • Press Release

Orchid Security Recognized by Gartner® as a Representative Vendor of Guardian Agents

cybernewswire March 17, 2026 0
New York, United States, 17th March 2026, CyberNewswire
Read More Read more about Orchid Security Recognized by Gartner® as a Representative Vendor of Guardian Agents
CVE Watchtower Launches Enterprise Automation Suite Featuring 30-Day Intelligence Dashboards, Predictive EPSS Scoring, REST API, and ITSM Webhooks cve
  • Announcement

CVE Watchtower Launches Enterprise Automation Suite Featuring 30-Day Intelligence Dashboards, Predictive EPSS Scoring, REST API, and ITSM Webhooks

ddos-admin March 17, 2026 0

Discover CVE Watchtower's new enterprise suite featuring 30-day threat analytics, predictive EPSS scoring, Jira/ServiceNow webhooks, and a private REST API.

Broken Keys: Critical Authlib Flaws Expose Millions to JWT Forgery and Padding Oracles Authlib Vulnerabilities CVE-2026-27962
  • Vulnerability Report

Broken Keys: Critical Authlib Flaws Expose Millions to JWT Forgery and Padding Oracles

Do Son March 17, 2026 0

Three critical flaws in Authlib (including CVSS 9.1 CVE-2026-27962) allow JWT forgery and padding oracle attacks. Update to version 1.6.9 immediately.

GitGuardian Reports an 81% Surge of AI-Service Leaks as 29M Secrets Hit Public GitHub BLOG_State_Of_2026_1_1773309985oZJL6G80kS
  • Press Release

GitGuardian Reports an 81% Surge of AI-Service Leaks as 29M Secrets Hit Public GitHub

cybernewswire March 17, 2026 0
New York, NY, 17th March 2026, CyberNewswire
Read More Read more about GitGuardian Reports an 81% Surge of AI-Service Leaks as 29M Secrets Hit Public GitHub
GlassWorm Abuses VS Code Extensions to Fuel Supply Chain Attacks GlassWorm Malware Open VSX Supply Chain
  • Malware

GlassWorm Abuses VS Code Extensions to Fuel Supply Chain Attacks

Do Son March 17, 2026 0

Socket Research exposes how GlassWorm malware abuses Open VSX dependencies for transitive delivery of an RCE backdoor using Solana blockchain dead drops.

The “Microslop” Backlash: Is Microsoft Finally Retreating from Windows 11 AI Bloat? Windows Secure Lock Screen Clock Lag Windows 11 KB5079391 error Windows 11 Kernel Driver Trust Microslop Windows 11 Windows 11 modem driver removal 2026, CVE-2025-24052 Agere driver exploit Windows 11 Password Icon Bug Lock Screen Glitch Windows 11 26H1 ARM Snapdragon X2 Windows 11 Reboot-Free, Insider Build Windows Update Error, 0x80070103 File Explorer, NTLM leak Windows bug, WinRE Windows Update, UAC prompts Secure Boot Certificate, Windows Security Windows 11 22H2 Installation security updates Windows UEFI CA 2023 Windows 11 25H2
  • Windows

The “Microslop” Backlash: Is Microsoft Finally Retreating from Windows 11 AI Bloat?

Do Son March 17, 2026 0

Faced with the "Microslop" viral critique and a ban on the term in official forums, Microsoft is reportedly scaling back its aggressive Windows 11 AI integration.

Weaponized Browsers: How the ‘DRILLAPP’ Backdoor Turns Microsoft Edge into an Espionage Tool DRILLAPP Backdoor Browser Exploitation
  • Malware

Weaponized Browsers: How the ‘DRILLAPP’ Backdoor Turns Microsoft Edge into an Espionage Tool

Do Son March 17, 2026 0

LAB52 uncovers the DRILLAPP backdoor, a novel espionage campaign targeting Ukraine that weaponizes Microsoft Edge for screen recording and surveillance.

High-Severity Angular XSS Flaw Bypasses Built-In Sanitization Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity Angular XSS Flaw Bypasses Built-In Sanitization

Do Son March 17, 2026 0

An 8.6 CVSS Angular XSS vulnerability (CVE-2026-32635) bypasses built-in sanitization via i18n attributes. Patch your web applications immediately.

Operation CamelClone: New Global Espionage Campaign Hijacks Public Cloud Tools Operation CamelClone Cloud Storage Abuse
  • Cybercriminals

Operation CamelClone: New Global Espionage Campaign Hijacks Public Cloud Tools

Do Son March 17, 2026 0

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.

The Fake VPN Trap: Microsoft Warns of Storm-2561 SEO Poisoning Campaigns Stealing Corporate Credentials Storm-2561 SEO Poisoning
  • Cybercriminals

The Fake VPN Trap: Microsoft Warns of Storm-2561 SEO Poisoning Campaigns Stealing Corporate Credentials

Do Son March 17, 2026 0

Microsoft Defender Experts warn of Storm-2561 using SEO poisoning to distribute fake enterprise VPN clients like Pulse Secure, stealing user credentials.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.