
 Do Son
Socket uncovers a Packagist supply chain attack targeting Vietnamese OphimCMS streaming sites with trojanized themes linked to sanctioned entity FUNNULL.

CISA adds a Wing FTP Server flaw (CVE-2025-47813) to its KEV catalog. The actively exploited cookie vulnerability exposes internal server paths. Update now.

Aikido uncovers a supply chain attack via AstrOOnauta, backdooring two popular React Native packages to steal crypto wallets and developer credentials.

Critical 9.8 CVSS unpatched RCE flaws in the SGLang AI framework (CVE-2026-3059 & CVE-2026-3060) expose servers via unsafe Python pickle deserialization.

Critical 9.7 CVSS flaw in TinaCMS (CVE-2026-28792) lets attackers hijack local developer machines via CORS and path traversal. Patch to 2.1.8 immediately.

A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.

An 8.6 CVSS flaw (CVE-2026-31386) in LiteSpeed Web Server editions allows OS command injection and system compromise. Restrict WebAdmin access immediately.
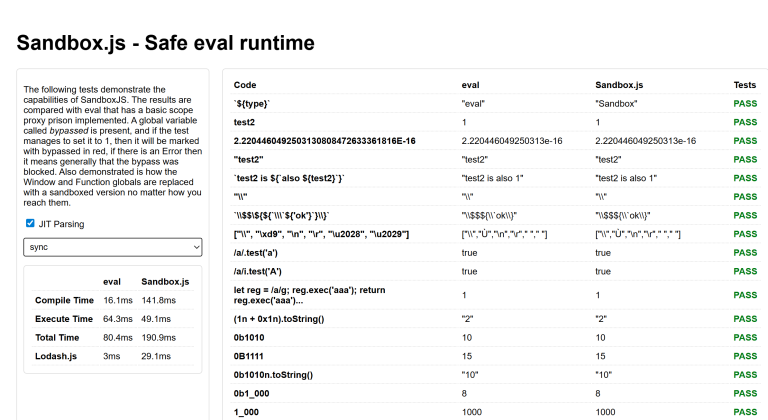
Critical 10.0 CVSS flaw in SandboxJS (CVE-2026-26954) allows attackers to escape the sandbox and achieve Remote Code Execution. Patch to version 0.8.34 now.

OFAC sanctions a North Korean IT worker network and global facilitators for defrauding U.S. businesses of nearly $800M to fund the regime's WMD programs.

Google and Accel’s Atoms initiative picks 5 Indian startups from 4,000+ apps to revolutionize ERP, life sciences, and manufacturing with native AI workflows.

Anthropic doubles Claude usage quotas from March 13–27 during off-peak hours. Learn how this "moral victory" is fueling a massive user migration from OpenAI.

OpenAI confirms ChatGPT ads remain a US-only test for Free and Go tiers. Discover how the "Answer Independence" firewall protects AI response neutrality.
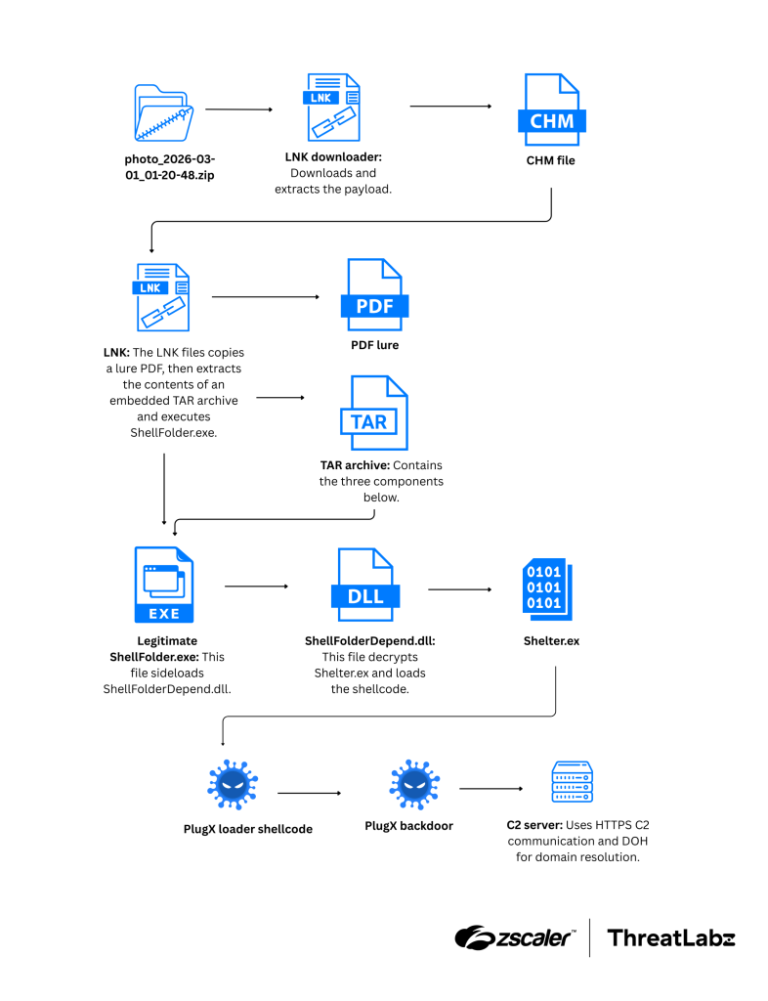
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
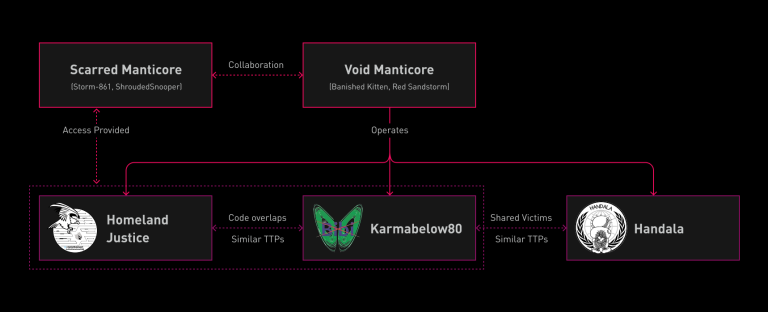
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.
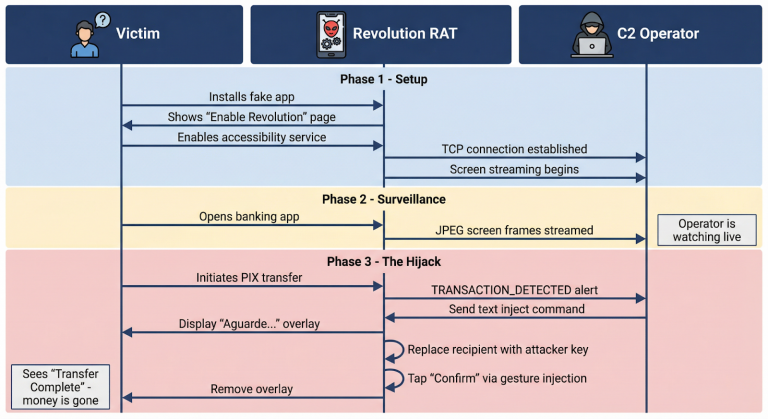
Zimperium's zLabs exposes PixRevolution, a novel Android banking trojan using real-time surveillance to hijack Brazil's PIX instant payments.
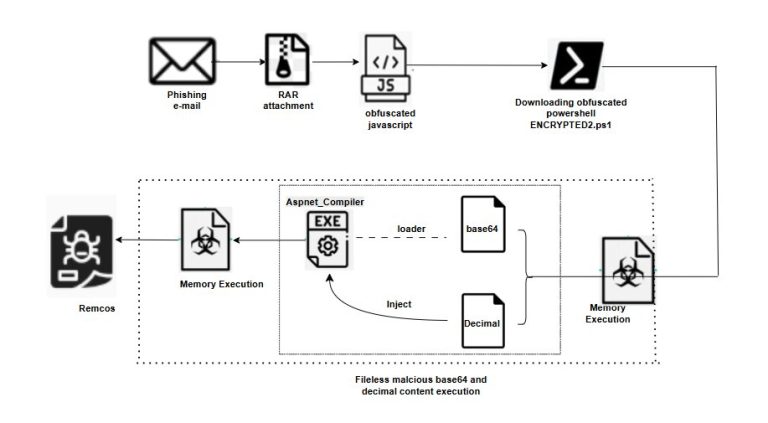
Trellix uncovers a stealthy, fileless Remcos RAT campaign utilizing process hollowing to execute entirely in memory and evade traditional security.
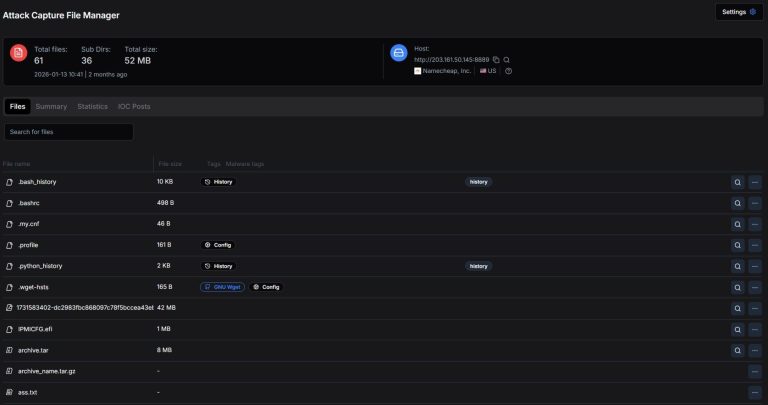
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.
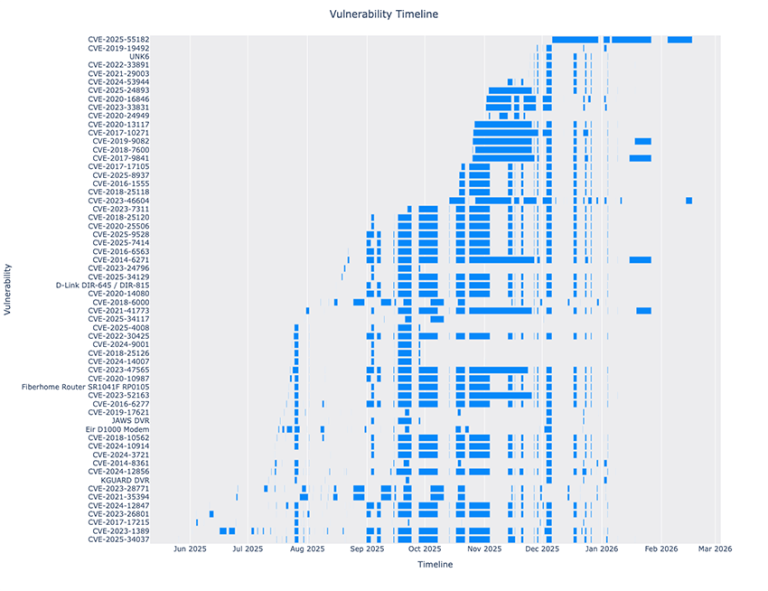
BitSight exposes RondoDox, a relentless IoT botnet using a "shotgun approach" with 174 exploits to hijack residential devices for massive DoS attacks.
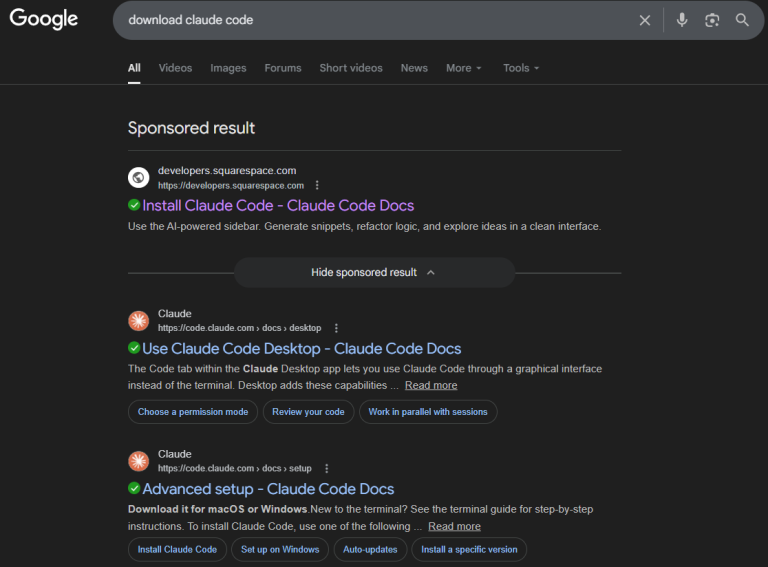
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.
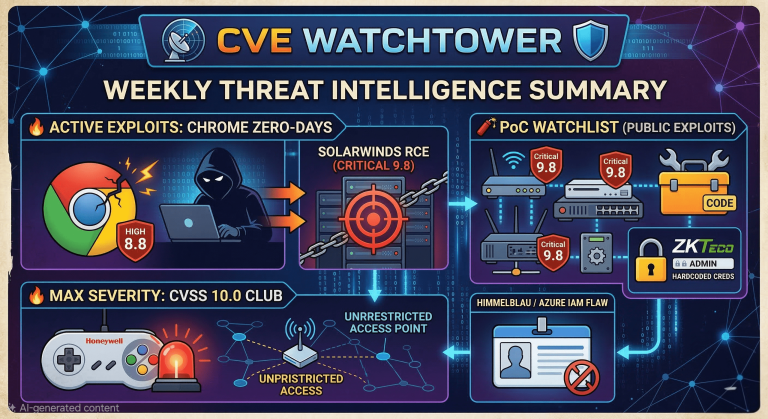
Google Chrome zero-days and a CVSS 10.0 building controller flaw top this week's 1,388 new CVEs. Patch the perimeter before threat actors automate the exploit.

Microsoft and Samsung are investigating a Windows 11 bug that blocks C drive access on Galaxy Books. Learn about the February 2026 update causing these errors.

Apple’s "HomePad" smart display is reportedly finished but delayed until September 2026. Discover why Siri’s AI overhaul is holding back the new smart home hub.