Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Transparency Restored: Apple’s Plan to Fix Liquid Glass in iOS 27 with a Systemwide Slider iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

Transparency Restored: Apple’s Plan to Fix Liquid Glass in iOS 27 with a Systemwide Slider

Do Son March 16, 2026 0

Apple’s iOS 27 will reportedly skip a major redesign in favor of an "incremental refinement": a systemwide slider to control the divisive Liquid Glass effects.

Blitz Brigantine Weaponizes Email Bombing and DNS MX Records to Deploy AOBackdoor Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

Blitz Brigantine Weaponizes Email Bombing and DNS MX Records to Deploy AOBackdoor

Do Son March 16, 2026 0

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground Iranian Cyber Espionage Void Manticore
  • Cybercriminals

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Do Son March 15, 2026 0

Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.
Silence of the Hops: The KadNap Botnet Conscripts 14,000 Routers KadNap Botnet Asus Routers
  • Malware

Silence of the Hops: The KadNap Botnet Conscripts 14,000 Routers

Do Son March 15, 2026 0

Black Lotus Labs uncovers KadNap, a stealthy P2P botnet infecting over 14,000 Asus routers to fuel the Doppelgänger dark web proxy network.

SentinelOne Unmasks Exploitation of FortiGate Appliances as Gateways to Network Takeover Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability Report

SentinelOne Unmasks Exploitation of FortiGate Appliances as Gateways to Network Takeover

Do Son March 15, 2026 0

SentinelOne DFIR reveals how attackers exploit FortiGate NGFW flaws to extract credentials, abuse Active Directory, and establish persistent network access.
Tenable Uncovers ‘LeakyLooker’ Flaws Turning Google Looker Studio into a Cloud Backdoor LeakyLooker Looker Studio Vulnerability
  • Vulnerability Report

Tenable Uncovers ‘LeakyLooker’ Flaws Turning Google Looker Studio into a Cloud Backdoor

Do Son March 15, 2026 0

Tenable exposes "LeakyLooker"—9 cross-tenant flaws in Google Looker Studio that let hackers manipulate and exfiltrate GCP data. Google has patched them.
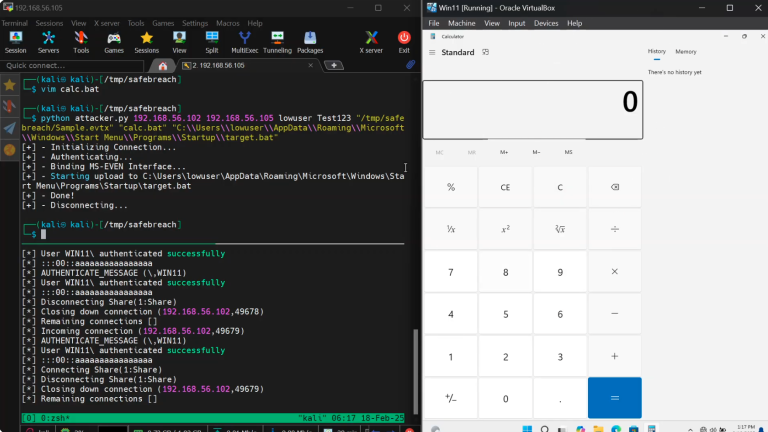
PoC Exploit Disclosed: Researcher Unveils Windows MS-EVEN RPC Vulnerability EventLogin CVE-2025-29969
  • Vulnerability Report

PoC Exploit Disclosed: Researcher Unveils Windows MS-EVEN RPC Vulnerability

Do Son March 15, 2026 0

SafeBreach Labs releases PoC exploit code for EventLogin (CVE-2025-29969), a TOCTOU flaw in Windows MS-EVEN RPC allowing remote file writes. Patch now.

Buying the Truth: Meta Inks Multi-Million Dollar Global News Deals to Fix AI Accuracy Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Technology

Buying the Truth: Meta Inks Multi-Million Dollar Global News Deals to Fix AI Accuracy

Do Son March 15, 2026 0

Meta partners with global news giants like Le Figaro and News Corp to boost Meta AI's real-time accuracy. Discover the $50M deals reshaping the AI landscape.
iPhone Chip, Windows Soul? Parallels Brings Windows 11 to the $599 MacBook Neo MacBook Neo 8GB RAM limit MacBook Neo Windows Parallels
  • Technology

iPhone Chip, Windows Soul? Parallels Brings Windows 11 to the $599 MacBook Neo

Do Son March 15, 2026 0

Parallels Desktop confirms Windows 11 runs on the $599 MacBook Neo. Discover how the A18 Pro chip handles virtualization and why 8GB RAM is the ultimate bottleneck.
The $82,000 Mistake: Google AI Studio Finally Launches API Spending Ceilings Google AI Studio spending limit
  • Technology

The $82,000 Mistake: Google AI Studio Finally Launches API Spending Ceilings

Do Son March 14, 2026 0

After a developer hit an $82k debt in 48 hours, Google AI Studio has added spending limits. Learn how to set your fiscal guardrails and protect your account.

The ARM64 Awakening: Google Chrome Finally Lands Natively on Linux in Q2 2026 Chrome 148 lazy loading Chrome for Linux ARM64 Chrome 145 Update Chrome Security Fixes Chrome Security Update CVE-2026-1220 Chrome 144 Security Update CVE-2026-0899 Chrome Memory Safety, WebGPU UAF Chrome V8 Type Confusion, Google Updater Flaw Chrome V8 Flaw, CVE-2025-13042 Chrome V8, Type Confusion, Chrome 142 Update Chrome V8 Flaw, CVE-2025-12036 Chrome 141, WebGPU Overflow Google Chrome preloading Chrome, V8 vulnerability CVE-2025-9132 Chrome Security Update, Use-After-Free Chrome V8, Type Confusion Chrome Telemetry, Windows 10 EOL Microsoft Family Safety, Chrome Blocking Chrome Security Update, High-Severity Google Chrome, Antitrust CVE-2024-10487 and CVE-2024-10488 Google Chrome Root Program Chrome Update, CVE-2025-3619 Chrome Acquisition, Perplexity.ai
  • Linux

The ARM64 Awakening: Google Chrome Finally Lands Natively on Linux in Q2 2026

Do Son March 14, 2026 0

Google has ended years of hesitation by announcing native Chrome support for Linux ARM64 in Q2 2026. Discover the impact on AI hardware like NVIDIA DGX SPARK.
The Last Guardian: Mozilla Extends Firefox Support for Windows 7 Until August 2026 Firefox Windows 7 support
  • Technology

The Last Guardian: Mozilla Extends Firefox Support for Windows 7 Until August 2026

Do Son March 14, 2026 0

Mozilla has extended Firefox 115 ESR support for Windows 7/8.1 until August 2026. Discover why Firefox remains the last secure browser for legacy OS users.
The Invisible Speed Boost: How Google’s “AutoFDO” Is Quietly Redefining Android Performance Android Kernel AutoFDO
  • Android

The Invisible Speed Boost: How Google’s “AutoFDO” Is Quietly Redefining Android Performance

Do Son March 14, 2026 0

Google’s new AutoFDO for the Android kernel uses real-world data to cut app lag and boost battery life. Discover the 2026 update making your phone feel new.
The Sandbox Slip: How a Security Audit Unearthed Perplexity’s Exposed Claude Code Tokens Perplexity Computer token leak Perplexity Computer Max
  • Data Leak

The Sandbox Slip: How a Security Audit Unearthed Perplexity’s Exposed Claude Code Tokens

Do Son March 14, 2026 0

A 2026 audit of Perplexity Computer revealed exposed Claude Code tokens in config files. Learn how session-bound API keys could lead to massive billing debts.
AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP image-1200x720_1773385757UnFYetYvjm
  • Press Release

AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP

cybernewswire March 13, 2026 0
Menlo Park, California, USA, 13th March 2026, CyberNewswire
Read More Read more about AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP
45 Seconds to Empty: Ledger Unmasks Critical MediaTek Flaw That Turns Phones Into Glass Vaults MediaTek eavesdropping vulnerabilities MediaTek TEE vulnerability
  • Vulnerability Report

45 Seconds to Empty: Ledger Unmasks Critical MediaTek Flaw That Turns Phones Into Glass Vaults

Do Son March 13, 2026 0

Ledger Donjon uncovers a critical MediaTek TEE flaw allowing attackers to extract PINs and crypto seed phrases in 45 seconds. Patch now.

The Multiplier Model: OpenAI Leaks New $100 “ChatGPT Pro 5x” Tier to Bridge the Pro Gap ChatGPT Pro 5x
  • Technology

The Multiplier Model: OpenAI Leaks New $100 “ChatGPT Pro 5x” Tier to Bridge the Pro Gap

Do Son March 13, 2026 0

OpenAI is launching a $100 "ChatGPT Pro 5x" tier to bridge the gap between Plus and Pro. Experience 5x the compute power without the $200 price tag.
Network Hijack: Critical 9.8 CVSS Flaw in AdGuard Home Grants Hackers Full DNS Control AdGuard Home Vulnerability CVE-2026-32136
  • Vulnerability Report

Network Hijack: Critical 9.8 CVSS Flaw in AdGuard Home Grants Hackers Full DNS Control

Do Son March 13, 2026 0

A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.

Winter CMS Urgently Patches Critical 10.0 CVSS Privilege Escalation Flaw Winter CMS Vulnerability CVE-2026-27591
  • Vulnerability Report

Winter CMS Urgently Patches Critical 10.0 CVSS Privilege Escalation Flaw

Do Son March 13, 2026 0

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

Total Takeover: Veeam Patches Critical 9.9 CVSS RCE Flaws in Backup & Replication 12.3.2 Veeam RCE Vulnerability CVE-2026-21666 CVE-2024-40711 Veeam Backup & Replication
  • Vulnerability Report

Total Takeover: Veeam Patches Critical 9.9 CVSS RCE Flaws in Backup & Replication 12.3.2

Do Son March 13, 2026 0

Veeam urgently patches critical 9.9 CVSS RCE flaws (CVE-2026-21666, CVE-2026-21708) in Backup & Replication 12.3.2. Update your servers immediately.
Legacy Under Siege: Apple Pushes Emergency iOS 15.8.7 Update to Thwart ‘Coruna’ Exploit Kit Coruna Exploit Kit iOS Security Update Apple Zero-Day CVE-2026-20700 Apple Data Privacy Day 2026, iPhone privacy features guide iOS Privilege Escalation, CVE-2025-24085 PoC Apple Manufacturing Academy, US Investment CVE-2024-44258 - symlink vulnerability
  • Vulnerability Report

Legacy Under Siege: Apple Pushes Emergency iOS 15.8.7 Update to Thwart ‘Coruna’ Exploit Kit

Do Son March 13, 2026 0

Apple releases emergency iOS 15.8.7 and 16.7.15 updates for older iPhones to block the actively exploited "Coruna" WebKit and Kernel exploit kit. Patch now.

Breaking the Shield: ‘CrackArmor’ Flaws Expose 12.6 Million Linux Servers to Full Root Takeover CrackArmor AppArmor Vulnerabilities Linux Kernel UAF, Privilege Escalation PoC CVE-2024-27397 PoC
  • Linux
  • Vulnerability Report

Breaking the Shield: ‘CrackArmor’ Flaws Expose 12.6 Million Linux Servers to Full Root Takeover

Do Son March 13, 2026 0

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.