Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Unit 42 Unmasks CL-STA-1087’s Years-Long Cyber Espionage Against Asian Militaries UNC5221 HAFNIUM Extradition PRC State Espionage
  • Cyber Security
  • Malware

Unit 42 Unmasks CL-STA-1087’s Years-Long Cyber Espionage Against Asian Militaries

Do Son March 13, 2026 0

Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.

Apache Livy Patches Path Traversal and File Access Flaws Exposing Spark Clusters Apache Livy Security Path Traversal
  • Vulnerability Report

Apache Livy Patches Path Traversal and File Access Flaws Exposing Spark Clusters

Do Son March 13, 2026 0

Protect your Spark clusters: Apache Livy 0.9.0 patches two important file access and path traversal vulnerabilities (CVE-2025-60012 & CVE-2025-66249).

Veeam Urgently Patches Critical 9.9 CVSS RCE Flaws in Backup Servers Veeam RCE Vulnerability CVE-2026-21669 Veeam RCE, CVE-2025-48983 CVE-2025-48984
  • Vulnerability Report

Veeam Urgently Patches Critical 9.9 CVSS RCE Flaws in Backup Servers

Do Son March 13, 2026 0

Veeam releases a critical security update fixing 9.9 CVSS RCE flaws (CVE-2026-21669, CVE-2026-21708) in Backup & Replication. Patch servers immediately.
Critical 9.8 CVSS telnetd Buffer Overflow Grants Pre-Auth Root pre
  • Vulnerability

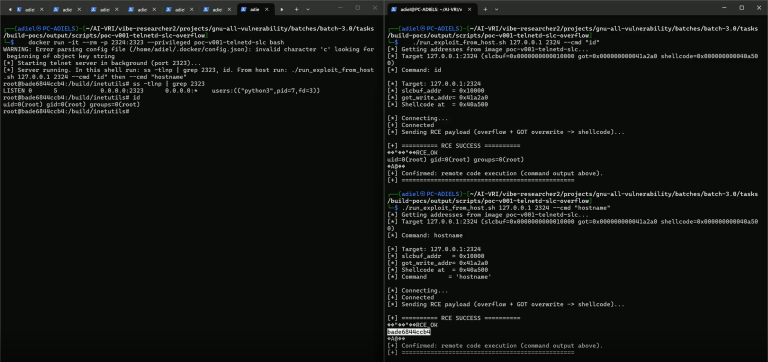
Critical 9.8 CVSS telnetd Buffer Overflow Grants Pre-Auth Root

Do Son March 13, 2026 0

A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.

The “CrashFix” Evolution: KongTuke’s New Playbook for Enterprise Infiltration UAT-8099 BadIIS Malware Pacific Islands Forum Cyberattack
  • Malware

The “CrashFix” Evolution: KongTuke’s New Playbook for Enterprise Infiltration

Do Son March 13, 2026 0

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

TaxiSpy RAT: New Android Banking Trojan Targets Russian Financial Sector Android zero day flaw June 2026 security bulletin RuTaxi Trojan Android Banking Malware Pixel 9 zero-click exploit, Dolby UDC vulnerability CVE-2025-54957 NexusRoute Android RAT, India E-Challan Phishing ClayRat Self-Defense, Android Accessibility Abuse Android Trojan, AntiDot Android Malware "BadPack"
  • Malware

TaxiSpy RAT: New Android Banking Trojan Targets Russian Financial Sector

Do Son March 13, 2026 0

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

A Single Line of Code: Pre-Auth OpenSSH Flaw Exposes Ubuntu and Debian Servers OpenSSH 10.3 Patch SSH Command Injection CVE-2023-38408 OpenSSH Vulnerability CVE-2026-3497
  • Vulnerability Report

A Single Line of Code: Pre-Auth OpenSSH Flaw Exposes Ubuntu and Debian Servers

Do Son March 13, 2026 0

A pre-auth flaw in OpenSSH's GSSAPI Key Exchange (CVE-2026-3497) exposes Ubuntu and Debian servers to heap corruption and data leaks. Patch now.
The Amphibious Gamer: How Google’s “Buy Once, Play Anywhere” Strategy is Taking on Steam Google Play PC cross-platform
  • Android

The Amphibious Gamer: How Google’s “Buy Once, Play Anywhere” Strategy is Taking on Steam

Do Son March 13, 2026 0

Google’s GDC 2026 updates bring "buy once, play anywhere" licenses and AI-powered "Sidekick" tips to PC and mobile. See how they're challenging Steam’s monopoly.
The Arm64 Vanguard: Valve Shatters x86 Hegemony with Steam Frame and “SteamOS on Arm” SteamOS on Arm
  • Technology

The Arm64 Vanguard: Valve Shatters x86 Hegemony with Steam Frame and “SteamOS on Arm”

Do Son March 13, 2026 0

Valve’s GDC 2026 reveal of "SteamOS on Arm" and the Steam Frame marks the end of x86 dominance. Discover the new 1080p/30FPS Steam Machine Verified standards.
Hardware Autonomy: Meta’s “High Velocity” Roadmap to Deploy Four AI Chips by 2027 Meta MTIA roadmap
  • Technology

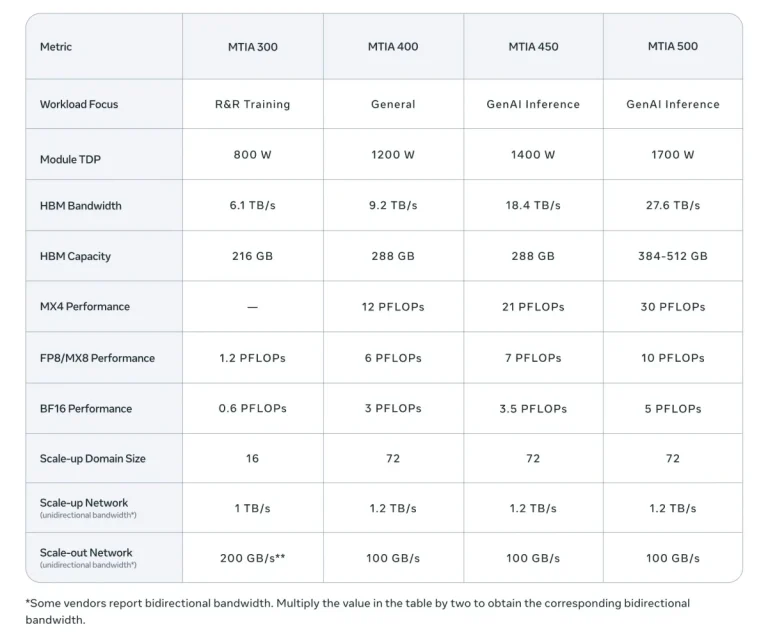
Hardware Autonomy: Meta’s “High Velocity” Roadmap to Deploy Four AI Chips by 2027

Do Son March 13, 2026 0

Meta shatters the industry standard with a 6-month chip cycle. Discover the MTIA 300-500 roadmap designed to slash AI costs and power 3 billion users by 2027.
The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode” Xbox Project Helix Xbox Mode Windows 11
  • Windows

The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode”

Do Son March 13, 2026 0

Microsoft’s new "Xbox Mode" brings a full-screen, controller-first console experience to all Windows 11 PCs this April. Say goodbye to shader stutter in 2026.

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws

Do Son March 12, 2026 0

Google releases an emergency Chrome update to patch two actively exploited zero-day vulnerabilities (CVE-2026-3909 & CVE-2026-3910). Update immediately.
The $32 Billion Fortress: Google Completes Historic Wiz Acquisition to Solve the “AI-Native” Risk Google Wiz acquisition 2026
  • Technology

The $32 Billion Fortress: Google Completes Historic Wiz Acquisition to Solve the “AI-Native” Risk

Do Son March 12, 2026 0

Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.

The Silicon Schism: Google Deploys 3 Million AI Agents to the Pentagon as Anthropic Faces Exile AI Overviews opt out Google Gemini Pentagon contract Penske Media, AI Overviews
  • Technology

The Silicon Schism: Google Deploys 3 Million AI Agents to the Pentagon as Anthropic Faces Exile

Do Son March 12, 2026 0

Google has deployed Gemini AI agents to 3 million Pentagon staff following a fallout with Anthropic. Discover the ethics shift and the new "GenAI.mil" portal.
Beyond the Formula: ChatGPT’s New “Dynamic Visuals” Turn Equations Into Interactive Sandboxes ChatGPT Dynamic Visual Explanations
  • Technology

Beyond the Formula: ChatGPT’s New “Dynamic Visuals” Turn Equations Into Interactive Sandboxes

Do Son March 12, 2026 0

ChatGPT’s new "Dynamic Visual Explanations" let you manipulate variables in real-time diagrams for 70+ math and science concepts. No more static formulas.

Agentic War: Amazon Secures Landmark Injunction to Block Perplexity’s AI Shopping Bot Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

Agentic War: Amazon Secures Landmark Injunction to Block Perplexity’s AI Shopping Bot

Do Son March 12, 2026 0

A San Francisco judge has blocked Perplexity’s Comet AI from buying on Amazon. Learn how this 2026 ruling defines the legal boundaries of agentic AI commerce.
One Vector to Rule Them All: How Gemini Embedding 2 Unifies Text, Audio, and Video Gemini Embedding 2
  • Technology

One Vector to Rule Them All: How Gemini Embedding 2 Unifies Text, Audio, and Video

Do Son March 12, 2026 0

Google DeepMind’s Gemini Embedding 2 is here. Map text, images, 120s of video, and native audio into one vector space to revolutionize multimodal RAG and search.
The Mutable Tag Trap: Critical 9.4 CVSS Attack on Xygeni GitHub Action Exposes CI/CD Pipelines Xygeni Tag Poisoning CVE-2026-31976
  • Malware
  • Vulnerability Report

The Mutable Tag Trap: Critical 9.4 CVSS Attack on Xygeni GitHub Action Exposes CI/CD Pipelines

Do Son March 12, 2026 0

A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
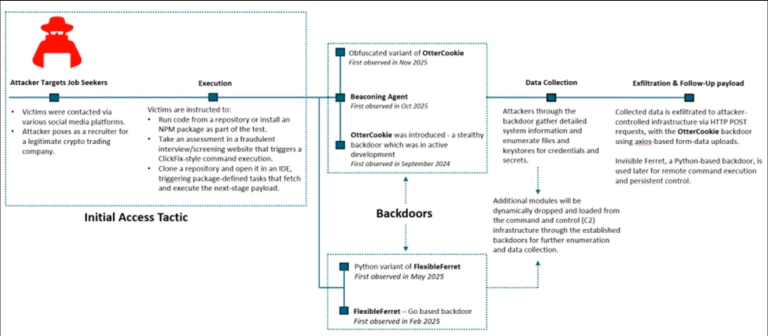
The Fake Job Trap: Microsoft Exposes the ‘Contagious Interview’ Campaign Targeting Developers Contagious Interview Invisible Ferret
  • Cybercriminals

The Fake Job Trap: Microsoft Exposes the ‘Contagious Interview’ Campaign Targeting Developers

Do Son March 12, 2026 0

Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
CISA Mandates Urgent Patch for Maximum 10.0 CVSS n8n RCE Flaw n8n RCE Vulnerability CVE-2025-68613 CISA KEV WinRAR Zero-Day, Cloud Files UAF OpenPLC ScadaBR, CVE-2021-26829 CISA KEV, Gladinet LFI RCE XWiki RCE, VMware EoP CISA KEV CISA, Known Exploited Vulnerabilities CVE-2020-2883 CISA, Trend Micro
  • Vulnerability Report

CISA Mandates Urgent Patch for Maximum 10.0 CVSS n8n RCE Flaw

Do Son March 12, 2026 0

CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.

High-Privilege Havoc: Splunk Patches RCE Flaw Lurking in File Previews Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

High-Privilege Havoc: Splunk Patches RCE Flaw Lurking in File Previews

Do Son March 12, 2026 0

Splunk warns of a high-severity RCE flaw (CVE-2026-20163) in its REST API. Attackers with edit_cmd rights can execute arbitrary commands. Patch immediately.
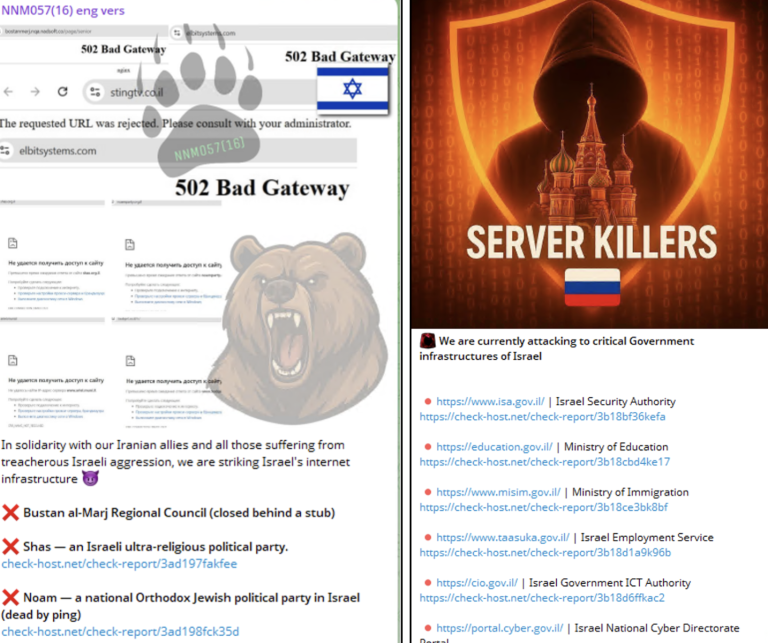
Cyber Escalation in the Middle East: Disruption, Deception, and the Quest for Data State-Sponsored Espionage
  • Cyber Security
  • Vulnerability Report

Cyber Escalation in the Middle East: Disruption, Deception, and the Quest for Data

Do Son March 12, 2026 0

Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.