Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
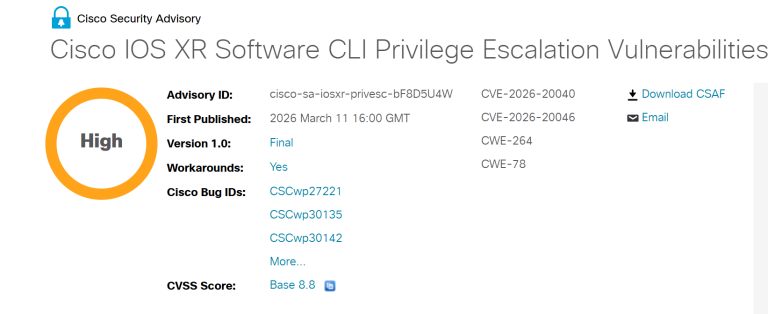
Root Access via CLI: Cisco Patches Critical IOS XR Privilege Escalation Flaws Cisco IOS XR Vulnerability CVE-2026-20040
  • Vulnerability Report

Root Access via CLI: Cisco Patches Critical IOS XR Privilege Escalation Flaws

Do Son March 12, 2026 0

Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.
Iran-Aligned TA453 Weaponizes ‘Operation Epic Fury’ for Cyber Espionage Operation Epic Fury TA453 Phishing
  • Cyber Security

Iran-Aligned TA453 Weaponizes ‘Operation Epic Fury’ for Cyber Espionage

Do Son March 12, 2026 0

Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
The Dark Side of Telegram: How Cybercriminals Weaponize Bot APIs for Stealthy Data Exfiltration Telegram Bot API Data Exfiltration
  • Cybercriminals

The Dark Side of Telegram: How Cybercriminals Weaponize Bot APIs for Stealthy Data Exfiltration

Do Son March 12, 2026 0

A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

Chrome 146 Arrives with 29 Security Fixes: Critical WebML Flaw Discovered Chrome 146 Security CVE-2026-3913
  • Vulnerability Report

Chrome 146 Arrives with 29 Security Fixes: Critical WebML Flaw Discovered

Do Son March 12, 2026 0

Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

Code Red: GitLab’s Latest Security Update Patches High-Severity XSS and API DoS Vulnerabilities GitLab Security Update Account Impersonation GitLab Security Update CVE-2026-1090 GitLab vulnerability GitLab vulnerability, GitLab patches
  • Vulnerability Report

Code Red: GitLab’s Latest Security Update Patches High-Severity XSS and API DoS Vulnerabilities

Do Son March 12, 2026 0

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

Operation False Siren: The Weaponization of Israel’s Red Alert App for Geo-Fenced Espionage Goldoon Botnet Operation False Siren Red Alert Spyware
  • Cybercriminals

Operation False Siren: The Weaponization of Israel’s Red Alert App for Geo-Fenced Espionage

Do Son March 12, 2026 0

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
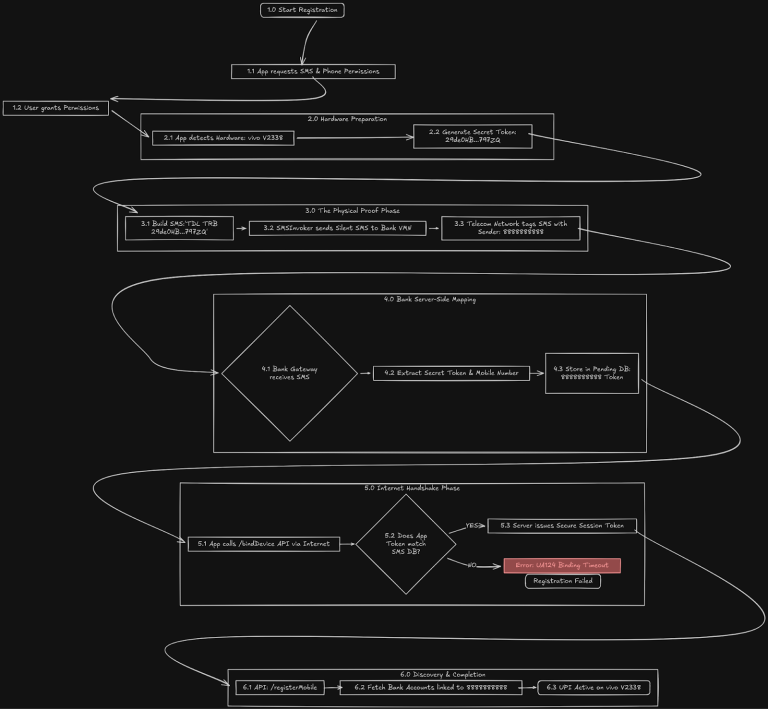
Gaslighting Android: How the ‘Digital Lutera’ Attack Uses LSPosed to Bypass UPI SIM-Binding UPI SIM-Binding Bypass LSPosed Framework
  • Malware

Gaslighting Android: How the ‘Digital Lutera’ Attack Uses LSPosed to Bypass UPI SIM-Binding

Do Son March 12, 2026 0

CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.

The Sleeper in Your Toolbar: How a “Featured” Chrome Extension Turned Into a Full-Scale Infostealer ShotBird extension malware
  • Malware

The Sleeper in Your Toolbar: How a “Featured” Chrome Extension Turned Into a Full-Scale Infostealer

Do Son March 12, 2026 0

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.
How CTEM Allows Security Teams to Uncover What Attackers Already See Salesforce vulnerability CVE-2025-9844 Salt Typhoon cyberattack
  • Technique

How CTEM Allows Security Teams to Uncover What Attackers Already See

Do Son March 11, 2026 0
Most security teams operate from the inside out. They rely on logs and alerts to see what’s...
Read More Read more about How CTEM Allows Security Teams to Uncover What Attackers Already See
Critical 9.8 CVSS Bypass Unearthed in HPE Aruba AOS-CX Switches CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability Report

Critical 9.8 CVSS Bypass Unearthed in HPE Aruba AOS-CX Switches

Do Son March 11, 2026 0

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

The ‘Must-Patch’ Release: WordPress 6.9.2 Scrambles to Fix 10 Critical Flaws from XSS to SSRF WordPress 6.9.2 WordPress 6.9.2 WordPress Security Update WordPress Security Update WordPress.org Suspended
  • Vulnerability Report

The ‘Must-Patch’ Release: WordPress 6.9.2 Scrambles to Fix 10 Critical Flaws from XSS to SSRF

Do Son March 11, 2026 0

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.

High-Severity SQL Injection in Ally WordPress Plugin Threatens 400K Sites Ally Plugin Vulnerability SQL Injection
  • Vulnerability Report

High-Severity SQL Injection in Ally WordPress Plugin Threatens 400K Sites

Do Son March 11, 2026 0

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.

The Default Danger: Maximum 10.0 CVSS Vulnerability Leaves Honeywell IQ4x Controllers Wide Open Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

The Default Danger: Maximum 10.0 CVSS Vulnerability Leaves Honeywell IQ4x Controllers Wide Open

Do Son March 11, 2026 0

A critical 10.0 CVSS flaw (CVE-2026-3611) in Honeywell IQ4x BMS controllers leaves web HMIs exposed without authentication. Secure your systems immediately.
Industrial Alert: Critical Stored XSS Vulnerability Discovered in Siemens SIMATIC S7-1500 Siemens SIMATIC Vulnerability CVE-2025-40943 CVE-2024-47901 - Siemens InterMesh system CVE-2025-40804 Siemens SIVaaS
  • Vulnerability Report

Industrial Alert: Critical Stored XSS Vulnerability Discovered in Siemens SIMATIC S7-1500

Do Son March 11, 2026 0

A critical 9.6 CVSS XSS vulnerability (CVE-2025-40943) in Siemens SIMATIC S7-1500 CPUs allows attackers to inject malicious code via trace files.

Microsoft Patch Tuesday March 2026: 93 Vulnerabilities Addressed, Including Two Zero-Days Microsoft Patch Tuesday fixes disclosed zero day vulnerabilities Windows Wormable Exploit April 2026 Patch Tuesday Microsoft Patch Tuesday Zero-Day Vulnerabilities Microsoft, Patch Tuesday CVE-2025-55234 CVE-2024-43573 and CVE-2024-43572 Microsoft Patch Tuesday Security Vulnerabilities
  • Vulnerability Report

Microsoft Patch Tuesday March 2026: 93 Vulnerabilities Addressed, Including Two Zero-Days

Do Son March 11, 2026 0

Microsoft's March 2026 Patch Tuesday addresses 93 vulnerabilities, including two public zero-days affecting SQL Server and .NET. Patch your systems now.

Maximum 10.0 CVSS Flaws in OneUptime Allow Full Account Takeovers and RCE OneUptime Vulnerabilities CVE-2026-30956
  • Vulnerability Report

Maximum 10.0 CVSS Flaws in OneUptime Allow Full Account Takeovers and RCE

Do Son March 11, 2026 0

Two critical 10.0 CVSS flaws (CVE-2026-30956, CVE-2026-30957) in OneUptime allow full account takeovers and Server-Side RCE. Update to 10.0.21 immediately.
Malicious npm Package “pino-sdk-v2” Caught Harvesting Secrets pino-sdk-v2 npm Supply Chain Attack
  • Malware

Malicious npm Package “pino-sdk-v2” Caught Harvesting Secrets

Do Son March 11, 2026 0

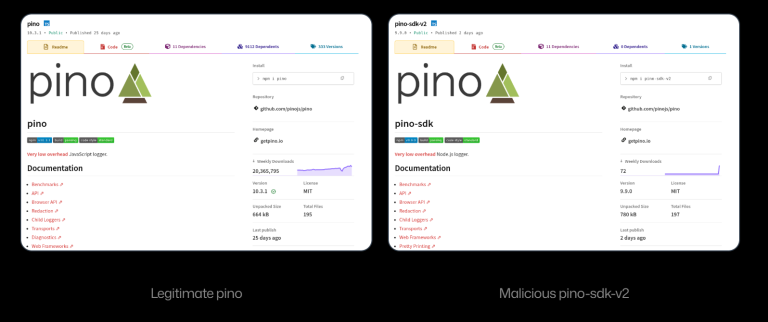
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
APT-C-23 Weaponized Israel’s ‘Red Alert’ App for Mobile Espionage Red Alert Trojan APT-C-23
  • Cybercriminals

APT-C-23 Weaponized Israel’s ‘Red Alert’ App for Mobile Espionage

Do Son March 11, 2026 0

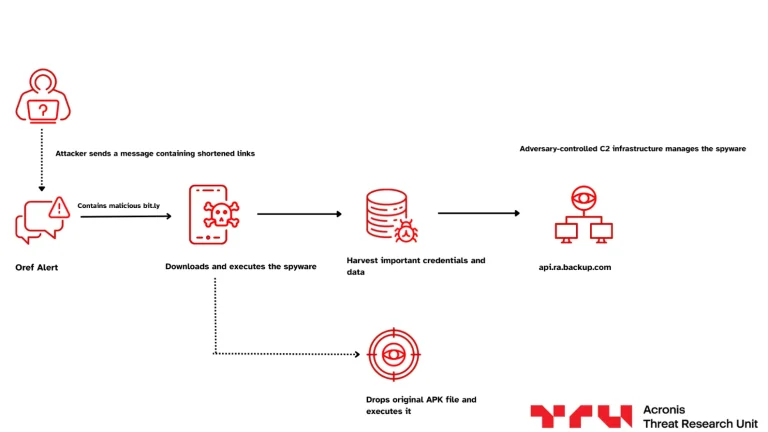
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
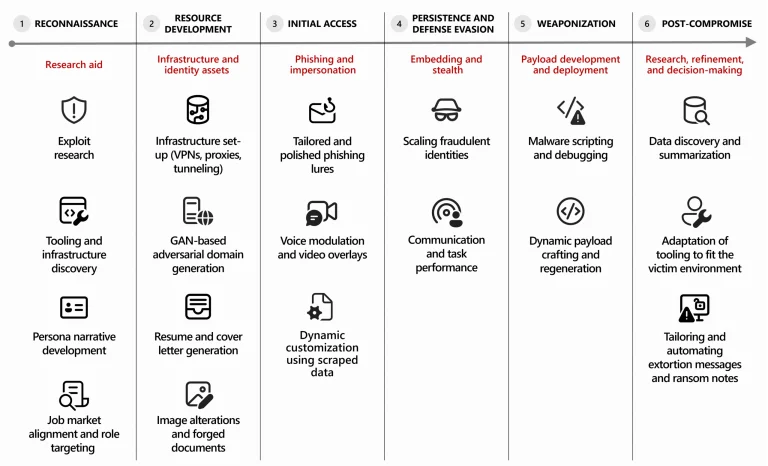
Microsoft Exposes How Hackers Use Generative Models as a Force Multiplier Malicious AI AI Memory Poisoning
  • Cybercriminals

Microsoft Exposes How Hackers Use Generative Models as a Force Multiplier

Do Son March 11, 2026 0

Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
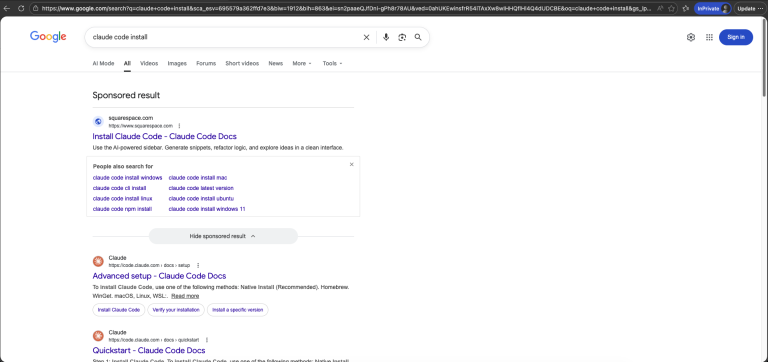
The Vibe-Coding Trap: Fake Claude Code Installers Unleash Amatera Malware via Search Ads Claude Code Malvertising Amatera Malware
  • Malware

The Vibe-Coding Trap: Fake Claude Code Installers Unleash Amatera Malware via Search Ads

Do Son March 11, 2026 0

Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.

Zscaler Uncovers 8,000+ Domains and APT Backdoors Exploiting Middle East Tensions Middle East Cyber Threats
  • Cybercriminals

Zscaler Uncovers 8,000+ Domains and APT Backdoors Exploiting Middle East Tensions

Do Son March 11, 2026 0

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.
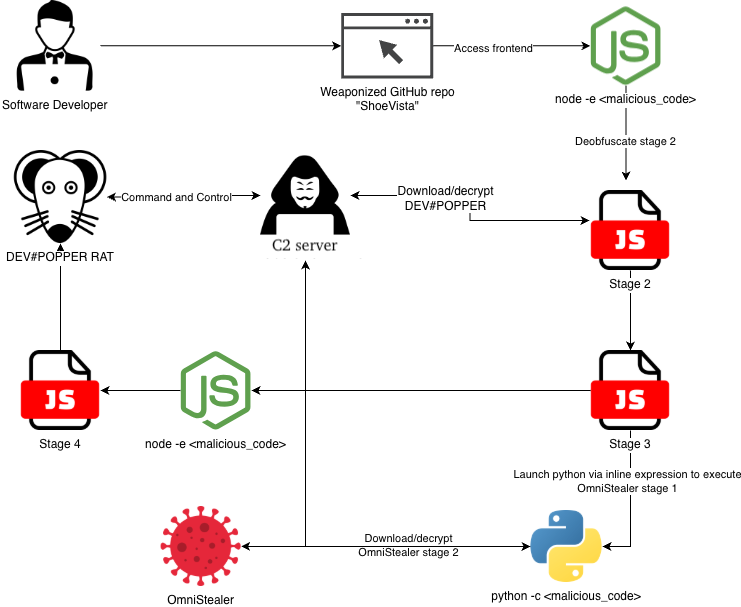
North Korean APT Unleashes DEV#POPPER RAT via GitHub to Drain Crypto Wallets DEV#POPPER OmniStealer
  • Malware

North Korean APT Unleashes DEV#POPPER RAT via GitHub to Drain Crypto Wallets

Do Son March 11, 2026 0

eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.