 Do Son
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Critical flaws (CVE-2025-41709) in Janitza and Weidmueller energy meters allow remote code execution and full system takeover. Update to firmware 3.14 now.
Zoom patches a critical 9.6 CVSS flaw (CVE-2026-30903) allowing unauthenticated remote privilege escalation on Windows. Update your clients immediately.
CISA adds three actively exploited flaws in SolarWinds, Ivanti, and Omnissa to its KEV catalog. Patch these critical enterprise vulnerabilities immediately.
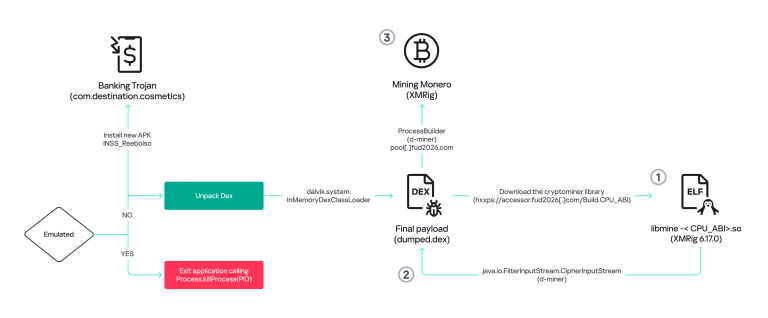
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.
 cybernewswire

In the gig economy, your face is your brand. Before a prospect reads your proposal, scrolls through...

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.

SAP's latest security update addresses 15 flaws, including critical RCE (CVE-2019-17571) and deserialization (CVE-2026-27685) vulnerabilities. Patch now.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.
Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture

Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture
OpenAI has acquired AI security vanguard Promptfoo. Discover how this $86M deal will automate red-teaming and protect AI agents from prompt injection in 2026.

Google’s experimental Workspace CLI ends the era of AI account bans, offering a "skills" bridge for agents like OpenClaw and Claude to automate Gmail and Drive.
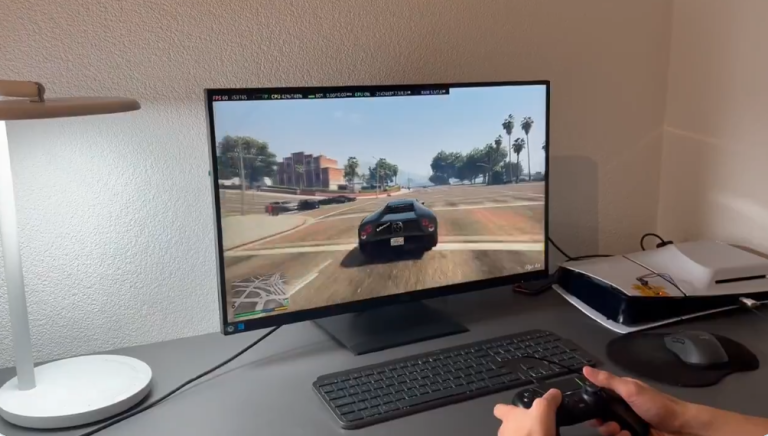
Security researcher Andy Nguyen has successfully ported Linux to the PS5, running Steam and GTA V at 1440p/60FPS with Ray Tracing. See the future of PS5 modding.

Microsoft’s new native NVMe driver (nvmedisk.sys) boosts 4K random reads by 65% and slashes CPU load. Learn how to unlock this hidden feature in Windows 11.
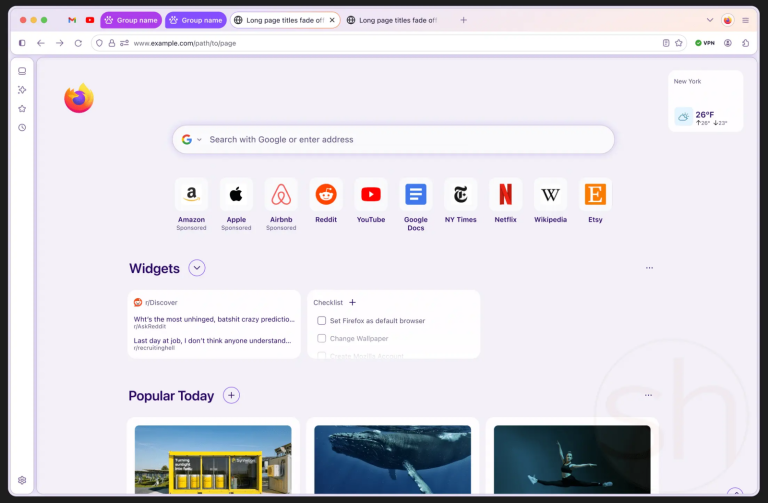
Mozilla’s "Project NOVA" is a 3D, floating-element reimagining of the Firefox UI. See the leaked wireframes of the biggest browser metamorphosis since 2021.

X's new "anti-bot" audit has backfired, silencing legitimate users with unlocked bootloaders or jailbroken phones. Is your device now "unauthorized" to post?
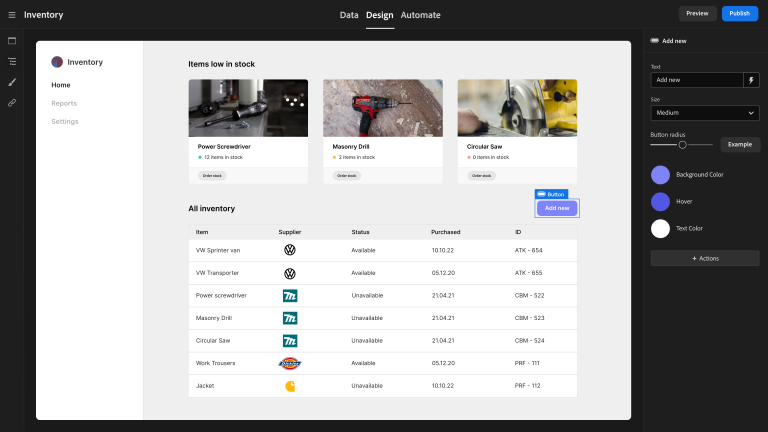
Two critical flaws in Budibase (CVE-2026-31816, CVE-2026-30240) allow unauthenticated API access and secret exfiltration via path traversal. Patch immediately.

A critical 9.8 CVSS authentication bypass (CVE-2026-0953) in Tutor LMS Pro is being actively exploited in the wild. Update to version 3.9.6 immediately.

A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.
A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.

Discover how attackers use shadow archives (CVE-2026-0866) to bypass AV and EDR by malforming ZIP metadata, keeping malware hidden but executable.
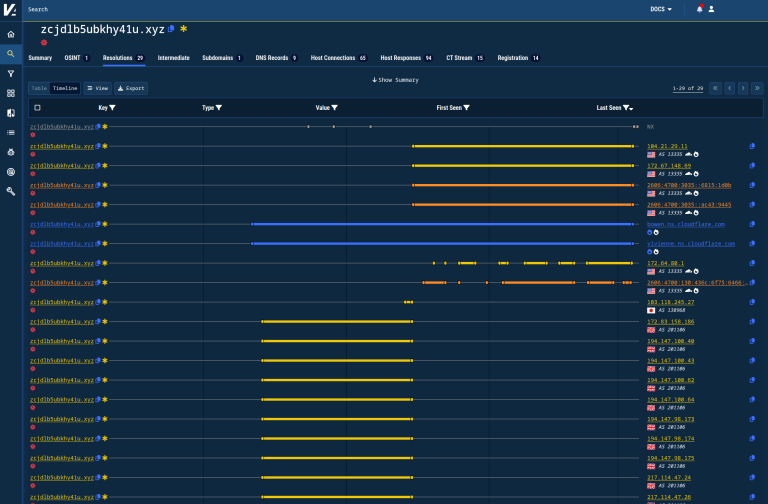
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.