Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Fake CleanMyMac Site Unleashes SHub Stealer to Drain macOS Crypto Wallets SHub Stealer Mac Malware
  • Malware

Fake CleanMyMac Site Unleashes SHub Stealer to Drain macOS Crypto Wallets

Do Son March 10, 2026 0

A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.

Critical 9.8 CVSS Flaws Expose SICK Lector Scanners to Hijacking SICK Lector Vulnerability CVE-2026-2331 CVE-2022-0778 and CVE-2025-0867
  • Vulnerability Report

Critical 9.8 CVSS Flaws Expose SICK Lector Scanners to Hijacking

Do Son March 10, 2026 0

SICK PSIRT warns of critical vulnerabilities (CVE-2026-2330, CVE-2026-2331) in Lector85x and Lector83x scanners allowing full device takeover. Update now.
Malicious “Hex Visualizer” Chrome Extension Targeting imToken Users Crypto Wallet Drainer ImToken Phishing
  • Cybercriminals

Malicious “Hex Visualizer” Chrome Extension Targeting imToken Users

Do Son March 10, 2026 0

Socket researchers uncover "ImToken Chromophore," a malicious Chrome extension using fake branding and homoglyphs to steal crypto wallet seed phrases.
Critical 9.3 CVSS Flaw in Gogs Turns Repositories into Malware Delivery Vectors Gogs LFS Vulnerability CVE-2026-25921
  • Vulnerability Report

Critical 9.3 CVSS Flaw in Gogs Turns Repositories into Malware Delivery Vectors

Do Son March 10, 2026 0

A critical 9.3 CVSS flaw (CVE-2026-25921) in Gogs' LFS handling allows attackers to silently overwrite repository files, risking severe supply-chain attacks.

Agencies Issue Urgent Warning on INC Ransom Healthcare Attacks INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Cybercriminals

Agencies Issue Urgent Warning on INC Ransom Healthcare Attacks

Do Son March 10, 2026 0

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
Critical Request Smuggling & Cache Flaws Discovered in Cloudflare’s Pingora Pingora Vulnerabilities Cloudflare Pingora
  • Vulnerability Report

Critical Request Smuggling & Cache Flaws Discovered in Cloudflare’s Pingora

Do Son March 10, 2026 0

Discover three critical flaws (including CVE-2026-2835) in Cloudflare's Pingora Rust framework causing request smuggling and cache poisoning. Update now.
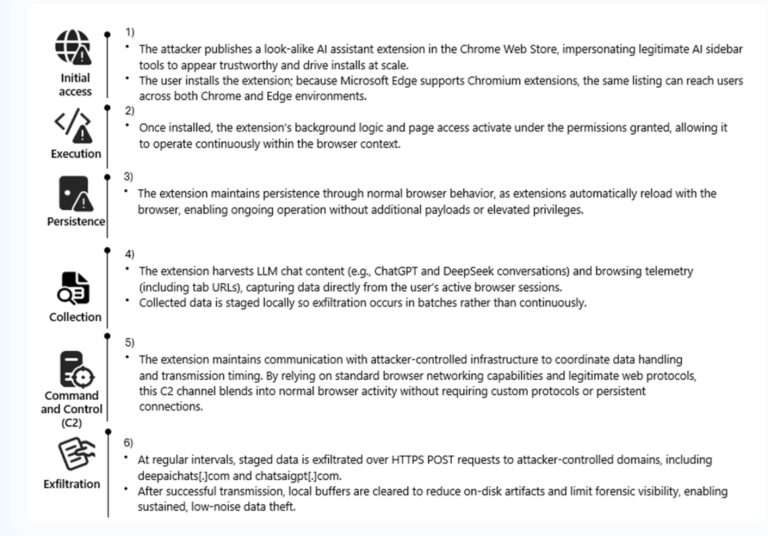
The Spy in Your Sidebar: Fake AI Browser Extensions Steal Data from 900,000 Users Malicious AI Extensions Chromium Browser Security
  • Malware

The Spy in Your Sidebar: Fake AI Browser Extensions Steal Data from 900,000 Users

Do Son March 10, 2026 0

Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.
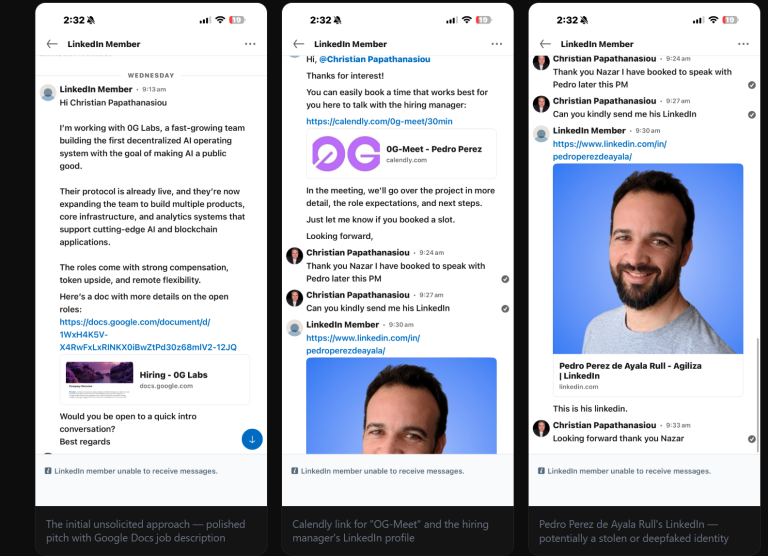
The ‘Contagious Interview’ Trap: How a Web3 CEO Unmasked North Korean Stealth Malware Contagious Interview North Korean Malware
  • Cybercriminals

The ‘Contagious Interview’ Trap: How a Web3 CEO Unmasked North Korean Stealth Malware

Do Son March 10, 2026 0

A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.
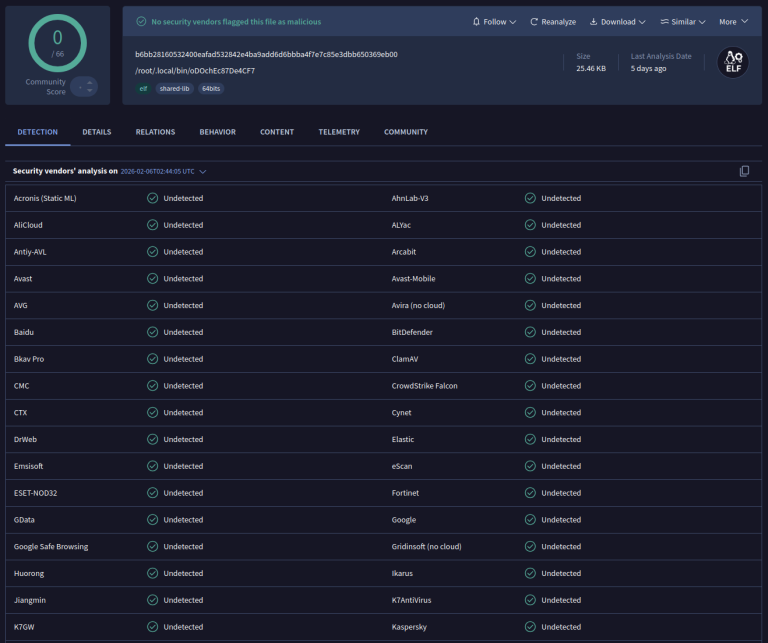
Silently Swapped: How ClipXDaemon Hijacks Linux Cryptowallets Without a C2 Server ClipXDaemon Linux Malware
  • Malware

Silently Swapped: How ClipXDaemon Hijacks Linux Cryptowallets Without a C2 Server

Do Son March 10, 2026 0

Cyble Research unmasks ClipXDaemon, a C2-less Linux malware that silently hijacks cryptocurrency wallet addresses in X11 clipboard environments.
Security Risk Advisors Releases “The Purple Perspective 2026” Report purple-perspective-social-press2_1772821885s5aslCzJZX
  • Press Release

Security Risk Advisors Releases “The Purple Perspective 2026” Report

cybernewswire March 9, 2026 0
Philadelphia, PA, United States, 9th March 2026, CyberNewswire
Read More Read more about Security Risk Advisors Releases “The Purple Perspective 2026” Report
AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision AWS Phishing AiTM Attack
  • Cybercriminals

AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision

Do Son March 9, 2026 0

Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Industrial Alert: Urgent Apache IoTDB Patches Fix RCE and “Open Door” Default Flaws Apache IoTDB JEXL injection Apache IoTDB, Security Vulnerabilities
  • Vulnerability

Industrial Alert: Urgent Apache IoTDB Patches Fix RCE and “Open Door” Default Flaws

Do Son March 9, 2026 0

Apache IoTDB issues an urgent fix for a critical JEXL injection flaw (CVE-2026-24713) and insecure defaults. Upgrade to 1.3.7 or 2.0.7 to secure your IIoT data.
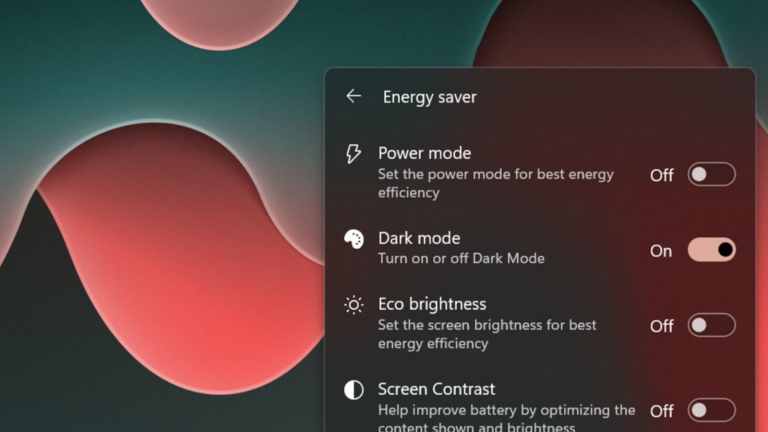
The Hidden Toggle: Why Windows 11’s New One-Click Dark Mode is Hiding in Your Battery Settings Windows 11 Dark Mode toggle
  • Windows

The Hidden Toggle: Why Windows 11’s New One-Click Dark Mode is Hiding in Your Battery Settings

Do Son March 9, 2026 0

Microsoft finally adds a one-click Dark Mode toggle to the Windows 11 taskbar—but it's hidden in the Energy Saver menu. Is this a genius move or a UI fail?
The AI Arms Race for Developers: OpenAI Counters Anthropic with “Codex for Open Source” Codex rate limit reset OpenAI Codex limits, flexible rate limit resets, Codex vs Claude Code Vibe coding software engineer jobs OpenAI Codex for Open Source
  • Technology

The AI Arms Race for Developers: OpenAI Counters Anthropic with “Codex for Open Source”

Do Son March 9, 2026 0

OpenAI's new "Codex for Open Source" offers maintainers 6 months of ChatGPT Pro and Codex Security. Is your repository eligible for this $1,200 AI grant?

The Robotics Revolt: Why OpenAI’s Top Hardware Executive Quit Over the Pentagon’s New AI Pact OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Robotics Revolt: Why OpenAI’s Top Hardware Executive Quit Over the Pentagon’s New AI Pact

Do Son March 9, 2026 0

OpenAI's robotics lead Caitlin Kalinowski resigns in a "crisis of governance" over the Pentagon deal. Discover the "red lines" shaking the AI industry in 2026.

The Ethics Embargo: Why the Pentagon Blacklisted Anthropic and the Tech Giants Struck Back Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The Ethics Embargo: Why the Pentagon Blacklisted Anthropic and the Tech Giants Struck Back

Do Son March 9, 2026 0

The Pentagon brands Anthropic a "Supply-Chain Risk" over ethical AI refusals. See how Microsoft, Google, and Amazon are defying the military to save Claude.

Nintendo Sues the U.S. Government Over “Unlawful” Trump Tariffs Nintendo tariff lawsuit 2026 Nintendo Switch 2, MIG Tool Nintendo Switch 2, USB-C Restrictions Nintendo Switch 2, Vulnerability
  • Technology

Nintendo Sues the U.S. Government Over “Unlawful” Trump Tariffs

Do Son March 9, 2026 0

Nintendo sues the U.S. for a full refund of "unlawful" Trump tariffs. Discover how the 2026 IEEPA ruling could shift the price of the Nintendo Switch 2.

Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Cyber Security
  • Malware

Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor

Do Son March 9, 2026 0

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Escalation in the Shadows: Iranian APT Seedworm Deploys ‘Dindoor’ Backdoor in New Cyberoffensive Vulnerability Digest Zero-Day Exploits Seedworm APT Dindoor Backdoor RedKitten Campaign AI-Generated Malware WSUS RCE ShadowPad CVE-2025-59287
  • Cyber Security
  • Malware

Escalation in the Shadows: Iranian APT Seedworm Deploys ‘Dindoor’ Backdoor in New Cyberoffensive

Do Son March 9, 2026 0

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

Fake GitHub Repositories Unleash BoryptGrab Stealer and TunnesshClient Backdoor TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Fake GitHub Repositories Unleash BoryptGrab Stealer and TunnesshClient Backdoor

Do Son March 9, 2026 0

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.
Critical 9.4 CVSS Zephyr RTOS Flaw Exposes Millions of IoT Devices to RCE Zephyr RTOS Vulnerability CVE-2026-1678
  • Vulnerability Report

Critical 9.4 CVSS Zephyr RTOS Flaw Exposes Millions of IoT Devices to RCE

Do Son March 9, 2026 0

A critical 9.4 CVSS buffer overflow flaw (CVE-2026-1678) in Zephyr RTOS's DNS parser allows unauthenticated RCE on IoT devices. Patch immediately.
Vault Unlocked: High-Severity Flaws in Vaultwarden Expose Encrypted Secrets and Allow Privilege Escalation Vaultwarden Vulnerabilities CVE-2026-27898
  • Vulnerability Report

Vault Unlocked: High-Severity Flaws in Vaultwarden Expose Encrypted Secrets and Allow Privilege Escalation

Do Son March 9, 2026 0

Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.