Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
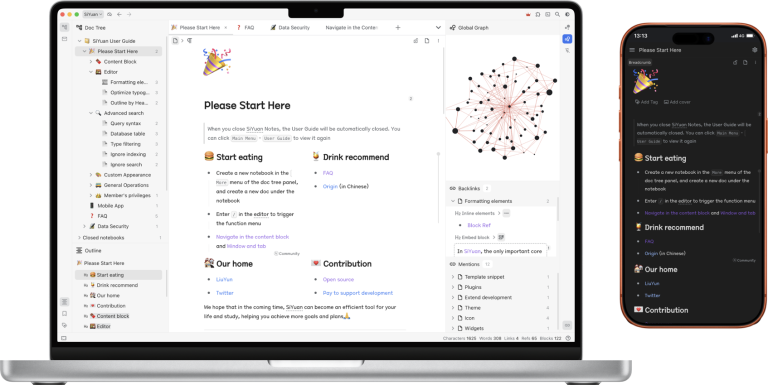
Critical 9.3 CVSS Flaw in SiYuan Lets Hackers Steal Private Notes via SVG Injection SiYuan XSS Vulnerability CVE-2026-29183
  • Vulnerability Report

Critical 9.3 CVSS Flaw in SiYuan Lets Hackers Steal Private Notes via SVG Injection

Do Son March 9, 2026 0

A critical 9.3 CVSS reflected XSS flaw (CVE-2026-29183) in SiYuan's dynamic icon API lets attackers steal private notes via SVG injection. Update now.

Critical Bypasses and Secret Leaks Patched in Apache ZooKeeper CVE-2023-44981 Apache ZooKeeper Vulnerabilities CVE-2026-24281
  • Vulnerability Report

Critical Bypasses and Secret Leaks Patched in Apache ZooKeeper

Do Son March 9, 2026 0

Apache ZooKeeper vulnerabilities (CVE-2026-24281, CVE-2026-24308) allow PTR record spoofing and sensitive data leaks in logs. Update clusters immediately.

Polygon Powered: Vietnamese Operator Deploys 16 Generations of LuaJIT Malware via GitHub Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

Polygon Powered: Vietnamese Operator Deploys 16 Generations of LuaJIT Malware via GitHub

Do Son March 9, 2026 0

Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.

1-Click to Compromise: Critical 9.3 CVSS Flaw in ZITADEL Exposes Accounts to Full Takeover ZITADEL Vulnerability CVE-2026-29191 CVE-2025-27507 ZITADEL SSRF, Login UI Hijack
  • Vulnerability Report

1-Click to Compromise: Critical 9.3 CVSS Flaw in ZITADEL Exposes Accounts to Full Takeover

Do Son March 9, 2026 0

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.

From Theory to Threat: Hackers Are Now Weaponizing Web Pages to Brainwash AI Agents axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Cybercriminals

From Theory to Threat: Hackers Are Now Weaponizing Web Pages to Brainwash AI Agents

Do Son March 9, 2026 0

Unit 42 reveals the first real-world cases of Indirect Prompt Injection (IDPI), where hackers weaponize website content to bypass AI security filters.

Dust Specter: Iran-Linked Hackers Weaponize Iraqi Government Sites in New Cyber Espionage Campaign Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

Dust Specter: Iran-Linked Hackers Weaponize Iraqi Government Sites in New Cyber Espionage Campaign

Do Son March 9, 2026 0

Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.

Unauthenticated Nginx UI Flaw Leaks Decryption Keys and Server Secrets Nginx UI Vulnerability CVE-2026-27944
  • Vulnerability Report

Unauthenticated Nginx UI Flaw Leaks Decryption Keys and Server Secrets

Do Son March 8, 2026 0

A critical 9.8 CVSS flaw (CVE-2026-27944) in Nginx UI lets hackers download and decrypt full system backups via an open API. Update and rotate secrets!
AI vs. Bugs: OpenAI Launches “Codex Security” to Revolutionize AppSec OpenAI Advanced Account Security Phishing-Resistant AI Authentication OpenAI Codex Security AI Application Security
  • Technology

AI vs. Bugs: OpenAI Launches “Codex Security” to Revolutionize AppSec

Do Son March 7, 2026 0

OpenAI launches Codex Security, an advanced AI agent that uses reasoning to find and fix complex vulnerabilities without the noise of false positives.

The Silicon Squeeze: Apple Sacrifices High-End Memory to Survive the Global AI Chip Famine Apple memory supply chain crisis
  • Technology

The Silicon Squeeze: Apple Sacrifices High-End Memory to Survive the Global AI Chip Famine

Do Son March 7, 2026 0

Apple overhauls its hardware lineup amidst a global DRAM famine. Discover why the 512GB Mac Studio is extinct and how the MacBook Air is being reborn.

The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright AI pre-release vetting AI copyright law US UK FoundationMotion, AI Motion Understanding AI Deregulation, DOGE AI Self-Preservation, GPT-4o Country of Geniuses
  • Technology

The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright

Do Son March 7, 2026 0

The US Supreme Court denies AI-generated copyright, while the UK suspends its controversial "opt-out" data bill. Is the era of free AI training over?
Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security Employees Risk
  • Technique

Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security

Do Son March 6, 2026 0
Identity is now the primary target in cyberattacks. Attackers go after authentication systems—especially Microsoft Active Directory (AD)....
Read More Read more about Identity Under Attack: Why Deception Is Becoming Essential for Active Directory Security
The “Threads” Trap: How X is Weaponizing Narrative Suspense to Dethrone Meta X Creator Subscriptions 2.0
  • Technology

The “Threads” Trap: How X is Weaponizing Narrative Suspense to Dethrone Meta

Do Son March 6, 2026 0

X launches "Exclusive Threads," a masterful 2.0 upgrade that lets creators paywall the climax of their stories. See how suspense is the new currency for 2026.

The Ruwiki Sleeper: How a Slumbering JavaScript Worm Paralyzed Wikipedia’s Global Infrastructure Wikipedia JavaScript worm Wikimedia Enterprise AI partners, Wikipedia 25th anniversary monetization Wikipedia down Wikipedia Paid API AI Traffic Decline
  • Technology

The Ruwiki Sleeper: How a Slumbering JavaScript Worm Paralyzed Wikipedia’s Global Infrastructure

Do Son March 6, 2026 0

A dormant ruwiki script triggered a global Wikipedia lockdown. Discover how a 23-minute JavaScript worm compromised admins and forced a read-only mandate.
The Torrent Titanic Sinks: YggTorrent Breached as Hackers Expose “Turbo” Tier Greed and 54,000 Credit Cards Booking.com Data Breach Claude Code Leak Anthropic Source Code YggTorrent data breach PS5 BootROM key leak 2026, PlayStation 5 unpatchable jailbreak Great Firewall data leak Dating App Breach, Tea App Leak 23andMe Data Leak
  • Data Leak

The Torrent Titanic Sinks: YggTorrent Breached as Hackers Expose “Turbo” Tier Greed and 54,000 Credit Cards

Do Son March 6, 2026 0

YggTorrent infrastructure falls to unknown hackers. Discover the massive 54,000 credit card leak, the "Turbo" tier scandal, and the new ygg.gratis clone.

Unmasking the Shadows: A Global Hunt for PlugX Staging Infrastructure Mustang Panda C2 Procurement
  • Malware

Unmasking the Shadows: A Global Hunt for PlugX Staging Infrastructure

Do Son March 6, 2026 0

Researcher @goyaramen reveals how PRC threat actors like Mustang Panda use expired domains and Cloudflare to mask their PlugX C2 infrastructure.
Unmasking Genisys: The AI-Powered Ad Fraud Scheme Silently Hijacking Your Smartphone Genisys Ad Fraud
  • Malware

Unmasking Genisys: The AI-Powered Ad Fraud Scheme Silently Hijacking Your Smartphone

Do Son March 6, 2026 0

IAS Threat Lab unmasks Genisys, a massive AI-powered mobile ad fraud scheme hijacking smartphones to generate fake traffic and steal from advertisers.
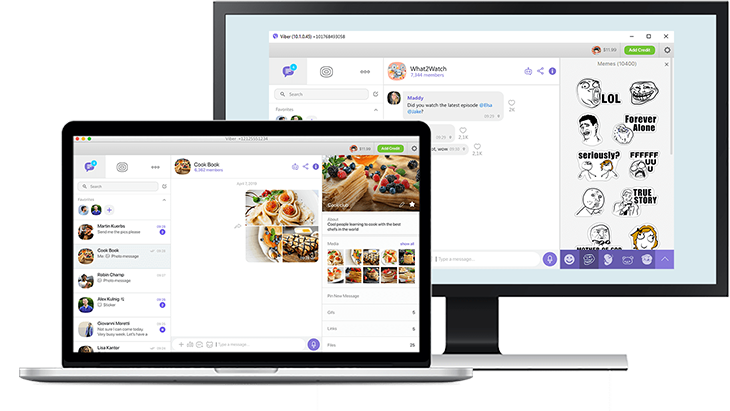
Exposed in Plain Sight: Critical Privacy Flaw Defeats Viber’s Anti-Censorship ‘Cloak’ Mode Viber Cloak Vulnerability CVE-2025-13476
  • Vulnerability Report

Exposed in Plain Sight: Critical Privacy Flaw Defeats Viber’s Anti-Censorship ‘Cloak’ Mode

Do Son March 6, 2026 0

CERT/CC reveals a major privacy flaw (CVE-2025-13476) in Viber's Cloak mode, allowing network censors to easily identify and block proxy traffic. Update now.

OpenAI Unveils GPT-5.4: The “Professional” Frontier with Native Computer Control and 1M Token Context ChatGPT advertising US only OpenAI GPT-5.4 launch OpenAI Responses API file support ChatGPT Ads pricing ChatGPT conversational advertising, OpenAI monetization strategy 2026 OpenAI Code Red, ChatGPT Sycophancy Crisis AI music ChatGPT memory, targeted ads ChatGPT User Milestone, Generative AI Adoption ChatGPT ads, AI monetization GPT-5, OpenAI
  • Technology

OpenAI Unveils GPT-5.4: The “Professional” Frontier with Native Computer Control and 1M Token Context

Do Son March 6, 2026 0

OpenAI launches GPT-5.4, featuring native computer control that beats human benchmarks and a 1M token context window. See the new "Professional" AI in action.

Sovereign & AI-Native: Broadcom’s VMware Telco Cloud Platform 9 Rewrites the TCO Rulebook at MWC 2026 VMware Telco Cloud Platform 9 Tesco, Broadcom, VMware Walmart Broadcom Jericho4, Distributed AI Infrastructure Broadcom VMware, Perpetual Licenses AI Data Centers, Network Switch Unix automation security, Broadcom vulnerability
  • Technology

Sovereign & AI-Native: Broadcom’s VMware Telco Cloud Platform 9 Rewrites the TCO Rulebook at MWC 2026

Do Son March 6, 2026 0

Broadcom unveils VMware Telco Cloud Platform 9 at MWC 2026, promising a 40% TCO reduction through AI-native architecture and sovereign cloud-ready infrastructure.
The iPhone’s Shadow: Why the MacBook Neo is Trapped with 8GB of RAM and a Single Chip MacBook Neo 8GB RAM limit MacBook Neo Windows Parallels
  • Technology

The iPhone’s Shadow: Why the MacBook Neo is Trapped with 8GB of RAM and a Single Chip

Do Son March 6, 2026 0

Discover why Apple's new MacBook Neo is stuck with 8GB of RAM. We dive into the A18 Pro chip constraints and the trade-offs of this $599 ultra-entry laptop.

The Cart is Empty: Why OpenAI is Abandoning In-App Shopping to Become an “AI Discovery Engine” ChatGPT Shopping retreat ChatGPT Search, OpenAI
  • Technology

The Cart is Empty: Why OpenAI is Abandoning In-App Shopping to Become an “AI Discovery Engine”

Do Son March 6, 2026 0

OpenAI is pulling the plug on ChatGPT's native checkout. Discover why the "Amazon killer" is pivoting to an ad-based discovery model after a Shopify slump.

Eyes on the Front: Iranian Threat Actors Weaponize IP Cameras in Middle East Conflict Iranian Cyber Reconnaissance IP Camera Security NCSC Warning Russian Hacktivists Taiwan Cyberattacks China State-Sponsored Hacking state-sponsored threat actor Ransomware RAT Abuse, AnyDesk
  • Cyber Security
  • Vulnerability Report

Eyes on the Front: Iranian Threat Actors Weaponize IP Cameras in Middle East Conflict

Do Son March 6, 2026 0

A new Check Point Research report reveals how Iranian-nexus threat actors compromise IP cameras in the Middle East for real-time missile reconnaissance.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-124585CVSS 9.4
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This issue affects the function...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123870CVSS 9.5
    The otterdog webapp evaluates a format-string built from the incoming GitHub webhook JSON body using Python's eval(). When...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124580CVSS 10.0
    A vulnerability was found in Chengdu Feiyuxing Technology VW2100 and VEC10GP 1.0 B-MB3W202-210825-r11775. This impacts the function handle_wechat_cn_wifi...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124577CVSS 9.3
    A weakness has been identified in Intelbras SG 2404 PoE L2+ 1.00.70/1.00.72. The affected element is an unknown...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17408CVSS 9.8
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17399CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17340CVSS 9.8
    IBM API Connect 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute arbitrary code due to a...
    📅 Updated: Nov 9, 2026
  • CVE-2026-17342CVSS 9.9
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote authenticated attacker to execute...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.