 Do Son
Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.

Google has deployed Gemini AI agents to 3 million Pentagon staff following a fallout with Anthropic. Discover the ethics shift and the new "GenAI.mil" portal.
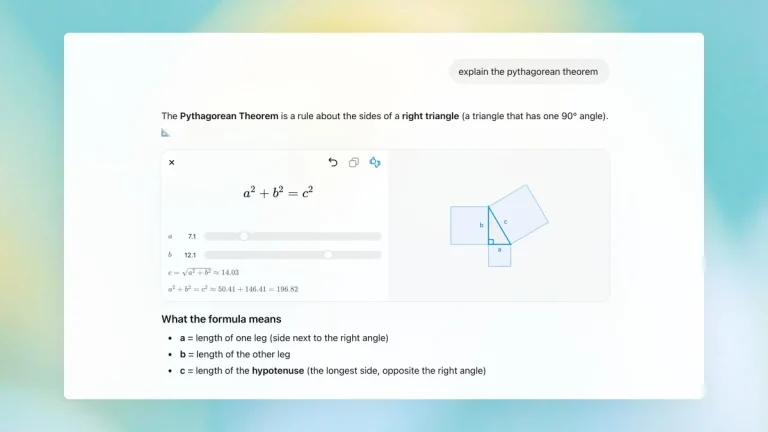
ChatGPT’s new "Dynamic Visual Explanations" let you manipulate variables in real-time diagrams for 70+ math and science concepts. No more static formulas.

A San Francisco judge has blocked Perplexity’s Comet AI from buying on Amazon. Learn how this 2026 ruling defines the legal boundaries of agentic AI commerce.
Google DeepMind’s Gemini Embedding 2 is here. Map text, images, 120s of video, and native audio into one vector space to revolutionize multimodal RAG and search.
A critical 9.4 CVSS tag poisoning attack (CVE-2026-31976) hit the xygeni-action GitHub Action, injecting a C2 backdoor into CI/CD pipelines. Update now.
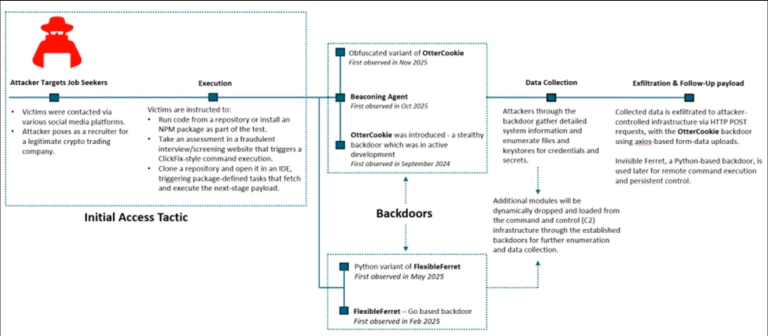
Microsoft exposes the "Contagious Interview" campaign. Fake recruiters trick developers into installing Invisible Ferret malware during coding tests.
CISA warns of a critical 10.0 CVSS RCE flaw (CVE-2025-68613) in n8n workflow automation. Update to version 1.122.0 immediately to prevent server takeover.

Splunk warns of a high-severity RCE flaw (CVE-2026-20163) in its REST API. Attackers with edit_cmd rights can execute arbitrary commands. Patch immediately.
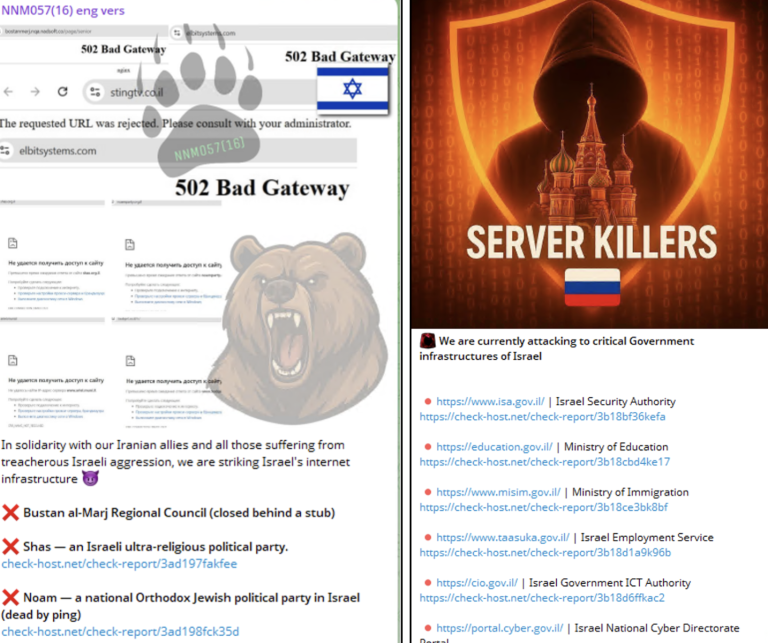
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
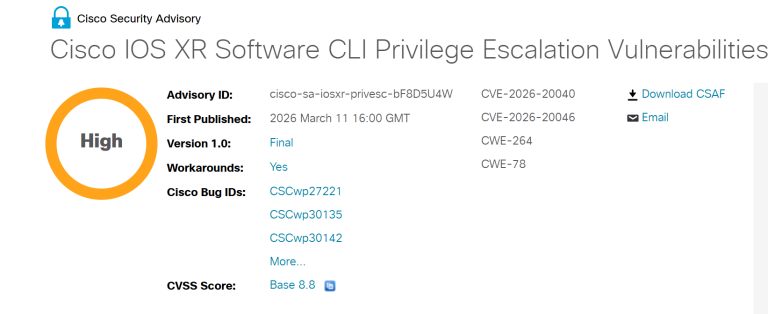
Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.
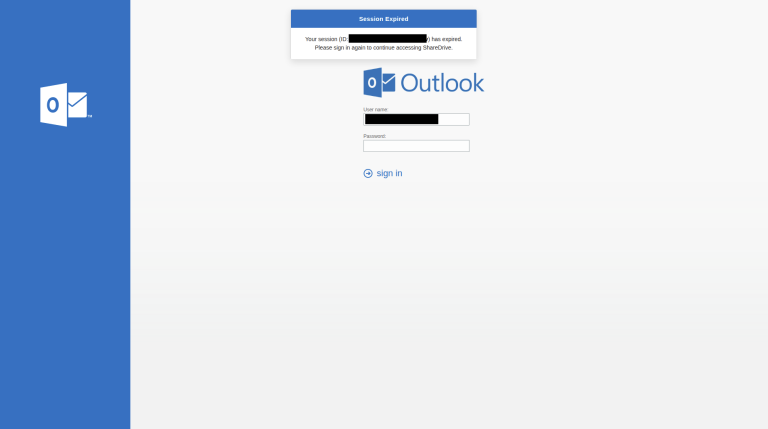
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
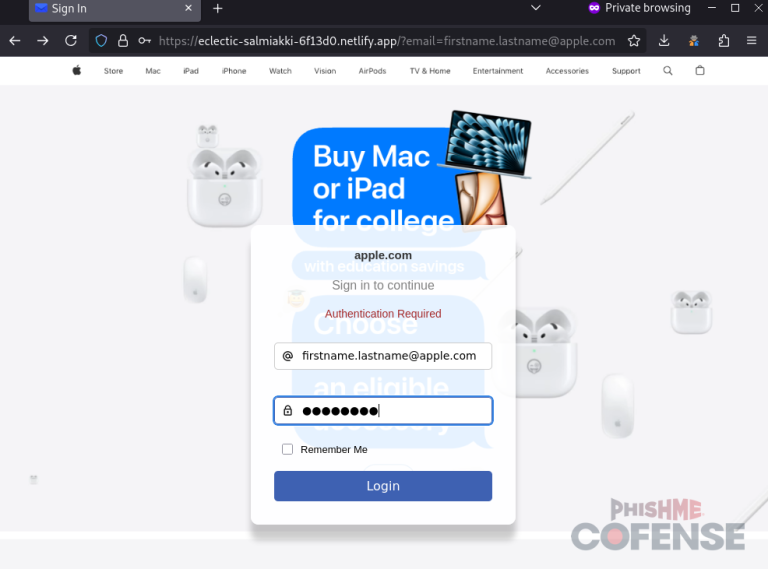
A new Cofense report reveals how hackers abuse legitimate Telegram Bot APIs to create stealthy Command and Control (C2) centers for data exfiltration.

Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

GitLab issues urgent security updates (18.9.2, 18.8.6, 18.7.6) fixing critical XSS (CVE-2026-1090) and DoS flaws. Patch self-managed instances today.

Discover how Operation False Siren weaponizes Israel's Red Alert app via smishing, deploying advanced Android spyware for geo-fenced mobile espionage.
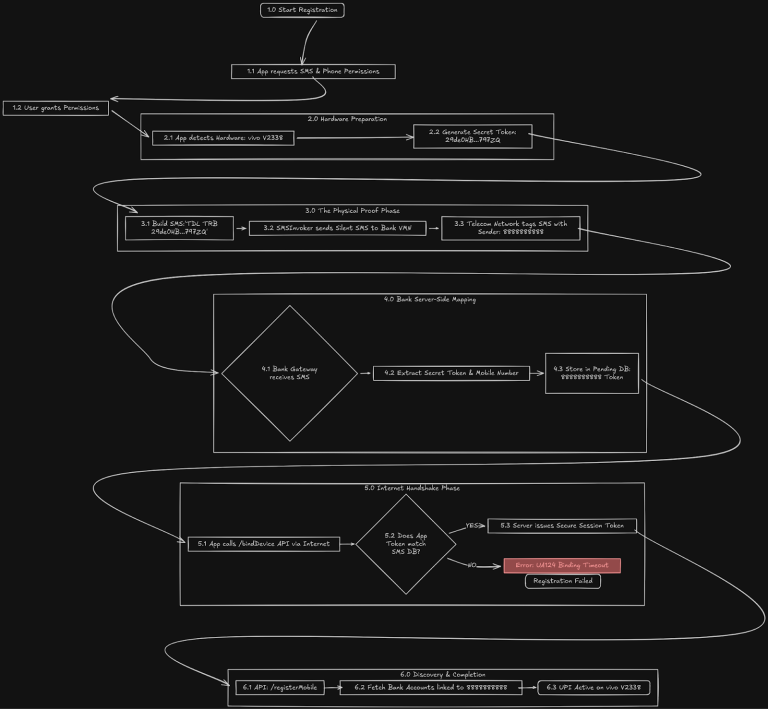
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.

Once a "Featured" tool, the ShotBird extension now delivers malware via "vibecoded" scripts and fake updates. Remove it now to protect your passwords and data.
Most security teams operate from the inside out. They rely on logs and alerts to see what’s...

HPE Aruba patches a critical 9.8 CVSS bypass in AOS-CX switches that allows unauthenticated password resets. Upgrade to 10.17.1001+ to secure your network now.

Urgent: WordPress 6.9.2 patches 10 critical security flaws, including XSS, SSRF, and path traversal. Update your site immediately to prevent exploitation.

A critical SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin exposes 400K+ sites to database theft. Update to version 4.1.0 immediately.