Skip to content
November 5, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The Invisible Speed Boost: How Google’s “AutoFDO” Is Quietly Redefining Android Performance Android Kernel AutoFDO
  • Android

The Invisible Speed Boost: How Google’s “AutoFDO” Is Quietly Redefining Android Performance

Do Son March 14, 2026 0

Google’s new AutoFDO for the Android kernel uses real-world data to cut app lag and boost battery life. Discover the 2026 update making your phone feel new.
The Sandbox Slip: How a Security Audit Unearthed Perplexity’s Exposed Claude Code Tokens Perplexity Computer token leak Perplexity Computer Max
  • Data Leak

The Sandbox Slip: How a Security Audit Unearthed Perplexity’s Exposed Claude Code Tokens

Do Son March 14, 2026 0

A 2026 audit of Perplexity Computer revealed exposed Claude Code tokens in config files. Learn how session-bound API keys could lead to massive billing debts.
AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP image-1200x720_1773385757UnFYetYvjm
  • Press Release

AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP

cybernewswire March 13, 2026 0
Menlo Park, California, USA, 13th March 2026, CyberNewswire
Read More Read more about AI-HealthTech Innovator Humata Health Partners with AccuKnox for Zero Trust CNAPP
45 Seconds to Empty: Ledger Unmasks Critical MediaTek Flaw That Turns Phones Into Glass Vaults MediaTek eavesdropping vulnerabilities MediaTek TEE vulnerability
  • Vulnerability Report

45 Seconds to Empty: Ledger Unmasks Critical MediaTek Flaw That Turns Phones Into Glass Vaults

Do Son March 13, 2026 0

Ledger Donjon uncovers a critical MediaTek TEE flaw allowing attackers to extract PINs and crypto seed phrases in 45 seconds. Patch now.

The Multiplier Model: OpenAI Leaks New $100 “ChatGPT Pro 5x” Tier to Bridge the Pro Gap ChatGPT Pro 5x
  • Technology

The Multiplier Model: OpenAI Leaks New $100 “ChatGPT Pro 5x” Tier to Bridge the Pro Gap

Do Son March 13, 2026 0

OpenAI is launching a $100 "ChatGPT Pro 5x" tier to bridge the gap between Plus and Pro. Experience 5x the compute power without the $200 price tag.
Network Hijack: Critical 9.8 CVSS Flaw in AdGuard Home Grants Hackers Full DNS Control AdGuard Home Vulnerability CVE-2026-32136
  • Vulnerability Report

Network Hijack: Critical 9.8 CVSS Flaw in AdGuard Home Grants Hackers Full DNS Control

Do Son March 13, 2026 0

A critical 9.8 CVSS vulnerability (CVE-2026-32136) in AdGuard Home lets unauthenticated attackers hijack network DNS settings. Update to v0.107.73 now.

Winter CMS Urgently Patches Critical 10.0 CVSS Privilege Escalation Flaw Winter CMS Vulnerability CVE-2026-27591
  • Vulnerability Report

Winter CMS Urgently Patches Critical 10.0 CVSS Privilege Escalation Flaw

Do Son March 13, 2026 0

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

Total Takeover: Veeam Patches Critical 9.9 CVSS RCE Flaws in Backup & Replication 12.3.2 Veeam RCE Vulnerability CVE-2026-21666 CVE-2024-40711 Veeam Backup & Replication
  • Vulnerability Report

Total Takeover: Veeam Patches Critical 9.9 CVSS RCE Flaws in Backup & Replication 12.3.2

Do Son March 13, 2026 0

Veeam urgently patches critical 9.9 CVSS RCE flaws (CVE-2026-21666, CVE-2026-21708) in Backup & Replication 12.3.2. Update your servers immediately.
Legacy Under Siege: Apple Pushes Emergency iOS 15.8.7 Update to Thwart ‘Coruna’ Exploit Kit Coruna Exploit Kit iOS Security Update Apple Zero-Day CVE-2026-20700 Apple Data Privacy Day 2026, iPhone privacy features guide iOS Privilege Escalation, CVE-2025-24085 PoC Apple Manufacturing Academy, US Investment CVE-2024-44258 - symlink vulnerability
  • Vulnerability Report

Legacy Under Siege: Apple Pushes Emergency iOS 15.8.7 Update to Thwart ‘Coruna’ Exploit Kit

Do Son March 13, 2026 0

Apple releases emergency iOS 15.8.7 and 16.7.15 updates for older iPhones to block the actively exploited "Coruna" WebKit and Kernel exploit kit. Patch now.

Breaking the Shield: ‘CrackArmor’ Flaws Expose 12.6 Million Linux Servers to Full Root Takeover CrackArmor AppArmor Vulnerabilities Linux Kernel UAF, Privilege Escalation PoC CVE-2024-27397 PoC
  • Linux
  • Vulnerability Report

Breaking the Shield: ‘CrackArmor’ Flaws Expose 12.6 Million Linux Servers to Full Root Takeover

Do Son March 13, 2026 0

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

Unit 42 Unmasks CL-STA-1087’s Years-Long Cyber Espionage Against Asian Militaries UNC5221 HAFNIUM Extradition PRC State Espionage
  • Cyber Security
  • Malware

Unit 42 Unmasks CL-STA-1087’s Years-Long Cyber Espionage Against Asian Militaries

Do Son March 13, 2026 0

Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.

Apache Livy Patches Path Traversal and File Access Flaws Exposing Spark Clusters Apache Livy Security Path Traversal
  • Vulnerability Report

Apache Livy Patches Path Traversal and File Access Flaws Exposing Spark Clusters

Do Son March 13, 2026 0

Protect your Spark clusters: Apache Livy 0.9.0 patches two important file access and path traversal vulnerabilities (CVE-2025-60012 & CVE-2025-66249).

Veeam Urgently Patches Critical 9.9 CVSS RCE Flaws in Backup Servers Veeam RCE Vulnerability CVE-2026-21669 Veeam RCE, CVE-2025-48983 CVE-2025-48984
  • Vulnerability Report

Veeam Urgently Patches Critical 9.9 CVSS RCE Flaws in Backup Servers

Do Son March 13, 2026 0

Veeam releases a critical security update fixing 9.9 CVSS RCE flaws (CVE-2026-21669, CVE-2026-21708) in Backup & Replication. Patch servers immediately.
Critical 9.8 CVSS telnetd Buffer Overflow Grants Pre-Auth Root pre
  • Vulnerability

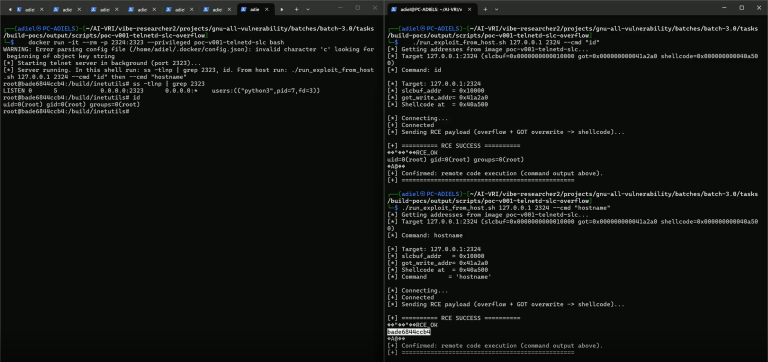
Critical 9.8 CVSS telnetd Buffer Overflow Grants Pre-Auth Root

Do Son March 13, 2026 0

A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.

The “CrashFix” Evolution: KongTuke’s New Playbook for Enterprise Infiltration UAT-8099 BadIIS Malware Pacific Islands Forum Cyberattack
  • Malware

The “CrashFix” Evolution: KongTuke’s New Playbook for Enterprise Infiltration

Do Son March 13, 2026 0

Trend Micro exposes KongTuke's new "CrashFix" tactic, which tricks enterprise users via fake Chrome errors into deploying the fileless modeloRAT backdoor.

TaxiSpy RAT: New Android Banking Trojan Targets Russian Financial Sector Android zero day flaw June 2026 security bulletin RuTaxi Trojan Android Banking Malware Pixel 9 zero-click exploit, Dolby UDC vulnerability CVE-2025-54957 NexusRoute Android RAT, India E-Challan Phishing ClayRat Self-Defense, Android Accessibility Abuse Android Trojan, AntiDot Android Malware "BadPack"
  • Malware

TaxiSpy RAT: New Android Banking Trojan Targets Russian Financial Sector

Do Son March 13, 2026 0

Cyfirma uncovers the RuTaxi Android banking Trojan, a highly persistent malware using VNC capabilities to hijack Russian bank accounts and crypto wallets.

A Single Line of Code: Pre-Auth OpenSSH Flaw Exposes Ubuntu and Debian Servers OpenSSH 10.3 Patch SSH Command Injection CVE-2023-38408 OpenSSH Vulnerability CVE-2026-3497
  • Vulnerability Report

A Single Line of Code: Pre-Auth OpenSSH Flaw Exposes Ubuntu and Debian Servers

Do Son March 13, 2026 0

A pre-auth flaw in OpenSSH's GSSAPI Key Exchange (CVE-2026-3497) exposes Ubuntu and Debian servers to heap corruption and data leaks. Patch now.
The Amphibious Gamer: How Google’s “Buy Once, Play Anywhere” Strategy is Taking on Steam Google Play PC cross-platform
  • Android

The Amphibious Gamer: How Google’s “Buy Once, Play Anywhere” Strategy is Taking on Steam

Do Son March 13, 2026 0

Google’s GDC 2026 updates bring "buy once, play anywhere" licenses and AI-powered "Sidekick" tips to PC and mobile. See how they're challenging Steam’s monopoly.
The Arm64 Vanguard: Valve Shatters x86 Hegemony with Steam Frame and “SteamOS on Arm” SteamOS on Arm
  • Technology

The Arm64 Vanguard: Valve Shatters x86 Hegemony with Steam Frame and “SteamOS on Arm”

Do Son March 13, 2026 0

Valve’s GDC 2026 reveal of "SteamOS on Arm" and the Steam Frame marks the end of x86 dominance. Discover the new 1080p/30FPS Steam Machine Verified standards.
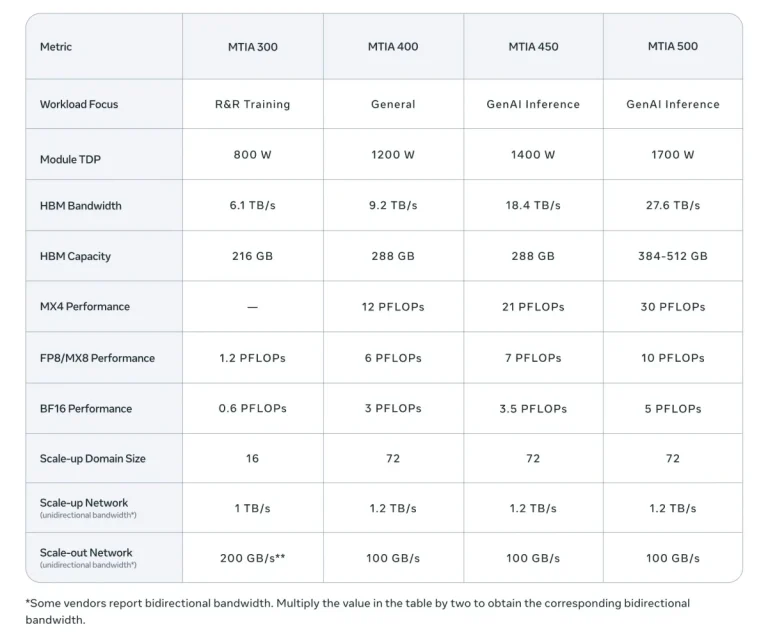
Hardware Autonomy: Meta’s “High Velocity” Roadmap to Deploy Four AI Chips by 2027 Meta MTIA roadmap
  • Technology

Hardware Autonomy: Meta’s “High Velocity” Roadmap to Deploy Four AI Chips by 2027

Do Son March 13, 2026 0

Meta shatters the industry standard with a 6-month chip cycle. Discover the MTIA 300-500 roadmap designed to slash AI costs and power 3 billion users by 2027.
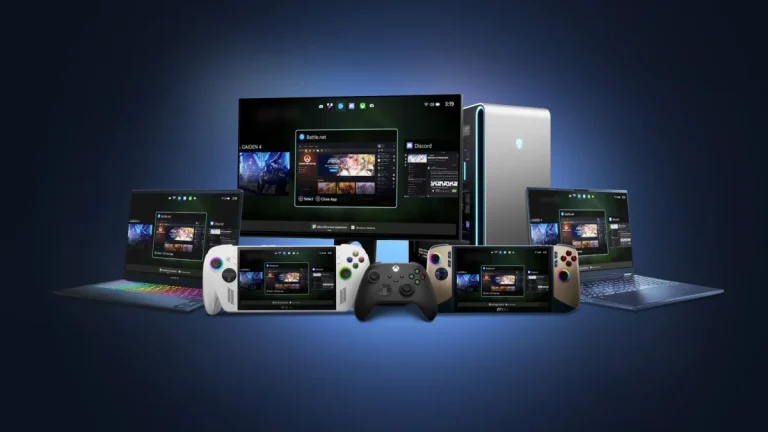
The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode” Xbox Project Helix Xbox Mode Windows 11
  • Windows

The “Helix” Horizon: Microsoft Transforms Windows 11 Into a Console With “Xbox Mode”

Do Son March 13, 2026 0

Microsoft’s new "Xbox Mode" brings a full-screen, controller-first console experience to all Windows 11 PCs this April. Say goodbye to shader stutter in 2026.

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Double Zero-Day Threat: Emergency Chrome Update Patches Actively Exploited Skia and V8 Flaws

Do Son March 12, 2026 0

Google releases an emergency Chrome update to patch two actively exploited zero-day vulnerabilities (CVE-2026-3909 & CVE-2026-3910). Update immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-112443CVSS 9.1
    The issue was addressed with improved memory handling. This issue is fixed in macOS Golden Gate 27.2, macOS...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121234CVSS 9.6
    Privilege elevation in Contacts in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 5, 2026
  • CVE-2026-121077CVSS 9.6
    Use after free in Mobile in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 5, 2026
  • CVE-2026-123198CVSS 9.3
    LMFDB before commit 01829bd contains a server-side template injection vulnerability in the render_knowl function that allows unauthenticated attackers...
    📅 Updated: Nov 5, 2026
  • CVE-2026-105606CVSS 9.5
    Joomla Extension - joomlaboat.com - Unauthenticated arbitrary file upload in Custom Tables < 3.7.8 - An unauthenticated attacker...
    📅 Updated: Nov 5, 2026
  • CVE-2026-115828CVSS 9.4
    In Secret Server on-prem versions earlier than 12.3.1, Secret Server did not always validate the PIN or biometric...
    📅 Updated: Nov 5, 2026
  • CVE-2026-115829CVSS 9.9
    In Secret Server on-prem versions earlier than 12.3.1, a user could cause a two-factor pin code to be...
    📅 Updated: Nov 5, 2026
  • CVE-2026-102788CVSS 9.3
    Joomla Extension - balbooa.com - Unauthenticated SQL injection in Gridbox < 2.20.4.2 - On store product list pages,...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.