
 Do Son
A critical 10.0 CVSS flaw (CVE-2026-3611) in Honeywell IQ4x BMS controllers leaves web HMIs exposed without authentication. Secure your systems immediately.
A critical 9.6 CVSS XSS vulnerability (CVE-2025-40943) in Siemens SIMATIC S7-1500 CPUs allows attackers to inject malicious code via trace files.

Microsoft's March 2026 Patch Tuesday addresses 93 vulnerabilities, including two public zero-days affecting SQL Server and .NET. Patch your systems now.

Two critical 10.0 CVSS flaws (CVE-2026-30956, CVE-2026-30957) in OneUptime allow full account takeovers and Server-Side RCE. Update to 10.0.21 immediately.
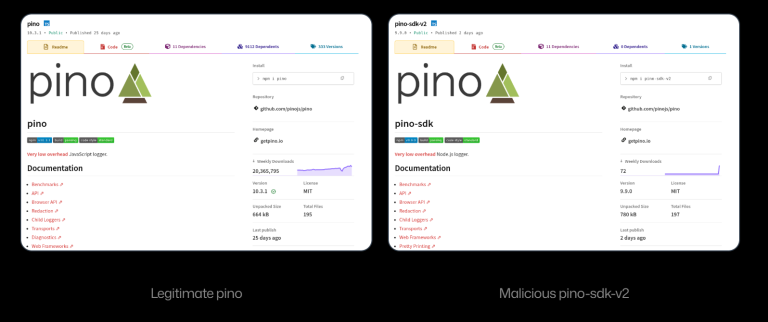
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
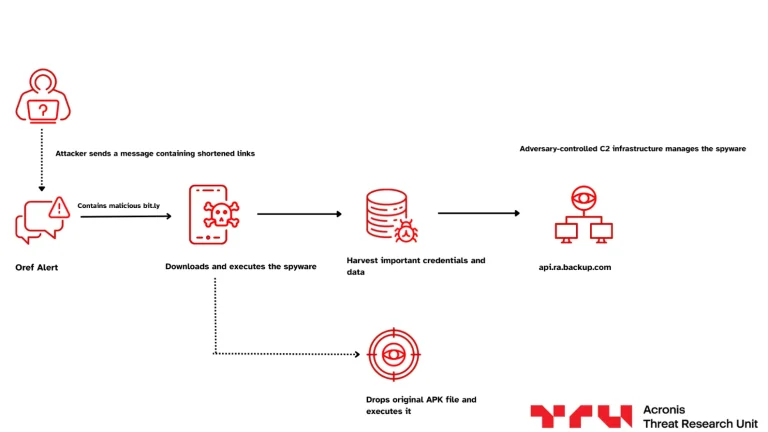
Acronis TRU uncovers a trojanized Red Alert rocket warning app targeting Israelis. Linked to APT-C-23, this Android malware steals data while alerting users.
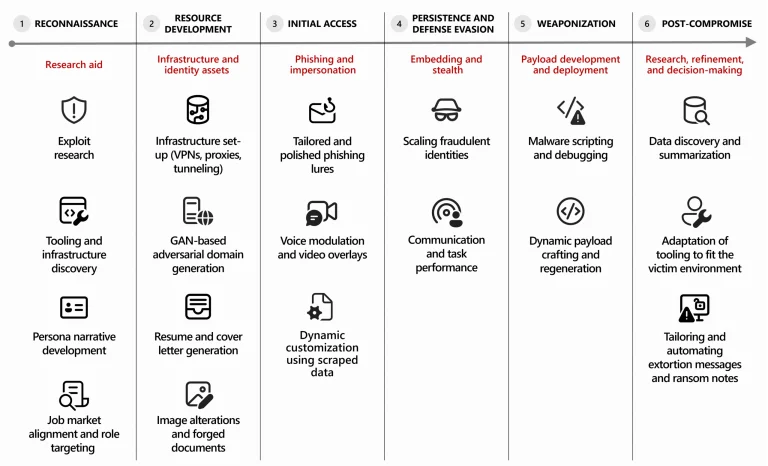
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
Hackers are targeting AI developers with a fake Claude Code "InstallFix" malvertising campaign, using malicious terminal commands to drop Amatera malware.

Zscaler ThreatLabz reveals a surge in Middle East conflict-themed cyberattacks, uncovering 8,000+ malicious domains, LOTUSLITE backdoors, and scams.
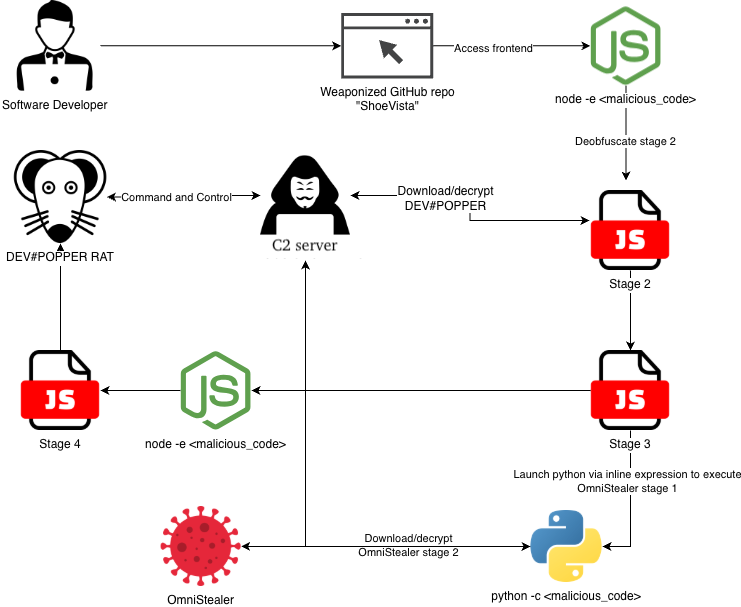
eSentire exposes DEV#POPPER, a North Korean RAT hiding in GitHub repos. It uses blockchain to deploy OmniStealer, targeting crypto and dev secrets.
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Critical flaws (CVE-2025-41709) in Janitza and Weidmueller energy meters allow remote code execution and full system takeover. Update to firmware 3.14 now.
Zoom patches a critical 9.6 CVSS flaw (CVE-2026-30903) allowing unauthenticated remote privilege escalation on Windows. Update your clients immediately.
CISA adds three actively exploited flaws in SolarWinds, Ivanti, and Omnissa to its KEV catalog. Patch these critical enterprise vulnerabilities immediately.
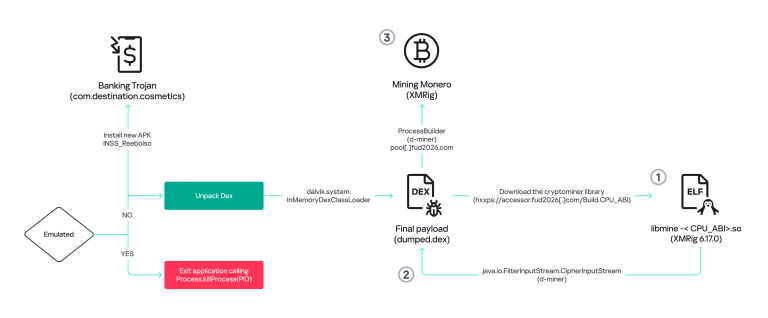
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.
 cybernewswire

In the gig economy, your face is your brand. Before a prospect reads your proposal, scrolls through...

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.

SAP's latest security update addresses 15 flaws, including critical RCE (CVE-2019-17571) and deserialization (CVE-2026-27685) vulnerabilities. Patch now.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.
Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture

Securing the Frontier: Why OpenAI Just Vaulted This $86M Security Startup Into Its Core Architecture
OpenAI has acquired AI security vanguard Promptfoo. Discover how this $86M deal will automate red-teaming and protect AI agents from prompt injection in 2026.

Google’s experimental Workspace CLI ends the era of AI account bans, offering a "skills" bridge for agents like OpenClaw and Claude to automate Gmail and Drive.