Skip to content
November 6, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
From Ban to Bridge: Google’s New Workspace CLI Welcomes Viral AI Agents Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

From Ban to Bridge: Google’s New Workspace CLI Welcomes Viral AI Agents

Do Son March 10, 2026 0

Google’s experimental Workspace CLI ends the era of AI account bans, offering a "skills" bridge for agents like OpenClaw and Claude to automate Gmail and Drive.
Beyond the Console: How Andy Nguyen Turned the PlayStation 5 Into a 4K Ray-Tracing Linux PC PS5 Linux Steam Machine
  • Linux

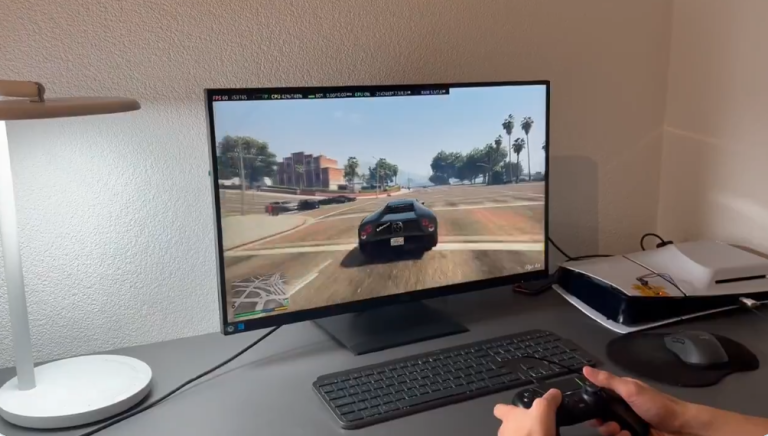
Beyond the Console: How Andy Nguyen Turned the PlayStation 5 Into a 4K Ray-Tracing Linux PC

Do Son March 10, 2026 0

Security researcher Andy Nguyen has successfully ported Linux to the PS5, running Steam and GTA V at 1440p/60FPS with Ray Tracing. See the future of PS5 modding.

Unlocking the Beast: How Microsoft’s New Native NVMe Driver Delivers a 65% Performance Surge Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Unlocking the Beast: How Microsoft’s New Native NVMe Driver Delivers a 65% Performance Surge

Do Son March 10, 2026 0

Microsoft’s new native NVMe driver (nvmedisk.sys) boosts 4K random reads by 65% and slashes CPU load. Learn how to unlock this hidden feature in Windows 11.
The Floating Browser: A First Look at Firefox’s Radical “Project NOVA” Redesign Firefox Project NOVA
  • Technology

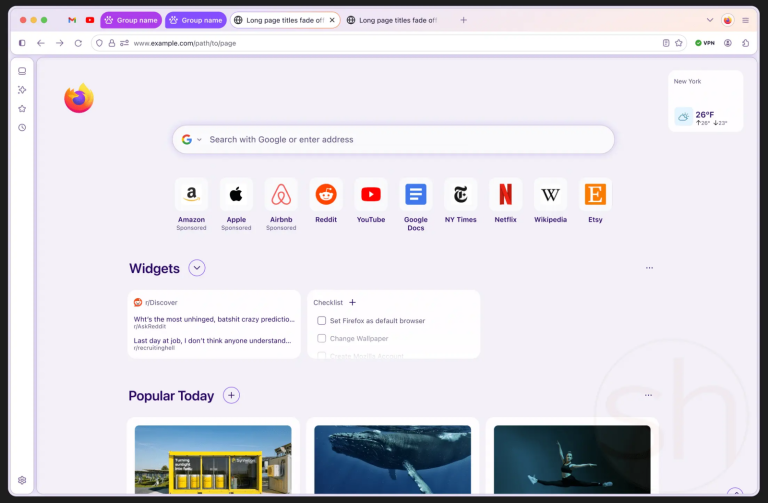
The Floating Browser: A First Look at Firefox’s Radical “Project NOVA” Redesign

Do Son March 10, 2026 0

Mozilla’s "Project NOVA" is a 3D, floating-element reimagining of the Firefox UI. See the leaked wireframes of the biggest browser metamorphosis since 2021.

X Incapacitates Thousands of Android and iOS Users with Draconian Device Audits Elon Musk SEC settlement X bootloader verification X Creator Revenue Sharing suspension X Platform, AI Training X open-source algorithm 2026, Elon Musk ad transparency
  • Technology

X Incapacitates Thousands of Android and iOS Users with Draconian Device Audits

Do Son March 10, 2026 0

X's new "anti-bot" audit has backfired, silencing legitimate users with unlocked bootloaders or jailbroken phones. Is your device now "unauthorized" to post?
Total Platform Compromise: Critical 9.6 CVSS Flaws in Budibase Expose Production Secrets Budibase RCE SSRF Vulnerability Budibase Vulnerabilities Authentication Bypass
  • Vulnerability Report

Total Platform Compromise: Critical 9.6 CVSS Flaws in Budibase Expose Production Secrets

Do Son March 10, 2026 0

Two critical flaws in Budibase (CVE-2026-31816, CVE-2026-30240) allow unauthenticated API access and secret exfiltration via path traversal. Patch immediately.

Under Active Attack: Critical 9.8 CVSS Tutor LMS Pro Flaw Exploited in the Wild for Full Site Takeover CVE-2024-11972 - Hunk Companion
  • Vulnerability Report

Under Active Attack: Critical 9.8 CVSS Tutor LMS Pro Flaw Exploited in the Wild for Full Site Takeover

Do Son March 10, 2026 0

A critical 9.8 CVSS authentication bypass (CVE-2026-0953) in Tutor LMS Pro is being actively exploited in the wild. Update to version 3.9.6 immediately.

Home Network Alert: TP-Link Patches RCE Vulnerability in Archer AXE75 Routers Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Home Network Alert: TP-Link Patches RCE Vulnerability in Archer AXE75 Routers

Do Son March 10, 2026 0

A critical 8.5 CVSS command injection flaw (CVE-2025-15568) in TP-Link Archer AXE75 routers allows complete root-level network takeover. Patch immediately.
Kubernetes Security Alert: “Ingress-Nginx” Injection Flaw Risks Cluster-Wide Secret Exposure ingress-nginx Vulnerability CVE-2026-3288
  • Vulnerability Report

Kubernetes Security Alert: “Ingress-Nginx” Injection Flaw Risks Cluster-Wide Secret Exposure

Do Son March 10, 2026 0

A high 8.8 CVSS flaw (CVE-2026-3288) in ingress-nginx allows arbitrary code execution and massive Kubernetes secret leakage. Patch immediately.

CVE-2026-0866: Malformed ZIP Headers Allow Malware to Slip Past EDR Scanners shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-0866: Malformed ZIP Headers Allow Malware to Slip Past EDR Scanners

Do Son March 10, 2026 0

Discover how attackers use shadow archives (CVE-2026-0866) to bypass AV and EDR by malforming ZIP metadata, keeping malware hidden but executable.
“Coruna” Exploit Kit: Mass iOS Attacks Pivot from Crypto Scams to Iran-Themed Lures Coruna Exploit Kit iOS Malware
  • Cybercriminals

“Coruna” Exploit Kit: Mass iOS Attacks Pivot from Crypto Scams to Iran-Themed Lures

Do Son March 10, 2026 0

Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.
Fake CleanMyMac Site Unleashes SHub Stealer to Drain macOS Crypto Wallets SHub Stealer Mac Malware
  • Malware

Fake CleanMyMac Site Unleashes SHub Stealer to Drain macOS Crypto Wallets

Do Son March 10, 2026 0

A fake CleanMyMac website is using ClickFix tactics to trick macOS users into installing SHub Stealer, a potent malware targeting passwords and crypto.

Critical 9.8 CVSS Flaws Expose SICK Lector Scanners to Hijacking SICK Lector Vulnerability CVE-2026-2331 CVE-2022-0778 and CVE-2025-0867
  • Vulnerability Report

Critical 9.8 CVSS Flaws Expose SICK Lector Scanners to Hijacking

Do Son March 10, 2026 0

SICK PSIRT warns of critical vulnerabilities (CVE-2026-2330, CVE-2026-2331) in Lector85x and Lector83x scanners allowing full device takeover. Update now.
Malicious “Hex Visualizer” Chrome Extension Targeting imToken Users Crypto Wallet Drainer ImToken Phishing
  • Cybercriminals

Malicious “Hex Visualizer” Chrome Extension Targeting imToken Users

Do Son March 10, 2026 0

Socket researchers uncover "ImToken Chromophore," a malicious Chrome extension using fake branding and homoglyphs to steal crypto wallet seed phrases.
Critical 9.3 CVSS Flaw in Gogs Turns Repositories into Malware Delivery Vectors Gogs LFS Vulnerability CVE-2026-25921
  • Vulnerability Report

Critical 9.3 CVSS Flaw in Gogs Turns Repositories into Malware Delivery Vectors

Do Son March 10, 2026 0

A critical 9.3 CVSS flaw (CVE-2026-25921) in Gogs' LFS handling allows attackers to silently overwrite repository files, risking severe supply-chain attacks.

Agencies Issue Urgent Warning on INC Ransom Healthcare Attacks INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Cybercriminals

Agencies Issue Urgent Warning on INC Ransom Healthcare Attacks

Do Son March 10, 2026 0

A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
Critical Request Smuggling & Cache Flaws Discovered in Cloudflare’s Pingora Pingora Vulnerabilities Cloudflare Pingora
  • Vulnerability Report

Critical Request Smuggling & Cache Flaws Discovered in Cloudflare’s Pingora

Do Son March 10, 2026 0

Discover three critical flaws (including CVE-2026-2835) in Cloudflare's Pingora Rust framework causing request smuggling and cache poisoning. Update now.
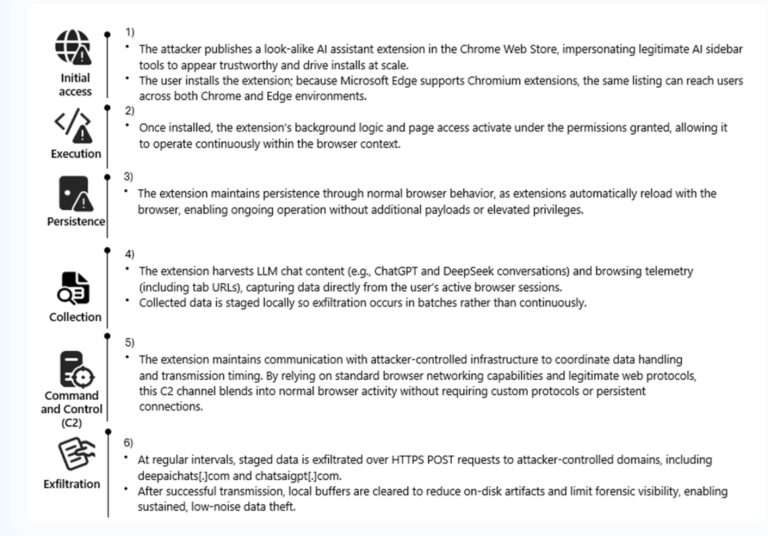
The Spy in Your Sidebar: Fake AI Browser Extensions Steal Data from 900,000 Users Malicious AI Extensions Chromium Browser Security
  • Malware

The Spy in Your Sidebar: Fake AI Browser Extensions Steal Data from 900,000 Users

Do Son March 10, 2026 0

Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.
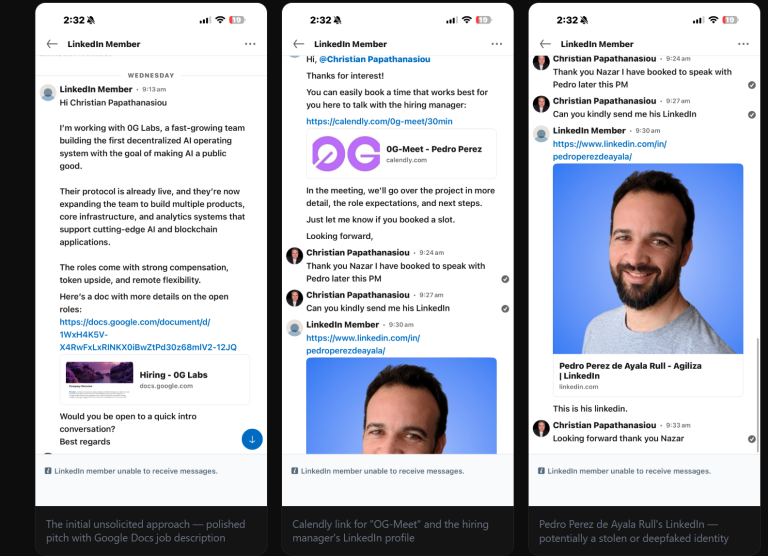
The ‘Contagious Interview’ Trap: How a Web3 CEO Unmasked North Korean Stealth Malware Contagious Interview North Korean Malware
  • Cybercriminals

The ‘Contagious Interview’ Trap: How a Web3 CEO Unmasked North Korean Stealth Malware

Do Son March 10, 2026 0

A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.
Silently Swapped: How ClipXDaemon Hijacks Linux Cryptowallets Without a C2 Server ClipXDaemon Linux Malware
  • Malware

Silently Swapped: How ClipXDaemon Hijacks Linux Cryptowallets Without a C2 Server

Do Son March 10, 2026 0

Cyble Research unmasks ClipXDaemon, a C2-less Linux malware that silently hijacks cryptocurrency wallet addresses in X11 clipboard environments.
Security Risk Advisors Releases “The Purple Perspective 2026” Report purple-perspective-social-press2_1772821885s5aslCzJZX
  • Press Release

Security Risk Advisors Releases “The Purple Perspective 2026” Report

cybernewswire March 9, 2026 0
Philadelphia, PA, United States, 9th March 2026, CyberNewswire
Read More Read more about Security Risk Advisors Releases “The Purple Perspective 2026” Report
AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision AWS Phishing AiTM Attack
  • Cybercriminals

AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision

Do Son March 9, 2026 0

Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2024-27834CVSS 5.5
    The issue was addressed with improved checks. This issue is fixed in Safari 17.5, iOS 16.7.8 and iPadOS...
    CISA KEV📅 Added to KEV: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-46408CVSS 9.8
    An issue was discovered in the methods push.lite.avtech.com.AvtechLib.GetHttpsResponse and push.lite.avtech.com.Push_HttpService.getNewHttpClient in AVTECH EagleEyes 2.0.0. The methods set ALLOW_ALL_HOSTNAME_VERIFIER,...
    📅 Updated: Nov 5, 2026
  • CVE-2025-52053CVSS 9.8
    TOTOLINK X6000R V9.4.0cu.1360_B20241207 was found to contain a command injection vulnerability in the sub_417D74 function via the file_name...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57174CVSS 9.8
    An issue was discovered in Siklu Communications Etherhaul 8010TX and 1200FX devices, Firmware 7.4.0 through 10.7.3 and possibly...
    📅 Updated: Nov 5, 2026
  • CVE-2025-56074CVSS 9.8
    A SQL Injection vulnerability was discovered in the foreigner-bwdates-reports-details.php file of PHPGurukul Park Ticketing Management System v2.0. This...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57432CVSS 9.8
    Blackmagic Web Presenter version 3.3 exposes a Telnet service on port 9977 that accepts unauthenticated commands. This service...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57601CVSS 9.8
    AiKaan Cloud Controller uses a single hardcoded SSH private key and the username `proxyuser` for remote terminal access...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57437CVSS 9.8
    The Blackmagic Web Presenter HD firmware version 3.3 exposes sensitive information via an unauthenticated Telnet service on port...
    📅 Updated: Nov 5, 2026
  • CVE-2025-57441CVSS 9.8
    The Blackmagic ATEM Mini Pro 2.7 exposes sensitive device and stream configuration information via an unauthenticated Telnet service...
    📅 Updated: Nov 5, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.