
 Do Son
A joint advisory warns of INC Ransom's devastating pivot to the Pacific. Discover how this RaaS group uses double extortion to target healthcare sectors.
Discover three critical flaws (including CVE-2026-2835) in Cloudflare's Pingora Rust framework causing request smuggling and cache poisoning. Update now.
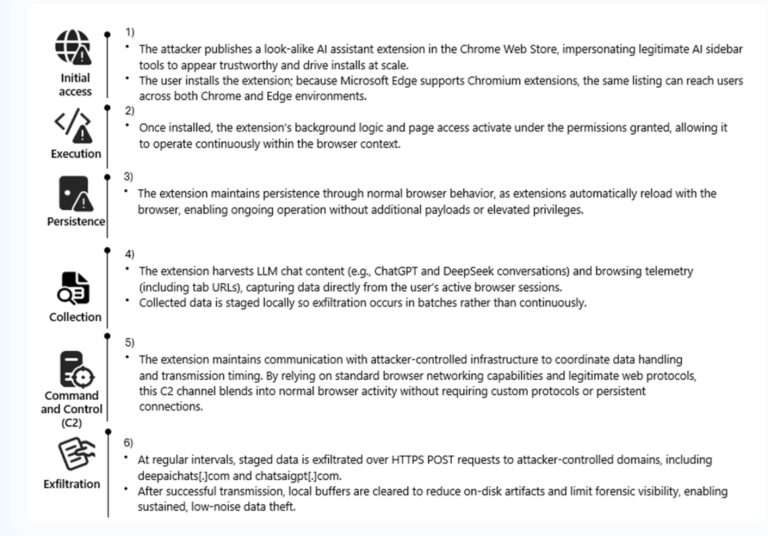
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.
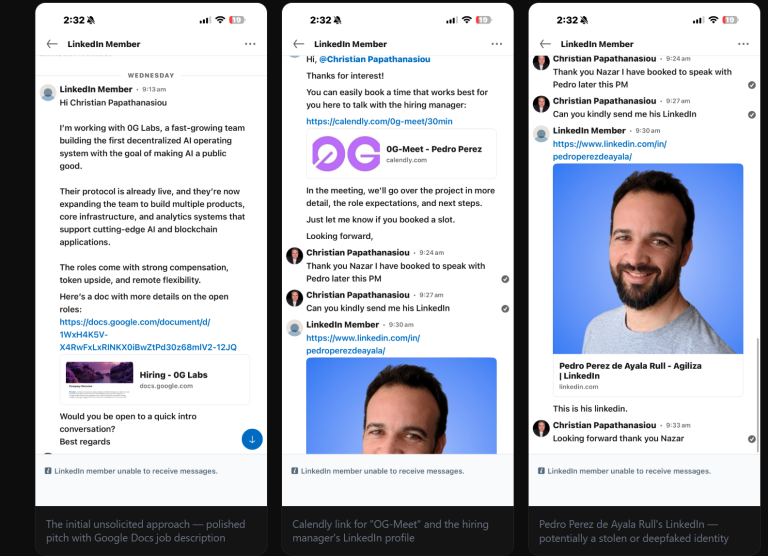
A fake LinkedIn recruiter and a poisoned GitHub repo: See how a CEO uncovered the North Korean "Contagious Interview" malware targeting Web3 developers.
Cyble Research unmasks ClipXDaemon, a C2-less Linux malware that silently hijacks cryptocurrency wallet addresses in X11 clipboard environments.
 cybernewswire
Philadelphia, PA, United States, 9th March 2026, CyberNewswire
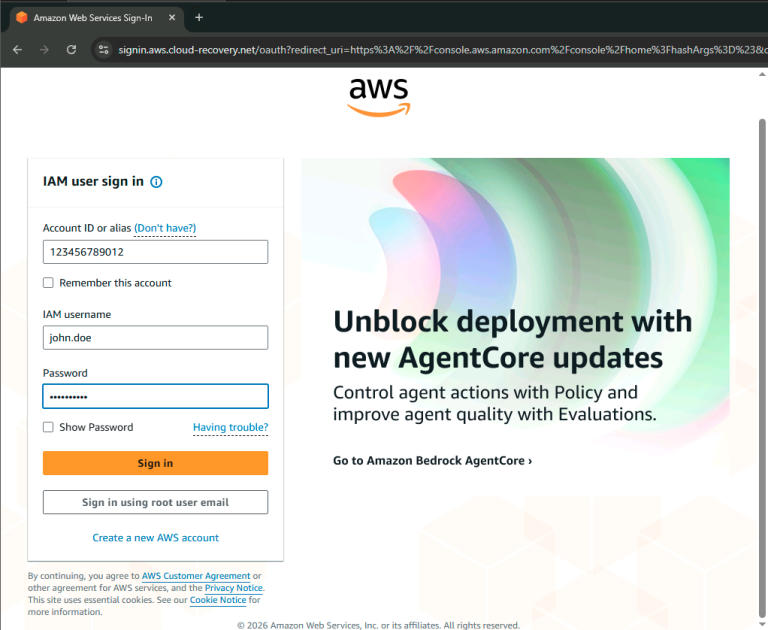
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Apache IoTDB issues an urgent fix for a critical JEXL injection flaw (CVE-2026-24713) and insecure defaults. Upgrade to 1.3.7 or 2.0.7 to secure your IIoT data.
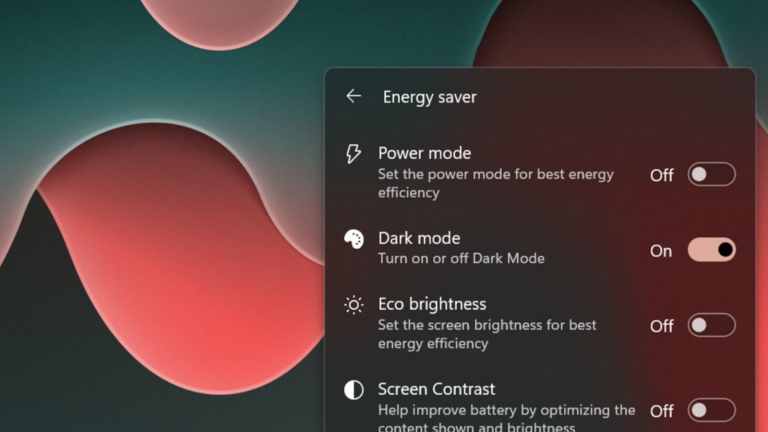
Microsoft finally adds a one-click Dark Mode toggle to the Windows 11 taskbar—but it's hidden in the Energy Saver menu. Is this a genius move or a UI fail?
OpenAI's new "Codex for Open Source" offers maintainers 6 months of ChatGPT Pro and Codex Security. Is your repository eligible for this $1,200 AI grant?

OpenAI's robotics lead Caitlin Kalinowski resigns in a "crisis of governance" over the Pentagon deal. Discover the "red lines" shaking the AI industry in 2026.

The Pentagon brands Anthropic a "Supply-Chain Risk" over ethical AI refusals. See how Microsoft, Google, and Amazon are defying the military to save Claude.

Nintendo sues the U.S. for a full refund of "unlawful" Trump tariffs. Discover how the 2026 IEEPA ruling could shift the price of the Nintendo Switch 2.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.

Trend Micro reveals the BoryptGrab info stealer campaign using SEO-optimized fake GitHub repos to deploy the TunnesshClient reverse SSH backdoor.
A critical 9.4 CVSS buffer overflow flaw (CVE-2026-1678) in Zephyr RTOS's DNS parser allows unauthenticated RCE on IoT devices. Patch immediately.
Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.
A critical 9.3 CVSS reflected XSS flaw (CVE-2026-29183) in SiYuan's dynamic icon API lets attackers steal private notes via SVG injection. Update now.

Apache ZooKeeper vulnerabilities (CVE-2026-24281, CVE-2026-24308) allow PTR record spoofing and sensitive data leaks in logs. Update clusters immediately.

Researchers uncover a massive campaign by a Vietnamese operator using GitHub and Polygon blockchain smart contracts to distribute the StealC infostealer.

A critical 9.3 CVSS XSS vulnerability (CVE-2026-29191) in ZITADEL's SAML endpoint allows unauthenticated 1-click account takeover. Upgrade immediately.