Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Fake Security Checkup: How a Rogue ‘Google’ App Hijacks Your Digital Life PWA Malware Google-prism
  • Cybercriminals

The Fake Security Checkup: How a Rogue ‘Google’ App Hijacks Your Digital Life

Do Son March 3, 2026 0

Cybercriminals are using a fake Google security checkup (google-prism) to trick you into installing powerful PWA malware. Learn how to spot the trap.

The Invisible Trap: How Hackers Weaponize the Internet’s Root Infrastructure (.arpa) to Bypass Security Kali365 phishing platform EmEditor Supply Chain Attack, WALSHAM INVESTMENTS LIMITED EggStreme, fileless malware North Korea Cybercrime, Remote IT Job Fraud RedDelta APT
  • Cybercriminals

The Invisible Trap: How Hackers Weaponize the Internet’s Root Infrastructure (.arpa) to Bypass Security

Do Son March 3, 2026 0

Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.

OpenAI Exposes the Massive Global Underworld of Malicious AI OpenAI Threat Report Cyber Special Operations
  • Cybercriminals

OpenAI Exposes the Massive Global Underworld of Malicious AI

Do Son March 3, 2026 0

OpenAI’s Feb 2026 report reveals "cyber special operations," Cambodian "Date Bait" scams, and Russian content farms using AI to automate global disruption.

Bridging the Gap: North Korean APT37 Deploys ‘Ruby Jumper’ to Infiltrate Isolated Air-Gapped Networks CVE-2024-3393 - Zservers sanctions
  • Malware

Bridging the Gap: North Korean APT37 Deploys ‘Ruby Jumper’ to Infiltrate Isolated Air-Gapped Networks

Do Son March 3, 2026 0

Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

The High Cost of ‘Free’: How PiviGames Became a Lovecraftian Malware Hub for HijackLoader and ACRStealer Lotus Wiper Digital Sabotage G_Wagon Malware NPM Supply Chain Attack IMAPLoader malware ResolverRAT Malware Evasion
  • Malware

The High Cost of ‘Free’: How PiviGames Became a Lovecraftian Malware Hub for HijackLoader and ACRStealer

Do Son March 3, 2026 0

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026 1200_720_1_1772088331SAvTYOiwF2
  • Press Release

Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026

cybernewswire March 2, 2026 0
Torrance, United States / California, 2nd March 2026, CyberNewswire
Read More Read more about Criminal IP to Present Decision-Ready Threat Intelligence at RSAC™ 2026
Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat Link11_ECR_Eng_1772103046oiPBPragVC
  • Press Release

Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat

cybernewswire March 2, 2026 0
Frankfurt am Main, Germany, 2nd March 2026, CyberNewswire
Read More Read more about Link11 Releases European Cyber Report 2026: DDoS Attacks Become a Constant Threat
Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions Amazon Redshift JDBC Driver RCE CVE-2026-8178 AWS Bahrain fire 2026 AWS UAE data center fire Amazon North Korean hacker keystroke latency, Arizona laptop farm infiltration
  • Technology

Cloud Under Fire: Unidentified “Objects” Strike AWS Data Center in UAE Amid Regional Tensions

Do Son March 2, 2026 0

An AWS data center in the UAE (mec1-az2) was struck by "objects" on March 1, triggering a fire and power outage amid regional missile and drone activity.

The Antigravity Reinstatement: Google Relents on Ban Wave but Issues Final Warning on OpenClaw Proxies Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

The Antigravity Reinstatement: Google Relents on Ban Wave but Issues Final Warning on OpenClaw Proxies

Do Son March 2, 2026 0

Google has refreshed Antigravity and started reinstating accounts suspended for token proxying. Learn how to recover your access and avoid permanent bans.

Critical Backup Flaws Expose Vitess Environments to Complete Takeover Vitess Backup Poisoning CVE-2026-27969
  • Vulnerability Report

Critical Backup Flaws Expose Vitess Environments to Complete Takeover

Do Son March 2, 2026 0

Vitess patches critical flaws (CVE-2026-27969 & 27965) where poisoned backup manifests lead to path traversal and RCE during restoration. Update to v23.0.3 now.
Critical 9.8 Flaw in Langflow’s AI CSV Agent Opens a Direct Path to Root Shell Langflow Vulnerability CVE-2026-42048 Langflow RCE CVE-2026-27966 Langflow Vulnerabilities CVE-2026-33017
  • Vulnerability Report

Critical 9.8 Flaw in Langflow’s AI CSV Agent Opens a Direct Path to Root Shell

Do Son March 2, 2026 0

Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

Critical Flaws in Vikunja Expose Users to Persistent Account Takeovers Vikunja Persistent Takeover CVE-2026-28268
  • Vulnerability Report

Critical Flaws in Vikunja Expose Users to Persistent Account Takeovers

Do Son March 2, 2026 0

Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.
The Cryptography Trojan: Malicious Go Module Impersonates Foundational Library to Steal Passwords and Deploy Root Backdoors Go Supply Chain Attack Rekoobe Backdoor
  • Malware

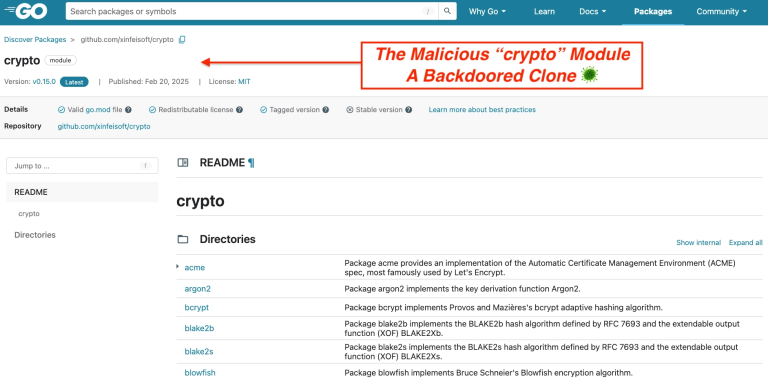
The Cryptography Trojan: Malicious Go Module Impersonates Foundational Library to Steal Passwords and Deploy Root Backdoors

Do Son March 2, 2026 0

Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
Dohdoor: New Stealth Backdoor Targets US Healthcare and Education Dohdoor Backdoor UAT-10027
  • Malware

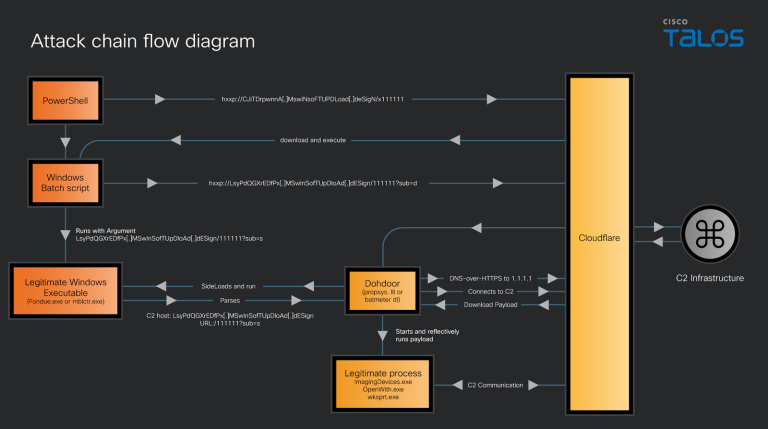
Dohdoor: New Stealth Backdoor Targets US Healthcare and Education

Do Son March 2, 2026 0

Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.
The GTFire Scheme: How Cybercriminals are Weaponizing Google’s Trusted Services for Global Phishing GTFire Phishing Campaign Google Firebase Abuse
  • Cybercriminals

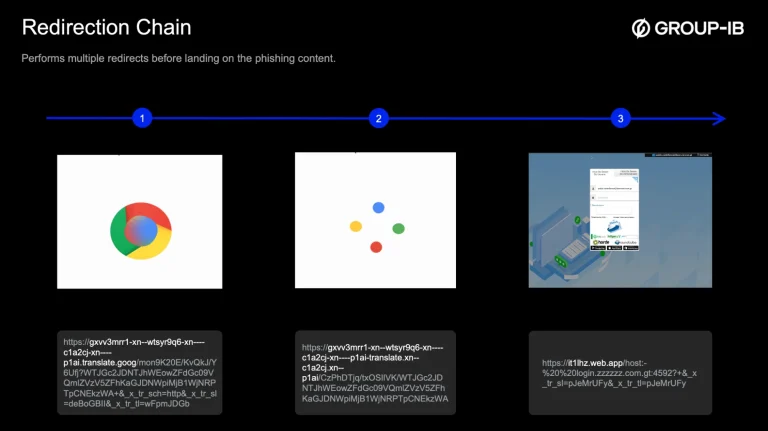
The GTFire Scheme: How Cybercriminals are Weaponizing Google’s Trusted Services for Global Phishing

Do Son March 2, 2026 0

Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.
OCRFix: When Fake CAPTCHAs, AI, and Blockchains Collide to Build a Botnet OCRFix Malware Campaign ClickFix Tactic
  • Malware

OCRFix: When Fake CAPTCHAs, AI, and Blockchains Collide to Build a Botnet

Do Son March 2, 2026 0

CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

CVE-2026-27728 (CVSS 10): Critical Command Injection Flaw in OneUptime Probe Enables Full Server Takeover OneUptime RCE CVE-2026-27728
  • Vulnerability Report

CVE-2026-27728 (CVSS 10): Critical Command Injection Flaw in OneUptime Probe Enables Full Server Takeover

Do Son March 2, 2026 0

OneUptime 10.0.7 patches a critical 10.0 CVSS vulnerability (CVE-2026-27728). Attackers can use traceroute probes to execute root commands and steal data.

Critical Path Traversal Flaw in basic-ftp Exposes Node.js Apps to Arbitrary File Writes shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical Path Traversal Flaw in basic-ftp Exposes Node.js Apps to Arbitrary File Writes

Do Son March 2, 2026 0

Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.

Steering the Server: Critical 9.2 Severity SSRF Flaw in Angular SSR Allows Internal Network Probing Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

Steering the Server: Critical 9.2 Severity SSRF Flaw in Angular SSR Allows Internal Network Probing

Do Son March 2, 2026 0

Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

The New Voice of Fraud: Cybercrime ‘Supergroup’ Recruits Female Callers to Breach Corporate IT Help Desks CRussian Market, "Fly" (Flyded) hange Healthcare Cyberattack - CVE-2024-50603 Exploit
  • Cybercriminals

The New Voice of Fraud: Cybercrime ‘Supergroup’ Recruits Female Callers to Breach Corporate IT Help Desks

Do Son March 2, 2026 0

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.

WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors Screenshot_20260303_002337_Docs
  • Technique

WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors

Do Son March 2, 2026 0
The last 50% percent reduction of the price of bitcoin has dramatically changed the trend of crypto...
Read More Read more about WPA Hash Analysis: Turning Bitcoin’s 50% Drop into Cloud Mining Opportunities for Investors
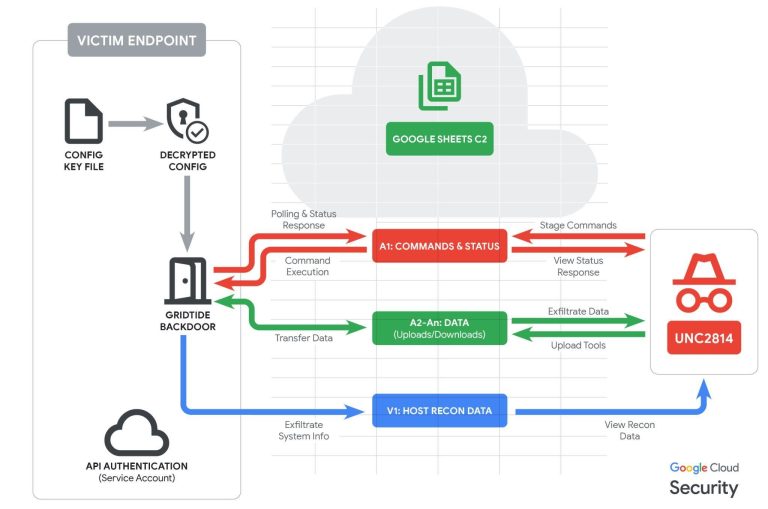
Google Dismantles UNC2814’s Global Espionage Network Fueled by Google Sheets UNC2814 Espionage GRIDTIDE Backdoor
  • Cybercriminals

Google Dismantles UNC2814’s Global Espionage Network Fueled by Google Sheets

Do Son March 2, 2026 0

Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-68935CVSS 9.1
    Chartbrew is an open-source web application for creating charts from databases and APIs. In versions 4.8.5 through 5.2.2,...
    📅 Updated: Nov 6, 2026
  • CVE-2025-9230CVSS 9.8
    Issue summary: An application trying to decrypt CMS messages encrypted using password based encryption can trigger an out-of-bounds...
    📅 Updated: Nov 6, 2026
  • CVE-2024-4741CVSS 9.8
    Issue summary: Calling the OpenSSL API function SSL_free_buffers may cause memory to be accessed that was previously freed...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.