Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses OAuth Phishing Redirect URI Abuse
  • Cybercriminals

OAuth Hijack: Phishing Campaigns Weaponize Legitimate Redirection to Bypass Defenses

Do Son March 4, 2026 0

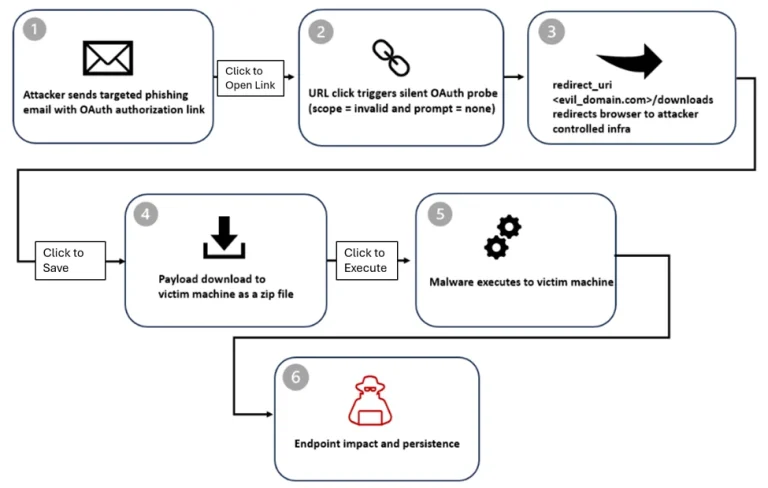
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing ClickFix Malware Crypto VC Scam
  • Malware

ClickFix Alert: Fake Venture Capitalists Target Web3 Pros with “Terminal” Phishing

Do Son March 4, 2026 0

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading FileZilla Malware DLL Hijacking
  • Malware

Trojanized FileZilla FTP Client Targets Developer Credentials via DLL Sideloading

Do Son March 4, 2026 0

Malwarebytes uncovers a trojanized FileZilla campaign using DLL hijacking and DNS-over-HTTPS to silently steal FTP credentials and bypass security.
Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request Qwik RCE CVE-2026-27971
  • Vulnerability Report

Critical RCE Flaw in Qwik Framework Allows Server Takeover via Single Request

Do Son March 4, 2026 0

Qwik framework patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-27971) where unsafe deserialization in server$ RPC allows total server takeover.
The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia Sloppy Lemming BurrowShell Malware
  • Cyber Security
  • Malware

The BurrowShell Threat: Inside ‘Sloppy Lemming’s’ Stealthy Cyber Espionage Campaign in South Asia

Do Son March 4, 2026 0

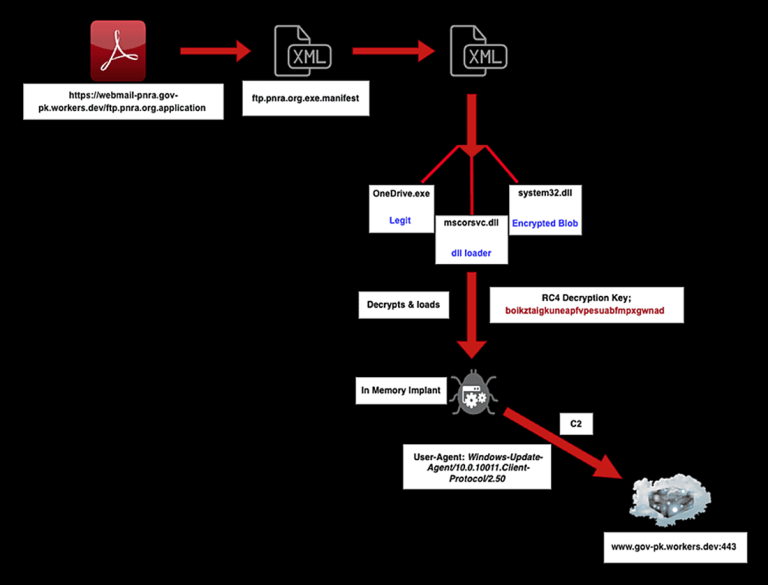
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void AuraStealer Malware Infostealer
  • Malware

AuraStealer: The “Result-Oriented” Malware Rising from the Post-Lumma Void

Do Son March 4, 2026 0

Following the Lumma takedown, the sophisticated AuraStealer malware is rapidly gaining ground, using TikTok scams and stealth to harvest data.

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots AI Prompt Injection Aqua Trivy Breach AI Assistant Apertus, open-source AI .ai domain milestone
  • Vulnerability Report

The Trojan Prompt: How an Autonomous AI Hijacked Aqua Trivy to Weaponize Developer Copilots

Do Son March 4, 2026 0

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Malware

PlugX Evolves: New “Meeting Invitation” Phishing Campaign Leverages Trusted Security Software

Do Son March 4, 2026 0

LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM image_18_1772539903dkCSeaHBoZ
  • Press Release

Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM

cybernewswire March 3, 2026 0
San Francisco, CA, United States, 3rd March 2026, CyberNewswire
Read More Read more about Archipelo and Checkmarx Announce Partnership Connecting AppSec Detection with DevSPM
Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury” GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Cyber Escalation: Multi-Vector Attacks Surge Following “Operation Epic Fury”

Do Son March 3, 2026 0

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.

Security Alert: “Hackerbot-Claw” Autonomous Campaign Exploits GitHub Actions hackerbot-claw campaign Cisco RCE Exploit CVE-2026-20045 SonicWall VPN, Akira Ransomware Nobelium Apache Tomcat, Apache Camel
  • Vulnerability Report

Security Alert: “Hackerbot-Claw” Autonomous Campaign Exploits GitHub Actions

Do Son March 3, 2026 0

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

Anthropic Launches “Memory Import” to Rescue Your ChatGPT Context Amid #QuitGPT Exodus Claude Memory Import
  • Technology

Anthropic Launches “Memory Import” to Rescue Your ChatGPT Context Amid #QuitGPT Exodus

Do Son March 3, 2026 0

Anthropic’s new "Memory Import" tool lets you move your ChatGPT context to Claude in minutes. Perfect for those joining the #QuitGPT movement this March.

Samsung Wallet Adopts Aliro Standard to Unlock Your Home with a Galaxy Tap Samsung Wallet Digital Home Key
  • Technology

Samsung Wallet Adopts Aliro Standard to Unlock Your Home with a Galaxy Tap

Do Son March 3, 2026 0

Samsung Wallet now supports "Digital Home Key" via the Aliro standard. Unlock your door with a Galaxy tap, secured by EAL6+ hardware and Samsung Knox.

Apple Unveils the iPhone 17e with A19 Power and MagSafe for $599 A19 processor
  • Technology

Apple Unveils the iPhone 17e with A19 Power and MagSafe for $599

Do Son March 3, 2026 0

Apple’s new iPhone 17e brings the A19 chip, MagSafe, and Apple Intelligence to a $599 price point. With 256GB base storage, it’s the new king of value.

Red Lines in the Rubble: OpenAI Enters the “Department of War” as Claude AI Powers Strikes on Iran OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Red Lines in the Rubble: OpenAI Enters the “Department of War” as Claude AI Powers Strikes on Iran

Do Son March 3, 2026 0

OpenAI signs a classified deal with the "Department of War" as the US military continues using banned Anthropic tech for high-stakes airstrikes in Iran.

Urgent Patch Required: HPE AutoPass License Server Hits Maximum Severity Risk HPE AutoPass Vulnerability, CVE-2026-23600 CVE-2024-22442 - HPE vulnerability HPE Storage Vulnerability CVE-2026-23594
  • Vulnerability Report

Urgent Patch Required: HPE AutoPass License Server Hits Maximum Severity Risk

Do Son March 3, 2026 0

HPE warns of a critical CVSS 10.0 vulnerability (CVE-2026-23600) in AutoPass License Server. Remote attackers can bypass authentication. Patch to 9.19 now!

North Korean “StegaBin” Campaign Targets Developers with Steganographic Malware North Korean Laptop Farm DPRK Insider Threat North Korea WMD Cyber Funding, Australia Sanctions Insider threat, North Korean hackers Kimsuky, cyber-espionage NPM Malware, North Korea Cyber-espionage North Korea, Remote IT Job Scam Laptop Farm - DriverEasy - Kimsuky Watering Hole Attack
  • Malware

North Korean “StegaBin” Campaign Targets Developers with Steganographic Malware

Do Son March 3, 2026 0

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.

Security Alert: Android March 2026 Update Targets Actively Exploited Zero-Day Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android
  • Vulnerability Report

Security Alert: Android March 2026 Update Targets Actively Exploited Zero-Day

Do Son March 3, 2026 0

Google’s March 2026 Android update fixes 129 flaws, including CVE-2026-21385—a high-severity Qualcomm vulnerability currently being exploited in the wild.

CVE-2026-2256: Unpatched Flaw in MS-Agent Lets Hackers Hijack AI Assistants shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-2256: Unpatched Flaw in MS-Agent Lets Hackers Hijack AI Assistants

Do Son March 3, 2026 0

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
Beyond the Router: How the Zerobotv9 Botnet is Hijacking Enterprise Automation Zerobotv9 Botnet n8n Vulnerability VMware ESXi Ransomware
  • Malware

Beyond the Router: How the Zerobotv9 Botnet is Hijacking Enterprise Automation

Do Son March 3, 2026 0

Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.

High-Severity XSS Flaw in Angular i18n Turns Language Files into Backdoors Angular hostname hijacking vulnerability Angular SSRF Origin Hijacking Angular XSS Vulnerability CVE-2026-32635 Angular i18n XSS CVE-2026-27970 Angular SSR SSRF CVE-2026-27739 Angular Vulnerability CVE-2026-22610 CVE-2025-59052 Angular security Angular XSS Bypass, SVG Injection
  • Vulnerability Report

High-Severity XSS Flaw in Angular i18n Turns Language Files into Backdoors

Do Son March 3, 2026 0

Angular patches a high-severity 7.6 CVSS XSS flaw (CVE-2026-27970). Attackers can weaponize i18n translation files to steal data and hijack user sessions.

From Chat App to Dark Web: How Telegram Became the New Hub for Cybercrime CVE-2024-22394
  • Cybercriminals

From Chat App to Dark Web: How Telegram Became the New Hub for Cybercrime

Do Son March 3, 2026 0

Cyfirma reveals how Telegram has replaced the dark web as the ultimate digital black market, making tools like malware and data theft available to anyone.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-68935CVSS 9.1
    Chartbrew is an open-source web application for creating charts from databases and APIs. In versions 4.8.5 through 5.2.2,...
    📅 Updated: Nov 6, 2026
  • CVE-2025-9230CVSS 9.8
    Issue summary: An application trying to decrypt CMS messages encrypted using password based encryption can trigger an out-of-bounds...
    📅 Updated: Nov 6, 2026
  • CVE-2024-4741CVSS 9.8
    Issue summary: Calling the OpenSSL API function SSL_free_buffers may cause memory to be accessed that was previously freed...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.