Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Stealth and Deception: Transparent Tribe’s Multi-Stage Assault on Indian Government Entities NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cyber Security

Stealth and Deception: Transparent Tribe’s Multi-Stage Assault on Indian Government Entities

Do Son March 5, 2026 0

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.

Intelligence Compromised: Data Abyss Report Details China’s Exploitation of U.S. IARPA Research IARPA Research Security Data Abyss Report Telecom threat, Secret Service cybersecurity news - Cyber Espionage Campaign
  • Cyber Security

Intelligence Compromised: Data Abyss Report Details China’s Exploitation of U.S. IARPA Research

Do Son March 5, 2026 0

A new Data Abyss report reveals how PRC-affiliated entities systematically exploited U.S. IARPA research to advance China's military capabilities.
The Return of Funnull: Rebranded and Ramping Up Supply Chain Attacks Funnull Syndicate RingH23 Framework
  • Cybercriminals

The Return of Funnull: Rebranded and Ramping Up Supply Chain Attacks

Do Son March 5, 2026 0

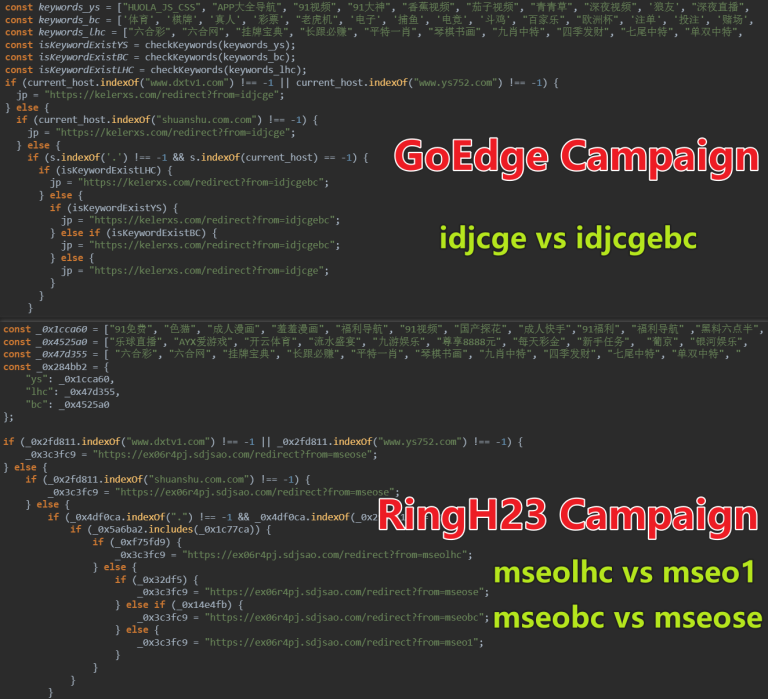
XLab researchers reveal the return of OFAC-sanctioned Funnull. The group is using the new RingH23 framework to hijack CDNs and poison supply chains.
Reclaim Security Raises $26M to Eliminate the 27-Day Remediation Gap WhatsApp_Image_2026-03-04_at_35548_PM_17726342808yOtGeCk70
  • Press Release

Reclaim Security Raises $26M to Eliminate the 27-Day Remediation Gap

cybernewswire March 4, 2026 0
New York, USA, 4th March 2026, CyberNewswire
Read More Read more about Reclaim Security Raises $26M to Eliminate the 27-Day Remediation Gap
How to Improve Home Security: What Every St. Louis Homeowner Needs to Know WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Technique

How to Improve Home Security: What Every St. Louis Homeowner Needs to Know

Do Son March 4, 2026 0
Home security is a growing concern for residents across St. Louis, Missouri. Whether you live in Soulard,...
Read More Read more about How to Improve Home Security: What Every St. Louis Homeowner Needs to Know
Android’s March Update Brings “Find Hub” Luggage Sharing and Play Store Shorts Android March 2026 update
  • Android

Android’s March Update Brings “Find Hub” Luggage Sharing and Play Store Shorts

Do Son March 4, 2026 0

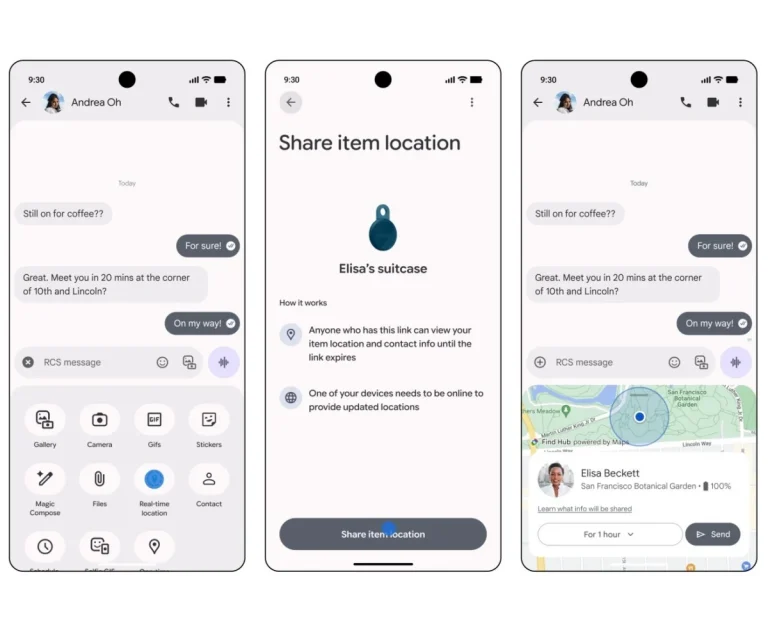
Google’s March 2026 update is live! From sharing lost luggage links with airlines via Find Hub to perusing apps via Play Store Shorts, see what's new.

From $180 to $82,000 in 48 Hours: The Gemini API Key Leak Bankrupting Small Dev Teams Google Gemini Enterprise, AI Agents No-Code
  • Data Leak

From $180 to $82,000 in 48 Hours: The Gemini API Key Leak Bankrupting Small Dev Teams

Do Son March 4, 2026 0

A Mexican dev team faces bankruptcy after a leaked Gemini API key racked up an $82,314 bill in 48 hours. Is Google Cloud's billing model to blame?
240,000 OpenClaw AI Instances Exposed to the Public Web OpenClaw AI security
  • Data Leak

240,000 OpenClaw AI Instances Exposed to the Public Web

Do Son March 4, 2026 0

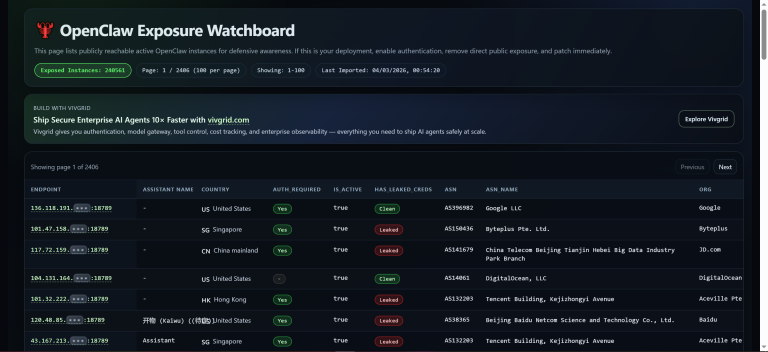
240,000 OpenClaw AI instances are currently exposed to the public internet. Learn how to secure your personal assistant before it becomes a portal for hackers.

Drone Strikes Cripple AWS Data Centers Across the Middle East Motorola Smart Feed redirect Anthropic Amazon 5GW partnership Amazon Perplexity lawsuit AWS-LC Vulnerabilities Cryptographic Bypass AWS Middle East drone strikes Amazon layoffs 2026, Amazon AI restructuring Amazon Kindle DRM Policy, Publisher Control EPUB AWS Nova Forge AI Model Customization AWS Trainium3 EC2 Trn3 UltraServer Route 53 Accelerated Recovery AWS DNS Resilience AI Browser War, Amazon Comet Amazon layoffs, cost reduction AWS outage, DynamoDB DNS AWS outage, cloud dependency AWS VPN Client, Root Privilege Escalation WSA shutdown, Amazon Appstore Amazon Wondery, Podcast Restructuring Amazon Q2 2025 Generative AI AWS Client VPN, Privilege Escalation Amazon AI, Wearable AI
  • Technology

Drone Strikes Cripple AWS Data Centers Across the Middle East

Do Son March 4, 2026 0

Successive drone strikes on AWS data centers in the UAE and Bahrain have caused catastrophic outages. Amazon urges immediate data migration as conflict escalates.
Google Launches Gemini 3.1 Flash-Lite for High-Speed, Low-Cost AI Scaling Gemini AI branching threads Gemini 3.1 Flash-Lite Google Gemini compute shortage affecting Meta operations and AI token limits
  • Technology

Google Launches Gemini 3.1 Flash-Lite for High-Speed, Low-Cost AI Scaling

Do Son March 4, 2026 0

Google’s Gemini 3.1 Flash-Lite is here! At $0.25/1M tokens and 2.5x faster speeds, it’s the new champion for high-volume, low-latency enterprise AI workloads.
The AI Heartbeat: Why Microsoft is Moving Build 2026 to San Francisco’s Historic Fort Mason Microsoft Build 2026
  • Technology

The AI Heartbeat: Why Microsoft is Moving Build 2026 to San Francisco’s Historic Fort Mason

Do Son March 4, 2026 0

Microsoft Build 2026 moves to San Francisco on June 2–3. With a 2,500-attendee limit at Fort Mason, the focus is on "Agentic AI" and deep technical immersion.

Personal Superintelligence: Meta AI Unveils “Shopping Research” to Take on Gemini and ChatGPT Instagram account recovery flaw Meta incident notification Meta AI data center Louisiana Meta AI news partnerships Meta AI Shopping Assistant Meta Vibes standalone app Meta Oversight Board account ban, Instagram permanent suspension review Meta Compute initiative 2026, personal superintelligence nuclear power Meta AI News Licensing Publisher Content Deal Meta Project Mercury Omnilingual ASR 1600 Languages Meta $600B Investment, AI Data Centers Meta AI strategy, Llama models Meta AI Glasses, Smart Glasses
  • Technology

Personal Superintelligence: Meta AI Unveils “Shopping Research” to Take on Gemini and ChatGPT

Do Son March 4, 2026 0

Meta AI launches "Shopping Research" trials in the US. With visual carousels and tailored advice, Zuckerberg’s agentic tools aim to revolutionize e-commerce.
The Ray Tracing Revolution: Microsoft’s Shader Model 6.9 Unlocks a 90% Power Surge for Intel and NVIDIA Shader Execution Reordering (SER)
  • Technology

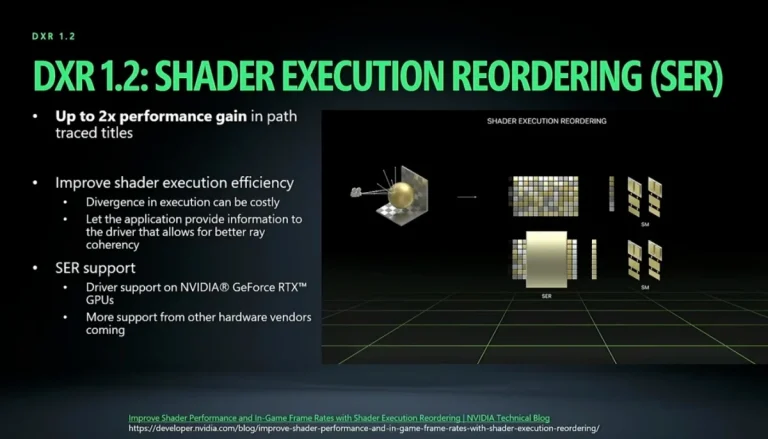
The Ray Tracing Revolution: Microsoft’s Shader Model 6.9 Unlocks a 90% Power Surge for Intel and NVIDIA

Do Son March 4, 2026 0

Microsoft’s Shader Model 6.9 introduces Shader Execution Reordering (SER), delivering a staggering 90% ray tracing boost for Intel Arc and 40% for NVIDIA GPUs.

From Vision to Validation: Ericsson Unveils the “Superbrain” of 6G with First Live OTA Trials at MWC 2026 Ericsson 6G OTA trial CVE-2024-39696
  • Technology

From Vision to Validation: Ericsson Unveils the “Superbrain” of 6G with First Live OTA Trials at MWC 2026

Do Son March 4, 2026 0

Ericsson makes 6G real at MWC 2026 with the world’s first pre-standard OTA trial and radar-like ISAC technology, powering the next era of AI-native networks.

Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins iOS 27 Apple Intelligence Apple AI Extensions bazaar Siri iOS 27 Gemini integration Apple AI server Baltra Siri AI delay iOS 26.4 Apple Google Gemini Siri partnership, Siri powered by Google Gemini 2026 Siri Gemini, Apple Intelligence Siri, Apple AI Apple "Veritas", Siri AI Siri Gemini Supercharged Siri, AI assistant Siri Integration, App Intents Apple Siri Apple AI Strategy, ChatGPT Rival
  • Technology

Siri’s Secret Engine: Why 90% of Apple’s AI Servers are Idle as Google Gemini Takes the Reins

Do Son March 4, 2026 0

Apple’s AI infrastructure faces a 90% dormancy crisis. To save Siri, Apple is turning to Google Gemini while secretly developing the 3nm "Baltra" AI chip.
Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service OpenStack Vitrage RCE CVE-2026-28370
  • Vulnerability Report

Critical RCE Vulnerability Discovered in OpenStack Vitrage Root Cause Analysis Service

Do Son March 4, 2026 0

Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.
Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability

Critical Auth Bypass in Apache Artemis: Attackers Can Hijack Message Queues

Do Son March 4, 2026 0

A critical flaw (CVE-2026-27446) in Apache Artemis allows unauthenticated attackers to hijack message queues via rogue brokers. Update to 2.52.0 immediately.

Django Releases Security Patches to Address DoS and Permission Vulnerabilities Django Security Update CVE-2026-25673 Django Security Update SQL Injection Vulnerability Django SQL Injection, PostgreSQL Flaw CVE-2022-34265 PoC Django, SQL injection
  • Vulnerability Report

Django Releases Security Patches to Address DoS and Permission Vulnerabilities

Do Son March 4, 2026 0

Django releases security updates (6.0.3, 5.2.12, 4.2.29) to fix a Windows DoS flaw (CVE-2026-25673) and file permission risks. Upgrade your framework now.

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability Report

CISA Adds Qualcomm and VMware Flaws to Known Exploited Catalog

Do Son March 4, 2026 0

CISA adds actively exploited Qualcomm (CVE-2026-21385) and VMware (CVE-2026-22719) flaws to its KEV catalog. See the impact and patch deadlines inside.

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes Iranian Hacktivists Operation Epic Fury Cyber New Generation Warfare Russian Hybrid Escalation Plex data breach Water Systems Cybersecurity - Threat Actor Naming Standard
  • Cyber Security

Cyber Retaliation Escalates: Iranian Hacktivists Target Critical Infrastructure Following Military Strikes

Do Son March 4, 2026 0

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution AVideo RCE YPTSocket Vulnerability AVideo Vulnerabilities Streaming Platform Security AVideo Vulnerabilities CVE-2026-28501
  • Vulnerability Report

Critical Vulnerabilities in AVideo: From SQL Injection to Remote Code Execution

Do Son March 4, 2026 0

AVideo patches two critical flaws (CVE-2026-28501 & 28502) allowing unauthenticated SQL injection and remote code execution. Update to version 23 now.

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin WordPress Privilege Escalation CVE-2026-1492 Sneeit Framework RCE, Unauthenticated Code Execution Post SMTP, Account Takeover WordPress Vulnerability, Unpatched XSS WordPress Vulnerability, PHP Object Injection WordPress AI Engine, Privilege Escalation CVE-2024-43153 & CVE-2024-43234
  • Vulnerability Report

WordPress Security Alert: Critical Privilege Escalation Flaw in Popular Membership Plugin

Do Son March 4, 2026 0

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-109469CVSS 10.0
    Authorization bypass through user-controlled key in Entra Device Registration allows an unauthorized attacker to elevate privileges over a...
    📅 Updated: Nov 6, 2026
  • CVE-2026-68935CVSS 9.1
    Chartbrew is an open-source web application for creating charts from databases and APIs. In versions 4.8.5 through 5.2.2,...
    📅 Updated: Nov 6, 2026
  • CVE-2025-9230CVSS 9.8
    Issue summary: An application trying to decrypt CMS messages encrypted using password based encryption can trigger an out-of-bounds...
    📅 Updated: Nov 6, 2026
  • CVE-2024-4741CVSS 9.8
    Issue summary: Calling the OpenSSL API function SSL_free_buffers may cause memory to be accessed that was previously freed...
    📅 Updated: Nov 6, 2026
  • CVE-2026-59104CVSS 9.3
    UgCS server before 6.2 contains an authentication bypass in the HCI protocol login handler (LoginHandler) exposed on TCP...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54143CVSS 9.8
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before version 0.57.13, an...
    📅 Updated: Nov 6, 2026
  • CVE-2026-54141CVSS 9.0
    OpenHuman is an open-source agent harness available as a desktop application and Rust library. Before 0.57.13, a remote...
    📅 Updated: Nov 6, 2026
  • CVE-2026-77596CVSS 9.6
    Kubeflow Pipelines enables users to build and deploy portable, scalable machine learning workflows. Prior to 2.18.0, the multi-user...
    📅 Updated: Nov 6, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.