Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Beyond the Chatbot: Google I/O 2026 to Unveil the “Agentic” Future of Android 17 Google I/O 2026 dates
  • Technology

Beyond the Chatbot: Google I/O 2026 to Unveil the “Agentic” Future of Android 17

Do Son February 18, 2026 0

Google I/O 2026 kicks off May 19! Discover how Gemini 3 and Android 17 are turning your phone into a proactive AI concierge. The era of the agent is here.

Critical Honeywell CCTV Flaw (CVSS 9.8) Allows Unauthenticated Takeover Honeywell CCTV Vulnerability CVE-2026-1670 EagleMsgSpy Spyware Tool ResidentBat Spyware, Belarusian KGB Surveillance
  • Vulnerability Report

Critical Honeywell CCTV Flaw (CVSS 9.8) Allows Unauthenticated Takeover

Do Son February 18, 2026 0

CISA warns of Honeywell CCTV flaw CVE-2026-1670. Unauthenticated attackers can reset passwords & hijack feeds. Update firmware immediately.

New CRESCENTHARVEST Malware Targets Iranian Dissidents Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

New CRESCENTHARVEST Malware Targets Iranian Dissidents

Do Son February 18, 2026 0

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

Fake Jobs, Real Theft: “Contagious Interview” Malware Drains Crypto Wallets Contagious Interview Campaign MetaMask Malware
  • Cybercriminals

Fake Jobs, Real Theft: “Contagious Interview” Malware Drains Crypto Wallets

Do Son February 18, 2026 0

North Korean hackers target IT pros with "Contagious Interview" malware. Fake job offers install trojanized MetaMask extensions to steal crypto.

The “I Paid Twice” Trap: New Booking.com Phishing Kit Targets Hotels & Guests Booking.com Fraud Hospitality Phishing
  • Cybercriminals

The “I Paid Twice” Trap: New Booking.com Phishing Kit Targets Hotels & Guests

Do Son February 18, 2026 0

Bridewell warns of Russian hackers targeting Booking.com. Phishing kits steal hotel staff creds to scam guests with "I Paid Twice" messages.
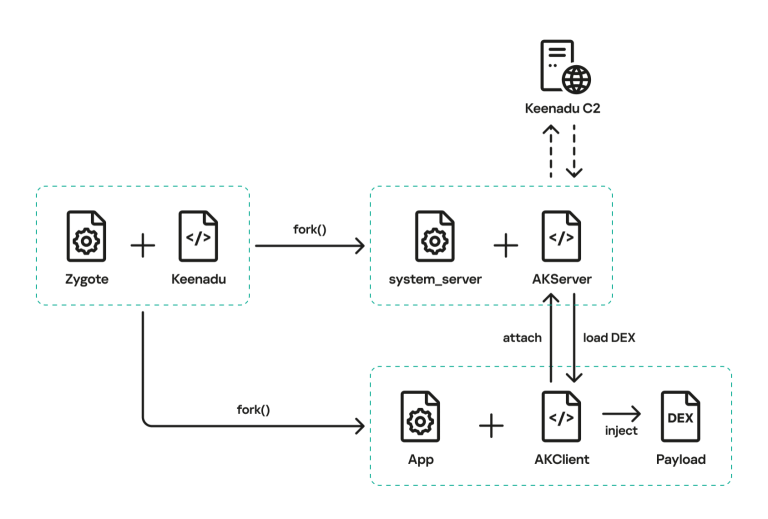
Infected Out of the Box: “Keenadu” Backdoor Hijacks Android at the Firmware Level Keenadu Malware Android Firmware Backdoor
  • Malware

Infected Out of the Box: “Keenadu” Backdoor Hijacks Android at the Firmware Level

Do Son February 18, 2026 0

Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.

PostgreSQL Fixes 5 Security Flaws Including Critical Code Execution Risks PostgreSQL Vulnerabilities CVE-2026-2006 PostgreSQL, security update CVE-2023-5869 - CVE-2025-1094
  • Vulnerability Report

PostgreSQL Fixes 5 Security Flaws Including Critical Code Execution Risks

Do Son February 18, 2026 0

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.

Ghost NICs & Secret Knocks: Dell Zero-Day (CVSS 10) Exploited by UNC6201 FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Cyber Security
  • Vulnerability Report

Ghost NICs & Secret Knocks: Dell Zero-Day (CVSS 10) Exploited by UNC6201

Do Son February 18, 2026 0

Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.

Hackers Use Jira Notifications to Bypass Spam Filters Layoff Phishing Scam Remcos RAT Malware Aruba Phishing, Phishing-as-a-Service PyPI, phishing CVE-2024-25608 PyPI Phishing, Credential Theft
  • Cybercriminals

Hackers Use Jira Notifications to Bypass Spam Filters

Do Son February 18, 2026 0

Hackers abuse Atlassian Jira notifications to bypass spam filters. Trend Micro warns of scams targeting enterprise users via trusted alerts.

“Dormant” Backdoors: Ivanti EPMM Zero-Days Exploited to Plant Long-Term Spies Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability Report

“Dormant” Backdoors: Ivanti EPMM Zero-Days Exploited to Plant Long-Term Spies

Do Son February 18, 2026 0

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.

CISA Adds 2008 Windows Flaw & Chrome Zero-Day to KEV Ivanti EPMM Vulnerability CVE-2026-1340 CISA KEV Catalog CVE-2026-21385 CISA KEV Update CVE-2008-0015 CISA KEV, Array Networks Command Injection CVE-2025-0111 & CVE-2025-23209 CISA, Known Exploited Vulnerabilities
  • Vulnerability Report

CISA Adds 2008 Windows Flaw & Chrome Zero-Day to KEV

Do Son February 18, 2026 0

CISA adds 4 flaws to KEV: Ancient Windows ActiveX bug (CVE-2008-0015) & new Chrome zero-day (CVE-2026-2441). Patch now to prevent exploitation.

CredShields Leads OWASP Smart Contract Top 10 2026 as Governance and Access Failures Drive Onchain Risk image_11_1771162797WWbMlSTnA5
  • Press Release

CredShields Leads OWASP Smart Contract Top 10 2026 as Governance and Access Failures Drive Onchain Risk

cybernewswire February 17, 2026 0
SINGAPORE, Singapore, 17th February 2026, CyberNewswire
Read More Read more about CredShields Leads OWASP Smart Contract Top 10 2026 as Governance and Access Failures Drive Onchain Risk
Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution Cybersecurity_Insiders_Press_Release_FEB_2026_1771270319lAAqrrrXI9
  • Press Release

Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution

cybernewswire February 17, 2026 0
Washington DC, USA, 17th February 2026, CyberNewswire
Read More Read more about Cybersecurity Excellence Awards Reveal Nomination Shift from AI Hype to Governance Execution
Apache NiFi Flaw (CVE-2026-25903) Lets Users Bypass Restrictions Apache NiFi RCE CVE-2026-39816 Apache NiFi Vulnerability CVE-2026-25903 Apache NiFi Deserialization, GetAsanaObject Vulnerability CVE-2024-52067 - CVE-2024-56512 CVE-2025-27017
  • Vulnerability Report

Apache NiFi Flaw (CVE-2026-25903) Lets Users Bypass Restrictions

Do Son February 17, 2026 0

Apache NiFi flaw CVE-2026-25903 allows unauthorized users to modify restricted components. Update to version 2.8.0 immediately to secure data pipelines.

The Great Refurbishment: Why iOS 27 is the “Vernal Cleansing” Your iPhone Battery Needs FCC Chinese lab ban iPhone NATO certification iPhone 18 Pro Deep Red iOS 27 Snow Leopard update 2026 smartphone memory shortage, IDC mobile market forecast iPhone Satellite Natural Usage iPhone 17 Speaker Issue, USB-C Static iPhone 17 Pro, MagSafe Scratches iPhone 17 Pro, professional filmmaking
  • Technology

The Great Refurbishment: Why iOS 27 is the “Vernal Cleansing” Your iPhone Battery Needs

Do Son February 17, 2026 0

iOS 27 ditched flashy features for a "Snow Leopard" style cleanup. Discover how Apple is purging 20 years of legacy code to save your iPhone's battery life.

The Rise of the Digital Concierge: OpenAI Hires OpenClaw Visionary to Turn ChatGPT into an Autonomous Agent ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

The Rise of the Digital Concierge: OpenAI Hires OpenClaw Visionary to Turn ChatGPT into an Autonomous Agent

Do Son February 17, 2026 0

OpenAI hires OpenClaw creator Peter Steinberger to lead its "Personal Agent" revolution, aiming to turn ChatGPT into a proactive, task-executing concierge.

Hiding in Plain Sight: APT28’s “Operation MacroMaze” Hits European Govs GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Hiding in Plain Sight: APT28’s “Operation MacroMaze” Hits European Govs

Do Son February 17, 2026 0

APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.
The AI Baseline: Apple’s “Special Experience” to Launch Budget MacBooks and M5 Powerhouses Apple Experience March 4 Apple Spring Event 2026
  • Technology

The AI Baseline: Apple’s “Special Experience” to Launch Budget MacBooks and M5 Powerhouses

Do Son February 17, 2026 0

Apple’s March 4 "Experience" debuts M5 Pro/Max chips and a colorful $699 MacBook. Say goodbye to "AI orphans" as Apple Intelligence goes global.
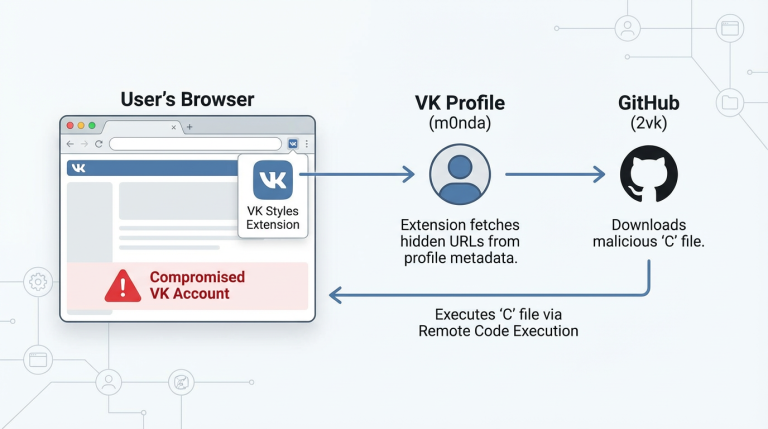
The “Styles” Trap: 500,000 VK Accounts Hijacked by Chrome Extensions VK Malicious Extensions VK Styles Campaign
  • Malware

The “Styles” Trap: 500,000 VK Accounts Hijacked by Chrome Extensions

Do Son February 17, 2026 0

500k VK accounts hijacked by "VK Styles" extensions. Malware forces subscriptions and bypasses CSRF tokens. Remove the extension immediately.
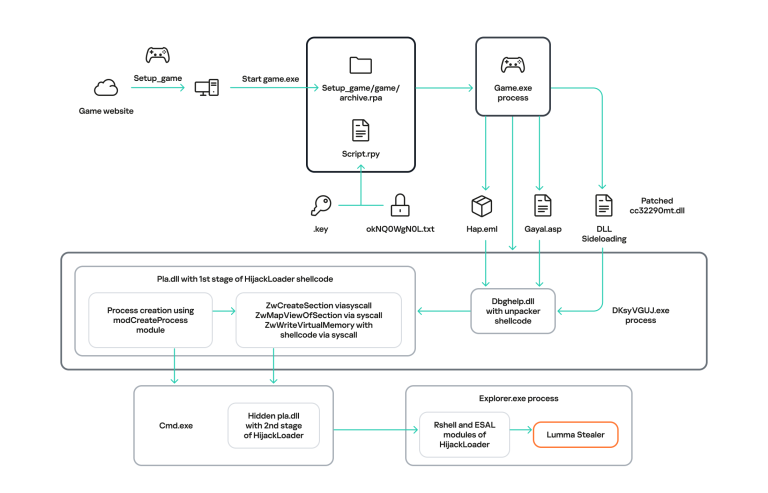
Game Over: “RenEngine” Malware Hides in Pirated Visual Novels RenEngine Malware Pirated Games Security
  • Malware

Game Over: “RenEngine” Malware Hides in Pirated Visual Novels

Do Son February 17, 2026 0

Kaspersky warns: Pirated visual novels are spreading RenEngine malware. Attackers use fake downloads to install ACR Stealer. Protect your data now.
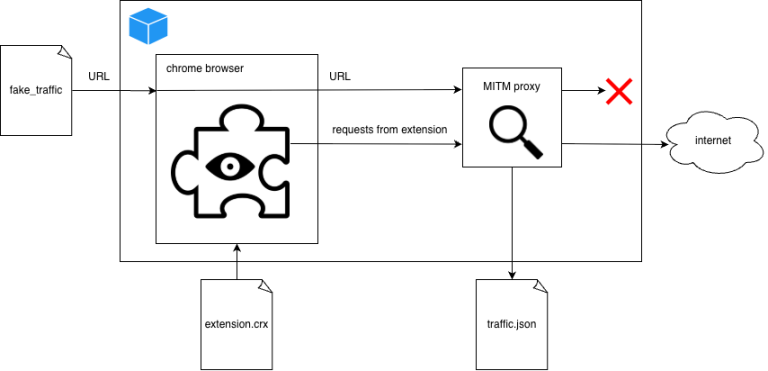
The 1% Breach: 287 Chrome Extensions Caught Spying on 37M Users Malicious Chrome Extensions
  • Data Leak

The 1% Breach: 287 Chrome Extensions Caught Spying on 37M Users

Do Son February 17, 2026 0

Q Continuum finds 287 Chrome extensions spying on 37M users. "Super PiP" & others exfiltrate history via Google Analytics. Check your browser now.
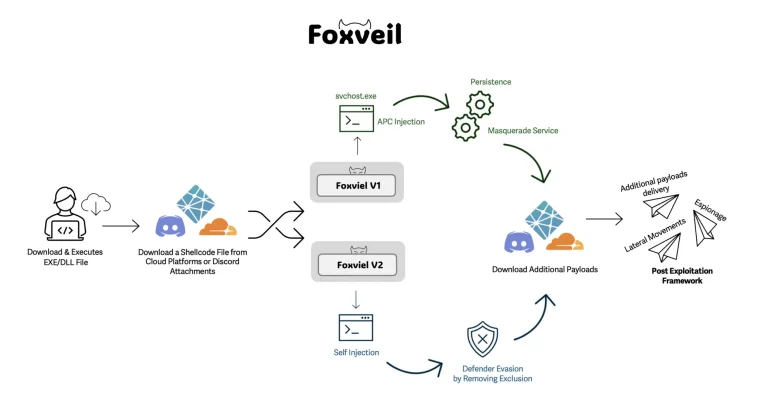
Foxveil: New Malware Loader Hides in Plain Sight Using Cloudflare and Discord Foxveil Malware
  • Malware

Foxveil: New Malware Loader Hides in Plain Sight Using Cloudflare and Discord

Do Son February 17, 2026 0

Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.