 Do Son
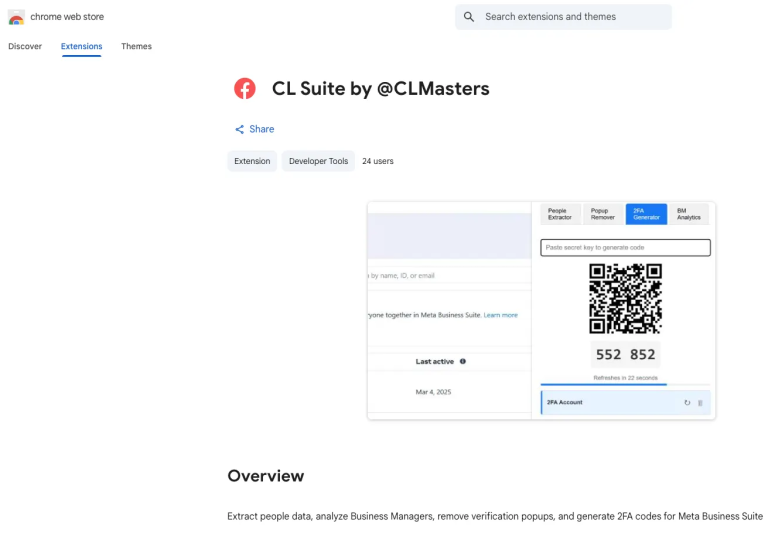
"CL Suite" Chrome extension steals Meta Business 2FA seeds & data. Attackers bypass security even after uninstall. Reset 2FA immediately.

Okta exposes North Korean IT workers using AI photos & stolen LinkedIn profiles to land remote jobs. Learn how "JJ" bypassed checks.

Elon Musk’s fortress holds firm. Despite slumping sales, Tesla resists Apple CarPlay due to navigation conflicts and iOS 26 adoption hurdles.

According to insights shared by Bloomberg’s Mark Gurman in his latest “Power On” dispatch, the rumored budget-oriented...
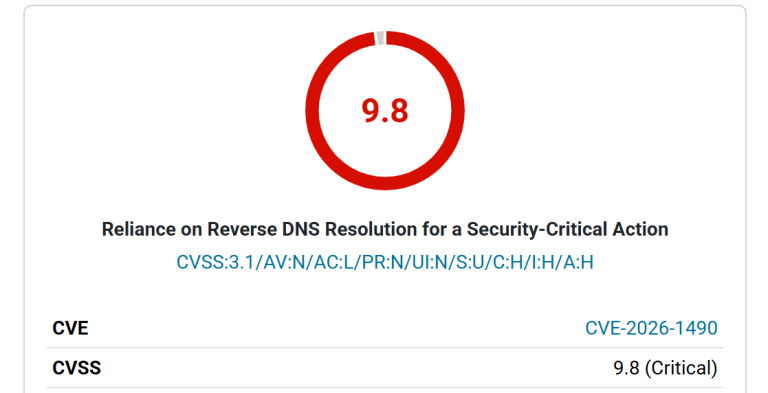
CleanTalk flaw CVE-2026-1490 (CVSS 9.8) exposes 200k sites to RCE via DNS spoofing. Attackers bypass auth to install plugins. Update to v6.72 now.
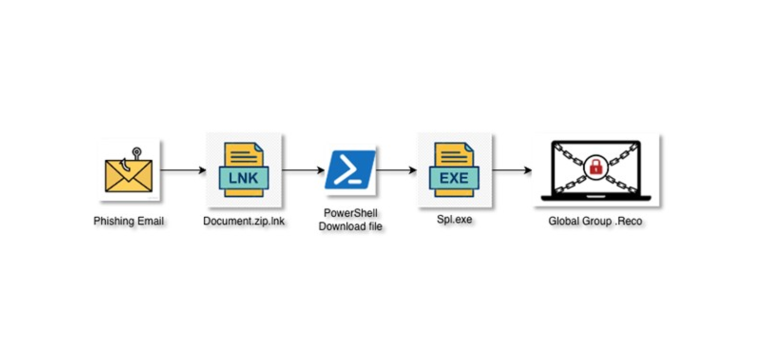
Phorpiex botnet returns in "Your Document" phishing campaign. Attackers use malicious .LNK files and hidden extensions to trick users.

CISA warns of critical Airleader Master vulnerability CVE-2026-1358. Unauthenticated attackers can upload files and gain RCE. Update to 6.386 now.
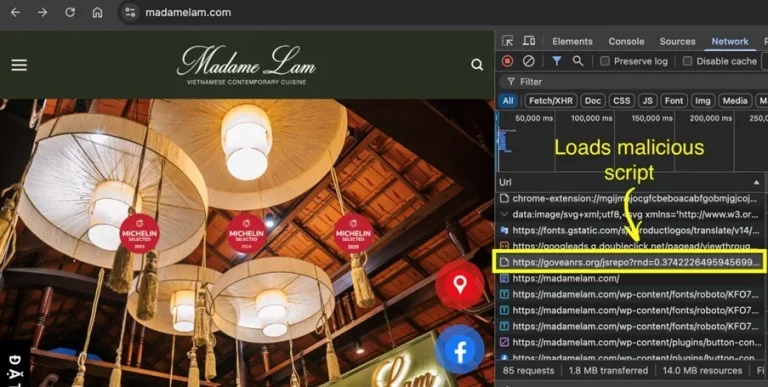
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.
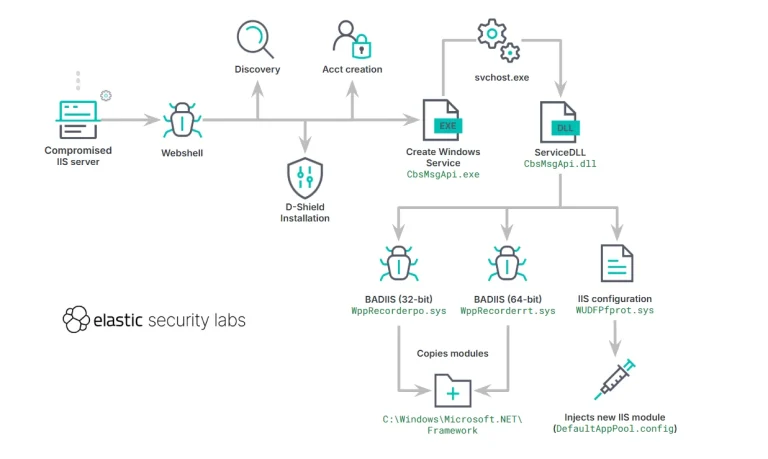
Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.
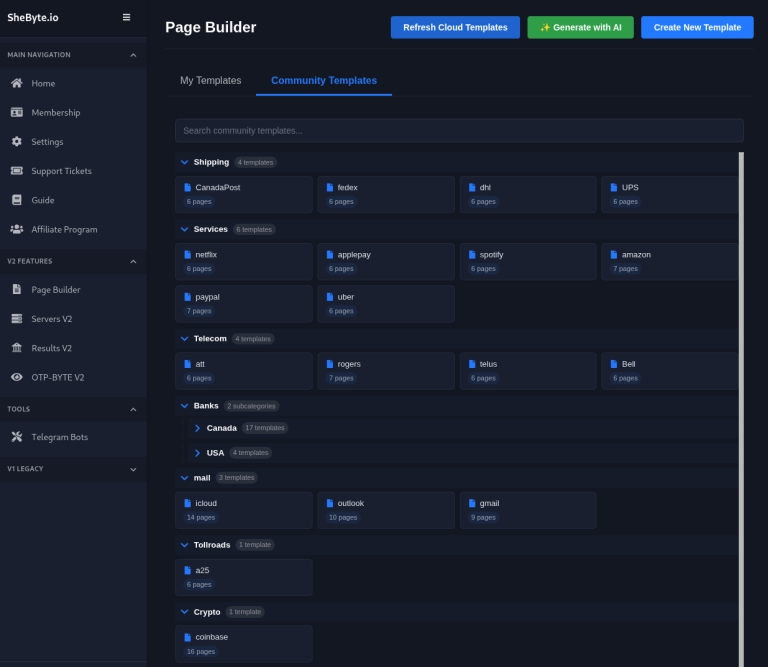
Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.
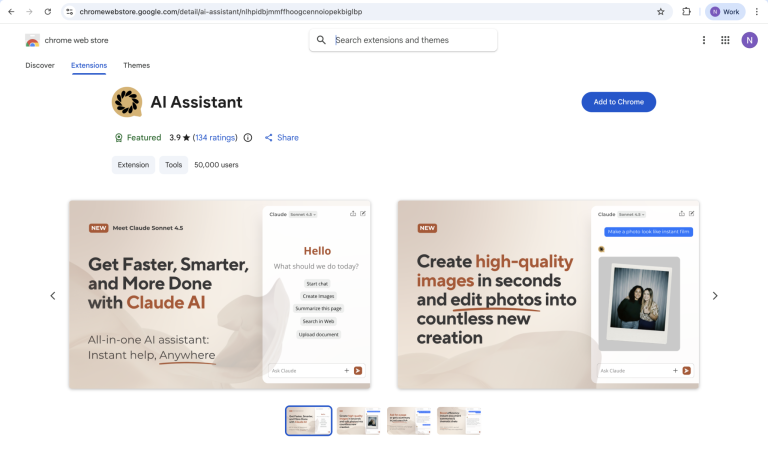
LayerX exposes 30+ malicious AI extensions spying on 260,000 users. These "privileged proxies" steal Gmail data & page content. Uninstall now.

New "Matryoshka" Mac malware uses "ClickFix" scams to steal crypto. Intego warns of fake error fixes patching Ledger & Trezor apps. Stay alert.

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

OysterLoader malware uses custom LZMA & steganography to evade tools. Linked to Rhysida ransomware, it hides in fake IT installers.
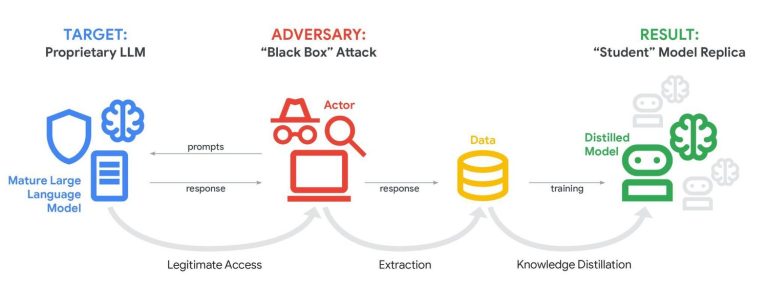
Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.

Critical FileZen flaw CVE-2026-25108 is under active attack. Antivirus feature allows command injection. Update to V5.0.11 immediately to secure data.
CISA warns of critical ZLAN5143D flaws CVE-2026-25084 & CVE-2026-24789. Attackers can bypass login & reset passwords. Isolate devices now.
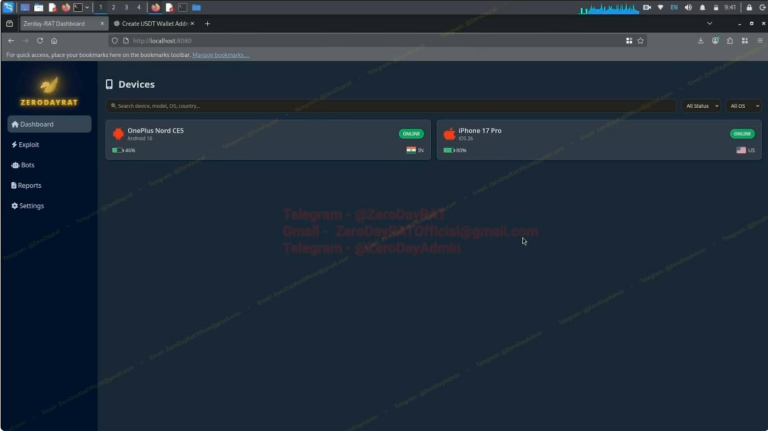
ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.
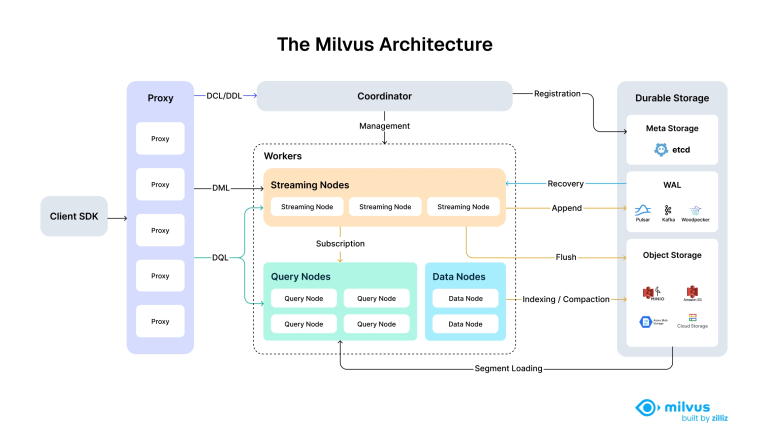
Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

While all strategies are interconnected, sales enablement and data-driven decision-making are among the most critical. Teams that combine strong enablement with actionable insights consistently outperform competitors.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.