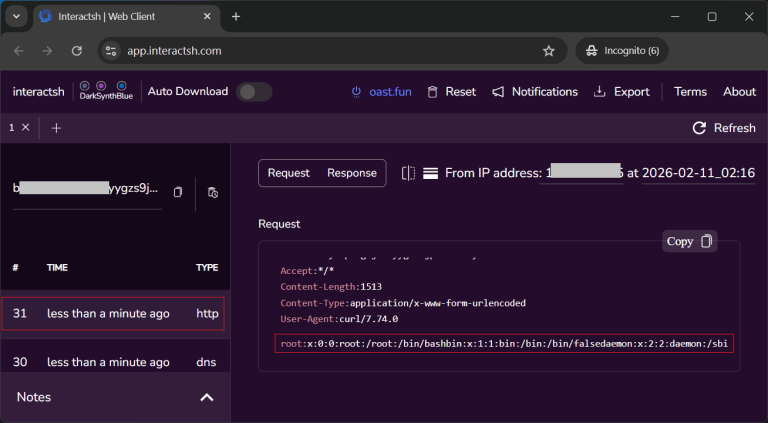
 Do Son
Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Google patches critical zero-day CVE-2026-2441. Attackers are exploiting this CSS use-after-free flaw in the wild. Update to Chrome 145 immediately.

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.

Storm-2603 exploits SmarterMail vulnerability CVE-2026-23760 to deploy Warlock ransomware. Upgrade to Build 9511 immediately to prevent system compromise.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.
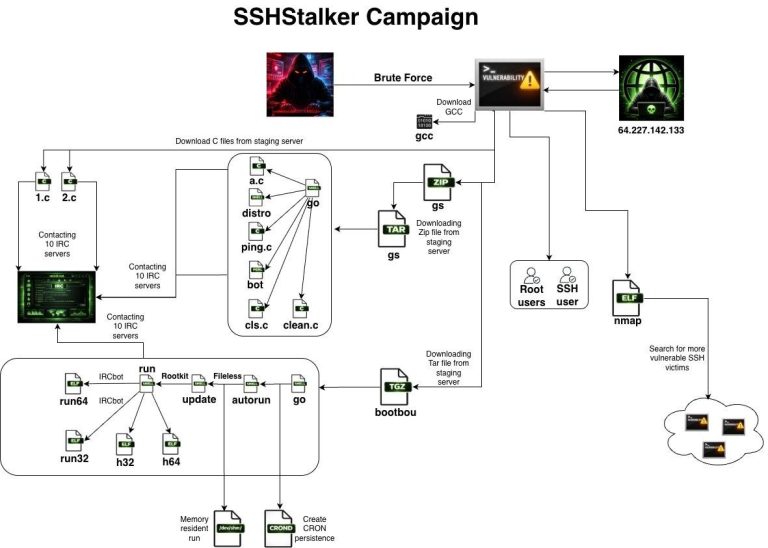
New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.
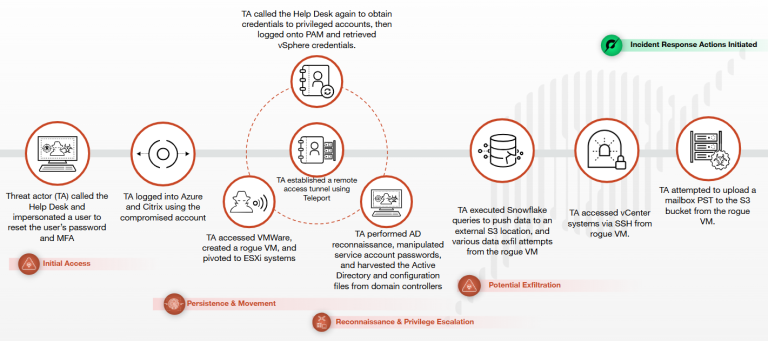
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Siri’s long-awaited AI overhaul is delayed again. Discover why Apple is postponing the "Gemini-powered" assistant until iOS 26.5 or later.

Google’s 2026 "Agent Commerce" shift uses the Universal Commerce Protocol to let AI agents buy products for you instantly. The search-to-sale gap is closing.

Anthropic just unlocked Sonnet 4.5, File Creation, and Connectors for all Claude Free users. No ads, no paywall—is this the end of ChatGPT's dominance?

MongoDB patches high-severity flaw CVE-2026-25611. Unauthenticated attackers can crash servers via memory exhaustion. Update to v8.2.4 or v8.0.18 now.

Ivanti patches critical EPM flaw CVE-2026-1603 allowing remote unauthenticated attackers to steal credentials. Update to 2024 SU5 immediately.

Public PoC released for Windows Storage flaw CVE-2026-21508. Attackers can gain SYSTEM privileges via WUDFHost.exe. Patch Windows 11 immediately.

Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

Google Chrome 145 patches 11 security flaws, including 3 high-severity bugs in CSS & Codecs. Update to v145.0.7632.45 now to stay safe.
Urgent: Apple patches zero-day CVE-2026-20700 in dyld. The flaw is being exploited in the wild against specific targets. Update to iOS 26.3 now.

Python cryptography flaw CVE-2026-26007 (CVSS 8.2) allows private key recovery via ECC Subgroup Attack. Update to v46.0.5 now.

Darktrace detects AI-generated "vibecoding" malware exploiting React2Shell (CVE-2025-55182). Attackers use AI to deploy XMRig miners on Docker.

Critical EverShop flaw CVE-2026-25993 (CVSS 9.3) allows Second-Order SQL Injection via URL keys. Update to v2.1.1 to prevent store takeover.