Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Data Mercantilism Era: Amazon and Microsoft Battle for the Future of Licensed AI Content AI content licensing marketplace AWS Nova 2 Nova Act AWS Agentic AI TwelveLabs Marengo 3.0
  • Technology

The Data Mercantilism Era: Amazon and Microsoft Battle for the Future of Licensed AI Content

Do Son February 11, 2026 0

Amazon and Microsoft launch competing AI content marketplaces, turning the "Wild West" of data scraping into a multi-billion dollar licensing frontier.

Sideloading Sidestepped: The UK’s “Light-Touch” Gamble on the Apple-Google Duopoly Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Technology

Sideloading Sidestepped: The UK’s “Light-Touch” Gamble on the Apple-Google Duopoly

Do Son February 11, 2026 0

The UK's CMA breaks from the EU, opting for "voluntary commitments" over forced sideloading for Apple and Google. Is this pragmatism or a lack of teeth?

Beyond the Screen: Samsung’s Galaxy S26 Ultra Debuts “Magic Flex” Privacy and Agentic AI Galaxy S26 AI Camera Galaxy Unpacked 2026
  • Android
  • Technology

Beyond the Screen: Samsung’s Galaxy S26 Ultra Debuts “Magic Flex” Privacy and Agentic AI

Do Son February 11, 2026 0

Galaxy Unpacked 2026 is officially set for Feb 25! Discover the Galaxy S26 Ultra's "Magic Flex" privacy screen and the autonomous power of Agentic AI.

Digital Firewall: Google’s New AI Arsenal Targets Deepfake and SSN Leaks Google search removal tools
  • Technology

Digital Firewall: Google’s New AI Arsenal Targets Deepfake and SSN Leaks

Do Son February 11, 2026 0

Google’s 2026 privacy update empowers victims to auto-filter deepfakes and monitor SSNs in real-time. Take control of your digital identity today.

Billions at Risk: Critical Windows Notepad Flaw Allows Remote Code Execution Windows Notepad Vulnerability CVE-2026-20841 Notepad Markdown Tables Copilot Streaming
  • Vulnerability Report

Billions at Risk: Critical Windows Notepad Flaw Allows Remote Code Execution

Do Son February 11, 2026 0

Microsoft patches critical Windows Notepad flaw CVE-2026-20841 (CVSS 8.8). Malicious Markdown links allow Remote Code Execution. Update now.

Backup Breach: Critical Acronis Flaws (CVSS 10.0) Allow Data Manipulation shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability

Backup Breach: Critical Acronis Flaws (CVSS 10.0) Allow Data Manipulation

Do Son February 11, 2026 0

Acronis fixes 3 critical flaws (CVSS 10.0) in Cyber Protect. Attackers can manipulate backups without auth. Update to v16 Update 4 immediately.

Patch Panic: Microsoft Fixes 6 Active Zero-Days in Feb 2026 Update Microsoft Patch Tuesday May 2026 Netlogon RCE CVE-2026-41089 SharePoint Exploit Patch Tuesday Windows DWM Zero-Day CVE-2026-21519 CVE-2024-49039 Microsoft Patch Tuesday March 2025
  • Vulnerability Report

Patch Panic: Microsoft Fixes 6 Active Zero-Days in Feb 2026 Update

Do Son February 11, 2026 0

Microsoft Feb 2026 update fixes 61 flaws, including critical DWM zero-day CVE-2026-21519 exploited in the wild. Patch now to stop SYSTEM takeover.

Null Byte Nightmare: Critical WPvivid Backup Flaw (CVSS 9.8) Exposes 800K WordPress Sites WPvivid Backup Vulnerability CVE-2026-1357
  • Vulnerability Report

Null Byte Nightmare: Critical WPvivid Backup Flaw (CVSS 9.8) Exposes 800K WordPress Sites

Do Son February 11, 2026 0

Critical WPvivid Backup flaw CVE-2026-1357 (CVSS 9.8) allows unauthenticated file upload via null byte key. Update to v0.9.124 to prevent RCE.

GitLab Patch Alert: High-Severity Web IDE Flaw Exposes Private Repos GitLab Security Update CVE-2025-7659 CVE-2024-5655 GitLab Vulnerabilities, XSS & Data Exposure
  • Vulnerability Report

GitLab Patch Alert: High-Severity Web IDE Flaw Exposes Private Repos

Do Son February 11, 2026 0

GitLab fixes critical CVE-2025-7659 (CVSS 8.0). Unauthenticated attackers can steal tokens via Web IDE. Update to v18.8.4 now to secure your code.

Under Siege: GTIG Report Exposes North Korean Spies & Russian Drone Hacks in Defense Sector GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security

Under Siege: GTIG Report Exposes North Korean Spies & Russian Drone Hacks in Defense Sector

Do Son February 11, 2026 0

GTIG report: Defense Industrial Base faces "constant siege" from Russian drone hackers & North Korean IT insiders. Learn the new threats.

“Fiber” Optic Failure: Predictable UUIDs Expose Go Web Framework to Hijacking CVE-2024-25124 Fiber Framework Vulnerability CVE-2025-66630
  • Vulnerability Report

“Fiber” Optic Failure: Predictable UUIDs Expose Go Web Framework to Hijacking

Do Son February 11, 2026 0

Critical Fiber framework vulnerability CVE-2025-66630 (CVSS 9.2) causes silent UUID failures, leading to session hijacking. Update to v2.52.11 now.

Sleeping with the Enemy: Dormant Backdoors Found in Ivanti EPMM GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability Report

Sleeping with the Enemy: Dormant Backdoors Found in Ivanti EPMM

Do Son February 11, 2026 0

New campaign targets Ivanti EPMM with dormant in-memory backdoors. Attackers use CVE-2026-1281 to plant "sleeper" agents. Restart servers immediately.

Unmasking the Proxy: Silent Push “Traffic Origin” Exposes True Actor Locations Residential Proxy Detection
  • Cybercriminals

Unmasking the Proxy: Silent Push “Traffic Origin” Exposes True Actor Locations

Do Son February 11, 2026 0

Silent Push's Traffic Origin technology strips away VPN masks to reveal the true location of threat actors. Detect North Korean & Russian proxies now.

Sandbox Breakout: Critical SandboxJS Flaw (CVE-2026-25881) Allows Host Takeover shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Sandbox Breakout: Critical SandboxJS Flaw (CVE-2026-25881) Allows Host Takeover

Do Son February 11, 2026 0

Critical SandboxJS flaw CVE-2026-25881 allows sandbox escape via prototype pollution. Malicious code can modify host logic & execute RCE. Update to v0.8.31.
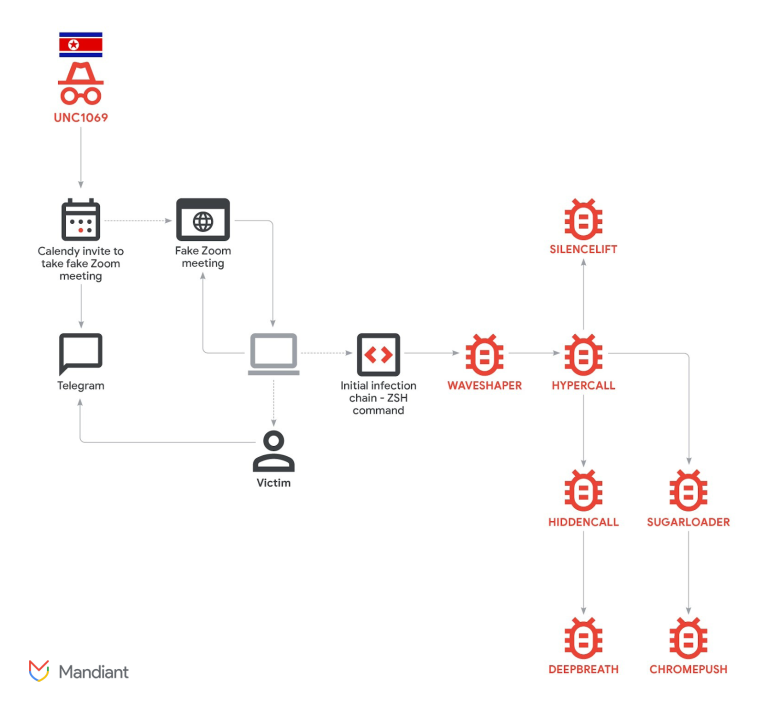
Fake CEO, Real Hack: North Korea Uses AI Deepfakes to Steal Crypto UNC1069 Deepfake Attack Cryptocurrency Malware
  • Cyber Security
  • Malware

Fake CEO, Real Hack: North Korea Uses AI Deepfakes to Steal Crypto

Do Son February 11, 2026 0

North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

Factory Flaw: Critical WAGO Switch Vulnerabilities (CVSS 9.8) Allow Remote Takeover shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Factory Flaw: Critical WAGO Switch Vulnerabilities (CVSS 9.8) Allow Remote Takeover

Do Son February 11, 2026 0

Critical flaws in WAGO 852 switches (CVSS 9.8) allow remote takeover via hardcoded keys & buffer overflows. Update firmware 2.64 immediately.

Hiding in the Cloud: GuLoader Malware Evolves to Evade Detection GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Malware

Hiding in the Cloud: GuLoader Malware Evolves to Evade Detection

Do Son February 11, 2026 0

Zscaler analyzes GuLoader's evolution. The malware uses Google Drive, polymorphic code, and exception-based obfuscation to evade detection.

CVE-2026-23906: Authentication Bypass Flaw Hits Apache Druid Analytics Clusters Apache Druid Vulnerability CVE-2026-23906
  • Vulnerability Report

CVE-2026-23906: Authentication Bypass Flaw Hits Apache Druid Analytics Clusters

Do Son February 11, 2026 0

Critical Apache Druid flaw (CVE-2026-23906) allows login with no password via LDAP anonymous binds. Update to v36.0.0 or disable anonymous binds now.
5 Benefits of Using Automation to Stay in Touch With Customers tech-customer
  • Technology

5 Benefits of Using Automation to Stay in Touch With Customers

Do Son February 11, 2026 0
Customers have the power to make or break any business. That’s why most business owners, regardless of...
Read More Read more about 5 Benefits of Using Automation to Stay in Touch With Customers
Signed” Sealed, Delivered: Cybercriminals Abuse PayPal and Apple to Bypass Email Security DKIM Replay Attack Invoice Phishing
  • Cybercriminals

Signed” Sealed, Delivered: Cybercriminals Abuse PayPal and Apple to Bypass Email Security

Do Son February 11, 2026 0

Hackers abuse PayPal & Apple to send "perfect" phishing emails. Learn how DKIM Replay attacks bypass security filters & DMARC checks.

Handshake Halt: GnuTLS 3.8.12 Fixes TLS 1.3 Crash & CPU Exhaustion GnuTLS Security Update DTLS Heap Overwrite GnuTLS Vulnerability CVE-2026-1584
  • Vulnerability Report

Handshake Halt: GnuTLS 3.8.12 Fixes TLS 1.3 Crash & CPU Exhaustion

Do Son February 11, 2026 0

GnuTLS v3.8.12 fixes high-severity DoS flaws (CVE-2026-1584). Malicious TLS 1.3 handshakes can crash servers. Update now to prevent outages.

CVE-2026-24343: Apache HertzBeat Flaw Opens Door to Resource Exhaustion Apache HertzBeat Vulnerability CVE-2026-24343
  • Vulnerability Report

CVE-2026-24343: Apache HertzBeat Flaw Opens Door to Resource Exhaustion

Do Son February 11, 2026 0

Apache HertzBeat flaw CVE-2026-24343 allows DoS via XPath injection. Vulnerable versions 1.7.1-1.7.9. Update to v1.8.0 immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.