 Do Son
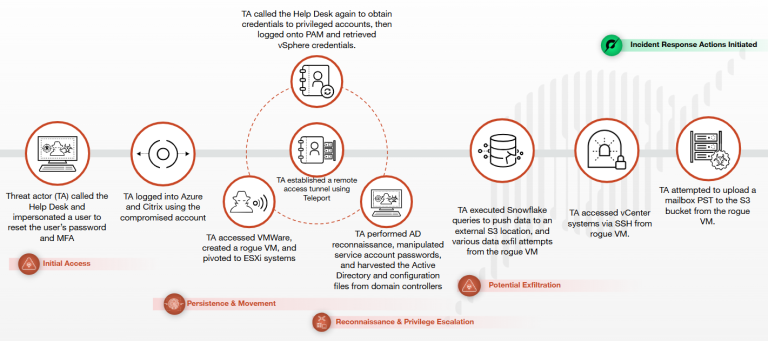
Unit 42 reveals Muddled Libra (Scattered Spider) uses rogue VMs in vSphere to persist. Learn how they bypass defenses without malware. Read more.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Siri’s long-awaited AI overhaul is delayed again. Discover why Apple is postponing the "Gemini-powered" assistant until iOS 26.5 or later.

Google’s 2026 "Agent Commerce" shift uses the Universal Commerce Protocol to let AI agents buy products for you instantly. The search-to-sale gap is closing.

Anthropic just unlocked Sonnet 4.5, File Creation, and Connectors for all Claude Free users. No ads, no paywall—is this the end of ChatGPT's dominance?

MongoDB patches high-severity flaw CVE-2026-25611. Unauthenticated attackers can crash servers via memory exhaustion. Update to v8.2.4 or v8.0.18 now.

Ivanti patches critical EPM flaw CVE-2026-1603 allowing remote unauthenticated attackers to steal credentials. Update to 2024 SU5 immediately.

Public PoC released for Windows Storage flaw CVE-2026-21508. Attackers can gain SYSTEM privileges via WUDFHost.exe. Patch Windows 11 immediately.

Critical PAN-OS flaw CVE-2026-0229 allows unauthenticated attackers to trigger reboot loops & maintenance mode via malicious packets. Patch immediately.

Google Chrome 145 patches 11 security flaws, including 3 high-severity bugs in CSS & Codecs. Update to v145.0.7632.45 now to stay safe.
Urgent: Apple patches zero-day CVE-2026-20700 in dyld. The flaw is being exploited in the wild against specific targets. Update to iOS 26.3 now.

Python cryptography flaw CVE-2026-26007 (CVSS 8.2) allows private key recovery via ECC Subgroup Attack. Update to v46.0.5 now.

Darktrace detects AI-generated "vibecoding" malware exploiting React2Shell (CVE-2025-55182). Attackers use AI to deploy XMRig miners on Docker.

Critical EverShop flaw CVE-2026-25993 (CVSS 9.3) allows Second-Order SQL Injection via URL keys. Update to v2.1.1 to prevent store takeover.

Cisco Talos reveals VoidLink, a modular Linux malware framework by UAT-9921. Features "compile-on-demand" tools to target IoT & cloud infrastructure.

Phishing emails use malicious Excel files to deploy XWorm RAT. The fileless attack exploits CVE-2018-0802 to steal data & control systems.

HPE Aruba patches critical Private 5G Core flaws. CVE-2026-23595 allows unauthenticated admin creation. Update to v1.25.1.0 now to prevent takeover.

New LTX Stealer malware abuses Node.js & Inno Setup to bypass antivirus. This $10 tool steals browser passwords & crypto wallets. Stay alert.

 cybernewswire

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.

Microsoft is rotating UEFI Secure Boot certificates before they expire in June 2026. Ensure your PC stays secure by following this massive coordination effort.

Alphabet triggers a $32 billion debt offensive to fund a record $185 billion AI CapEx. Is the "Century Bond" a vote of confidence or a sign of an AI bubble?