Skip to content
November 7, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The Silent Hijack: BADIIS Malware Turns 1,800+ Servers into Illicit Websites BADIIS Malware IIS SEO Poisoning
  • Malware

The Silent Hijack: BADIIS Malware Turns 1,800+ Servers into Illicit Websites

Do Son February 16, 2026 0

Elastic Security Labs uncovers BADIIS malware compromising 1,800+ IIS servers. Attackers use SEO poisoning to redirect users to illicit gambling sites.
“Carding” as a Service: How Stolen Credit Cards Became a Structured Economy Carding-as-a-Service Underground Credit Card Market
  • Cybercriminals

“Carding” as a Service: How Stolen Credit Cards Became a Structured Economy

Do Son February 16, 2026 0

Rapid7 reveals how "Carding-as-a-Service" mimics legitimate e-commerce. Fraud markets now offer refunds & "Fullz" data. Learn about the new threat.
Fake AI, Real Spies: 260,000 Users Hit by Malicious Browser Extensions Malicious AI Extensions Browser Surveillance
  • Malware

Fake AI, Real Spies: 260,000 Users Hit by Malicious Browser Extensions

Do Son February 16, 2026 0

LayerX exposes 30+ malicious AI extensions spying on 260,000 users. These "privileged proxies" steal Gmail data & page content. Uninstall now.

“Matryoshka” Malware: New macOS Attack Hides Inside “Russian Dolls” of Obfuscation OSX/Amos Stealer Electron ASAR Trojan MioLab Malware macOS Security MacSync Stealer macOS Malware ambar-src npm Malware Supply Chain Typosquatting Matryoshka Mac Malware ClickFix Crypto Scam Infostealer Evolution macOS Malware Predator Spyware Intellexa Anti-Analysis XCSSET macOS Malware, Xcode Supply Chain
  • Malware

“Matryoshka” Malware: New macOS Attack Hides Inside “Russian Dolls” of Obfuscation

Do Son February 16, 2026 0

New "Matryoshka" Mac malware uses "ClickFix" scams to steal crypto. Intego warns of fake error fixes patching Ledger & Trezor apps. Stay alert.

One Code to Lock Them All: LockBit 5.0 Unifies Attacks on Windows, Linux, and ESXi LockBit LockBit 5.0 Resurgence, ETW Blinding Ransomware
  • Malware

One Code to Lock Them All: LockBit 5.0 Unifies Attacks on Windows, Linux, and ESXi

Do Son February 16, 2026 0

LockBit 5.0 launches with a unified codebase targeting Windows, Linux, and ESXi. Acronis reveals identical encryption and ties to SmokeLoader.

OysterLoader: Multi-Stage Loader Evolves to Evade Detection and Deliver Ransomware INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Malware

OysterLoader: Multi-Stage Loader Evolves to Evade Detection and Deliver Ransomware

Do Son February 16, 2026 0

OysterLoader malware uses custom LZMA & steganography to evade tools. Linked to Rhysida ransomware, it hides in fake IT installers.
“Distillation” Theft: Attackers Target AI Models in New Wave of Intellectual Property Heists Model Extraction Attacks AI API Theft
  • Cybercriminals

“Distillation” Theft: Attackers Target AI Models in New Wave of Intellectual Property Heists

Do Son February 16, 2026 0

Google Threat Intelligence reports a surge in "model extraction" attacks. Private entities are cloning AI models & stealing API keys. Stay alert.

JPCERT/CC Warns of Active Exploits Targeting Critical FileZen Command Injection Flaw GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability Report

JPCERT/CC Warns of Active Exploits Targeting Critical FileZen Command Injection Flaw

Do Son February 16, 2026 0

Critical FileZen flaw CVE-2026-25108 is under active attack. Antivirus feature allows command injection. Update to V5.0.11 immediately to secure data.

Critical ZLAN5143D Flaws (CVSS 9.8) Allow Total Takeover, No Patch Available shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Critical ZLAN5143D Flaws (CVSS 9.8) Allow Total Takeover, No Patch Available

Do Son February 16, 2026 0

CISA warns of critical ZLAN5143D flaws CVE-2026-25084 & CVE-2026-24789. Attackers can bypass login & reset passwords. Isolate devices now.
Surveillance for Sale: ZeroDayRAT Turns Phones into Spies via Telegram ZeroDayRAT Mobile Spyware
  • Malware

Surveillance for Sale: ZeroDayRAT Turns Phones into Spies via Telegram

Do Son February 16, 2026 0

ZeroDayRAT mobile spyware is sold on Telegram. It offers full remote control of Android & iOS devices, including camera streaming & crypto theft.

HAProxy Patches High-Severity QUIC Flaws That Can Kill the Load Balancer HAProxy QUIC Vulnerability CVE-2026-26081 CVE-2024-45506 - HAProxy vulnerability
  • Vulnerability

HAProxy Patches High-Severity QUIC Flaws That Can Kill the Load Balancer

Do Son February 16, 2026 0

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.
AI Data at Risk: Critical Milvus Flaw (CVSS 9.8) Exposes Database via Port 9091 Milvus Vulnerability Vector Database Security
  • Vulnerability Report

AI Data at Risk: Critical Milvus Flaw (CVSS 9.8) Exposes Database via Port 9091

Do Son February 16, 2026 0

Critical Milvus flaw (CVSS 9.8) exposes port 9091. Unauthenticated attackers can steal secrets & delete data. Update to v2.5.27 or v2.6.10 immediately.

Top 8 B2B Sales Strategies in 2026 tech
  • Technique

Top 8 B2B Sales Strategies in 2026

Do Son February 16, 2026 0

While all strategies are interconnected, sales enablement and data-driven decision-making are among the most critical. Teams that combine strong enablement with actionable insights consistently outperform competitors.

Trusted Tool Weaponized: Lotus Blossom Hijacks Notepad++ Updates GemStuffer RubyGems Campaign RubyGems Data Exfiltration TanStack npm Compromise Supply Chain Attack DNS Hijacking APT28 (Fancy Bear) OpenVSX Supply Chain Attack Checkmarx Plugin Breach Stryker Cyberattack CISA Alert Trans-Regional Cyber Conflict Operation Epic Fury Cyber Operation MacroMaze APT28 Cyber Espionage Notepad++ Supply Chain Attack Lotus Blossom Group Defense Industrial Base Threats GTIG Report APT28 Operation Neusploit CVE-2026-21509 Bookworm Malware
  • Cyber Security
  • Malware

Trusted Tool Weaponized: Lotus Blossom Hijacks Notepad++ Updates

Do Son February 16, 2026 0

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.
Exploited in the Wild: Critical BeyondTrust Flaw (CVSS 9.9) Opens Door to Network Takeover BeyondTrust Vulnerability CVE-2026-1731
  • Vulnerability Report

Exploited in the Wild: Critical BeyondTrust Flaw (CVSS 9.9) Opens Door to Network Takeover

Do Son February 15, 2026 0

Arctic Wolf warns of CVE-2026-1731, a critical BeyondTrust flaw exploited in the wild. Attackers use it to deploy backdoors. Patch self-hosted instances now.

Critical Alert: Chrome Zero-Day (CVE-2026-2441) Exploited in the Wild Chrome security update exploit in the wild Chrome Zero-Day CVE-2026-3909 Chrome Zero-Day PoC CVE-2026-2441 Chrome Zero-Day CVE-2026-2441 Chrome Zero-Day, Active Exploitation CVE-2025-10585 Chrome vulnerability, zero-day exploit CVE-2025-6558 Chrome Zero-Day, V8 Vulnerability Chrome Zero-Day, Security Update
  • Vulnerability Report

Critical Alert: Chrome Zero-Day (CVE-2026-2441) Exploited in the Wild

Do Son February 15, 2026 0

Google patches critical zero-day CVE-2026-2441. Attackers are exploiting this CSS use-after-free flaw in the wild. Update to Chrome 145 immediately.

Inside Job: Abandoned Outlook Add-in “AgreeTo” Steals 4,000 Credentials Outlook Add-in Phishing AgreeTo Malicious Add-in
  • Malware

Inside Job: Abandoned Outlook Add-in “AgreeTo” Steals 4,000 Credentials

Do Son February 13, 2026 0

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.

Triple Threat Patched: Zimbra 10.1.16 Fixes XSS, XXE & LDAP Injection Zimbra 10.1.16 Zimbra Security Update Zimbra LFI, CVE-2025-68645 CVE-2025-25065 & CVE-2025-25064
  • Vulnerability Report

Triple Threat Patched: Zimbra 10.1.16 Fixes XSS, XXE & LDAP Injection

Do Son February 13, 2026 0

Zimbra 10.1.16 patches critical XSS, XXE, and LDAP injection flaws. Update immediately to secure your email collaboration suite and restore PDF previews.

Email Under Siege: Storm-2603 Exploits SmarterMail to Deploy Warlock Ransomware Cisco SD-WAN Vulnerability CVE-2026-20133 FortiGate Compromise Ivanti EPMM Zero-Day CVE-2026-1281 SmarterMail Vulnerability Storm-2603 WatchGuard Zero-Day, IKEv2 Out-of-Bounds Write Cisco Zero-Day, UAT-9686 Chinese APT FortiWeb RCE Exploitation CVE-2025-58034 VMware Zero-Day, Privilege Escalation Sitecore, remote code execution CVE-2025-53690 Windows CLFS, Privilege Escalation CVE-2024-47575 & CVE-2024-11120 CVE-2025-24983 vulnerability
  • Vulnerability Report

Email Under Siege: Storm-2603 Exploits SmarterMail to Deploy Warlock Ransomware

Do Son February 13, 2026 0

Storm-2603 exploits SmarterMail vulnerability CVE-2026-23760 to deploy Warlock ransomware. Upgrade to Build 9511 immediately to prevent system compromise.

Dream Job or Nightmare? Lazarus Group Hunts Crypto Devs with “Graphalgo” Malware TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Cyber Security
  • Malware

Dream Job or Nightmare? Lazarus Group Hunts Crypto Devs with “Graphalgo” Malware

Do Son February 13, 2026 0

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.

The Human Hack: LummaStealer Returns with Deceptive “ClickFix” Attacks Seedworm Espionage Campaign 2026 ChromElevator Stealer DLL Sideloading SIM Swapping Crypto Theft Lazarus Comebacker, Aerospace Espionage Delete PlugX Malware
  • Malware

The Human Hack: LummaStealer Returns with Deceptive “ClickFix” Attacks

Do Son February 13, 2026 0

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.
Back to the Future: SSHStalker Botnet Revives 2009 Tactics to Hijack Linux Servers SSHStalker Botnet Linux IRC Malware
  • Malware

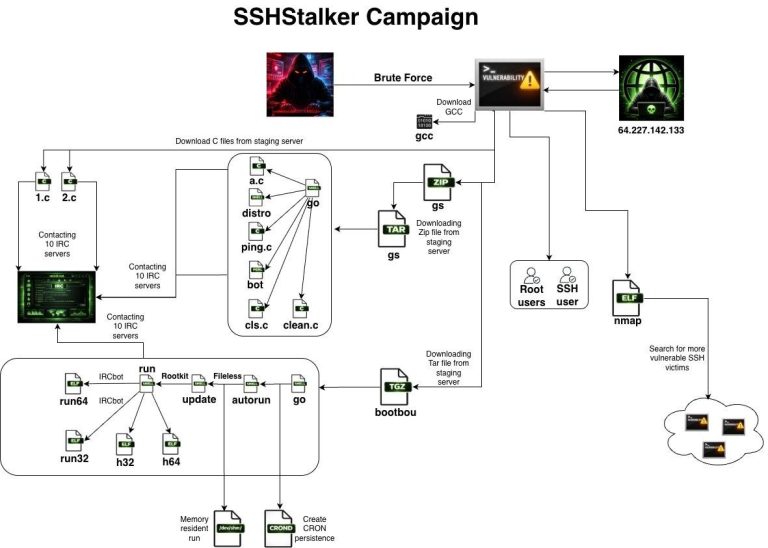
Back to the Future: SSHStalker Botnet Revives 2009 Tactics to Hijack Linux Servers

Do Son February 13, 2026 0

New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-117691CVSS 9.1
    A flaw was found in the SAML HTTP-Redirect binding implementation of Keycloak. The issue occurs because the server...
    📅 Updated: Nov 7, 2026
  • CVE-2026-120984CVSS 9.1
    A flaw was found in the Keycloak server's client management component. When a client is created or imported...
    📅 Updated: Nov 7, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 7, 2026
  • CVE-2026-122041CVSS 9.1
    The Checkout Field Editor for WooCommerce (Pro) plugin for WordPress is vulnerable to unauthorized deletion of arbitrary attachments...
    📅 Updated: Nov 7, 2026
  • CVE-2026-119075CVSS 9.8
    The Registration Form for WooCommerce plugin for WordPress is vulnerable to privilege escalation due to a missing allow-list...
    📅 Updated: Nov 7, 2026
  • CVE-2026-118066CVSS 9.1
    The Appointment Booking Plugin – LatePoint | Calendar & Scheduling for WordPress plugin for WordPress is vulnerable to...
    📅 Updated: Nov 7, 2026
  • CVE-2026-104014CVSS 9.8
    The Naimur Email OTP Verification for WooCommerce plugin for WordPress is vulnerable to authentication bypass in versions up...
    📅 Updated: Nov 7, 2026
  • CVE-2023-3961CVSS 9.1
    A path traversal vulnerability was identified in Samba when processing client pipe names connecting to Unix domain sockets...
    📅 Updated: Nov 7, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.