Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
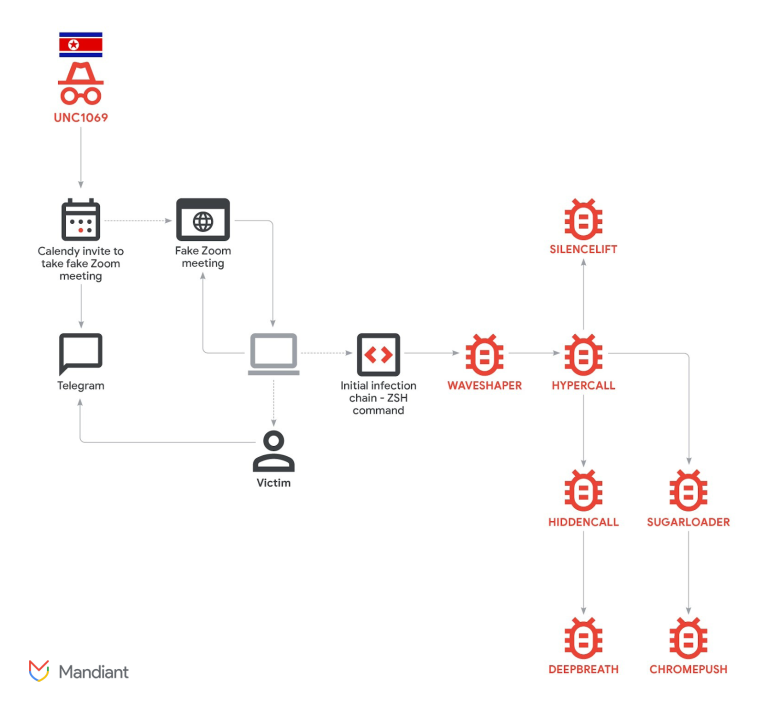
Fake CEO, Real Hack: North Korea Uses AI Deepfakes to Steal Crypto UNC1069 Deepfake Attack Cryptocurrency Malware
  • Cyber Security
  • Malware

Fake CEO, Real Hack: North Korea Uses AI Deepfakes to Steal Crypto

Do Son February 11, 2026 0

North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

Factory Flaw: Critical WAGO Switch Vulnerabilities (CVSS 9.8) Allow Remote Takeover shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Factory Flaw: Critical WAGO Switch Vulnerabilities (CVSS 9.8) Allow Remote Takeover

Do Son February 11, 2026 0

Critical flaws in WAGO 852 switches (CVSS 9.8) allow remote takeover via hardcoded keys & buffer overflows. Update firmware 2.64 immediately.

Hiding in the Cloud: GuLoader Malware Evolves to Evade Detection GuLoader Malware CloudEye Obfuscation npm, malware Ethereum, npm supply chain OAST techniques StilachiRAT macOS Malware PasivRobber
  • Malware

Hiding in the Cloud: GuLoader Malware Evolves to Evade Detection

Do Son February 11, 2026 0

Zscaler analyzes GuLoader's evolution. The malware uses Google Drive, polymorphic code, and exception-based obfuscation to evade detection.

CVE-2026-23906: Authentication Bypass Flaw Hits Apache Druid Analytics Clusters Apache Druid Vulnerability CVE-2026-23906
  • Vulnerability Report

CVE-2026-23906: Authentication Bypass Flaw Hits Apache Druid Analytics Clusters

Do Son February 11, 2026 0

Critical Apache Druid flaw (CVE-2026-23906) allows login with no password via LDAP anonymous binds. Update to v36.0.0 or disable anonymous binds now.
5 Benefits of Using Automation to Stay in Touch With Customers tech-customer
  • Technology

5 Benefits of Using Automation to Stay in Touch With Customers

Do Son February 11, 2026 0
Customers have the power to make or break any business. That’s why most business owners, regardless of...
Read More Read more about 5 Benefits of Using Automation to Stay in Touch With Customers
Signed” Sealed, Delivered: Cybercriminals Abuse PayPal and Apple to Bypass Email Security DKIM Replay Attack Invoice Phishing
  • Cybercriminals

Signed” Sealed, Delivered: Cybercriminals Abuse PayPal and Apple to Bypass Email Security

Do Son February 11, 2026 0

Hackers abuse PayPal & Apple to send "perfect" phishing emails. Learn how DKIM Replay attacks bypass security filters & DMARC checks.

Handshake Halt: GnuTLS 3.8.12 Fixes TLS 1.3 Crash & CPU Exhaustion GnuTLS Security Update DTLS Heap Overwrite GnuTLS Vulnerability CVE-2026-1584
  • Vulnerability Report

Handshake Halt: GnuTLS 3.8.12 Fixes TLS 1.3 Crash & CPU Exhaustion

Do Son February 11, 2026 0

GnuTLS v3.8.12 fixes high-severity DoS flaws (CVE-2026-1584). Malicious TLS 1.3 handshakes can crash servers. Update now to prevent outages.

CVE-2026-24343: Apache HertzBeat Flaw Opens Door to Resource Exhaustion Apache HertzBeat Vulnerability CVE-2026-24343
  • Vulnerability Report

CVE-2026-24343: Apache HertzBeat Flaw Opens Door to Resource Exhaustion

Do Son February 11, 2026 0

Apache HertzBeat flaw CVE-2026-24343 allows DoS via XPath injection. Vulnerable versions 1.7.1-1.7.9. Update to v1.8.0 immediately.

Smile for the Settings: Windows 11 Update Adds Native Camera Controls and Tired New Emojis Windows 11 Build 26300.7760
  • Windows

Smile for the Settings: Windows 11 Update Adds Native Camera Controls and Tired New Emojis

Do Son February 10, 2026 0

Windows 11 builds 26300.7760 & 26200.7755 bring native camera pan/tilt controls and Emoji 16.0. Fix your "bags under eyes" with the new tired face emoji!

The End of the Ad-Free Era: OpenAI Launches ChatGPT “Go” and Sponsored Responses to Fuel GPT-5.3 ChatGPT Go ads pilot
  • Technology

The End of the Ad-Free Era: OpenAI Launches ChatGPT “Go” and Sponsored Responses to Fuel GPT-5.3

Do Son February 10, 2026 0

OpenAI ends the ad-free era with a pilot for the free tier and $8 ChatGPT "Go" plan. Discover how the new GPT-5.3 model aims to soften the blow for users.

The AI Hectocorn: Anthropic Hits $350B Valuation as Microsoft and NVIDIA Hedge Their Bets Anthropic valuation $350 billion AI agent, prompt injection
  • Technology

The AI Hectocorn: Anthropic Hits $350B Valuation as Microsoft and NVIDIA Hedge Their Bets

Do Son February 10, 2026 0

Anthropic secures a $20B round, hitting a $350B valuation. With backing from NVIDIA and Microsoft, the "Claude" creator prepares for a blockbuster Summer 2026 IPO.

Critical SAP Alert: Code Injection (CVSS 9.9) Exposes S/4HANA Databases SAP Security Patches CVE-2026-27685 SAP Security Update CVE-2026-0488 CVE-2024-47578 - CVE-2025-0070 and CVE-2025-0066
  • Vulnerability Report

Critical SAP Alert: Code Injection (CVSS 9.9) Exposes S/4HANA Databases

Do Son February 10, 2026 0

SAP Feb 2026 update fixes critical CVE-2026-0488 (CVSS 9.9). Code injection in CRM & S/4HANA allows full database compromise. Patch immediately.

HTTP Down: High-Severity Axios Flaw (CVSS 7.5) Crashes Node.js Servers Axios proxy vulnerabilities prototype pollution gadget Axios Vulnerability Cloud Hijacking Axios npm supply chain attack Axios Vulnerability Node.js DoS CVE-2025-58754 CVE-2025-27152 Axios Vulnerability, Form-Data Flaw
  • Vulnerability Report

HTTP Down: High-Severity Axios Flaw (CVSS 7.5) Crashes Node.js Servers

Do Son February 10, 2026 0

Axios flaw CVE-2026-25639 (CVSS 7.5) crashes Node.js servers via malicious JSON. Attackers use __proto__ to trigger DoS. Update to v1.13.5 now.

30-Year-Old Bug: High-Severity libpng Flaw (CVSS 8.3) Exposes Millions of Apps libpng Vulnerability CVE-2026-25646 libpng Vulnerability Remote Code Execution (RCE)
  • Vulnerability Report

30-Year-Old Bug: High-Severity libpng Flaw (CVSS 8.3) Exposes Millions of Apps

Do Son February 10, 2026 0

A 30-year-old heap overflow in libpng (CVE-2026-25646) exposes apps to DoS & RCE. The flaw affects all versions since inception. Update to v1.6.55 now.

Sunset for the Father of Blu-ray: Sony Officially Terminates All Blu-ray Recorder Shipments Andariel APT
  • Technology

Sunset for the Father of Blu-ray: Sony Officially Terminates All Blu-ray Recorder Shipments

Do Son February 10, 2026 0

Sony, the "Father of Blu-ray," announces the final end of Blu-ray recorder shipments. Discover why the optical disc pioneer is pulling the plug on hardware.

March Madness: Apple’s M5 Mac Surge and the Surprising $599 “MacBook SE” Debut Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

March Madness: Apple’s M5 Mac Surge and the Surprising $599 “MacBook SE” Debut

Do Son February 10, 2026 0

Apple’s March 2026 event reveals M5 MacBook Pros, a refreshed M5 Air, and a $599 budget MacBook powered by the A18 Pro chip to challenge Chromebooks.

Flagship Power, Budget Price: How Apple’s iPhone 17e Aims to Crush the Mid-Range Market iOS 27 AirDrop speed, AirDrop transfer speed, AirDrop file transfer, AWDL protocol iPhone 17e rumors iPhone Air 2 Roadmap Apple Launch Cadence Shift iPhone Air sales collapse Apple iPhone Fold iPhone Air, thinnest iPhone camera flaw
  • Technology

Flagship Power, Budget Price: How Apple’s iPhone 17e Aims to Crush the Mid-Range Market

Do Son February 10, 2026 0

Apple’s iPhone 17e is coming. With the flagship A19 chip and MagSafe at just $599, it's a "budget" beast designed to dominate China, India, and enterprises.

Triple Threat: Critical Gogs Flaws (CVSS 9.3) Allow RCE & 2FA Bypass Gogs Vulnerability CVE-2025-8110 CVE-2025-64111
  • Vulnerability Report

Triple Threat: Critical Gogs Flaws (CVSS 9.3) Allow RCE & 2FA Bypass

Do Son February 10, 2026 0

Critical Gogs flaws (CVE-2025-64111) allow RCE & 2FA bypass. Attackers can execute commands via .git config. Update to v0.13.4 immediately.

Virtual Invasion: SolarWinds WHD Exploited to Host Hidden QEMU VMs SolarWinds Web Help Desk QEMU Persistence
  • Vulnerability Report

Virtual Invasion: SolarWinds WHD Exploited to Host Hidden QEMU VMs

Do Son February 10, 2026 0

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

Trust Broken: Critical Keylime Flaw (CVSS 9.4) Disables mTLS Authentication Keylime Vulnerability CVE-2026-1709
  • Vulnerability Report

Trust Broken: Critical Keylime Flaw (CVSS 9.4) Disables mTLS Authentication

Do Son February 10, 2026 0

Critical Keylime flaw CVE-2026-1709 (CVSS 9.4) disables mTLS in v7.12.0-7.13.0. Unauthorized clients can access the registrar. Update or firewall now.

Silent Killer: Black Basta Bundles “BYOVD” Driver to Blind Antivirus INC Ransom Pacific Cyber Threats OysterLoader Malware Rhysida Ransomware Black Basta Ransomware BYOVD Technique Velociraptor Abuse, Storm-2603 Ransomware Crypto24, Ransomware Ransomware Payments, UK Legislation ZACROS data breach
  • Malware

Silent Killer: Black Basta Bundles “BYOVD” Driver to Blind Antivirus

Do Son February 10, 2026 0

Black Basta ransomware now embeds a vulnerable NsecSoft driver (BYOVD) to silently kill antivirus processes like Sophos & CrowdStrike.

CVE-2026-25592: Critical Semantic Kernel Flaw (CVSS 10.0) Allows File Overwrite Semantic Kernel Vulnerability CVE-2026-25592
  • Vulnerability Report

CVE-2026-25592: Critical Semantic Kernel Flaw (CVSS 10.0) Allows File Overwrite

Do Son February 10, 2026 0

Microsoft warns of critical flaw CVE-2026-25592 (CVSS 10.0) in Semantic Kernel SDK. AI agents can overwrite system files. Update to v1.70.0 now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.