Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Open VSX Hijacked: “GlassWorm” Malware Poisons VS Code Extensions Open VSX Supply Chain Attack GlassWorm Malware
  • Malware

Open VSX Hijacked: “GlassWorm” Malware Poisons VS Code Extensions

Do Son February 5, 2026 0

GlassWorm malware found in Open VSX extensions. Hackers stole AWS & SSH keys from macOS devs using Solana C2. 22k+ downloads affected. Check your tools.

Industrial Alert: Critical Auth Bypass (CVSS 9.2) Hits Moxa Switches Moxa Linux kernel vulnerabilities Moxa Vulnerability CVE-2024-12297 Moxa OpenSSH Vulnerability CVE-2023-38408 CVE-2023-5961 - CVE-2024-9138 and CVE-2024-9140
  • Vulnerability Report

Industrial Alert: Critical Auth Bypass (CVSS 9.2) Hits Moxa Switches

Do Son February 5, 2026 0

Moxa warns of critical auth bypass (CVE-2024-12297, CVSS 9.2) in industrial switches. Flaw allows brute-force attacks. Patch TN-series devices now.

How Video Wall Controllers Improve Security Operations Centers Google SpaceX cloud deal
  • Technique

How Video Wall Controllers Improve Security Operations Centers

Do Son February 4, 2026 0
The right video wall setup helps control and security centers stay on top of potential crises, even...
Read More Read more about How Video Wall Controllers Improve Security Operations Centers
MomentProof Deploys Patented Digital Asset Protection MP_Logo_17696671914NZYKOZ46v
  • Press Release

MomentProof Deploys Patented Digital Asset Protection

cybernewswire February 4, 2026 0
Washington, DC, 4th February 2026, CyberNewsWire
Read More Read more about MomentProof Deploys Patented Digital Asset Protection
PoC Public & Exploited: Critical SolarWinds Help Desk Flaw Exploited in the Wild State-Sponsored Exploitation CISA KEV Catalog F5 BIG-IP RCE CISA KEV Catalog SolarWinds WHD Exploit CVE-2025-40551 Zimbra XSS Zero-Day CVE-2025-27915 Exploited Windows Security Vulnerabilities
  • Vulnerability

PoC Public & Exploited: Critical SolarWinds Help Desk Flaw Exploited in the Wild

Do Son February 4, 2026 0
The clock is ticking for organizations running SolarWinds Web Help Desk (WHD), as a nightmare scenario unfolds:...
Read More Read more about PoC Public & Exploited: Critical SolarWinds Help Desk Flaw Exploited in the Wild
Unpatchable & Critical: CISA Issues CVSS 10.0 Alert for Synectix Adapters Naxclow IoT vulnerabilities device takeover, CVE-2026-28742, CVE-2026-50101, CVE-2026-42947 CVE-2022-35914 Synectix LAN 232 TRIO CVE-2026-1633
  • Vulnerability Report

Unpatchable & Critical: CISA Issues CVSS 10.0 Alert for Synectix Adapters

Do Son February 4, 2026 0

CISA warns of CVSS 10.0 flaw in Synectix LAN 232 TRIO. With no auth and the vendor gone, these devices are unpatchable. Replace immediately.

One Identity Appoints Gihan Munasinghe as Chief Technology Officer gihan-pr_17700556783jOrji7CWo
  • Press Release

One Identity Appoints Gihan Munasinghe as Chief Technology Officer

cybernewswire February 4, 2026 0
Alisa Viejo, United States, 4th February 2026, CyberNewsWire
Read More Read more about One Identity Appoints Gihan Munasinghe as Chief Technology Officer
Native Sysmon Arrives in the Latest Windows 11 Insider Build 26300 Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Native Sysmon Arrives in the Latest Windows 11 Insider Build 26300

Do Son February 4, 2026 0

Microsoft integrates native Sysmon into Windows 11 Build 26300.7733 (KB5074178). Track process creation and network links with this built-in forensic "dashcam."

Breaking the AI Silo: How Google’s New “Import AI Chats” Feature Ends Context Lock-In Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

Breaking the AI Silo: How Google’s New “Import AI Chats” Feature Ends Context Lock-In

Do Son February 4, 2026 0

Google Gemini is testing an "Import AI Chats" tool to let users migrate histories from ChatGPT and Claude. Say goodbye to starting over with every new AI.

The Vanishing Taskbar: Windows 11’s Optional KB5074105 Update Rescues Users from “Explorer” Hell Windows 11 25H2 mandatory update Windows 11 KB5074105 fix Windows 11 Performance, Misleading Claim Windows 11 Kerberos
  • Windows

The Vanishing Taskbar: Windows 11’s Optional KB5074105 Update Rescues Users from “Explorer” Hell

Do Son February 4, 2026 0

Microsoft’s KB5074105 update fixes the disappearing taskbar and random icon shifts in Windows 11. Learn why this optional patch is a must for 24H2/25H2 users.

Silent Intrusion: “Metro4Shell” Exploited in the Wild Since December Metro4Shell CVE-2025-11953
  • Vulnerability Report

Silent Intrusion: “Metro4Shell” Exploited in the Wild Since December

Do Son February 4, 2026 0

VulnCheck reveals CVE-2025-11953 (Metro4Shell) was exploited in the wild since Dec 2025. Attackers target Windows & Linux dev servers. Patch now.

Urgent Django Update: Patches 3 Critical SQL Injections & DoS Risks Django Security Update CVE-2026-25673 Django Security Update SQL Injection Vulnerability Django SQL Injection, PostgreSQL Flaw CVE-2022-34265 PoC Django, SQL injection
  • Vulnerability Report

Urgent Django Update: Patches 3 Critical SQL Injections & DoS Risks

Do Son February 4, 2026 0

Django patches 3 critical SQL injection flaws & DoS risks in versions 6.0.2, 5.2.11, & 4.2.28. Update immediately to secure your database.

React Under Siege: Two IPs Drive 56% of Critical CVE-2025-55182 Attacks Weaver E-cology RCE CVE-2026-22679 CVE-2026-20127 Cisco SD-WAN Exploitation AI-Driven Cyberattack ARXON Malware React Server Components Vulnerability CVE-2025-55182 FortiWeb Auth Bypass, Unauthenticated Admin Takeover RayInitiator Bootkit, LINE VIPER CVE-2025-59689 Department of the Treasury cybersecurity - CVE-2025-0108 PoC CVE-2025-31103 Dior Data Breach SK Telecom data breach, long-term intrusion
  • Vulnerability Report

React Under Siege: Two IPs Drive 56% of Critical CVE-2025-55182 Attacks

Do Son February 4, 2026 0

Critical React flaw CVE-2025-55182 (CVSS 10.0) under mass exploitation. Two IPs drive 56% of attacks deploying miners & shells. Upgrade to v19.0.1+ now.

Chrome 144 Security Alert: V8 & Libvpx Flaws Expose Systems to Hacks Chrome Security Update Use After Free Chrome Security Update Critical Vulnerabilities Chrome Security Update CVE-2026-3062 Chrome Security Update V8 Engine Vulnerability Chrome Security Update CVE-2026-1862 CVE-2026-0628 Chrome 143 Update Chrome Safe Browsing UAF, CVE-2025-11756 Chrome Memory Flaws, CVE-2025-11460 Google Chrome, vulnerability CVE-2025-10200, CVE-2025-10201 Big Sleep CVE-2025-9478 Chrome Update, Security Vulnerabilities
  • Vulnerability Report

Chrome 144 Security Alert: V8 & Libvpx Flaws Expose Systems to Hacks

Do Son February 4, 2026 0

Google Chrome patches high-severity V8 (CVE-2026-1862) and libvpx (CVE-2026-1861) flaws. Update to version 144.0.7559.132 immediately.

Rooted via Wi-Fi 7: TP-Link Patches Command Injection in Archer BE230 Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Rooted via Wi-Fi 7: TP-Link Patches Command Injection in Archer BE230

Do Son February 4, 2026 0

TP-Link discloses command injection flaws in Archer BE230 routers (CVE-2026-0630). Authenticated attackers can gain root access. Update firmware now.

CVE-2026-24936: Critical ASUSTOR Flaw (CVSS 9.5) Allows Remote System Takeover Everon OCPP Vulnerability CVE-2026-26288 ASUSTOR ADM Vulnerability CVE-2026-24936 PrismX MX100 Vulnerability Hard-Coded Credentials Advantech Vulnerability CVE-2025-52694 Eaton UPS Companion, CVE-2025-59887 ASUS Router, Authentication Bypass ASUSTOR DLL Hijacking, Privilege Escalation OpenShift AI, Privilege Escalation GoAnywhere vulnerability CVE-2025-10035 LangChainGo, template injection DeepDiff, class pollution ToolShell Sunshine, CSRF Vulnerability KACE SMA, Critical Vulnerabilities Oracle Zero-Days - PDQ Deploy vulnerability
  • Vulnerability Report

CVE-2026-24936: Critical ASUSTOR Flaw (CVSS 9.5) Allows Remote System Takeover

Do Son February 4, 2026 0

Critical ASUSTOR ADM flaw CVE-2026-24936 (CVSS 9.5) allows remote file overwrite. Unauthenticated attackers can seize NAS control. Update to v5.1.2 now.
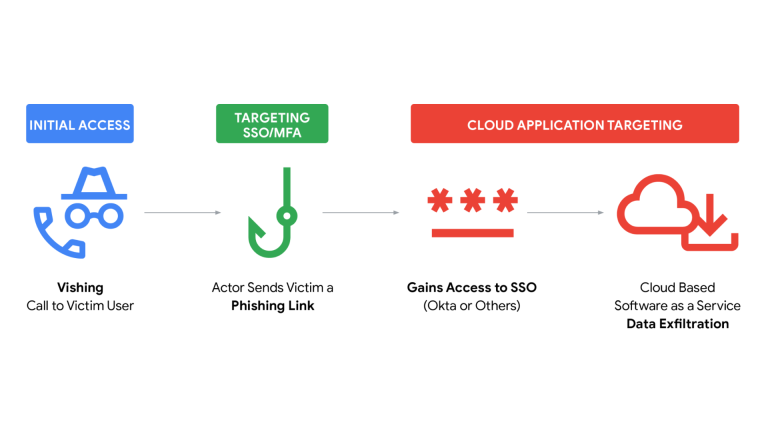
“IT Support” Imposters: ShinyHunters Vishing Rings Bypass MFA to Steal Data ShinyHunters Vishing Corporate Vishing Attacks
  • Cybercriminals

“IT Support” Imposters: ShinyHunters Vishing Rings Bypass MFA to Steal Data

Do Son February 4, 2026 0

Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

Poisoned Comments: Critical Orval Flaw (CVE-2026-25141) Injects Code CVE-2026-25141 Orval Vulnerability CVE-2026-23947
  • Vulnerability Report

Poisoned Comments: Critical Orval Flaw (CVE-2026-25141) Injects Code

Do Son February 4, 2026 0

Critical Orval flaw CVE-2026-25141 (CVSS 9.3) allows code injection via OpenAPI comments. 2.8M+ downloads affected. Update to v7.21.0 now.
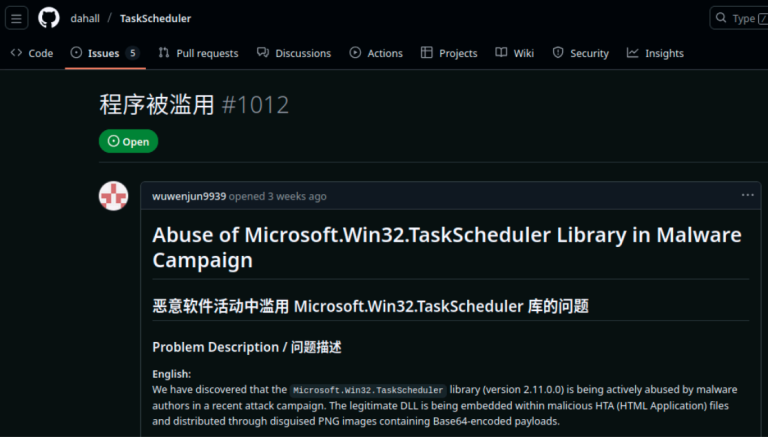
Digital Ghost: “PhantomVAI” Malware Revives Decade-Old RunPE Tricks PhantomVAI Loader RunPE Malware
  • Malware

Digital Ghost: “PhantomVAI” Malware Revives Decade-Old RunPE Tricks

Do Son February 4, 2026 0

New "PhantomVAI" malware recycles old Hackforums "RunPE" code to bypass modern EDR. Campaigns use task scheduler masquerading to deliver infostealers.

Silent Leak: High-Severity Rancher CLI Flaw Exposes Admin Credentials CVE-2024-52281 Rancher CLI Vulnerability CVE-2025-67601
  • Vulnerability Report

Silent Leak: High-Severity Rancher CLI Flaw Exposes Admin Credentials

Do Son February 4, 2026 0

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.
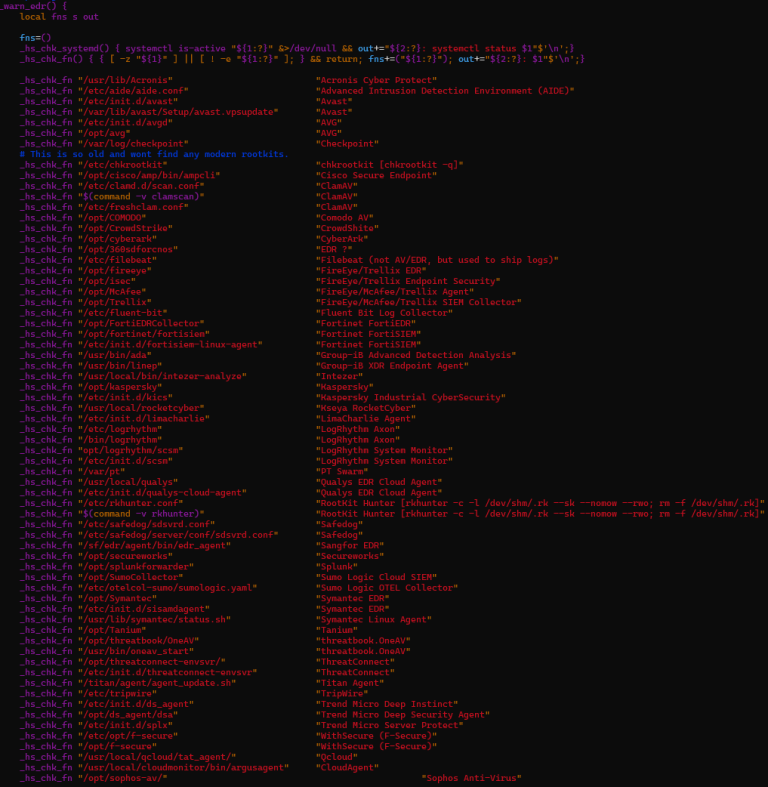
Invisible Intruder: “ShadowHS” Malware Weaponizes Hackshell on Linux ShadowHS Malware Linux Fileless Intrusion
  • Malware

Invisible Intruder: “ShadowHS” Malware Weaponizes Hackshell on Linux

Do Son February 4, 2026 0

Cyble uncovers "ShadowHS," a fileless Linux malware weaponizing hackshell. It uses GSocket tunneling to evade firewalls and kill rival bots.

TAMECAT Exposed: APT42’s Fileless Backdoor Targets Defense Chiefs AI Fraud Schemes TAMECAT Malware APT42 Espionage
  • Cyber Security
  • Malware

TAMECAT Exposed: APT42’s Fileless Backdoor Targets Defense Chiefs

Do Son February 4, 2026 0

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.