
 Do Son
In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...
Critical Odoo on NixOS flaw (CVE-2026-25137) leaves databases exposed due to configuration immutability. Restarts wipe the master password.

Interlock ransomware exploits a zero-day in gaming anti-cheat drivers to blind defenses. "Hotta Killer" tool targets education sector. Read the analysis.

Critical Ingress-Nginx flaws (CVE-2026-1580) allow RCE and secret theft via config injection. Upgrade to v1.13.7 or v1.14.3 immediately to secure K8s.

OpenAI retires GPT-4o on Feb 13, 2026. While Free and Plus users lose access, Enterprise and Education accounts can keep it. Learn how to toggle legacy mode.
Google’s "Aluminium OS" and a new Desktop Camera app have leaked. Discover how the unified Android-ChromeOS platform plans to bring Android 16 to your PC.

On January 29, 2026, Synology, a preeminent manufacturer of Network Attached Storage (NAS) solutions, disseminated a series...

Microsoft confirms Windows 10 updates KB5078131 and KB5073724 are causing shutdown failures on VSM-enabled PCs. Use the "shutdown /s /t 0" fix to power off.

Wiz Research exposes a critical flaw in Moltbook, the AI-only social network. 1.5M API tokens and plaintext OpenAI keys leaked due to AI-coded security gaps.

Microsoft is ending the "permanent off" rule for Smart App Control. You can finally toggle this Zero Trust feature without a full Windows 11 reinstallation.

Microsoft’s KB5074105 update adds a surprise security layer: only administrators can now access Storage settings. Standard users now face a mandatory UAC prompt.
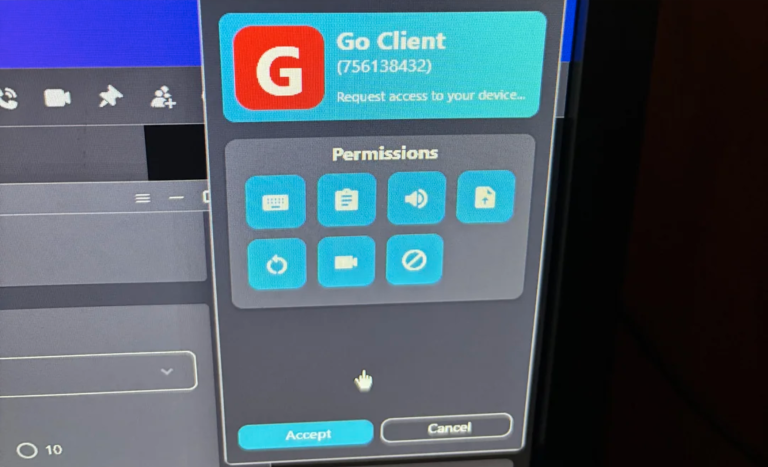
A massive botnet is targeting RustDesk users with fake "Go Client" connection requests. Learn how to lock down your ID and prevent unauthorized remote takeovers.

Samsung’s 2nm Exynos 2600 hits Geekbench, showing a 39% performance jump and narrowing the gap with Qualcomm. Is the "Exynos Curse" finally over for 2026?

CERT Polska reveals destructive attacks on energy infrastructure. "Static Tundra" used DynoWiper and LazyWiper to brick OT devices. Read more.

ASUS removes "File Shredder" from Business Manager due to CVE-2025-13348 (CVSS 8.5). The feature is gone in V3.0.37.0. Check your commercial PCs.

VirusTotal warns of massive supply chain attack on OpenClaw. Hackers use fake "skills" to deploy malware like Atomic Stealer. Verify your agents.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.
Hikvision patches high-severity command injection (CVE-2026-0709) in DS-3WAP access points. Authenticated attackers can execute code. Update now.

Critical KiloView flaw CVE-2026-1453 (CVSS 9.8) allows unauthenticated admin takeover. Broadcast feeds at risk. Check affected E1/E2 versions immediately.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

IClickFix malware hijacks 3,800+ WordPress sites with fake Cloudflare CAPTCHAs. This watering hole attack tricks users into running malicious PowerShell.