Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Identity at Risk: Apache Syncope Patches Critical Login XSS & XXE Flaws Apache Syncope Vulnerability CVE-2026-23794 Syncope Hardcoded Key, Password Decryption
  • Vulnerability Report

Identity at Risk: Apache Syncope Patches Critical Login XSS & XXE Flaws

Do Son February 3, 2026 0

Apache patches XSS (CVE-2026-23794) & XXE flaws in Syncope. Vulnerability allows session hijacking via login page. Update to v3.0.16 or v4.0.4 now.

One Click to “God Mode”: The Critical OpenClaw Flaw That Handed Attackers Your Master Keys shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

One Click to “God Mode”: The Critical OpenClaw Flaw That Handed Attackers Your Master Keys

Do Son February 2, 2026 0

A high-severity flaw in OpenClaw (formerly Clawdbot) allows 1-click Remote Code Execution. Update to v2026.1.29 immediately to prevent total account takeover.

Cracks in the $100 Billion Alliance: Why Jensen Huang is Putting NVIDIA’s OpenAI Mega-Deal on Ice OpenAI token price reduction OpenAI Deployment Company DeployCo OpenAI IPO strategy OpenAI Privacy Filter 1.5B OpenAI $122 billion funding OpenAI GitHub alternative OpenAI military agreement 2026 OpenAI Stargate project collapse NVIDIA OpenAI investment stall ChatGPT Go $8 subscription, OpenAI GPT-5.2 Instant ads OpenAI Torch acquisition, Unified Medical Memory OpenAI Head of Preparedness 2025, Sam Altman AI safety lawsuits ChatGPT Advertising Speculation OpenAI Ad Code Denial OpenAI AI Confession Hallucination Mitigation ChatGPT Quality Focus OpenAI Gemini Red Alert ChatGPT Login, AI ecosystem OpenAI Mental Health, AI Well-Being Council ChatGPT Instant Checkout, Agentic Commerce OpenAI cloud computing OpenAI, startup incubator OpenAI chips, NVIDIA competition AI competition, antitrust lawsuit GPT-5, OpenAI Livestream OpenAI Open-Weight, AI Models OpenAI Infrastructure, AI Data Centers ChatGPT Business, Office Productivity OpenAI Open-Weight Model, WindSurf Acquisition OpenAI AI Browser, ChatGPT Integration Mattel AI, OpenAI Partnership OpenAI o3, Price Cut OpenAI's Next-Gen AI: O3-Pro's Enhanced Reasoning PowerOpenAI profit OpenAI Bid OpenAI Social Network ChatGPT Social OpenAI Non-profit OpenAI UAE ChatGPT Plus free
  • Technology

Cracks in the $100 Billion Alliance: Why Jensen Huang is Putting NVIDIA’s OpenAI Mega-Deal on Ice

Do Son February 2, 2026 0

NVIDIA’s $100B infrastructure pact with OpenAI has reached a "deep freeze." CEO Jensen Huang cited business discipline concerns and rising rivals like Gemini.

The Fragmentation Trap: Why Android 16 is Struggling to Overtake Its Own Ancestors Android 16 adoption rate Android 16KB Page, .NET MAUI 9 Android Security, Fast Charging Android Canary, Developer Program Android Updates, EU Regulation Android 16 Google Android Terminal Cloud Compilation Android, Google I/O
  • Android

The Fragmentation Trap: Why Android 16 is Struggling to Overtake Its Own Ancestors

Do Son February 2, 2026 0

Google’s latest data reveals Android 16 has reached only 7.5% adoption. See how it stacks up against Android 15 and why fragmentation still haunts the platform.

The Flip Side of Innovation: Apple Labs Are Already Prototyping a “Square” Clamshell iPhone iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

The Flip Side of Innovation: Apple Labs Are Already Prototyping a “Square” Clamshell iPhone

Do Son February 2, 2026 0

Apple is exploring a "square" clamshell-style iPhone to rival the Galaxy Z Flip. Discover the latest leaks on the 2026 foldable roadmap and the "iPhone Flip."

The “Illogical” Threat: Why Jensen Huang is Betting $45 Billion That ASICs Can’t Catch NVIDIA NVIDIA acquisition rumors NVIDIA AI Security AI Framework Vulnerabilities Nvidia 595.76 Hotfix NVIDIA Megatron Bridge vulnerability GPU vs ASIC AI battle NVIDIA Driver Vulnerability CVE-2025-33217 NVIDIA biggest TSMC customer 2026, NVIDIA vs Apple TSMC revenue share NVIDIA CUDA Toolkit CVE-2025-33228 Groq NVIDIA licensing deal, Jonathan Ross acquihire 2025 NeMo Code Injection, AI Framework RCE NVIDIA App Privilege Escalation, CVE-2025-23358 NVIDIA Security Update, DLS Vulnerability CVE-2025-23316 NVIDIA NVDebug, vulnerabilities NVIDIA Driver Vulnerabilities, vGPU Security Nvidia Jetson, UEFI Vulnerabilities CVE-2024-0130 - CVE-2024-0136 CVE-2024-0148 NVIDIA Driver Support, Windows 10 EOL
  • Technology

The “Illogical” Threat: Why Jensen Huang is Betting $45 Billion That ASICs Can’t Catch NVIDIA

Do Son February 2, 2026 0

Jensen Huang dismisses custom AI chips as "illogical," announcing a $45B R&D surge to ensure NVIDIA’s programmable GPUs outpace static ASIC competitors.

Linear Freedom: Apple Overhauls the Mac Store to Unleash Bespoke M5 AI Powerhouses Apple Mac configuration update
  • Technology

Linear Freedom: Apple Overhauls the Mac Store to Unleash Bespoke M5 AI Powerhouses

Do Son February 2, 2026 0

Apple’s online store goes "linear," ditching pre-sets for a build-from-scratch Mac experience. Discover how the M5 and RDMA are turning Macs into AI clusters.

Notepad++ Hijacked: State-Sponsored Actors Poisoned Updates for Months FortiClient EMS exploitation Cisco FIRESTARTER Backdoor Arcane Door Campaign Dell RecoverPoint Zero-Day UNC6201 Espionage Notepad++ Compromise Supply Chain Attack Magento SessionReaper CVE-2025-54236 ShadowRay 2.0, AI-Generated Malware WordPress Auth Bypass, CVE-2025-5947 Exploited EcoStruxure Vulnerabilities, Industrial Control System UNC5820 - CVE-2014-2120 - CVE-2021-44207
  • Cyber Security

Notepad++ Hijacked: State-Sponsored Actors Poisoned Updates for Months

Do Son February 2, 2026 0

Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.

IIS Under Siege: UAT-8099 Deploys Region-Locked “BadIIS” & Linux Variants UAT-8099 BadIIS Malware Pacific Islands Forum Cyberattack
  • Cyber Security
  • Malware

IIS Under Siege: UAT-8099 Deploys Region-Locked “BadIIS” & Linux Variants

Do Son February 2, 2026 0

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.

The “Fix” is a Trap: ConsentFix Phishing Bypasses MFA via Azure CLI ConsentFix Phishing OAuth Token Theft
  • Cybercriminals

The “Fix” is a Trap: ConsentFix Phishing Bypasses MFA via Azure CLI

Do Son February 2, 2026 0

"ConsentFix" phishing tricks users into pasting OAuth codes from Azure CLI, bypassing MFA and Conditional Access. Detect this "fix" scam now.

Signed & Stolen: “Phantom Stealer” Hijacks Java App via Fake DHL Invoice Xloader Malware Information Stealer Phantom Stealer v3.5.0 DLL Sideloading Attack
  • Malware

Signed & Stolen: “Phantom Stealer” Hijacks Java App via Fake DHL Invoice

Do Son February 2, 2026 0

Attackers use fake DHL invoices to sideload Phantom Stealer v3.5.0 via a signed Java utility. Malware hides in AddInProcess32.exe. Watch out.

New Offensive OT Framework Targeting Energy Infrastructure Emerges on Dark Web ICS Offensive Framework APT IRAN
  • Cybercriminals

New Offensive OT Framework Targeting Energy Infrastructure Emerges on Dark Web

Do Son February 2, 2026 0

New "APT IRAN" framework targets energy grids & military networks. Lab52 links the tool to the IRGC. See the threat to critical infrastructure.

Silent Intruder: “EncystPHP” Web Shell Burrows into FreePBX Systems EncystPHP Web Shell FreePBX Vulnerability
  • Cybercriminals
  • Vulnerability Report

Silent Intruder: “EncystPHP” Web Shell Burrows into FreePBX Systems

Do Son February 2, 2026 0

INJ3CTOR3 hackers target FreePBX with EncystPHP web shell via CVE-2025-64328. Malware uses cron jobs for persistence. Patch immediately.

“Exfil Out&Look” Flaw Lets Spies Steal Emails via OWA Undetected Exfil Out&Look Microsoft 365 Logging Gap Outlook Classic KB5074109 freeze, January 2026 POP3 PST bug Outlook Classic POP3 freeze, KB5074109 Windows 11 bug Outlook, CPU Usage Outlook lag Outlook Lite discontinued
  • Vulnerability Report

“Exfil Out&Look” Flaw Lets Spies Steal Emails via OWA Undetected

Do Son February 2, 2026 0

New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.

Hidden in Plain Sight: TA584 Deploys “Tsundere Bot” & Invisible Registry Keys TA584 Tsundere Bot Invisible Registry Persistence
  • Cybercriminals

Hidden in Plain Sight: TA584 Deploys “Tsundere Bot” & Invisible Registry Keys

Do Son February 2, 2026 0

TA584 triples activity with new "Tsundere Bot" malware. Attackers use invisible Registry keys to hide persistence. Read the Proofpoint analysis.
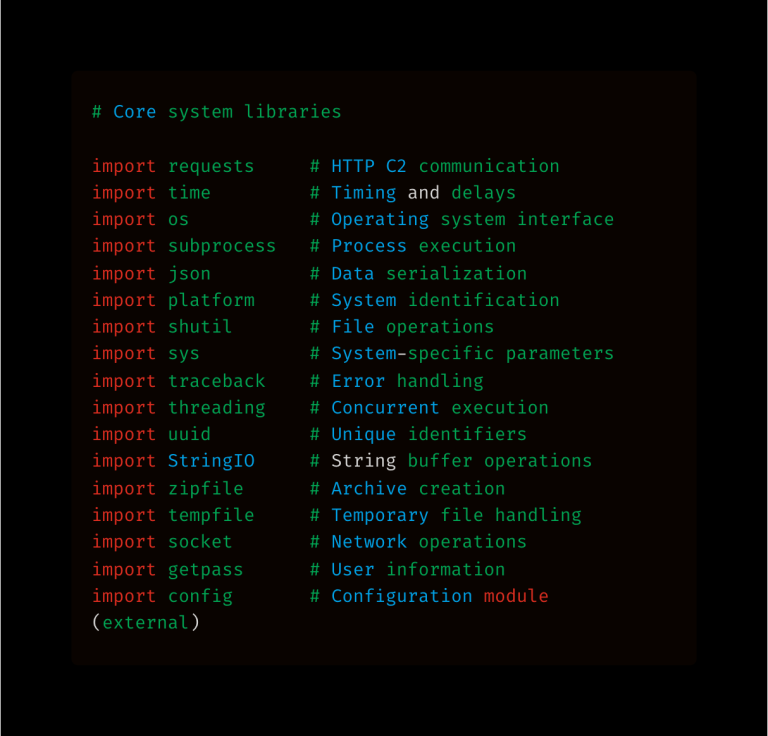
Wrapped in Stealth: Python RAT Hides Inside ELF Binary to Evade Detection Python-based RAT Adaptive Beaconing
  • Malware

Wrapped in Stealth: Python RAT Hides Inside ELF Binary to Evade Detection

Do Son February 2, 2026 0

K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.

AI-Coded Malware: Vietnamese “Huna” Actor Targets Job Seekers with PureRAT AccountDumpling Phishing Google AppSheet Abuse AI-Generated Malware PureRAT Campaign RondoDoX Botnet, Next.js React2Shell EchoGather, Paper Werewolf Salt Typhoon, Telecom Espionage BreachForums, Conor Fitzpatrick Ransomware Negotiation, DOJ Investigation MirrorFace group - Earth Kasha Emperor Dragonfly
  • Malware

AI-Coded Malware: Vietnamese “Huna” Actor Targets Job Seekers with PureRAT

Do Son February 2, 2026 0

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

EdTech startups and the role of LMS in their growth tech
  • Technique

EdTech startups and the role of LMS in their growth

Do Son January 31, 2026 0
What are EdTech startups? EdTech startups are typically presented as young tech companies that build digital products...
Read More Read more about EdTech startups and the role of LMS in their growth
VPNs & Fake Updates: Google Dismantles Massive IPIDEA Proxy Network IPIDEA Proxy Network Residential Proxy Disruption
  • Cybercriminals

VPNs & Fake Updates: Google Dismantles Massive IPIDEA Proxy Network

Do Son January 31, 2026 0

Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.

From User to SYSTEM: PoC Released for Zabbix Privilege Escalation CVE-2024-42330 Zabbix Privilege Escalation CVE-2025-27237
  • Vulnerability

From User to SYSTEM: PoC Released for Zabbix Privilege Escalation

Do Son January 30, 2026 0

Exploit code released for Zabbix flaw CVE-2025-27237. Low-level users can gain SYSTEM privileges on Windows via OpenSSL config. Update now.

“Update” to Nightmare: eScan Antivirus Hacked to Distribute Malware TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

“Update” to Nightmare: eScan Antivirus Hacked to Distribute Malware

Do Son January 30, 2026 0

Critical supply chain attack hits eScan antivirus. Hackers hijacked updates to install malware and disable the AV. Manual patch required.

Smart Buildings at Risk: Critical Johnson Controls Flaw (CVSS 10) Allows Remote SQL Injection shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

Smart Buildings at Risk: Critical Johnson Controls Flaw (CVSS 10) Allows Remote SQL Injection

Do Son January 30, 2026 0

CISA warns of CVSS 10 flaw CVE-2025-26385 in Johnson Controls Metasys. Remote SQL execution possible. Patch now or close TCP port 1433.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.