Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
The “Zeroplayer” Arsenal: WinRAR Flaw CVE-2025-8088 Weaponized by Spies WinRAR Vulnerability CVE-2025-8088
  • Cybercriminals
  • Vulnerability Report

The “Zeroplayer” Arsenal: WinRAR Flaw CVE-2025-8088 Weaponized by Spies

Do Son January 29, 2026 0

Critical WinRAR flaw CVE-2025-8088 is exploited by spies & cybercriminals. "Zeroplayer" sells the exploit. Update to v7.13 to stop Startup folder attacks.
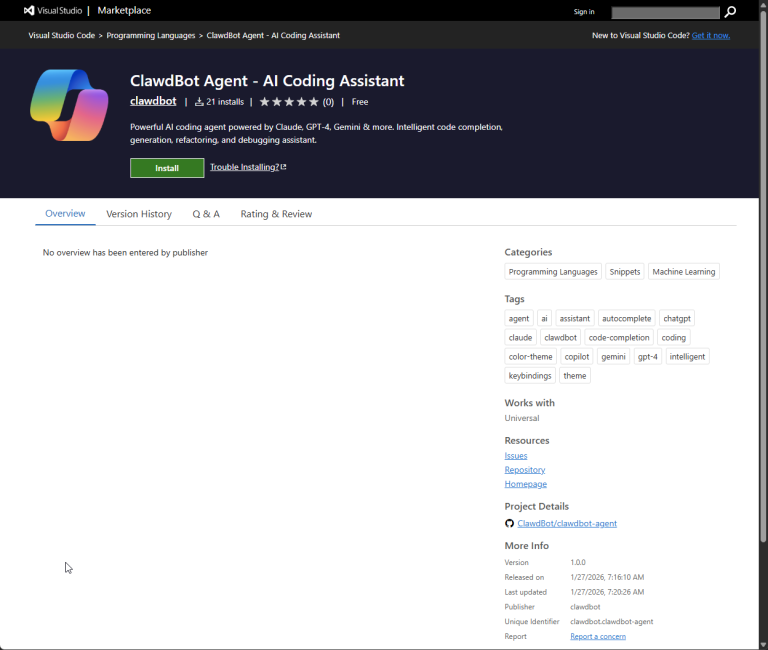
Fake AI Assistant: Malicious “ClawdBot” Extension Hides Trojan in VS Code ClawdBot Malware VS Code Trojan
  • Malware

Fake AI Assistant: Malicious “ClawdBot” Extension Hides Trojan in VS Code

Do Son January 29, 2026 0

Malicious "ClawdBot Agent" VS Code extension exposed. Functioning as a real AI tool, it silently dropped malware. Microsoft removed it after 21 installs.

CVE-2026-23830: Critical SandboxJS Flaw (CVSS 10) Allows Total Sandbox Escape shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2026-23830: Critical SandboxJS Flaw (CVSS 10) Allows Total Sandbox Escape

Do Son January 29, 2026 0

CVSS 10 flaw CVE-2026-23830 in SandboxJS allows RCE via unpatched Async functions. Attackers bypass all limits. Update to v0.8.26 immediately.

CVE-2025-14988: Critical 9.8 Vulnerability hits ibaPDA Industrial Software shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

CVE-2025-14988: Critical 9.8 Vulnerability hits ibaPDA Industrial Software

Do Son January 29, 2026 0

Critical ibaPDA flaw CVE-2025-14988 (CVSS 9.8) exposes industrial systems to file tampering. Update to v8.12.1 or harden settings now.

The “Fake CAPTCHA” Trap: Malware Hides in Google Calendar & Images CloudComputating - QSC framework
  • Malware

The “Fake CAPTCHA” Trap: Malware Hides in Google Calendar & Images

Do Son January 29, 2026 0

New Fake CAPTCHA campaign uses Google Calendar & steganography to drop Amatera Stealer. See how this attack exploits legitimate Windows tools to stay hidden.

Science at the Speed of AI: OpenAI Unveils Prism for LaTeX Research ChatGPT Lockdown Mode OpenAI OpenClaw acquisition OpenAI Prism GPT-5.2 LaTeX, scientific research AI workspace OpenAI, Mixpanel Breach ChatGPT Data Preservation, NYT Lawsuit ChatGPT Apps SDK, super app OpenAI Jony Ive, AI Hardware Delay Musk Apple lawsuit, App Store antitrust UK AI Partnership, OpenAI Collaboration Jony Ive OpenAI, DoD Contract OpenAI Lawsuit, ChatGPT Privacy North Korea ChatGPT - GPT-4.5 model OpenAI Models, AI Advancements OpenAI pricing, Flex API
  • Technology

Science at the Speed of AI: OpenAI Unveils Prism for LaTeX Research

Do Son January 29, 2026 0

OpenAI launches Prism in Jan 2026. Powered by GPT-5.2, this free LaTeX workspace automates citations, equations, and diagrams for scientists.

The Return of the Guide: Yahoo Scout Challenges Google with AI-Native Search Yahoo Scout AI answer engine, Anthropic Claude Yahoo search 2026
  • Technology

The Return of the Guide: Yahoo Scout Challenges Google with AI-Native Search

Do Son January 29, 2026 0

Yahoo debuts Scout in Jan 2026. This Anthropic Claude-powered answer engine blends AI summaries with prominent links to save the open web.

Excel’s New Brain: Agent Mode Brings GPT-5.2 and Claude 4.5 to Desktop Microsoft Excel Agent Mode 2026, Copilot model selector GPT-5.2 Claude 4.5
  • Technology

Excel’s New Brain: Agent Mode Brings GPT-5.2 and Claude 4.5 to Desktop

Do Son January 29, 2026 0

Microsoft Excel's Agent Mode is now on Windows and Mac! Switch between GPT-5.2 and Claude 4.5 to automate complex workbooks and live web data.

The 13-Year Lifeline: Apple Updates the iPhone 5s to Save iMessage Apple iOS 12.5.8 certificate update, iPhone 5s legacy support 2026 CVE-2022-42856 vulnerability
  • Technology

The 13-Year Lifeline: Apple Updates the iPhone 5s to Save iMessage

Do Son January 29, 2026 0

Apple released iOS 12.5.8 in Jan 2026. This critical update extends iMessage and FaceTime support for the 13-year-old iPhone 5s until 2027.

The $40M Insider Heist: Son of Federal Contractor Investigated for Seized Crypto Theft CMDSS ZachXBT crypto theft, John Daghita U.S. Marshals investigation Bitfinex Hacker - DMM Bitcoin Cyberattack
  • Cybercriminals

The $40M Insider Heist: Son of Federal Contractor Investigated for Seized Crypto Theft

Do Son January 29, 2026 0

ZachXBT unmasks an alleged $40M theft of U.S. government crypto in Jan 2026. The suspect? The son of the USMS contractor hired to protect it.

SolarWinds Web Help Desk Hit with Multiple RCE and Auth Bypass Vulnerabilities CVE-2024-23476 & CVE-2024-23479 SolarWinds Web Help Desk Unauthenticated RCE
  • Vulnerability Report

SolarWinds Web Help Desk Hit with Multiple RCE and Auth Bypass Vulnerabilities

Do Son January 28, 2026 0

Critical SolarWinds Web Help Desk flaws (CVSS 9.8) allow unauthenticated RCE and auth bypass. Hardcoded credentials also found. Patch immediately.

Beyond ChromeOS: Google’s “Aluminum OS” Desktop Android Leaks Online Android CLI Android Security Zero-Interaction DoS CVE-2026-21385 Android Security Update UK CMA Apple Google regulation Google Aluminum OS Android 16 leak, ALOS Android ChromeOS merger Android sideloading certification 2026, Google developer verification APK Android AOSP biannual release, AOSP source code latency 2026 Android Zero-Day, Critical DoS Flaw Android Universal Clipboard Cross-Device Sync Gemini Nano Block, Unlocked Bootloader Android, Calling Cards Android Security Bulletin, RCE Vulnerability Android Linux GUI, Debian VM Android System Services, Google Transparency Android 16, Pixel Update
  • Android

Beyond ChromeOS: Google’s “Aluminum OS” Desktop Android Leaks Online

Do Son January 28, 2026 0

Google's secret Aluminum OS leaked in Jan 2026! See the first visual evidence of the Android 16 desktop merger and its deep Gemini AI integration.

Labels for Machines: Google Proposes ai-disclosure Tags for Every Web Element Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

Labels for Machines: Google Proposes ai-disclosure Tags for Every Web Element

Do Son January 28, 2026 0

Google proposes the ai-disclosure tag in Jan 2026. Discover how this new Chrome standard will label AI-generated text across the web.

AI for All: Google Launches $7.99 AI Plus Tier with Gemini 3 Pro Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

AI for All: Google Launches $7.99 AI Plus Tier with Gemini 3 Pro

Do Son January 28, 2026 0

Google launches AI Plus for $7.99 in Jan 2026. Get Gemini 3 Pro, Nano Banana Pro, and 200GB storage at half the price of AI Pro.

The Egress Explosion: Google Cloud to Double Interconnect Prices in May 2026 Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

The Egress Explosion: Google Cloud to Double Interconnect Prices in May 2026

Do Son January 28, 2026 0

Google Cloud will double CDN Interconnect and Peering rates on May 1, 2026. Discover how the 100% price hike impacts Cloudflare and your cloud bill.

Pivoting the Pin: Pinterest Cuts 15% of Staff to Fuel AI Ambitions Pinterest AI layoffs 2026, Pinterest workforce reduction 15% OpenAI Pinterest acquisition 2026, multimodal AI training data Pinterest Assistant, AI Search, Visual Discovery
  • Technology

Pivoting the Pin: Pinterest Cuts 15% of Staff to Fuel AI Ambitions

Do Son January 28, 2026 0

Pinterest announced a 15% layoff in Jan 2026. Discover how the visual discovery platform is pivoting 700+ jobs into an aggressive AI-forward strategy.

Sandbox Shattered: Critical n8n Flaw (CVSS 9.9) Allows Remote Code Execution n8n Node RCE Vulnerabilities CVE-2026-44791 Prototype Pollution n8n RCE Vulnerabilities CVE-2026-27497 CVE-2026-25053 n8n RCE Vulnerability CVE-2026-21877 n8n RCE, CVE-2025-68613 n8n Git RCE, core.hooksPath Exploit
  • Vulnerability Report

Sandbox Shattered: Critical n8n Flaw (CVSS 9.9) Allows Remote Code Execution

Do Son January 28, 2026 0

Critical n8n RCE (CVE-2026-1470) lets attackers bypass sandbox defenses via malicious expressions. CVSS 9.9. Check versions 1.123.17 & 2.x now.

HPE Aruba Patches High-Severity RCE and OpenSSL Flaws CVE-2024-42509 & CVE-2024-47460 HPE Aruba Fabric Composer CVE-2026-23592 Aruba AOS-CX CVE-2026-23813
  • Vulnerability Report

HPE Aruba Patches High-Severity RCE and OpenSSL Flaws

Do Son January 28, 2026 0

HPE patches critical RCE (CVE-2026-23592) in Fabric Composer. Authenticated attackers can seize the OS via backup tools. Update to v7.3.0 immediately.

Snatch-and-Run Stopped: Android’s New AI Locks Stolen Phones Instantly Android Theft Protection Theft Detection Lock
  • Android

Snatch-and-Run Stopped: Android’s New AI Locks Stolen Phones Instantly

Do Son January 28, 2026 0

New Android anti-theft updates use AI to detect "snatch-and-run" theft and instantly lock your screen. Identity Check adds biometric layers to stop thieves.

46 Months for $37 Million: Chinese National Sentenced for Role in Cambodian Crypto Scam Ring FIFA website spoofing scams FBI World Cup alert Pig Butchering Scam Jingliang Su Sentencing Meta China Scam Ads, Zuckerberg Revenue Conflict Trading Bot Scam BEC Scam Rental Payment Fraud
  • Cybercriminals

46 Months for $37 Million: Chinese National Sentenced for Role in Cambodian Crypto Scam Ring

Do Son January 28, 2026 0

Jingliang Su sentenced to 46 months for laundering $36.9M in "pig butchering" proceeds. The scheme funneled crypto to Cambodian fraud hubs.

Pre-Auth RCE Risk: OpenSSL Patches High-Severity Stack Overflow (CVE-2025-15467) OpenSSL Vulnerability RSA Memory Leak OpenSSL Vulnerability CVE-2025-15467 CVE-2022-2274 OpenSSL Vulnerabilities, Timing Side-Channel
  • Vulnerability Report

Pre-Auth RCE Risk: OpenSSL Patches High-Severity Stack Overflow (CVE-2025-15467)

Do Son January 28, 2026 0

OpenSSL patches 12 flaws, including high-severity CVE-2025-15467 allowing pre-auth RCE via CMS. Update to 3.6.1/3.0.19 immediately to secure systems.

Under Attack: Critical Fortinet Auth Bypass (CVE-2026-24858) Exploited in the Wild GUARDIANWALL MailSuite Exploit CVE-2026-32661 FileZen Vulnerability CVE-2026-25108 Ivanti EPMM Vulnerability Dormant Backdoor Fortinet Authentication Bypass CVE-2026-24858 VMware vCenter Server Flaw CVE-2025-21590
  • Vulnerability Report

Under Attack: Critical Fortinet Auth Bypass (CVE-2026-24858) Exploited in the Wild

Do Son January 28, 2026 0

Fortinet warns of critical flaw CVE-2026-24858 exploited in the wild. Attackers use FortiCloud SSO to bypass auth on FortiOS/Manager. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.