Skip to content
November 9, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Chrome Patches High-Severity Background Fetch Flaw (CVE-2026-1504) Chrome security update, CVE-2026-12007, CVE-2026-12008, CVE-2026-12010 Chrome Security Update CVE-2026-1504 Chrome WebGPU Overflow, V8 RCE
  • Vulnerability Report

Chrome Patches High-Severity Background Fetch Flaw (CVE-2026-1504)

Do Son January 28, 2026 0

Chrome 144 fixes high-severity flaw CVE-2026-1504 in Background Fetch API. Malicious sites could abuse downloads. Update immediately to stay safe.
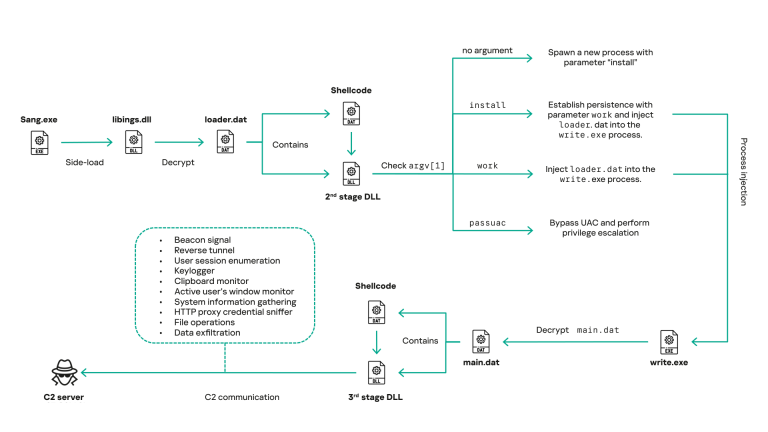
HoneyMyte Evolved: Spies Use Pixeldrain & CoolClient for Real-Time Surveillance HoneyMyte Espionage CoolClient Backdoor
  • Cyber Security
  • Malware

HoneyMyte Evolved: Spies Use Pixeldrain & CoolClient for Real-Time Surveillance

Do Son January 28, 2026 0

HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

The “PayTool” Trap: Massive Fraud Cluster Impersonates Canada Gov & Air Canada WhatsApp Worm, Brazilian Banking Trojan LAPSUS$ Alliance, Scattered Spider Ransomware, Cybercrime RedCurl APT group Russian Cyberespionage, ApolloShadow Malware
  • Cybercriminals

The “PayTool” Trap: Massive Fraud Cluster Impersonates Canada Gov & Air Canada

Do Son January 28, 2026 0

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

Router Takeover: High-Severity Command Injection Flaw Hits TP-Link Archer MR600 Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Router Takeover: High-Severity Command Injection Flaw Hits TP-Link Archer MR600

Do Son January 28, 2026 0

TP-Link patches CVE-2025-14756 (CVSS 8.5) in Archer MR600 routers. This command injection flaw allows full device takeover. Update firmware now.

“Gopher Strike”: New Pakistan-Linked Cyber Campaigns Target Indian Government Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

“Gopher Strike”: New Pakistan-Linked Cyber Campaigns Target Indian Government

Do Son January 28, 2026 0

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

Digital El Dorado: How the Tiny Island of Anguilla Hit the 1 Million .ai Domain Jackpot AI Prompt Injection Aqua Trivy Breach AI Assistant Apertus, open-source AI .ai domain milestone
  • Technology

Digital El Dorado: How the Tiny Island of Anguilla Hit the 1 Million .ai Domain Jackpot

Do Son January 28, 2026 0

Anguilla’s .ai domain has officially surpassed 1 million registrations, generating over $70M for the island and funding major national infrastructure.

The “Iron Man” Moment: Why Silicon Valley is Buying Out Mac Minis to Run Clawdbot Clawdbot AI agent
  • Technology

The “Iron Man” Moment: Why Silicon Valley is Buying Out Mac Minis to Run Clawdbot

Do Son January 28, 2026 0

Clawdbot is the viral "Local-First" AI agent turning Mac minis into personal digital employees. See why GitHub's latest star is a must-have for 2026.

Geopolitical Gridlock: Why China is Putting Meta’s $2 Billion Manus AI Deal Under the Microscope Meta Manus AI acquisition block Meta acquisition Manus AI agent, Manus $100M ARR startup
  • Technology

Geopolitical Gridlock: Why China is Putting Meta’s $2 Billion Manus AI Deal Under the Microscope

Do Son January 28, 2026 0

China launches a national security probe into Meta’s $2B acquisition of AI startup Manus. Algorithmic export and data sovereignty now threaten the deal.

The AI Throne Reclaimed? Samsung Nears Final NVIDIA “Seal of Approval” for Game-Changing HBM4 Samsung MagicInfo9 Vulnerability CVE-2026-25202 Galaxy S26 benchmarks Samsung HBM4 NVIDIA certification Samsung Bixby Perplexity integration, One UI 8.5 AI assistant Samsung Taylor 2nm mass production, TSMC 2nm capacity constraint 2026 Samsung SATA SSD Discontinuation, SSD Market Shift Samsung SATA SSD Discontinuation, M.2 Market Shift Samsung Foundry 4nm Yield Tsavorite OPU Chip Order Samsung Project Moohan, Android XR Samsung OpenAI Partnership, AI Infrastructure Samsung Exynos 2600, 2nm GAA Tesla AI Chips, Samsung Foundry Deal Samsung Foldables, Galaxy Unpacked 2025 Samsung AI, Perplexity AI Samsung data breach Q990D firmware US tariffs
  • Technology

The AI Throne Reclaimed? Samsung Nears Final NVIDIA “Seal of Approval” for Game-Changing HBM4

Do Son January 28, 2026 0

Samsung enters the final phase of NVIDIA’s HBM4 certification. Mass production in early 2026 could break SK Hynix’s monopoly and reshape the AI memory market.

Lock the Front Door: The “Localhost” Loophole Leaving Thousands of Clawdbot Agents Exposed Clawdbot security bypass
  • Data Leak

Lock the Front Door: The “Localhost” Loophole Leaving Thousands of Clawdbot Agents Exposed

Do Son January 27, 2026 0

A critical flaw in Clawdbot’s auth logic allows hackers to bypass security via reverse proxies. Over 1,000 instances are already exposed—is yours one of them?

Lost No More: Apple Unveils AirTag 2 With 50% More Range and a Genius Apple Watch Upgrade Apple AirTag 2
  • Technology

Lost No More: Apple Unveils AirTag 2 With 50% More Range and a Genius Apple Watch Upgrade

Do Son January 27, 2026 0

Apple’s new AirTag 2 is here! Enjoy 50% more range, louder alerts, and Precision Finding on your Apple Watch—all for the same $29 price. Order yours today.

Microsoft Unveils Maia 200: The 3nm Beast Designed to Break NVIDIA’s AI Grip Microsoft Maia 200
  • Technology

Microsoft Unveils Maia 200: The 3nm Beast Designed to Break NVIDIA’s AI Grip

Do Son January 27, 2026 0

Microsoft debuts Maia 200, a 3nm AI powerhouse with 140B transistors. Designed for GPT-5.2 and Copilot, it triples the performance of Amazon’s Trainium 3.

The 5-Gigawatt Power Play: NVIDIA Pumps $2B Into CoreWeave to Build the Future of AI Factories NVIDIA CoreWeave investment NVIDIA H200 China, AI Chip Export Fee
  • Technology

The 5-Gigawatt Power Play: NVIDIA Pumps $2B Into CoreWeave to Build the Future of AI Factories

Do Son January 27, 2026 0

NVIDIA doubles down on AI infrastructure with a $2B stake in CoreWeave. Together, they aim to build a massive 5GW "AI Factory" ecosystem by 2030.

Escape “Calendar Purgatory”: Google’s New Gemini AI Autopilot Schedules Your Meetings for You Google Calendar Gemini AI
  • Technology

Escape “Calendar Purgatory”: Google’s New Gemini AI Autopilot Schedules Your Meetings for You

Do Son January 27, 2026 0

Google Calendar integrates Gemini AI to scan schedules and suggest the perfect meeting times. Say goodbye to back-and-forth emails with this new AI concierge.

OpenAI’s Big Ad Gamble: Why ChatGPT Ads Cost 3x More Than Meta With Way Less Data ChatGPT advertising US only OpenAI GPT-5.4 launch OpenAI Responses API file support ChatGPT Ads pricing ChatGPT conversational advertising, OpenAI monetization strategy 2026 OpenAI Code Red, ChatGPT Sycophancy Crisis AI music ChatGPT memory, targeted ads ChatGPT User Milestone, Generative AI Adoption ChatGPT ads, AI monetization GPT-5, OpenAI
  • Technology

OpenAI’s Big Ad Gamble: Why ChatGPT Ads Cost 3x More Than Meta With Way Less Data

Do Son January 27, 2026 0

OpenAI is pitching ChatGPT ads at a premium $60 CPM—triple Meta's rate. Is "high-intent" AI conversation worth the price despite limited tracking data?

The Miami Glitch: How a Single Config Error Leaked Cloudflare’s IPv6 Routes to the Global Internet Cloudflare BGP route leak
  • Data Leak
  • Technology

The Miami Glitch: How a Single Config Error Leaked Cloudflare’s IPv6 Routes to the Global Internet

Do Son January 27, 2026 0

Cloudflare reveals how an inadvertent policy change in Miami triggered a 25-minute BGP route leak, impacting global IPv6 traffic and exposing network vulnerabilities.

Apple Unlocks AirTag 2: New iOS Update Brings High-Precision Tracking to Your Wrist iOS 27 rumors iOS 26.2.1 Update Apple Intelligence, iOS 26 iOS Notification Forwarding, EU DMA Compliance
  • Technology

Apple Unlocks AirTag 2: New iOS Update Brings High-Precision Tracking to Your Wrist

Do Son January 27, 2026 0

Apple releases iOS 26.2.1 to power the new AirTag 2. Discover how UWB 2 and a Gemini-backed Siri are set to redefine the Find My experience this spring.

CVSS 9.8 Sandbox Escape: Critical vm2 Flaw Exposes Millions of Apps Lockbit ransomware vm2 Vulnerability Sandbox Escape
  • Vulnerability Report

CVSS 9.8 Sandbox Escape: Critical vm2 Flaw Exposes Millions of Apps

Do Son January 27, 2026 0

CVSS 9.8 vm2 flaw (CVE-2026-22709) affects 3.7 million users, allowing total sandbox escape via async functions. Update to v3.10.2 immediately.

Incomplete Fix: High-Severity React Server Components DoS Flaw (CVE-2026-23864) React Server Components Vulnerability CVE-2026-23870 React Server Components Server-Side DoS React DoS Vulnerability CVE-2026-23864 React Server Components DoS, Source Code Disclosure React RCE, Server Components Deserialization CVE-2025-55182
  • Vulnerability Report

Incomplete Fix: High-Severity React Server Components DoS Flaw (CVE-2026-23864)

Do Son January 27, 2026 0

New React Server Components flaw CVE-2026-23864 (CVSS 7.5) exposes apps to DoS attacks. Previous patches were incomplete. Update to v19.0.4+ now.

High-Severity Flaw in Western Digital Installer Opens Door to Code Execution WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Vulnerability Report

High-Severity Flaw in Western Digital Installer Opens Door to Code Execution

Do Son January 27, 2026 0

Critical WD Discovery flaw CVE-2025-30248 (CVSS 8.9) allows DLL hijacking during installation. Update to v5.3 immediately to prevent system takeover.

Stealth in Script: “PeckBirdy” Framework Powers New Wave of China-Aligned Attacks CVE-2024-22394
  • Cyber Security
  • Malware

Stealth in Script: “PeckBirdy” Framework Powers New Wave of China-Aligned Attacks

Do Son January 27, 2026 0

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.

Under Attack: Microsoft Patches Office Zero-Day (CVE-2026-21509) Exploited in the Wild CVE-2024-38021 Microsoft Office Zero-Day CVE-2026-21509
  • Vulnerability Report

Under Attack: Microsoft Patches Office Zero-Day (CVE-2026-21509) Exploited in the Wild

Do Son January 27, 2026 0

Microsoft patches zero-day CVE-2026-21509, actively exploited in the wild. The flaw bypasses OLE security in Office 2016/2019. Update to Build 16.0.10417+.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123751
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120459CVSS 9.1
    python-jose through 3.5.0 contains an authentication bypass vulnerability that allows unauthenticated attackers to forge JWTs because HMACKey and...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 9, 2026
  • CVE-2026-115252CVSS 10.0
    The Confection WordPress Cable WordPress plugin from 0.4.0 to 0.4.7 does not perform any capability or nonce checks...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124060CVSS 9.4
    A vulnerability was detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this issue is the function UploadCustomModule of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123961CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. This impacts the function setWiFiBasicConfig of the file...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123957CVSS 9.4
    A vulnerability was determined in TOTOLINK CA300-PoE 6.2c.884. Impacted is the function setIpQosRules of the file /cgi-bin/cstecgi.cgi. This...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 9, 2026
  • CVE-2026-95731CVSS 9.8
    Hardcoded password vulnerabilities in the command-line interface of HPE Networking Fabric Composer could allow an unauthenticated remote attacker...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.