Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
High-Severity Flaw in Western Digital Installer Opens Door to Code Execution WD Discovery Vulnerability CVE-2025-30248 binary-parser Vulnerability CVE-2026-1245 H3C RCE Vulnerability CVE-2025-60262 Telenium RCE, CVE-2025-10659 Fuel station security, ICS vulnerabilities FreePBX vulnerability CVE-2024-9478 & CVE-2024-9479 SysTrack Vulnerability, Privilege Escalation
  • Vulnerability Report

High-Severity Flaw in Western Digital Installer Opens Door to Code Execution

Do Son January 27, 2026 0

Critical WD Discovery flaw CVE-2025-30248 (CVSS 8.9) allows DLL hijacking during installation. Update to v5.3 immediately to prevent system takeover.

Stealth in Script: “PeckBirdy” Framework Powers New Wave of China-Aligned Attacks CVE-2024-22394
  • Cyber Security
  • Malware

Stealth in Script: “PeckBirdy” Framework Powers New Wave of China-Aligned Attacks

Do Son January 27, 2026 0

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.

Under Attack: Microsoft Patches Office Zero-Day (CVE-2026-21509) Exploited in the Wild CVE-2024-38021 Microsoft Office Zero-Day CVE-2026-21509
  • Vulnerability Report

Under Attack: Microsoft Patches Office Zero-Day (CVE-2026-21509) Exploited in the Wild

Do Son January 27, 2026 0

Microsoft patches zero-day CVE-2026-21509, actively exploited in the wild. The flaw bypasses OLE security in Office 2016/2019. Update to Build 16.0.10417+.

Why Your Incident Response Plan Will Fail without a Sandbox Screenshot 2026-01-26 at 09.57.09
  • Technique

Why Your Incident Response Plan Will Fail without a Sandbox

Do Son January 27, 2026 0
Your IR plan probably isn’t failing because it’s “bad.” It fails because, when something suspicious shows up,...
Read More Read more about Why Your Incident Response Plan Will Fail without a Sandbox
What Makes an AI SOC Decision Trustworthy? CVE-2024-6806 & CVE-2024-6805
  • Technique

What Makes an AI SOC Decision Trustworthy?

Do Son January 27, 2026 0
When you put your career on the line over AI-driven decisions, those decisions had better be defensible,...
Read More Read more about What Makes an AI SOC Decision Trustworthy?
High-Severity DoS Flaw Hits Google Protocol Buffers (CVE-2026-0994) shell-quote command injection AI-Driven Vulnerabilities Q1 2026 Cyber Threats vm2 Sandbox Escape Node.js RCE upKeeper Privilege Escalation CVE-2026-2449 Pharos Controls Vulnerability Root Access Exploit Cybersecurity Vulnerability Roundup CVSS 10.0 Flaws Shadow Archives CVE-2026-0866 MS-Agent Prompt Injection CVE-2026-2256 basic-ftp Path Traversal CVE-2026-27699 telnetd Root Vulnerability CVE-1999-0073 Regression USR-W610 Vulnerabilities End-of-Life IoT Security IceWarp Security Update IceWarp Vulnerabilities Airleader Master Vulnerability CVE-2026-1358 ZLAN5143D Vulnerability CISA ICS Advisory Acronis Cyber Protect Vulnerability CVE-2025-30411 WAGO 852 Vulnerability OT Network Security SandboxJS Vulnerability Sandbox Escape (CVSS 10.0) Kubernetes Local Path Provisioner CVE-2025-62878 CISA Unresponsive Vendors Avation & RISS Vulnerabilities KiloView Vulnerability CVE-2026-1453 OpenClaw RCE vulnerability Johnson Controls Vulnerability CVE-2025-26385 SandboxJS Vulnerability CVE-2026-23830 ibaPDA Vulnerability CVE-2025-14988 Protobuf Vulnerability CVE-2026-0994 AVEVA Process Optimization Vulnerability CVE-2025-61937 ConnectWise PSA Vulnerability CVE-2026-0695 Aruba VIA Vulnerability CVE-2025-37186 aiohttp v3.13.3, Denial of Service (DoS) SmarterMail RCE, CVE-2025-52691 Airoha RACE, Headphone Jacking HPE OneView RCE CVE-2025-37164 FreePBX Auth Bypass, PBX Takeover ScreenConnect Config Flaw, Untrusted Extensions Ruby SAML Auth Bypass, XML Parser Differential Devolutions SQL Injection, Password Manager Flaw Vivotek Unauthenticated RCE, EOL IP Camera Flaw Lynx+ Critical Flaw, Unauthenticated Reset Firebox Default Credentials, CVE-2025-59396 Veeder-Root RCE, Critical ATG Flaw ArcGIS Server SQLi Watchdoc RCE, CVE-2025-58384 Delta DIALink Daikin Security Gateway, authentication bypass Frostbyte10, industrial controller security SunPower, vulnerability Ubiquiti UniFi Connect, EV Station Vulnerabilities Adobe Experience Manager, RCE Vulnerability UniFi Access, Command Injection LDAPNightmare - CVE-2025-1316
  • Vulnerability Report

High-Severity DoS Flaw Hits Google Protocol Buffers (CVE-2026-0994)

Do Son January 27, 2026 0

CVE-2026-0994 (CVSS 8.2) in Google Protobuf Python allows DoS via nested "Any" messages. Recursion limit bypass causes crashes. Update now.

“Repo Squatting”: How Hackers Are Using GitHub’s Own Features to Hijack Official Repos GitHub Copilot Pro trial suspension GitHub Actions Platform Fee, Self-Hosted Runner Tax 2026 GitHub Apple ID, Privacy Login GitHub Microsoft Github disruptions CVE-2025-30066 GitHub Outage, Service Disruption
  • Cybercriminals

“Repo Squatting”: How Hackers Are Using GitHub’s Own Features to Hijack Official Repos

Do Son January 27, 2026 0

Attackers exploit GitHub forks ("Repo Squatting") to push HijackLoader malware via official-looking URLs. Technique remains active; verify all downloads.

Exploit Code Publicly Released: Critical Firefox WebRTC Flaw Allows RCE (CVSS 9.8) Firefox built-in VPN Firefox VPN data limit, Firefox VPN countries, Mozilla VPN subscription Sanitizer API Firefox 148 Security Firefox WebRTC Vulnerability CVE-2025-14321 PoC Firefox VPN Feature, Browser-Only VPN Firefox Add-ons Rollback Firefox Encryption Firefox MKV support Firefox ESR, Windows 7
  • Vulnerability

Exploit Code Publicly Released: Critical Firefox WebRTC Flaw Allows RCE (CVSS 9.8)

Do Son January 27, 2026 0

Public PoC exploit released for critical Firefox WebRTC flaw CVE-2025-14321 (CVSS 9.8). AI-discovered bug allows remote code execution. Update now.

“G_Wagon” Malware Hides in Fake NPM UI Library to Steal Cloud Keys Lotus Wiper Digital Sabotage G_Wagon Malware NPM Supply Chain Attack IMAPLoader malware ResolverRAT Malware Evasion
  • Malware

“G_Wagon” Malware Hides in Fake NPM UI Library to Steal Cloud Keys

Do Son January 27, 2026 0

Malicious npm package "ansi-universal-ui" drops "G_Wagon" infostealer to steal cloud keys and wallets. Check for .gwagon_status and rotate creds now.
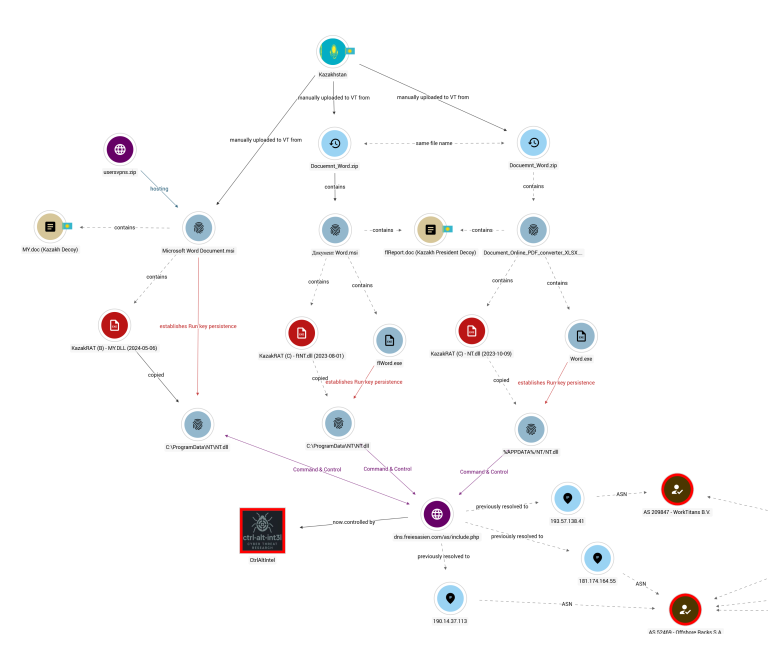
Hijacking the Hackers: Researchers Sinkhole “KazakRAT” Espionage Campaign KazakRAT Espionage State-Affiliated Malware
  • Cyber Security
  • Malware

Hijacking the Hackers: Researchers Sinkhole “KazakRAT” Espionage Campaign

Do Son January 27, 2026 0

Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

The CAPTCHA Trap: ClearFake Malware Tricks Users Into Hacking Themselves axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Malware

The CAPTCHA Trap: ClearFake Malware Tricks Users Into Hacking Themselves

Do Son January 27, 2026 0

New ClearFake malware uses fake CAPTCHAs & "ClickFix" tactics to trick users into pasting malicious code. 150k victims infected via blockchain.
“Contagious Interview”: How North Korean Hackers Use Fake Jobs to Breach IT Firms PurpleBravo Contagious Interview
  • Cybercriminals

“Contagious Interview”: How North Korean Hackers Use Fake Jobs to Breach IT Firms

Do Son January 27, 2026 0

North Korean group PurpleBravo uses fake job offers to breach IT firms. The "Contagious Interview" campaign deploys malware via coding tests.

Trusted Tool, Hidden Threat: Official EmEditor Installer Hijacked to Push Malware EmEditor Supply Chain Attack Trojanized Installer
  • Malware

Trusted Tool, Hidden Threat: Official EmEditor Installer Hijacked to Push Malware

Do Son January 27, 2026 0

Official EmEditor installer hijacked to push malware. This supply chain attack steals credentials & evades detection. Check your logs for these domains.

1Password’s New “Genius” Defense: A Shield Against the Sneaky Copy-Paste Phishing Trap 1Password phishing protection
  • Technology

1Password’s New “Genius” Defense: A Shield Against the Sneaky Copy-Paste Phishing Trap

Do Son January 26, 2026 0

1Password launches a new layer of security that warns you before pasting credentials into suspicious sites. Stop phishing scams before they steal your login.

The Ouroboros Effect: Is ChatGPT Citing Elon Musk’s AI-Generated Grokipedia Into a “Content Trap”? OpenAI desktop Super App GPT-4o retirement date AI Model Collapse ChatGPT Personalization Characteristics, OpenAI Tone Sliders 2025 ChatGPT Ads OpenAI Losses AI browser, ChatGPT Atlas ChatGPT Em Dash AI Writing Quirks
  • Technology

The Ouroboros Effect: Is ChatGPT Citing Elon Musk’s AI-Generated Grokipedia Into a “Content Trap”?

Do Son January 26, 2026 0

ChatGPT is reportedly citing Elon Musk’s AI-authored Grokipedia, sparking fears of "model collapse" and a circular loop of unverified AI-generated misinformation.

Boot Loop Nightmare: Microsoft Confirms Windows 11 January Update Causes System-Killing BSOD C Windows SecureBoot folder KB5089549 Windows 11 BSOD Microsoft Windows, Rust programming WINS Service Deprecation Windows Server DNS Migration Windows Driver Standard OEM Kernel Privileges Windows Agentic OS Task Manager Bug, Windows 11 Performance Windows 11, Microsoft, WinRE, Update Bug, Tech Support Windows 11 OOBE, Microsoft Account Mandatory Windows 11, SSD failures Windows 11 Recovery, Black Screen of Death Windows 11 Update Issue, KB5062324 Windows 11, Indicator Bar
  • Windows

Boot Loop Nightmare: Microsoft Confirms Windows 11 January Update Causes System-Killing BSOD

Do Son January 26, 2026 0

Microsoft confirms the January Windows 11 update is causing critical "Unmountable Boot Volume" errors. See if your hardware is at risk of a system collapse.

Microsoft Issues Emergency Auto-Patch: Is Your Outlook Classic Still Freezing? Windows 11 app updates Windows Insider preview build, Calculator app update, built-in Windows apps Windows 11 KB5089549 network lag Windows 11 Home to Pro Education upgrade Windows 11 Start menu update Windows 11 update KB5079391 Windows 11 KB5085516 OOB update Windows 11 C drive permission error Windows 11 C drive access denied Windows native NVMe driver UEFI Secure Boot certificate rotation Windows 11 printer driver policy Windows 11 printer driver deprecation Windows 11 Build 26300 Sysmon Windows 11 Storage settings restriction Windows 11 Build 26300.7674, Windows Insider channel migration 2026 Windows 11 Update Fix KB5073455 shutdown bug, Secure Launch restart loop Windows 11 File Explorer search performance, Search Indexer RAM usage fix Windows 11 Gaming PC Specs, NVMe DirectStorage Windows 10 End of Support Windows 11 Slow Adoption Windows 11 Crash Loop KB5062553 Bug Update and Shut Down, KB5067036 Windows authentication, Kerberos bug Windows 11 fix, localhost bug Windows 11 Update Restart, Update and Shut Down Windows SMBv1 Windows 11 Arm, Easy Anti-Cheat Windows 11 error, Pluton Windows 11 24H2, Easy Anti-Cheat Windows Firewall Bug, Microsoft Update Error Windows 11, JScript9Legacy Windows Activation, TSforge Windows 11 Update, Firewall Error Windows 11 25H2, Annual Update Windows Resiliency Initiative, Kernel Security Windows 11 Upgrade, ESU Program Windows 11 Recall, Data Export Windows 11 Easy Anti-Cheat Windows 11 Update, Cumulative Update Windows Update, ACPI.sys Windows Updates, Enterprise Software Windows 11 Start Data Encryption Standard Printing Problems Windows 11 updates Estimated installation time Smart App Control, Windows 11 security
  • Windows

Microsoft Issues Emergency Auto-Patch: Is Your Outlook Classic Still Freezing?

Do Son January 26, 2026 0

Microsoft releases emergency auto-updates to fix critical Outlook Classic freezes and cloud storage failures in Windows 11. Check your build number today.

Apple’s Grand Offensive: 20+ New Devices, Foldables, and Robotic AI Hubs Apple HomePad delay Tesla CarPlay integration 2026 Apple CarPlay AI integration 2026 Apple 2026 product roadmap rumors, foldable iPhone release date Apple Vision Pro sales slump, Vision Pro production cut Russia FaceTime Ban Network Blockade Apple Apple 2026 Roadmap, iPhone Foldable, Apple Intelligence Apple Maps ads, iOS monetization Apple, Digital Markets Act FCC Leak, iPhone 16e Schematics iPhone Fold Apple Made in India Apple US Investment, Indian Tariffs Apple Leadership, Tim Cook Tenure Siri Redesign, Apple AI Apple App Store Apple EU, Digital Markets Act CVE-2022-32898 Third-Party iOS Apps Apple Antitrust, DOJ Lawsuit
  • Technology

Apple’s Grand Offensive: 20+ New Devices, Foldables, and Robotic AI Hubs

Do Son January 26, 2026 0

Apple plans a 20-device blitz in 2026! From the foldable iPhone to a robotic Home Hub and a budget A18 MacBook, see the full leaked roadmap.

The Grand Reunion: Apple Taps Intel to Build Future “Made in USA” iPhone Chips Apple Spring Event 2026 Apple Intel 14A iPhone 2028, Intel Foundry Apple Silicon iPhone 18 glass cloth shortage, Nittobo T-glass Apple crisis Apple UK App Store lawsuit appeal, Apple tax £1.5bn damages Apple AI Leadership Shakeup Giannandrea Subramanya Touchscreen MacBook Pro Apple 2026 Roadmap Apple Smart Home, Desktop Robot Apple H3 Chip, AirPods Camera Apple chips, on-device AI Apple AI, retail chatbot MacBook, Affordable Foldable iPhone, Apple Strategy Apple COO, Leadership Transition DOJ Lawsuit Apple EU Policy, App Store Fees CVE-2024-23222 Apple French antitrust fine
  • Technology

The Grand Reunion: Apple Taps Intel to Build Future “Made in USA” iPhone Chips

Do Son January 26, 2026 0

Apple may return to Intel by 2028 to fab iPhone chips on the 14A node. Discover how NVIDIA's AI boom and U.S. politics are reshaping Apple Silicon.

The Master Key Trap: Microsoft Confirms It Hands BitLocker Keys to the FBI Microsoft BitLocker FBI recovery key, Windows 11 cloud escrow privacy BitLocker Recovery, Windows Update Bug BitLocker, data loss ShrinkLocker ransomware Windows update BitLocker, BitLocker fix
  • Windows

The Master Key Trap: Microsoft Confirms It Hands BitLocker Keys to the FBI

Do Son January 26, 2026 0

Microsoft confirms it surrenders BitLocker keys to the FBI in Jan 2026. Discover why your Windows 11 cloud-stored key is a major privacy liability.

Siri’s Gemini Glow-Up: Apple and Google Set to Launch “Truly Intelligent” iOS 26.4 Apple iOS 26.4 Siri Google Gemini, AFM v10 parameter count Gemini 3 Flash benchmarks, Google Gemini 3 Flash vs GPT-5.2
  • Technology

Siri’s Gemini Glow-Up: Apple and Google Set to Launch “Truly Intelligent” iOS 26.4

Do Son January 26, 2026 0

Apple debuts Gemini-powered Siri in Jan 2026! Discover how iOS 26.4 brings on-screen awareness and a 1.2T parameter AI model to your iPhone.

PoC Released for Critical Oracle E-Business Suite Flaw Exploited by Ransomware Oracle E-Business Suite RCE CVE-2025-61882 PoC
  • Vulnerability

PoC Released for Critical Oracle E-Business Suite Flaw Exploited by Ransomware

Do Son January 26, 2026 0

Public PoC released for critical Oracle E-Business Suite RCE (CVE-2025-61882). Ransomware gangs are actively exploiting this CVSS 9.8 flaw. Patch now.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115934CVSS 9.3
    An unauthenticated SQL injection can occur on the front end of any site that uses craft.search to perform a search,...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119756CVSS 9.3
    Tasmota through 16.0.0, fixed in commit e97e1e4, contains a heap out-of-bounds write vulnerability in SendReceiveDeviceGroupMessage() that allows unauthenticated...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 9, 2026
  • CVE-2026-102530CVSS 9.4
    JupyterLab Desktop is the cross-platform desktop application for JupyterLab. Prior to 4.6.2-1, remote-server URLs were inserted into the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123960CVSS 9.4
    A weakness has been identified in TOTOLINK CA300-PoE 6.2c.884. This affects the function setWanConfig of the file /cgi-bin/cstecgi.cgi....
    📅 Updated: Nov 9, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 9, 2026
  • CVE-2026-100358CVSS 9.4
    SuiteCRM is an open-source, enterprise-ready Customer Relationship Management (CRM) software application. Prior to 7.15.2 and 8.10.2, the Studio...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.