Skip to content
November 10, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
Booting Up Malware: Critical Flaw in Rufus Grants Admin Access (CVE-2026-23988) Rufus Vulnerability CVE-2026-23988
  • Vulnerability Report

Booting Up Malware: Critical Flaw in Rufus Grants Admin Access (CVE-2026-23988)

Do Son January 26, 2026 0

Rufus flaw CVE-2026-23988 allows local users to gain Admin rights via a race condition. Update to version 4.12 immediately to secure your system.
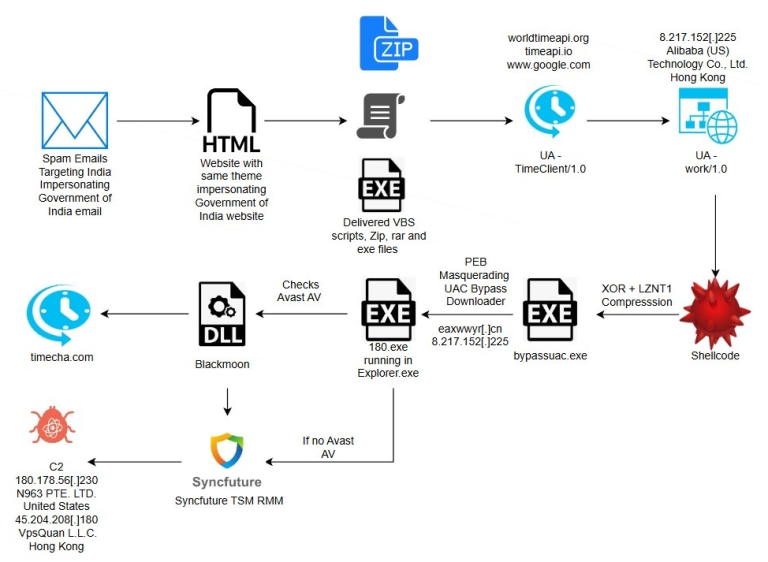
India Tax Scam Alert: “SyncFuture” Campaign Installs Chinese Surveillance Tool SyncFuture Espionage India Tax Phishing
  • Cybercriminals

India Tax Scam Alert: “SyncFuture” Campaign Installs Chinese Surveillance Tool

Do Son January 26, 2026 0

"SyncFuture" spies on Indian users via fake Income Tax emails. This advanced campaign bypasses antivirus & installs Chinese IT tools for total surveillance.

The Developer’s Backdoor: North Korea Weaponizes Visual Studio Code Mercenary Akula European Financial Targeting AI-Generated Malware React2Shell Exploit UAT-8837 Critical Infrastructure Attack APT36, BOSS Linux BRICKSTORM Malware, China Espionage Curly COMrades, MucorAgent Chinese APT - HTTP Client Tools Shuckworm Cyber Espionage
  • Cyber Security
  • Malware

The Developer’s Backdoor: North Korea Weaponizes Visual Studio Code

Do Son January 26, 2026 0

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

Code by AI: KONNI APT Targets Crypto Devs with “Polished” Backdoor NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Cybercriminals

Code by AI: KONNI APT Targets Crypto Devs with “Polished” Backdoor

Do Son January 26, 2026 0

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.

The Invisible Trap: GenAI Now Creates “Living” Polymorphic Phishing Pages GenAI Phishing Polymorphic Attacks
  • Cybercriminals

The Invisible Trap: GenAI Now Creates “Living” Polymorphic Phishing Pages

Do Son January 26, 2026 0

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.

“Osiris” Rises: New Ransomware Targets Southeast Asian Food Giant with Advanced Tactics Osiris Ransomware Inc Ransomware Connection CountLoader Massive Ransomware Campaign CVE-2025-0289
  • Malware

“Osiris” Rises: New Ransomware Targets Southeast Asian Food Giant with Advanced Tactics

Do Son January 26, 2026 0

New Osiris ransomware hits Southeast Asia, linking to Inc & Medusa groups. It uses BYOVD tactics to disable defenses. Unrelated to the 2016 variant.

CVE-2025-67968 (CVSS 9.9): Critical Flaw in Real Estate Theme Exposes 30,000 Sites to Takeover RealHomes CRM Vulnerability CVE-2025-67968
  • Vulnerability Report

CVE-2025-67968 (CVSS 9.9): Critical Flaw in Real Estate Theme Exposes 30,000 Sites to Takeover

Do Son January 26, 2026 0

Critical RealHomes CRM flaw CVE-2025-67968 (CVSS 9.9) allows any logged-in user to upload malicious files. Update to v1.0.1 immediately to prevent takeover.

CVE-2026-24656: Deserialization Flaw in Apache Karaf Exposes Systems to DoS CVE-2022-40145 Apache Karaf Vulnerability CVE-2026-24656
  • Vulnerability Report

CVE-2026-24656: Deserialization Flaw in Apache Karaf Exposes Systems to DoS

Do Son January 26, 2026 0

Apache Karaf Decanter flaw CVE-2026-24656 allows unauthenticated attackers to crash the log collector via deserialization. Update to v2.12.0 immediately.

Ghost in the Code: Critical RCE Found in Abandoned Python PLY Library (CVSS 9.8) Python Security Memory Safety PLY Vulnerability CVE-2025-56005 Python Software Foundation, NSF DEI CVE-2024-12254
  • Vulnerability Report

Ghost in the Code: Critical RCE Found in Abandoned Python PLY Library (CVSS 9.8)

Do Son January 26, 2026 0

Abandoned Python PLY library contains a critical RCE flaw (CVE-2025-56005) via an undocumented "picklefile" parameter. No patch is expected.

Be the Viral Star: Google Photos Launches AI “Me Meme” Feature Google Photos Me Meme feature, AI meme generator 2026
  • Technology

Be the Viral Star: Google Photos Launches AI “Me Meme” Feature

Do Son January 26, 2026 0

Google Photos debuts Me Meme in Jan 2026! Use generative AI to put your face in iconic meme templates with one tap. Now rolling out to U.S. users.

The Multi-Billion Dollar Suit: Solos Technology Aims to Halt Ray-Ban Meta Sales Meta Malibu 2 smartwatch Solos Technology vs Meta lawsuit, Ray-Ban Meta patent infringement
  • Technology

The Multi-Billion Dollar Suit: Solos Technology Aims to Halt Ray-Ban Meta Sales

Do Son January 26, 2026 0

Solos Technology sues Meta for billions in Jan 2026, alleging Ray-Ban Meta glasses use stolen patents. A sales ban could be a huge blow to Reality Labs.

TikTok’s Great Escape: Divestiture Closes as New USDS Entity Takes Control TikTok USDS Joint Venture LLC divestiture, Project Texas 2.0 ByteDance stake TikTokRefugee TikTok Ban, US Extension
  • Technology

TikTok’s Great Escape: Divestiture Closes as New USDS Entity Takes Control

Do Son January 26, 2026 0

TikTok avoids a U.S. ban in Jan 2026 by forming TikTok USDS Joint Venture LLC. ByteDance cedes 80.1% control to Oracle, Silver Lake, and MGX.

The DMA Standoff: Apple Slams EU “Delay Tactics” as Setapp Mobile Collapses iOS 27 Liquid Glass slider iPhone Flip rumors 2026 Setapp Mobile iOS shutdown, Apple DMA political delay tactics Apple AI pin wearable 2027, Siri Campos Gemini integration Apple AI strategy 2026, Liquid Glass interface Apple Intelligence Mac Pro Cancelled Mac Studio Future App Store antitrust, UK lawsuit iPhone Fold Hinge, Cost Optimization MacBook Pro, OLED display Apple supply chain, manufacturing automation Apple home security, smart camera Apple Earnings, AI Investment Apple EU Fine, DMA Appeal CVE-2023-23529
  • Technology

The DMA Standoff: Apple Slams EU “Delay Tactics” as Setapp Mobile Collapses

Do Son January 26, 2026 0

Apple accuses the EU of "political delay tactics" in Jan 2026 after Setapp Mobile shuts down. Discover why the Core Technology Fee is causing a crisis.

CVE-2025-27821: Apache Patches Out-of-Bounds Write Flaw in Hadoop HDFS Client CVE-2021-25642 Hadoop HDFS Vulnerability CVE-2025-27821
  • Vulnerability Report

CVE-2025-27821: Apache Patches Out-of-Bounds Write Flaw in Hadoop HDFS Client

Do Son January 25, 2026 0

Apache Hadoop HDFS native client flaw CVE-2025-27821 allows out-of-bounds writes. Update to v3.4.2 to prevent crashes and ensure data stability.
CISA Alert: Critical VMware vCenter RCE (CVSS 9.8) Now Exploited in the Wild CISA KEV Catalog DarkSword Exploit Draytek Routers VMware vCenter RCE CVE-2024-37079
  • Vulnerability Report

CISA Alert: Critical VMware vCenter RCE (CVSS 9.8) Now Exploited in the Wild

Do Son January 25, 2026 0

CISA adds VMware vCenter flaw CVE-2024-37079 (CVSS 9.8) to KEV catalog. Hackers are actively exploiting this RCE bug. Patch immediately.

How New Phishing Kits Are Turning Vishing into Real-Time Orchestration Vishing Kits MFA Bypass
  • Cybercriminals

How New Phishing Kits Are Turning Vishing into Real-Time Orchestration

Do Son January 25, 2026 0

Okta reveals new vishing kits that "drive" victim browsers. These real-time tools sync phone calls with phishing pages to bypass MFA number matching.

Bitwarden Evolution: New Monthly Billing and Proactive Phishing Defense for 2026 Bitwarden pricing update 2026, Bitwarden Premium monthly cost Windows 11 Passkey API Password Manager Integration
  • Technology

Bitwarden Evolution: New Monthly Billing and Proactive Phishing Defense for 2026

Do Son January 25, 2026 0

Bitwarden updates pricing in Jan 2026: Premium is now $1.65/mo. Discover the new Phishing Blocker, 5GB storage, and loyalty discounts for users.
End of an Era: Linux 7.0 Finally Retires the 1980s Supercomputing Legend Linux Kernel 7.1 release Linux Kernel update, AMD ZEN 6 support, Linux driver fixes Linux Kernel 7.1 i486 support Linux 7.0 HIPPI support removal, legacy networking protocol retirement Linus Torvalds AI slop Linux kernel, Lorenzo Stoakes AI tool debate Linux Kernel Rust CVE-2025-68260, Android Binder Rust Race Condition TSEM Security Module Controversy, Linus Torvalds LSM Dispute Kernel Panic, PoC released Linux Kernel 6.16, File System Fixes CVE-2023-42753 - Linux Kernel Developers
  • Linux

End of an Era: Linux 7.0 Finally Retires the 1980s Supercomputing Legend

Do Son January 25, 2026 0

Linux 7.0 officially drops HIPPI support in Jan 2026. Discover the history of this 800Mbps supercomputing giant and why the kernel is moving on.

Deep Kernel Fix: Linux Closes a 5-Year-Old Flaw in x86 Memory Handling Linux Kernel legacy driver removal Linux kernel x86 page fault, interrupt state asymmetry fix Linux ISO, false positive CVE-2023-6200 - Linux Kernel 6.12 LTS 6.14
  • Linux

Deep Kernel Fix: Linux Closes a 5-Year-Old Flaw in x86 Memory Handling

Do Son January 25, 2026 0

A 5-year-old flaw in Linux x86 page fault handling has finally been patched in Kernel 6.19. Discover how engineers fixed this "combinatorial nightmare."
CISA Adds 4 Critical Flaws to “Must-Patch” List as Exploits Surge CISA KEV Update Versa Concerto Vulnerability KEV Catalog Vulnerability Patch CVE-2025-30406
  • Vulnerability Report

CISA Adds 4 Critical Flaws to “Must-Patch” List as Exploits Surge

Do Son January 23, 2026 0

CISA adds 4 flaws to KEV, including critical Versa Concerto auth bypass (CVSS 9.2) & malicious "Prettier" package. Patch by Feb 12 to stop active attacks.

The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support NexPhone multi-OS smartphone, Windows 11 Linux Android phone
  • Technology

The Hacker’s Dream: NexPhone Debuts with Triple-OS Boot and 2036 Support

Do Son January 23, 2026 0

Discover the NexPhone: A 2026 breakthrough running Android, Linux, and Windows 11 on a single chip. Built for geeks with support until 2036.

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits Fortinet patch bypass 2026, FortiGate SSO authentication exploit SharePoint Zero-Day, China APTs Exploited Vulnerabilities 2023
  • Vulnerability Report

“New” Path of Attack: Fully Upgraded Fortinet Devices Hit by SSO Exploits

Do Son January 23, 2026 0

Fortinet warns of a new Jan 2026 attack path bypassing December’s patches. Attackers use FortiCloud SSO to hijack firewalls. Learn the critical fix.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-125350
    Use after free in XML. Reported by anonymous on 2026-11-06. Google is aware that an exploit for CVE-2026-125350...
    Admin intel📅 Updated: Nov 10, 2026
  • CVE-2026-123751CVSS 9.8
    The WP Duplicate WordPress plugin through 1.1.11 does not properly verify a request authentication value and does not...
    Watchtower Verified📅 Updated: Nov 9, 2026
  • CVE-2026-111793CVSS 4.3
    Openwave Webtop Media Transcoder does not enforce administrator-defined file type restrictions to restrict the file-types to be converted....
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-114713CVSS 8.6
    The labeled-response module in UnrealIRCd 6.0.0 before 6.2.7.1 does not escape the IRCv3 "label" message tag when echoing...
    Admin intel📅 Updated: Nov 9, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    CISA KEV📅 Added to KEV: Nov 9, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-115934CVSS 9.3
    An unauthenticated SQL injection can occur on the front end of any site that uses craft.search to perform a search,...
    📅 Updated: Nov 9, 2026
  • CVE-2026-119756CVSS 9.3
    Tasmota through 16.0.0, fixed in commit e97e1e4, contains a heap out-of-bounds write vulnerability in SendReceiveDeviceGroupMessage() that allows unauthenticated...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123488CVSS 9.3
    Craft CMS 4.0.0 before 4.18.9 and 5.0.0 before 5.11.2 contains an unauthenticated SQL injection vulnerability in the element...
    📅 Updated: Nov 9, 2026
  • CVE-2026-102530CVSS 9.4
    JupyterLab Desktop is the cross-platform desktop application for JupyterLab. Prior to 4.6.2-1, remote-server URLs were inserted into the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-123960CVSS 9.4
    A weakness has been identified in TOTOLINK CA300-PoE 6.2c.884. This affects the function setWanConfig of the file /cgi-bin/cstecgi.cgi....
    📅 Updated: Nov 9, 2026
  • CVE-2026-123966CVSS 10.0
    A vulnerability was determined in Tenda AC19 16.03.10.07. Affected by this issue is the function saveParentControlInfo of the...
    📅 Updated: Nov 9, 2026
  • CVE-2026-124059CVSS 9.4
    A security vulnerability has been detected in TOTOLINK CA300-PoE 6.2c.884. Affected by this vulnerability is the function setWiFiWdsAddConfig...
    📅 Updated: Nov 9, 2026
  • CVE-2026-100358CVSS 9.4
    SuiteCRM is an open-source, enterprise-ready Customer Relationship Management (CRM) software application. Prior to 7.15.2 and 8.10.2, the Studio...
    📅 Updated: Nov 9, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.